What Enl Financial Document Spam Actually Looks Like
If you've ever checked your work email or personal inbox and found what appears to be a legitimate-looking notification from a financial services company, then something about it felt just slightly off, you've probably run into something like Enl Financial Document Spam. It typically arrives as an email or SMS claiming you have a pending document, statement, or verification request from an entity associated with ENL Financial. The attachments are usually PDFs that look professional enough to pass a quick glance, and they contain links directing you to a login portal where credentials get captured. The structure is consistent across most campaigns. You receive a message with a subject line like "Action Required: Your Financial Document Is Ready" or "Document Verification Needed." The body contains generic urgency language. A link is provided to a domain that looks nearly identical to the real company's URL. Once you enter your information, the account is compromised or used for further fraud.
How to Identify Enl Financial Document Spam
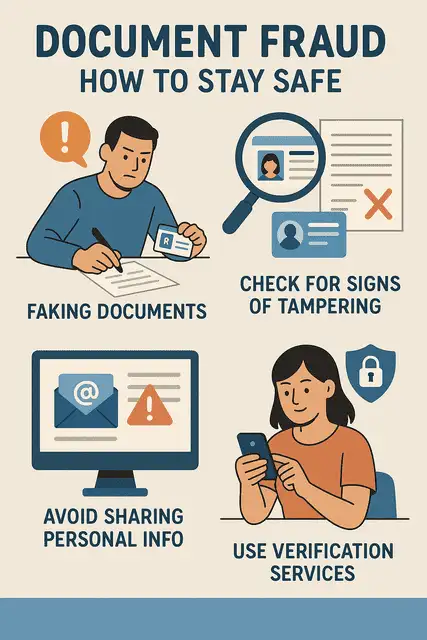
The first thing to check is the sender's actual email domain. Scammers often use lookalike domains such as enl-financial-portal.com, enlfinancial.net, or variations that add hyphens or extra words. The real ENL Financial uses specific official domains. If you're unsure, go directly to the company's known website by typing it into your browser rather than clicking any link in the message. Another tell is the attachment itself. Legitimate financial document notifications rarely contain direct .exe files or password-protected zip archives as the primary deliverable. If the attachment asks you to enable macros or enter a password to open a PDF, that's a strong indicator of a malicious payload. Real financial institutions send documents that are viewable without additional software or action on your part. I once dealt with a particularly well-made example that had proper branding, correct contact information, and even referenced a real account number format. The only clue was that the domain whois registration had been created three days before the message was sent. I verified by calling the company's known support number directly and confirming they had not sent any such communication. That verification step alone saved me from handing over credentials on a phish site that was nearly indistinguishable from the real login page.
What to Do When You Encounter It
Do not click any links. Do not download or open any attachments. Do not reply to the message. Mark it as spam or phishing in your email client so the service provider can potentially block similar messages for other users. If you already clicked a link and entered information, change your passwords immediately on the real website and contact the financial institution's fraud department through their official phone number listed on their actual website, not the one provided in the suspicious message. Some people try to report these by forwarding the email to the company it impersonates. That can help, but it's more effective to also report it through your email provider's phishing reporting tool. Google, Microsoft, and Yahoo all have built-in mechanisms for this. Federal complaint databases like the FTC's report site are another option, though they won't stop the next batch of emails targeting you specifically.
Get the Full Details
Why These Campaigns Keep Coming Back
The reason Enl Financial Document Spam persists is that the conversion rate, while low, is high enough to make it profitable. A single successful credential capture can lead to account takeover, identity theft, or further phishing campaigns using the compromised account as a trusted sender. Even if only one in ten thousand recipients falls for it, the return on investment for the attacker is substantial given how cheap it is to generate and distribute these messages at scale. The counter-intuitive part most people miss is that these emails are increasingly hard to filter out with standard spam rules. Attackers use authenticated sending methods, rotate domains quickly, and craft content that avoids common spam trigger words. They also time their sends to match business hours in your timezone. So relying solely on your email provider's spam filter is not enough. You have to actually read the envelope details — sender domain, date consistency, and whether the message context makes sense for your situation. If you receive one of these and you genuinely do have an account with the referenced financial entity, the safest path is always to log in through your bookmarked URL or the official app, check your messages there, and ignore the external notification entirely. The document, if real, will be waiting for you inside your account.