How I Actually Run Risk Assessments Without Losing My Mind
Most people treat enterprise risk assessment like it is a box you check annually. It is not. The process is iterative, messy, and usually falls apart because someone tried to do it all in one spreadsheet. I spent years watching teams produce documents that looked impressive and were completely useless six months later. Here is how it works when you stop treating it like compliance theater. Let me give you a concrete example before I get into the mechanics. A mid-size fintech company I consulted for needed to assess risk across their payment processing pipeline. They had three vendor integrations, two internal APIs handling sensitive data, and a legacy database that predated their security team. Their first attempt took eight weeks and produced a 47-page document. Nobody read past page three. The second attempt, done differently, took six days and actually changed their architecture decisions. The difference was not complexity. It was focus. They stopped trying to assess everything at once and started by mapping their actual data flow. Every transaction path, every handshake with a third party, every place data sat at rest. That map became the skeleton. Everything else hung off it. Risk categories, threat vectors, existing controls, gaps — all of it connected to something concrete they could point at and say this is where we are exposed.
What Most People Get Wrong About the Method
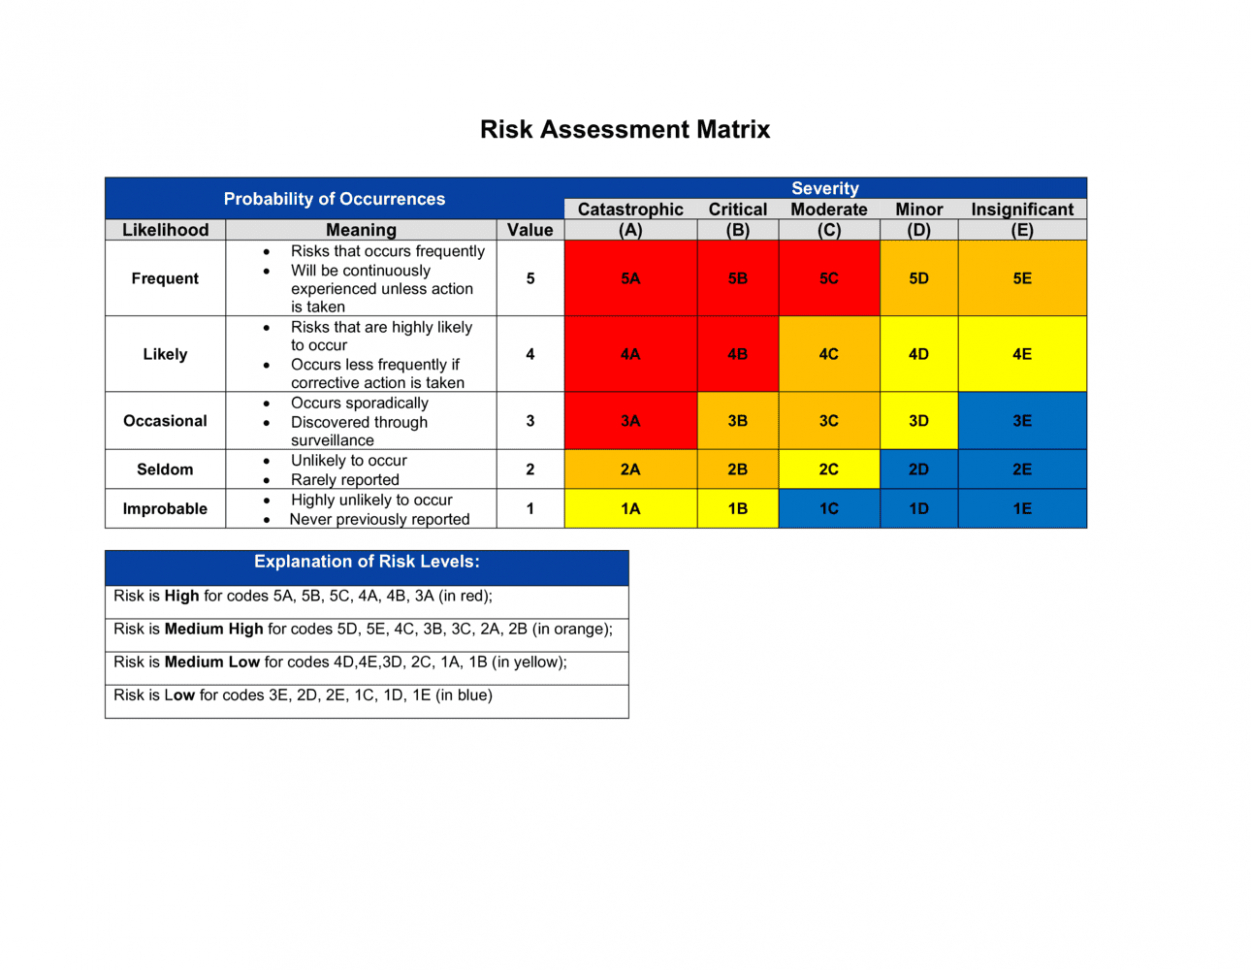
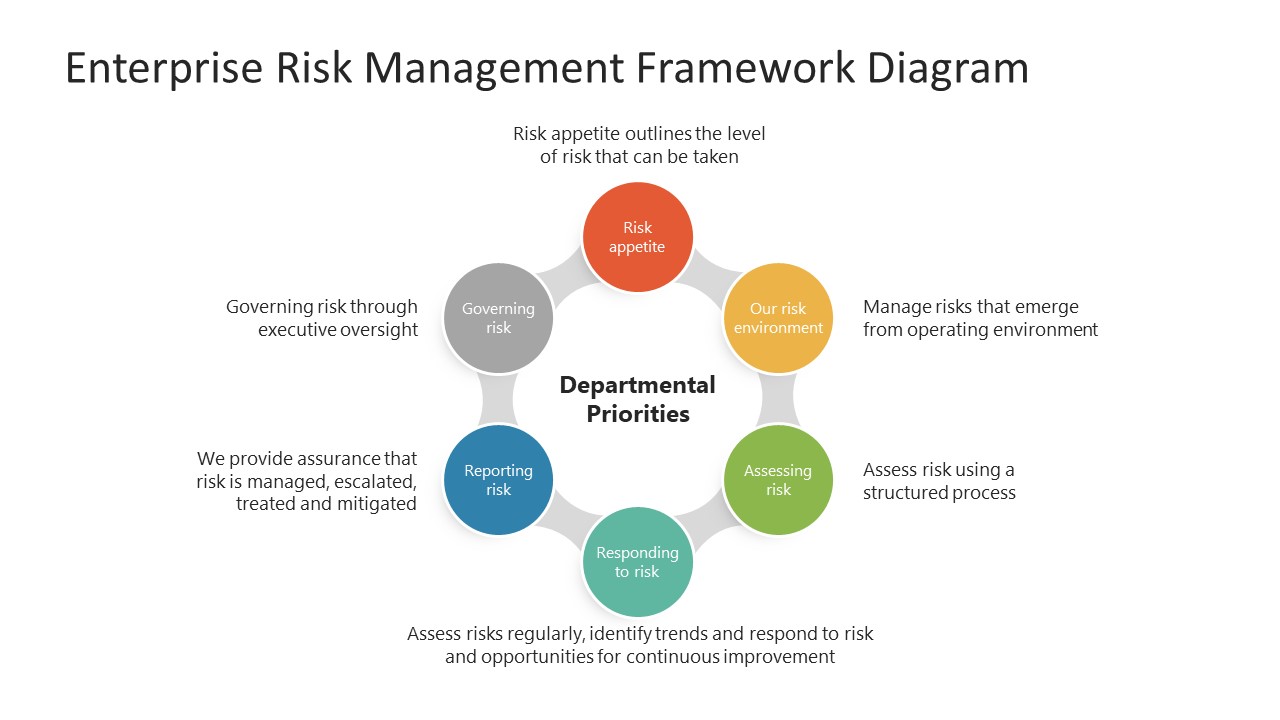
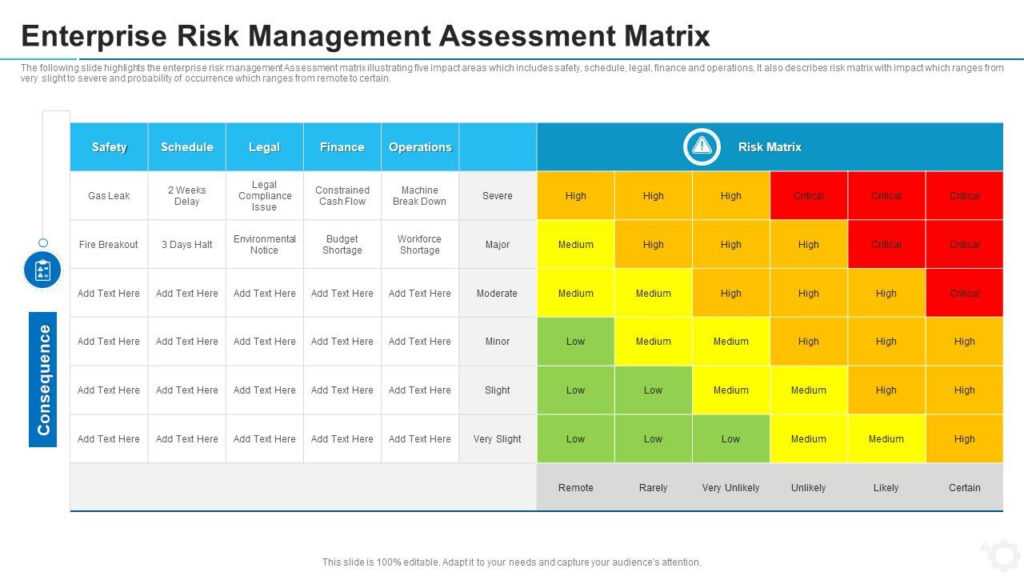
There is a standard framework most organizations follow. Identify, Assess, Mitigate, Monitor. That sequence makes sense on paper. In practice, the identification phase swallows everything because people cannot agree on what counts as a risk worth tracking. I have seen teams spend three months debating whether "employee negligence" was a valid risk category. It is not a risk category. It is a cause. You list causes under the appropriate threat, not as a standalone concern. Another common mistake is treating likelihood and impact as independent variables when they are often linked. If a threat vector becomes more likely, the impact usually shifts too. A distributed denial of service attack on your checkout page is one thing. That same attack on your internal identity management system is a completely different problem with different consequences. Score them accordingly. Do not slap the same impact rating on every event that disrupts revenue. I learned this the hard way during a healthcare compliance project. We had categorized a ransomware event as medium impact because the direct revenue loss from downtime was bounded. Six weeks into mitigation planning, we realized the same event could trigger HIPAA breach notification requirements for 14,000 patients. The impact rating jumped to critical and the mitigation timeline compressed from quarters to weeks. The original assessment had the right probability number but the wrong severity bucket. Everything downstream was wrong because of that single misclassification.
Building the Assessment Without the Bloat
Start with asset inventory. Not a comprehensive inventory. A targeted one. List the systems, data sets, and integrations that, if compromised or degraded, would cause material harm to operations, revenue, or compliance standing. Everything else can wait. In my experience, this narrows the scope to something manageable within a two to three week sprint for most organizations. A typical assessment covering five high-value asset classes with three threat scenarios each usually takes a small team about 40 person-hours total. Less if you reuse templates from previous cycles. After assets, map threats. Use a structured threat library rather than brainstorming from scratch. MITRE ATT&CK, NIST 800-30, or your own historical incident log. Pick one and stick with it. I recommend starting with your own incident log because it forces you to confront risks you actually face rather than risks that look scary in a framework document. The theoretical threats matter eventually. The known threats matter today. Then evaluate existing controls against those threats. This is where most assessments become shallow. Listing a control like "firewall deployed" tells you nothing. What firewall, what ruleset, when was it last reviewed, what traffic does it actually allow through, and has anyone tested whether it blocks the specific attack paths relevant to your assets. A control without evidence of effectiveness is just a hope. Record the evidence or mark the control as absent.
Get the Full Details
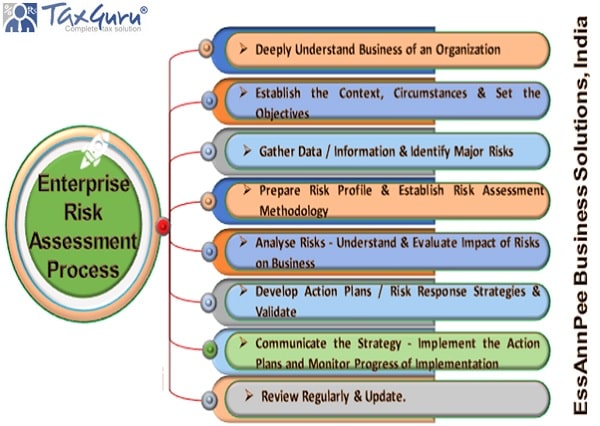
Calculate residual risk. Take the inherent risk of each asset-threat pair, subtract the risk reduction from validated controls, and you get residual risk. Compare that against your risk appetite. If it exceeds appetite, you either strengthen controls, accept the risk with documented justification, or remove the activity entirely. Most organizations stop at "strengthen controls" without asking whether the control is actually implementable within their technical constraints. I have seen teams plan controls that required infrastructure changes the engineering organization said would take nine months. That is not a mitigation plan. It is a wish list.
A Problem I Faced and How I Worked Around It
During a supply chain risk assessment for a logistics company, I hit a wall. Their third-party vendors refused to share their security posture documentation. Standard vendor risk program. Legal got involved, NDAs were exchanged, and still no usable data after six weeks. The risk assessment was stuck on a section that represented roughly 40 percent of their operational exposure. Instead of waiting for perfect data, I built the assessment around observable indicators. Uptime SLA adherence over 18 months. Public vulnerability disclosure history of the vendor. Customer breach announcements. Insurance coverage levels they disclosed in their procurement materials. SOC 2 Type II reports obtained through their parent company's public filings. None of it was ideal. All of it was better than nothing. I scored the vendor risk based on these proxies and added a confidence interval to each score. Low confidence items were flagged for reassessment once real data became available. The assessment moved forward. The risk wasn't eliminated, but it was quantified well enough for leadership to make decisions. Six months later, one of those low-confidence proxies — a vendor's unreported outage duration — turned out to be the actual failure point. The confidence interval would have caught it if we had revisited.
When This Approach Breaks Down
Enterprise risk assessment methods like this require organizational cooperation. If your security team cannot get basic cooperation from engineering or business units, no framework will save you. I have seen assessments fail because stakeholders treated the process as a security team problem rather than a business continuity problem. The output will be technically sound and organizationally ignored. The method also assumes you have some baseline visibility into your own systems. If you are running shadow IT, unmanaged cloud instances, or acquired companies whose technical stack you do not fully understand, the asset inventory will have holes. Those holes become blind spots in your risk picture. There is no workaround other than acknowledging the gaps and treating unassessed areas as highest risk until you can bring them into scope. Finally, keep in mind that this approach produces a snapshot, not a permanent state. A risk assessment loses roughly half its relevance within 90 days if you are in a fast-moving environment. Plan for quarterly refreshes of the high-priority sections even if you are not doing a full cycle. The cost of a focused refresh is a fraction of rebuilding from scratch, and it catches changes that matter — new integrations, regulatory shifts, threat landscape updates — before they become incidents.
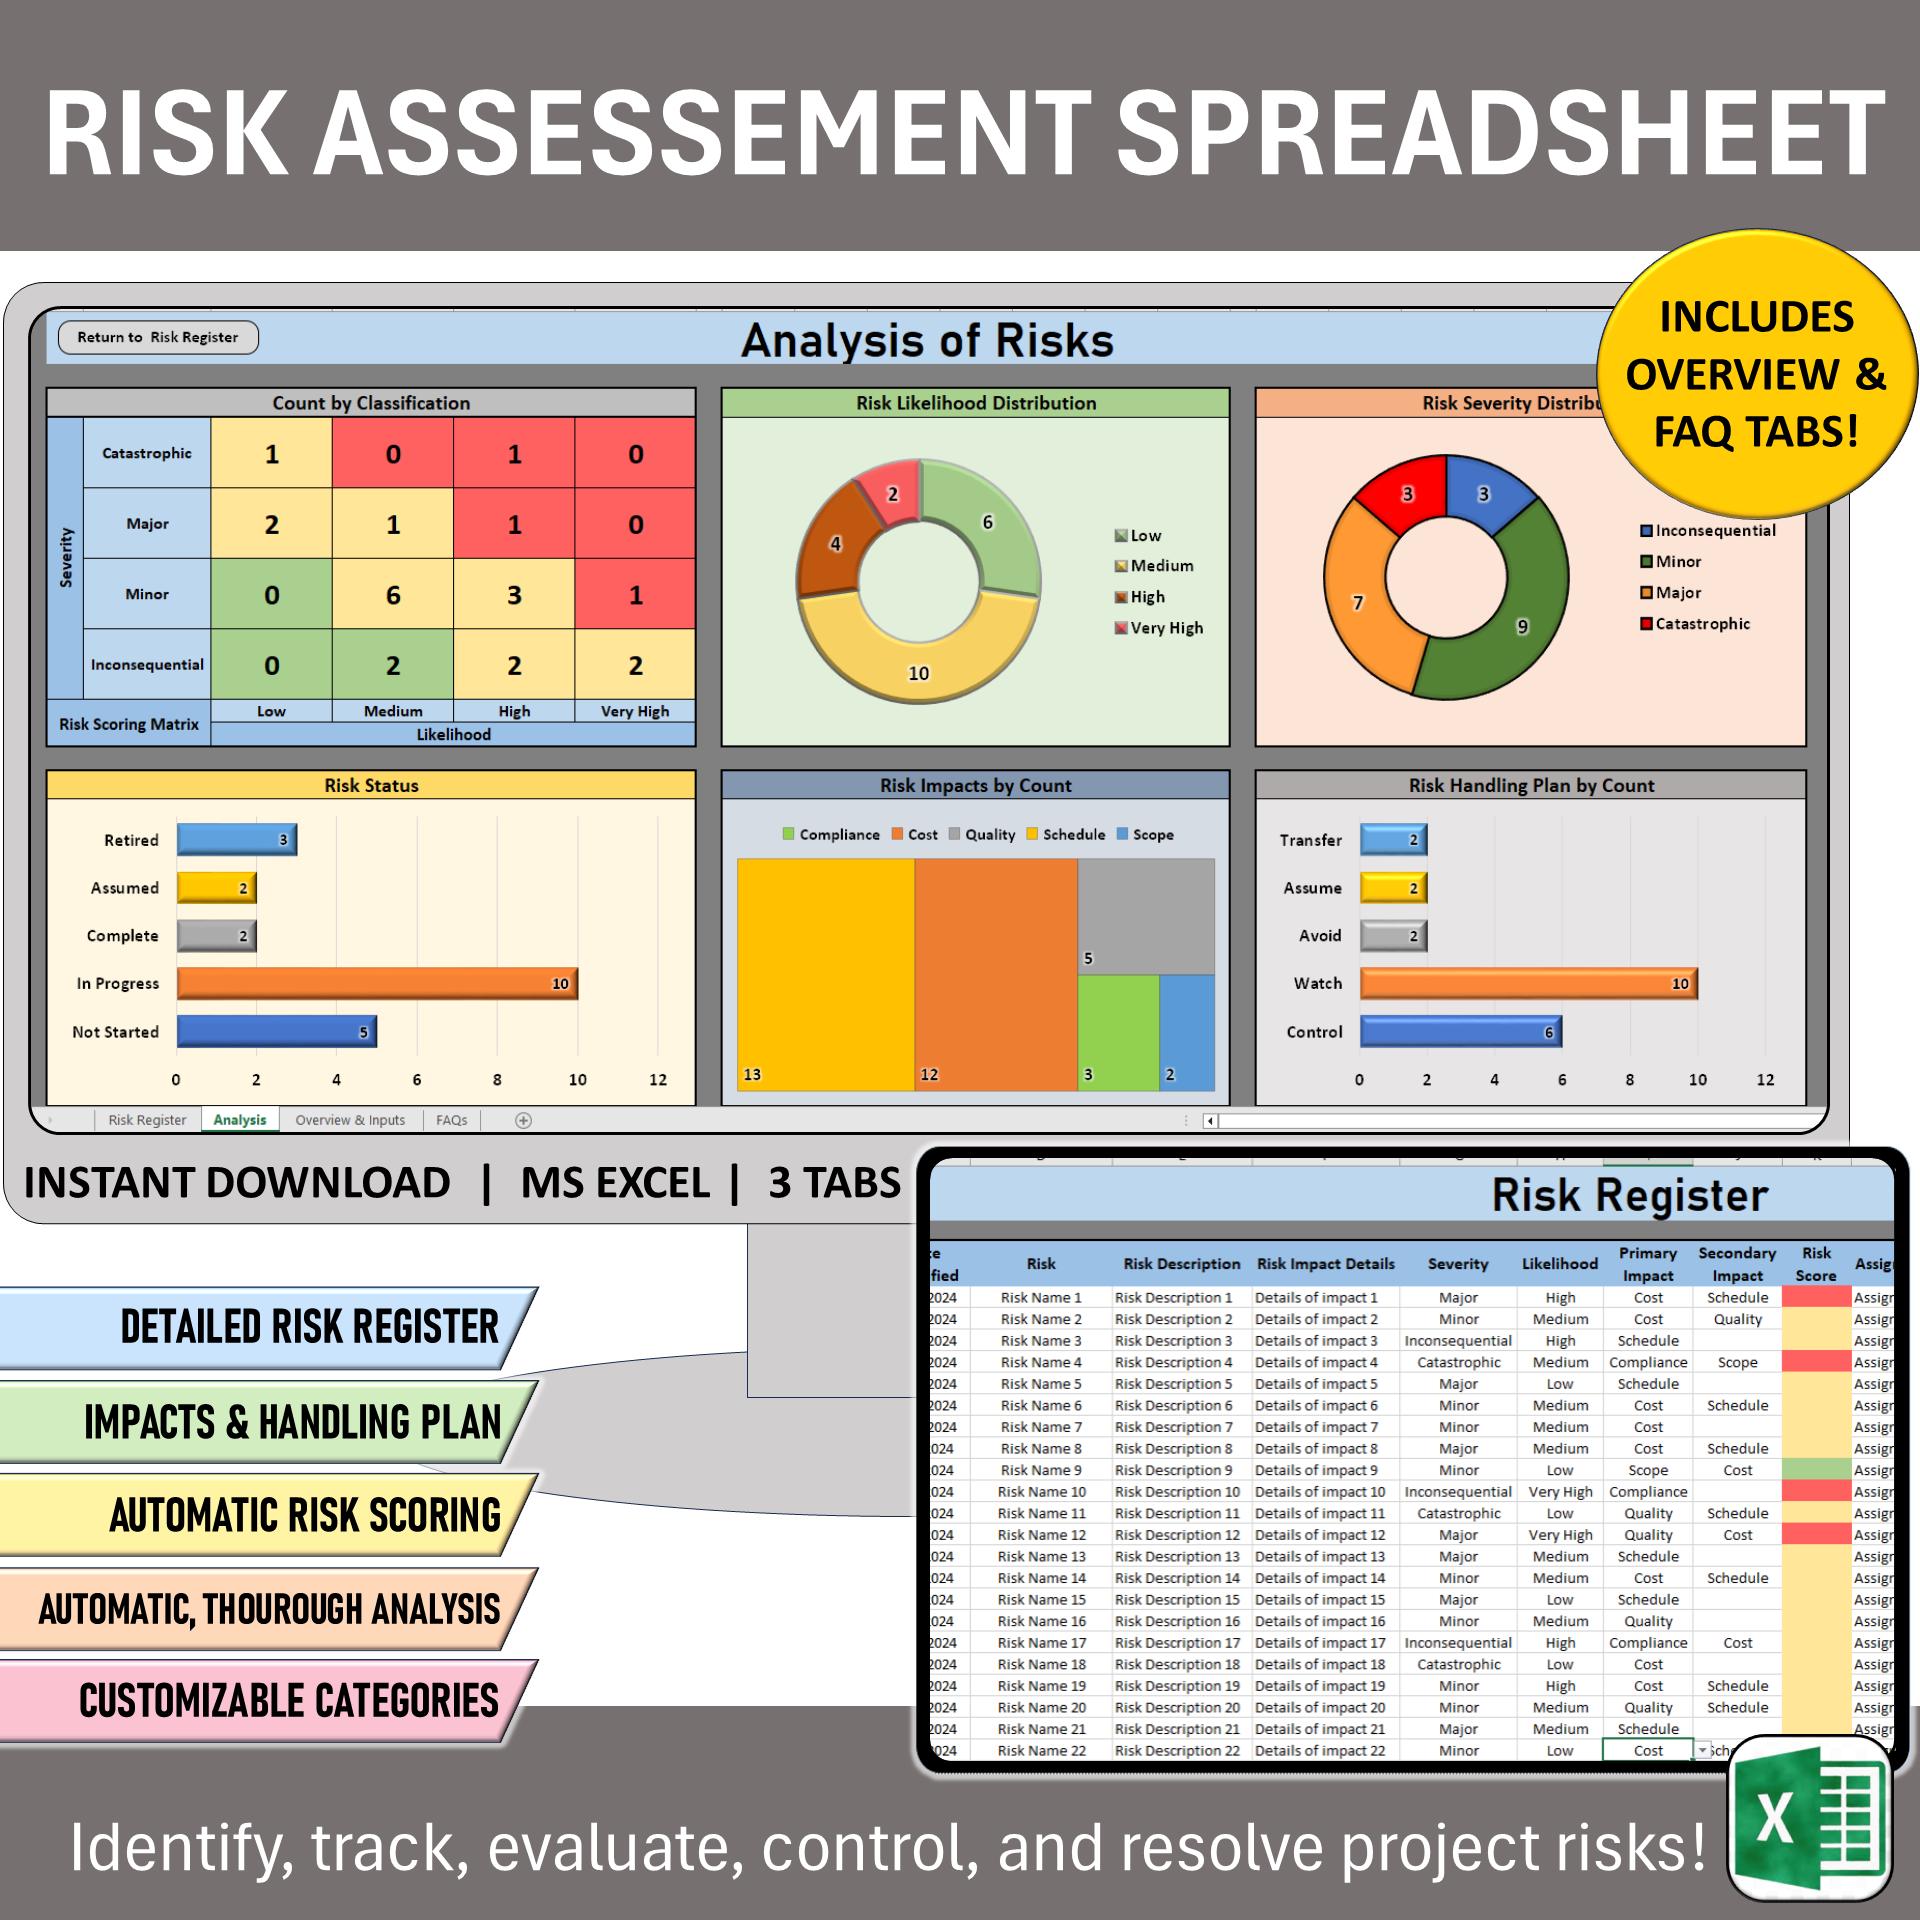
If your organization is small enough that a full formal assessment feels like overkill, start with the asset and threat mapping sections only. Drop the scoring matrix. Use a simple high-medium-low instead of numerical ratings. It takes less time, requires fewer meetings, and still gives you a prioritized list of what to address first. Perfection is the enemy of done. A rough assessment updated regularly beats a perfect one filed away and forgotten.