The Actual State of ERM
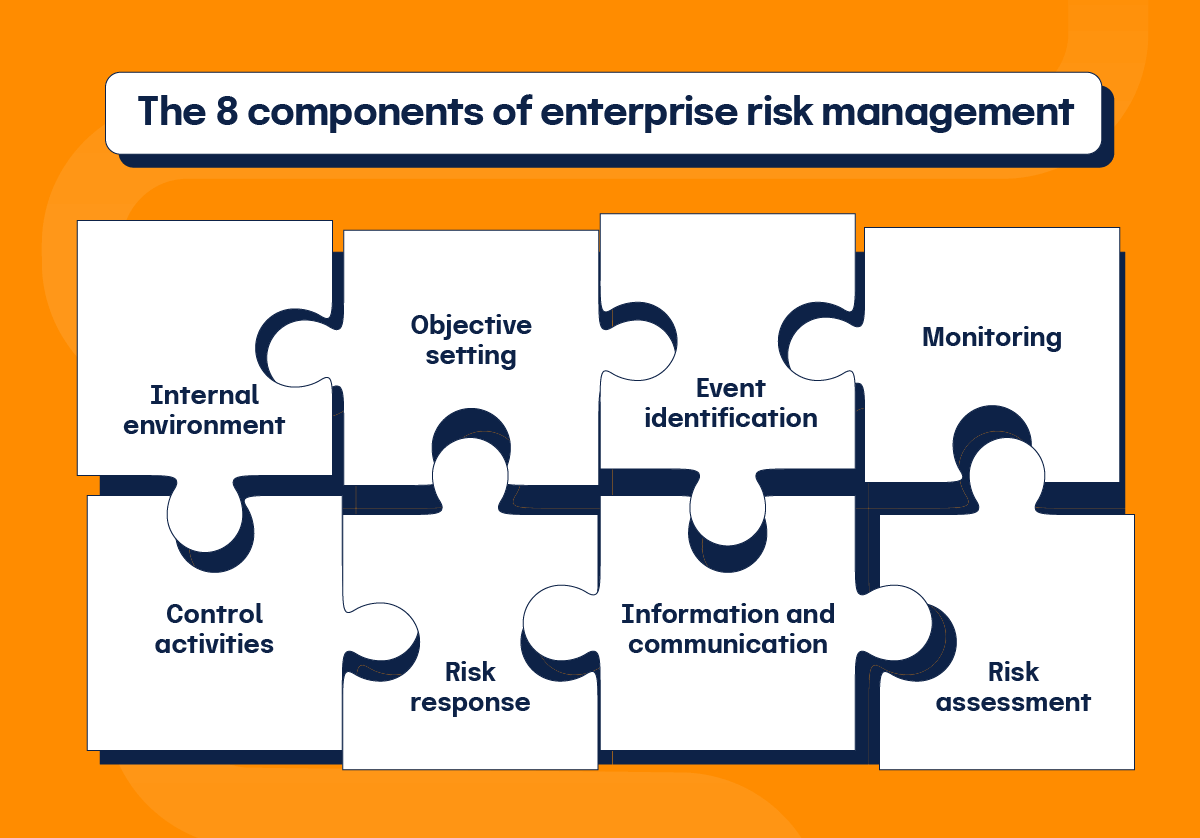
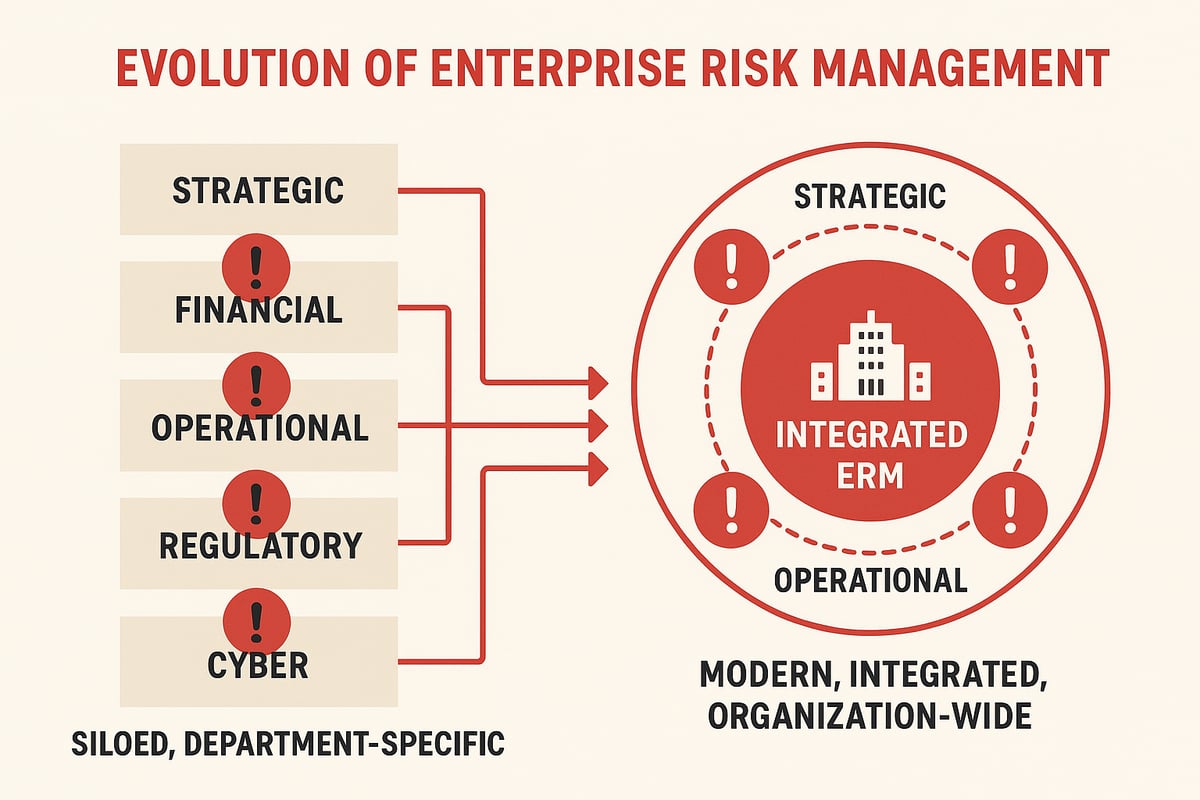
Most enterprise risk management programs exist as PowerPoint presentations that get updated quarterly and filed away until a regulator asks to see them. I have watched this happen across three industries and eight different organizations. The gap between what the textbook says ERM should be and what it actually is in practice is enormous. That is not a criticism so much as a starting point. If you are looking for Enterprise Risk Management For Dummies, you probably already know the theory. You have read about COSO frameworks, risk registers, heat maps, and the various committees that supposed to meet monthly. What you likely do not know is how much of that never makes it past the first year. Most programs collapse under their own paperwork weight. The ones that survive tend to be the ones that stop trying to be comprehensive and start being operational.
Why Enterprise Risk Management For Dummies Still Matters
The For Dummies branding works here because the actual concepts are straightforward. Risk identification, assessment, mitigation, monitoring, reporting. Five steps. Everyone can understand them. The reason they fail in enterprise settings is not complexity. It is organizational friction. Different departments use different definitions of risk. Finance thinks in monetary terms. Operations thinks in process terms. IT thinks in availability terms. When you try to consolidate those into a single framework, something always breaks. I learned this the hard way during a merger integration where the acquired company used qualitative risk ratings on a five-point scale and our internal system used a seven-point scale tied to financial materiality thresholds. They were not compatible. Neither was wrong. They just meant that a "high" risk in one system could be a "medium" risk in the other, and the board-level dashboard ended up showing a consolidated picture that was mathematically meaningless. The workaround was to build a mapping table at the control level rather than at the risk level. Controls are the common denominator. Every risk, regardless of how it is defined or rated, traces back to specific controls that manage it. We mapped both rating systems to the same control inventory, ran the merged dataset through a unified risk calculation, and only then produced the consolidated view. It took about two weeks of focused work and eliminated the next six months of reconciliation headaches.
The Operational Framework
Start with your control inventory before you try to build a risk model. This is counterintuitive for most people entering the field. They want to identify risks first, then find controls to address them. But if you start with risks, you will either miss things or overidentify. Controls are the anchor. They are concrete. You can point to them. You can test them. You can measure their effectiveness over time. A typical control library for a mid-sized financial services organization runs between 400 and 900 individual controls. From there you link each control to the risks it addresses using inherent risk scores. The inherent risk score represents the level of risk before any controls are applied. This is where most frameworks get fuzzy. People confuse inherent risk with residual risk. Inherent risk is what the risk looks like in a vacuum. Residual risk is what remains after controls. The difference matters enormously when you are trying to justify budget requests to a CFO. Here is a nuance that beginners consistently miss: inherent risk is not a static number. It changes when your business environment changes, even if your controls have not changed at all. I had a client who filed a routine risk assessment showing that their payment processing risk had dropped from high to medium because they had implemented new reconciliation controls. The risk committee approved the rating change. Two months later, a new regulation came out that imposed stricter transaction monitoring requirements on that same payment flow. Their inherent risk had actually increased, but their assessment still showed it as medium. The controls had not changed. The environment had. Their risk rating was now wrong, and nobody had caught it because they only reassessed when controls changed. This happens constantly. Budget cycles, regulatory changes, product launches, M&A activity, geographic expansion. Any of these can shift inherent risk without touching a single control.
Get the Full Details
Risk Appetite and Tolerance
The most abused concept in enterprise risk management is risk appetite. Boards love to declare a risk appetite statement. They write things like "we accept low risk in operational integrity and moderate risk in revenue growth." These statements sound authoritative. They are almost always useless because they are not quantified. What does low risk mean? What is the numerical threshold? Without numbers, risk appetite is just corporate poetry. The fix is to attach quantitative tolerance levels to each risk category. Financial risk: no more than 2% of quarterly revenue in unexpected losses. Operational risk: no more than three material incidents per year exceeding $500,000 in direct costs. Technology risk: no more than four hours of unplanned downtime per month for critical systems. These numbers do not need to be perfect. They need to be real numbers that the organization would actually respond to if breached. A risk appetite statement that says "we will not tolerate fraud" means nothing. A statement that says "any single fraud incident exceeding $100,000 triggers an immediate board notification and external audit" means something. I have seen risk committees spend three months debating the wording of an appetite statement and zero minutes discussing what actions would trigger when that appetite is breached. The result is a document that looks good in an annual report and changes nothing about how the organization actually behaves. This is the single biggest waste of time I have observed in ERM programs.
The Risk Register Problem
The risk register is where most ERM programs go to die. A typical enterprise risk register contains 200 to 500 risks. Most of them are duplicates, vaguely worded, or so abstract that no one knows what action they require. I reviewed a risk register once that listed "cybersecurity risk" and "data breach risk" as two separate line items. Another listed "employee turnover" and "loss of key personnel" separately when they were clearly the same risk with different labels. The person who built it had no understanding of MECE principles or basic taxonomic discipline. A well-maintained risk register for a company of 500 to 2,000 employees should contain between 30 and 60 risks. Not 300. Thirty to sixty. Each one should be specific enough that you can name the owner, the current controls, the residual risk rating, and the next review date. If a risk entry requires more than two sentences to describe, it is probably too broad and should be split into component risks. The process for maintaining this is simpler than people think. Quarterly risk reviews where each risk owner presents their top three risks, current control effectiveness, and any changes in risk profile since the last review. No elaborate scoring models. No complex algorithms. Just a conversation between the risk owner and the ERM function about whether the current assessment still holds. This usually takes about 20 minutes per risk owner. For a team of ten risk owners, that is two hours of work per quarter. Compare that to the typical approach where a centralized team spends 40 hours per quarter trying to collect and reconcile risk data from every department, and the difference is staggering.
Third-Party Risk
This is where most ERM programs have the biggest blind spots. Third-party risk assessments are routinely handled by procurement teams who use a standardized questionnaire that was designed fifteen years ago and has not been updated since. The questions ask about ISO certifications and disaster recovery plans. They do not ask about the subcontractor the vendor uses for cloud hosting, or the geographic concentration of the vendor's data centers, or the vendor's own cybersecurity insurance coverage. You will not know about these things until something goes wrong. The practical workaround is to require a tiered risk assessment based on the criticality of the relationship, not just the dollar value. A $50,000 vendor that provides a specialized compliance monitoring tool with access to sensitive customer data is riskier than a $2 million vendor that provides office supplies. I implemented a simple scoring matrix that weighted three factors: data sensitivity, operational criticality, and regulatory exposure. Vendors scoring above a certain threshold received enhanced due diligence including third-party security audit reports and contractual right-to-audit clauses. Vendors below the threshold received standard questionnaires. This reduced the number of vendors requiring deep assessment from 80% to about 25% of the total vendor population while actually improving risk coverage. The previous approach had been spending disproportionate effort on high-spend vendors regardless of actual risk profile.

Regulatory Mapping
One of the most valuable functions of an ERM program is regulatory mapping. Most organizations face requirements from multiple regulators: SEC, FINRA, OCC, state attorneys general, GDPR authorities, etc. Each regulator has its own expectations for risk governance. Mapping your controls to these requirements creates a compliance overlay that serves two purposes. It ensures you meet regulatory obligations. It gives you leverage when a regulator asks why a particular control exists, because you can trace it directly to a specific regulatory requirement rather than saying "because our risk framework says so." The problem is that regulatory landscapes change frequently. A control that satisfied an examiner in 2022 may not satisfy the same examiner in 2024 after a new guidance document is published. I maintain a living mapping document that tracks each control against its regulatory source, the date of the source document, and the next expected update cycle. When a regulation changes, I can immediately identify which controls are affected and prioritize remediation accordingly. This typically takes about 30 minutes per regulatory change. The alternative is scrambling after an examination finds a deficiency, which takes about 300 hours.
When ERM Does Not Work
Enterprise risk management fails in several specific scenarios and it is important to know them before you invest in a program. It does not work in organizations where executive leadership treats risk as a compliance function rather than a decision-making function. If the CEO and CFO do not actively use risk data in strategic decisions, the ERM program becomes a ceremonial exercise. It also does not work in organizations that expect ERM to predict the future. Risk management is about managing known uncertainties and identifying emerging risks. It cannot predict black swan events or prevent well-concealed fraud. A program that promises otherwise is selling something it cannot deliver. Another failure mode is when risk assessments are treated as annual checkboxes rather than continuous processes. The risk landscape changes continuously. An annual assessment produces a snapshot that is already stale by the time it is finalized. The most effective programs I have seen combine annual formal assessments with monthly risk monitoring dashboards and quarterly deep dives on the top five risks. This keeps the program alive year-round instead of concentrating all the effort into a single frantic period each December.
Getting Started
If you are building an ERM program from scratch or revitalizing a failing one, start with three things. First, secure executive sponsorship that goes beyond a signature on a policy document. The sponsor needs to actively reference risk data in leadership meetings and require risk considerations in strategic planning sessions. Second, build a simplified control inventory for your highest-risk areas only. Do not attempt to map every control in the organization. Start with the three or four areas where a failure would cause material financial, regulatory, or reputational damage. Third, establish a basic risk appetite framework with quantified tolerance levels for those same high-risk areas. Everything else can follow. Risk registers, committee structures, reporting dashboards, third-party risk programs, crisis management plans. They all depend on the foundation of executive engagement, a manageable control inventory, and quantified risk appetite. Without those three elements, you are building on sand regardless of how sophisticated your tools and processes appear. There is no downloadable template that will solve this for you. The frameworks exist in public domain documents from COSO, the Basle Committee, and various regulatory bodies. What you need is the discipline to adapt them to your actual operating environment rather than copying them verbatim. The organizations that get this right are not the ones with the most elaborate systems. They are the ones where risk data actually influences decisions. Everything else is overhead.