Using the Essential 8 Assessment Tool Without Losing Your Mind
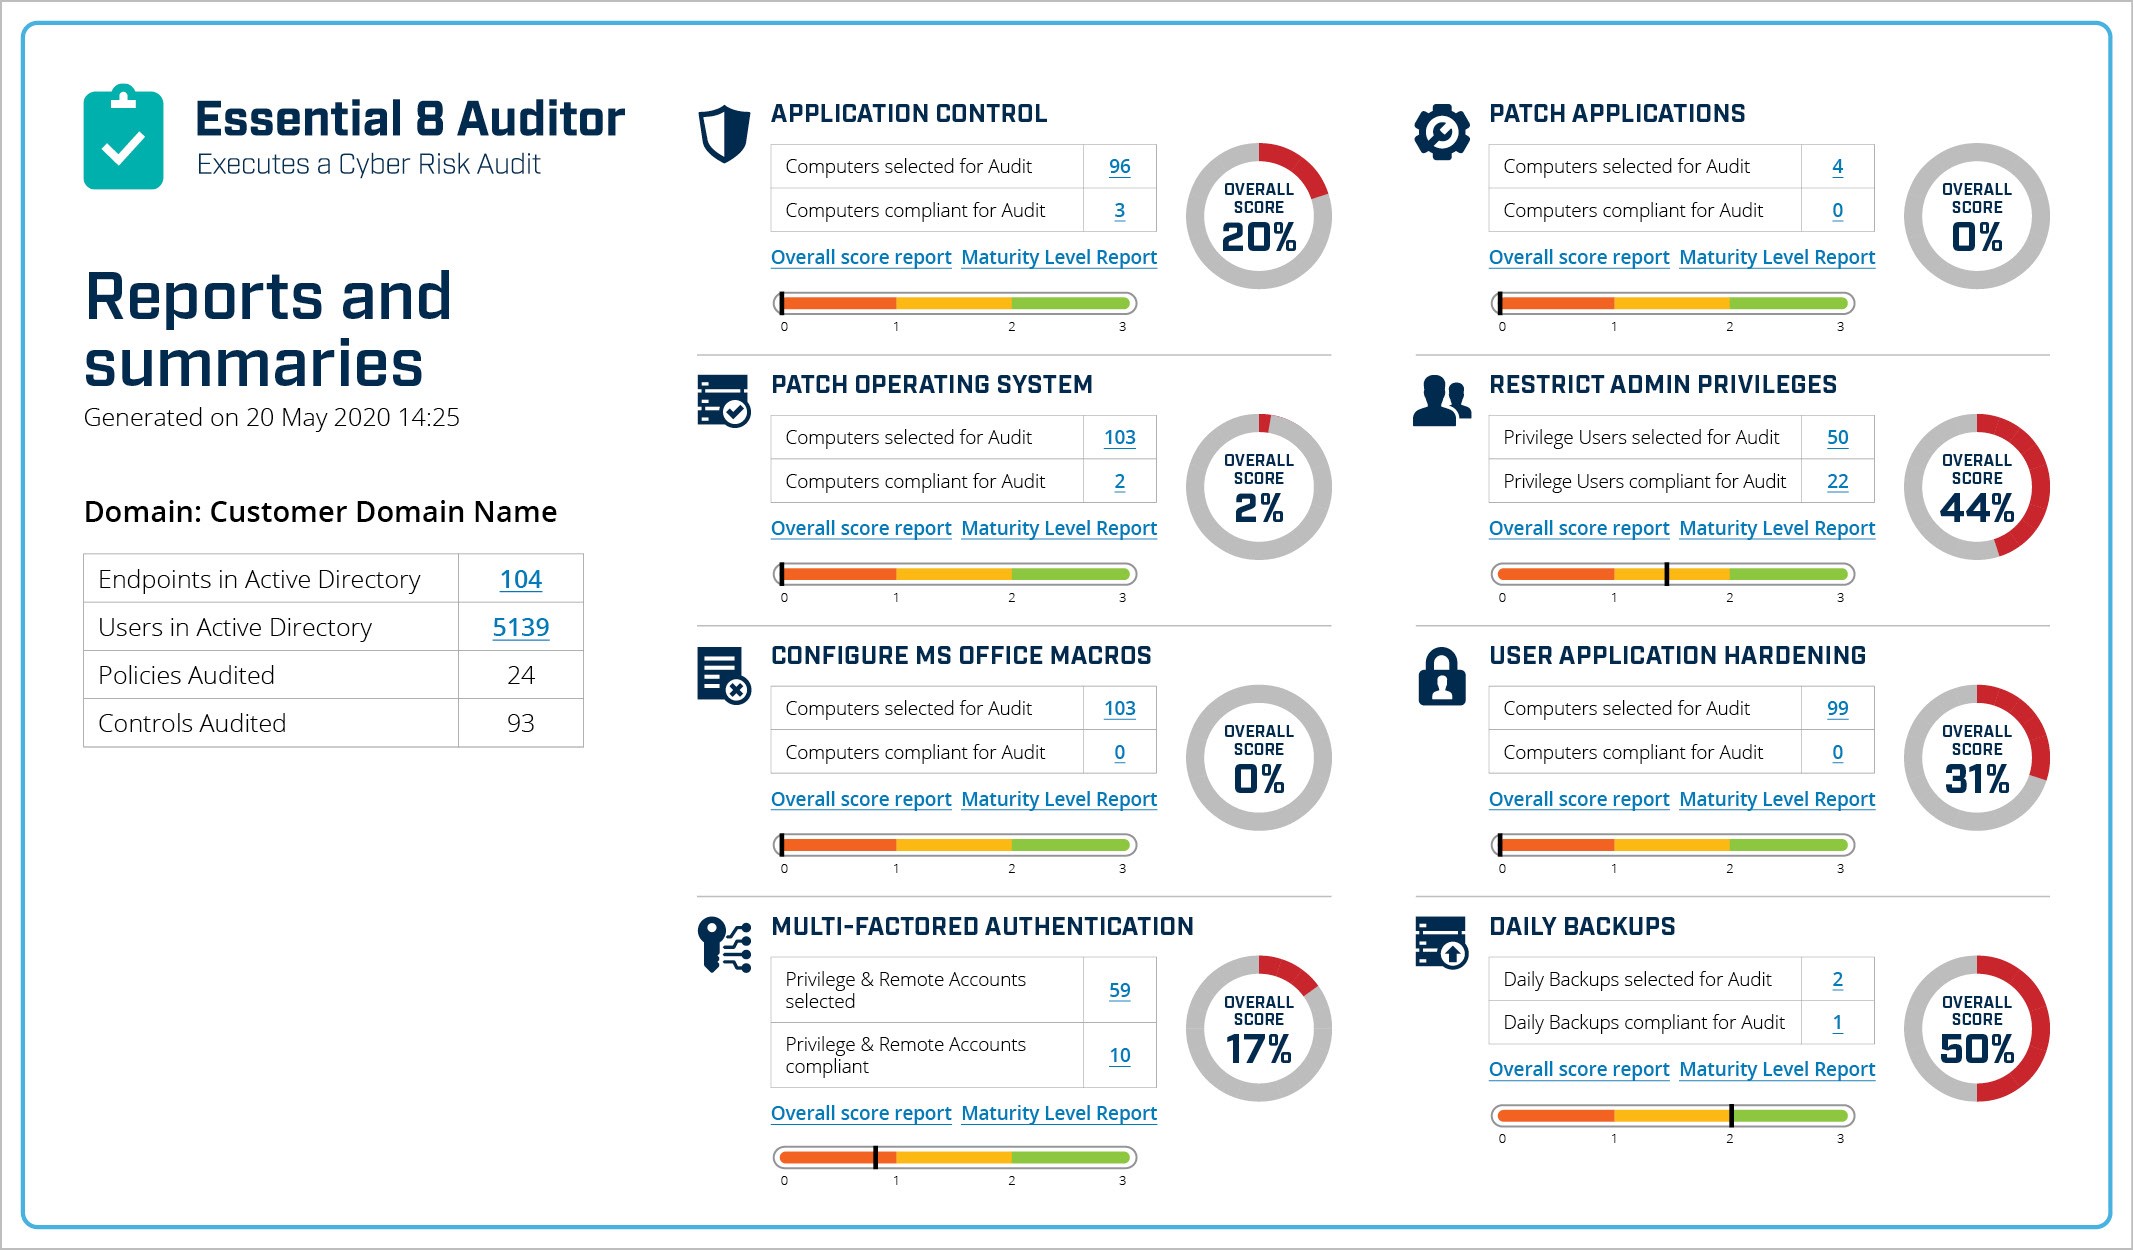
The Essential 8 Assessment Tool is a free web-based calculator provided by the Australian Cyber Security Centre. It asks you a series of questions about your organisation's security controls and returns a maturity score for each of the eight mitigation strategies. Nothing spectacular about the interface, but it forces you to look at things you would normally skip over. I've run this assessment for roughly half a dozen organisations now, usually as part of a broader security posture review. The process takes anywhere from two to eight hours depending on how clean your data is. If you haven't got a proper asset register, an accurate software inventory, and a documented patching policy before you open the tool, expect it to take the long end of that range.
Getting Started With the Essential 8 Assessment Tool
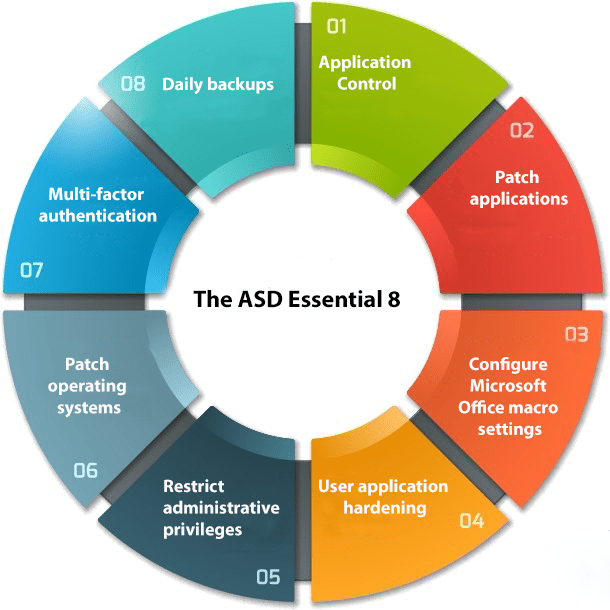
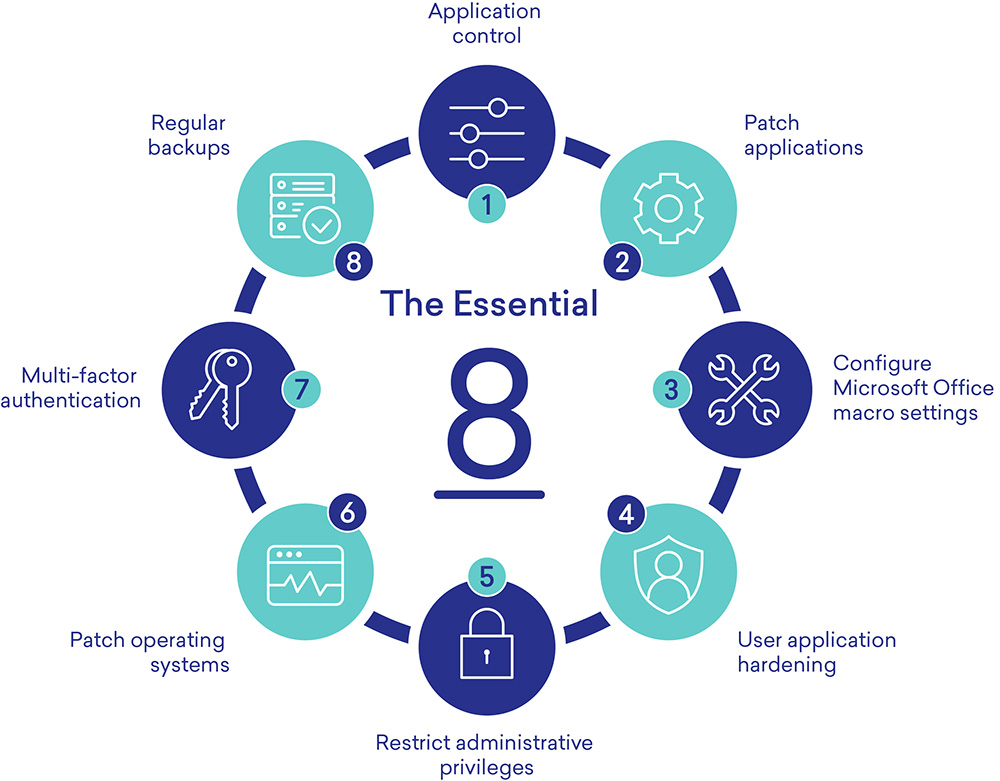
You can access the current version at essential8assessment.cyber.gov.au. It requires no login, no installation, and no payment. You enter your organisation details, answer configuration questions for each of the eight strategies, and the tool calculates your maturity level across four tiers for each strategy. Here is how the eight strategies break down in practice, with the things that actually trip people up: 1. Restrict application privileges (L1) — Most tools claim compliance here. That doesn't mean much. I had a client once who was using Group Policy to restrict local admin rights, but they had over four hundred exceptions baked into their GPO because "the old ERP system needs it." The tool caught this immediately and pushed their maturity score down to Level 1 for the entire strategy. The workaround was not adding more exceptions but migrating that ERP onto a virtualised environment with tighter controls.
2. Patch applications (L2) — This is where most organisations fail their first assessment. Not because they don't patch, but because they cannot demonstrate that every application on every endpoint was covered within the timeframe the strategy requires. The evidence you need is a ticketing or patch management log with timestamps. If you rely on IT staff "just knowing" what was patched last Tuesday, you are not going to make Level 2. 3. Patch operating systems (L3) — Similar story, different scope. Windows Update, SCCM, Intune, Jamf — whatever you use, the tool will verify that the patch cadence matches the maturity level you're claiming. A common pitfall is having strong automated patching on workstations but deliberately exempting server builds. That gap is visible and it drags the score down. 4. Multi-factor authentication (L4) — By Level 4 this strategy requires MFA on every endpoint and external service, including RDP. The hard part isn't deploying it. It's the edge cases: legacy VPN concentrators that don't support it, third-party vendors with their own login portals, and API keys that bypass authentication entirely. I once spent three weeks chasing down every integration point a mid-size hospital had before we could legitimately claim Level 4 for this strategy.
Get the Full Details
5. Browser hardening (L5) — This one gets ignored until ransomware hits. The assessment asks about content delivery rules, macro restrictions, and browser-based attack surface reduction. Most organisations run browsers with nothing but the default settings. Implementing even basic hardening here — disabling ActiveX, restricting Java, using application control policies — usually moves the needle from Level 1 to Level 2 quickly. 6. Application control (L6) — This is arguably the hardest strategy to get right because it requires whitelisting rather than blacklisting. The tool distinguishes between Level 6 (Windows Defender Application Control or AppLocker on all endpoints) and Level 7 (same but extended to network devices and servers). Many security teams aim for Level 6, find that their line-of-business applications break under the policy, and then spend months tuning before they can credibly claim compliance. 7. Macro restrictions (L7) — Disabling all Office macros except digitally signed ones. Simple in theory. In practice, organisations discover that their accounting software, their document management system, and their internal reporting tools all rely on unsigned macros. The audit trail for each exception matters here, and you need to prove that every macro is reviewed and approved. We found a procurement workflow using VBA macros that nobody had documentation for. Took two weeks to map it out and get it signed.
8. Logging (L8) — The final strategy covers event logging for user authentication, process execution, and network activity. The maturity levels here demand increasingly granular logging with centralised retention. The bottleneck is almost always log storage capacity and the ability to correlate events across multiple sources. A standard SIEM setup from three years ago usually falls short of Level 8 requirements without upgrading. One thing the tool does not do well is account for specialised environments. If your infrastructure is heavily Linux-based, or you run legacy IBM mainframes, or you operate in an SCIF environment with air-gapped systems, several of the Essential 8 strategies simply don't map cleanly. The tool will still ask you to score yourself, but the maturity levels it suggests may be unrealistic for your architecture. In those cases, I recommend supplementing the assessment with the ACSC's Infrastructure Sector guidelines, which provide mapped alternatives for non-Windows environments. The output you receive after completing the assessment is a PDF report with your maturity levels for each strategy and a combined overall score. It's useful for board-level reporting and for demonstrating progress against the Essential 8 over time. Running the same assessment six months apart and comparing the PDFs gives you a reasonably honest picture of where your security posture is moving.
The biggest mistake I see is treating the assessment as a one-off compliance exercise rather than a roadmap. The tool's real value isn't the score. It's the process of answering each question and discovering what you don't know about your own environment. That discovery phase is usually where the actual improvements happen.