Working Through CISSP Exam Questions That Actually Help You Pass
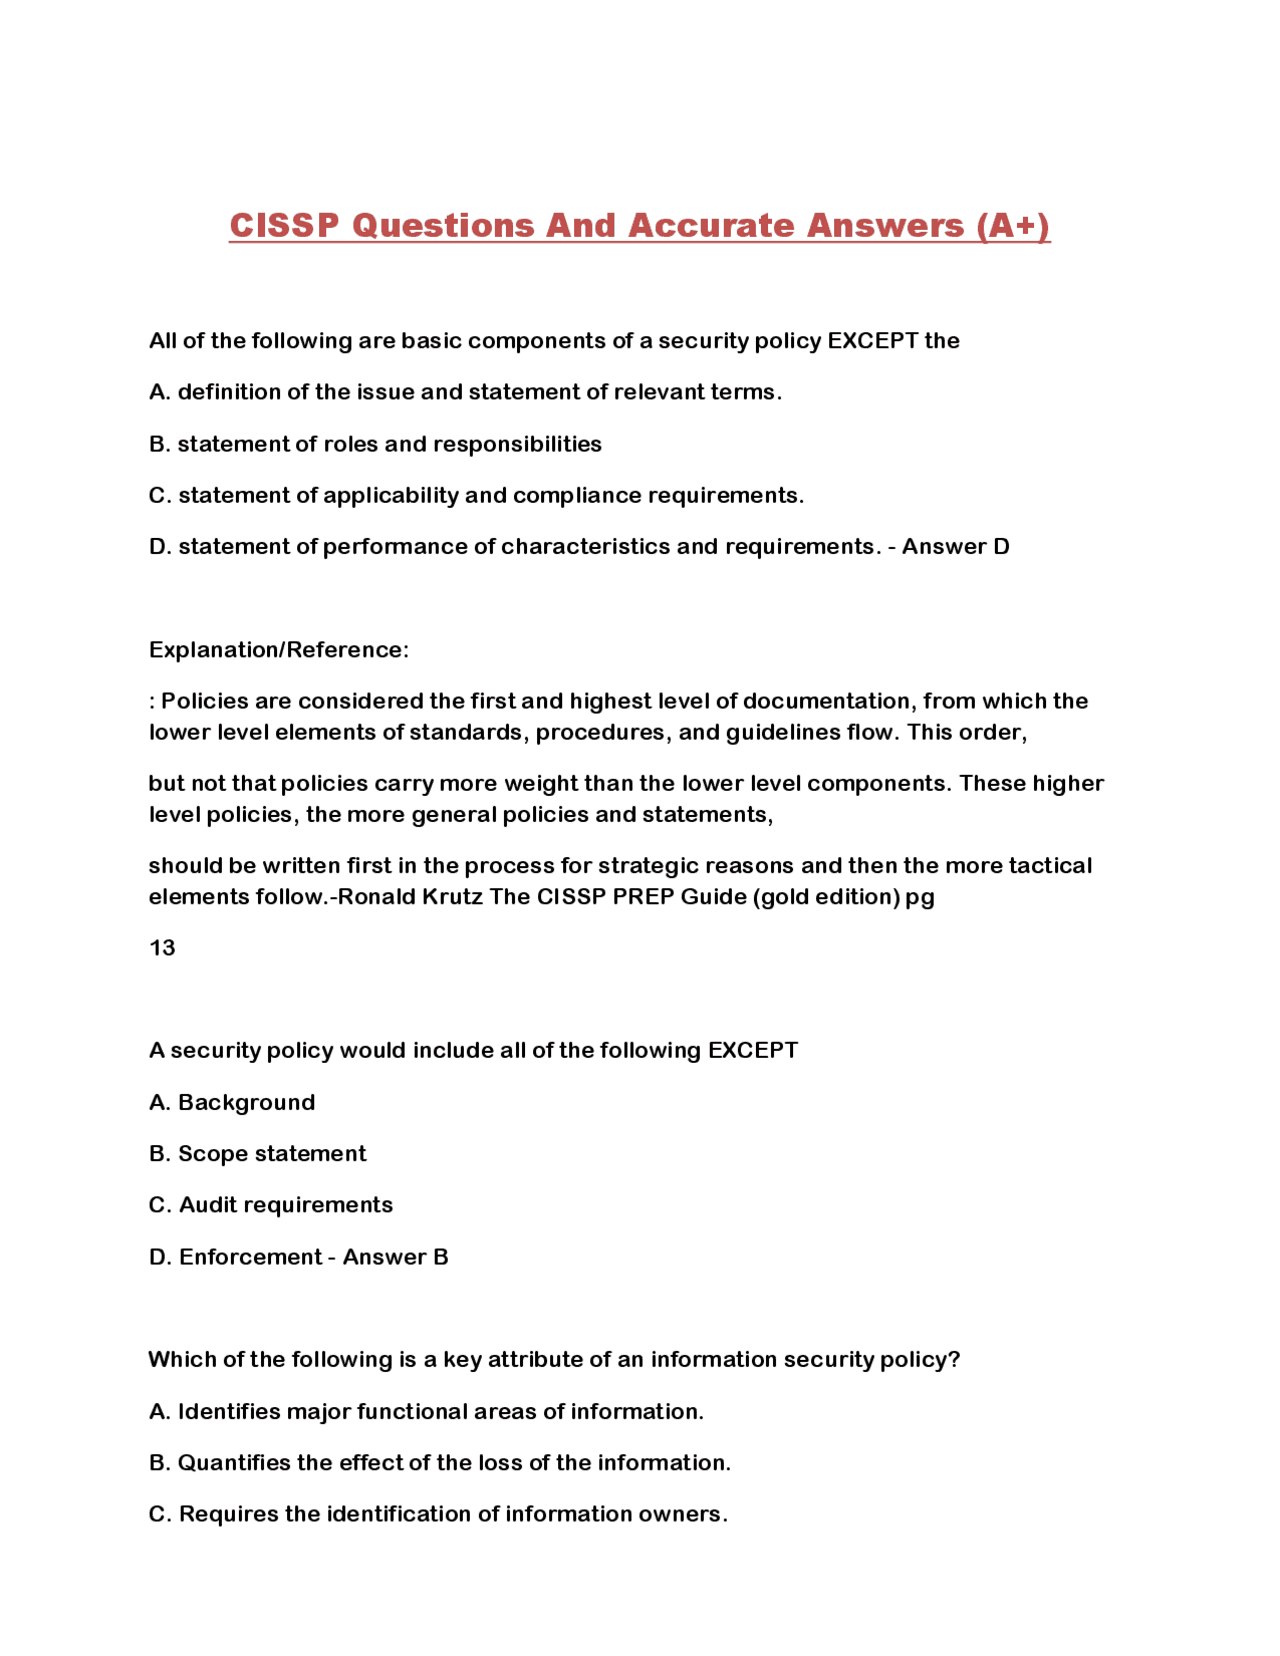
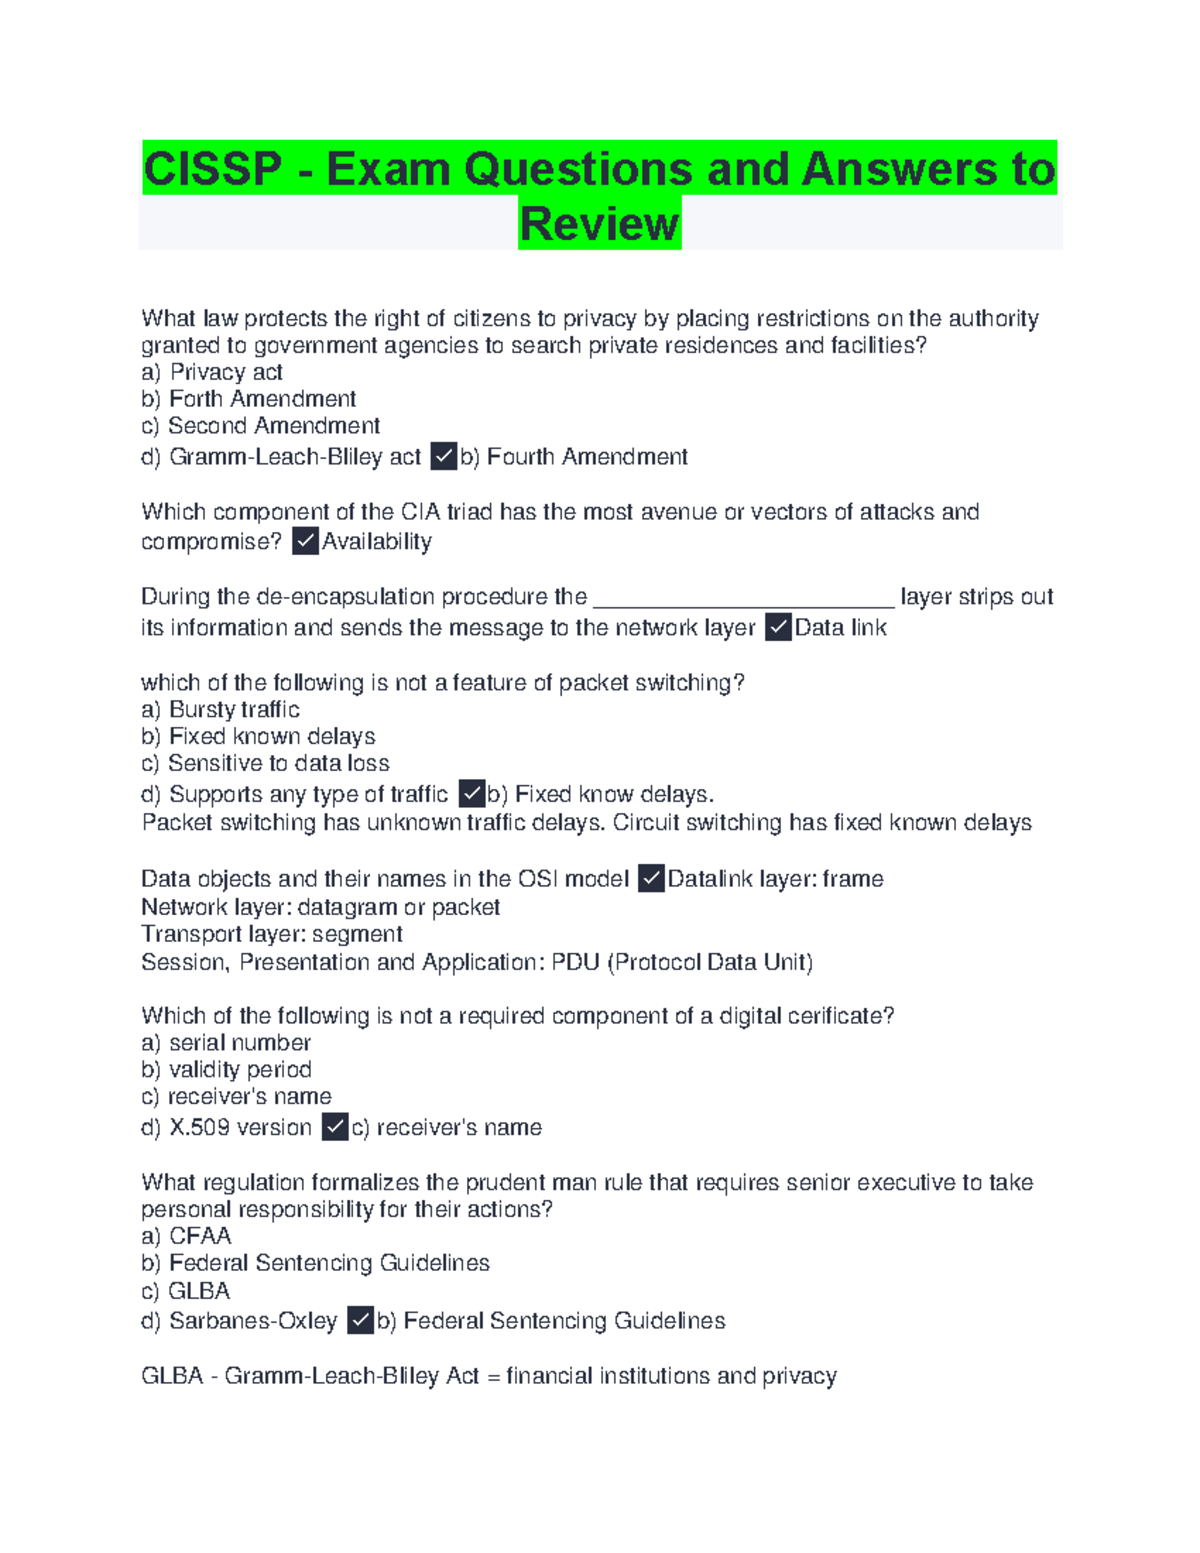
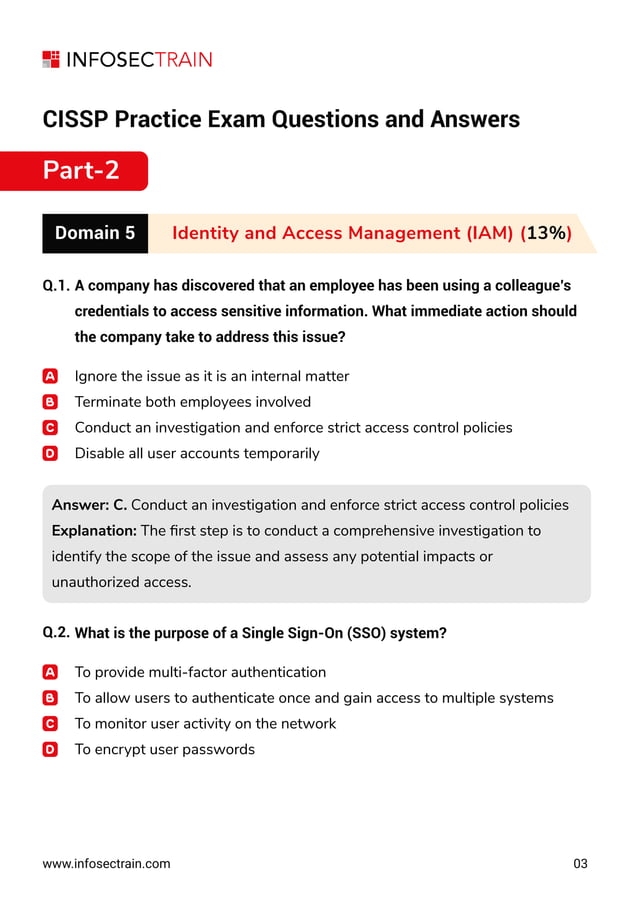
I've been around the CISSP long enough to know that most people fail the exam not because they don't know the material, but because they never learned how the questions actually work. The (ISC)² question style is its own dialect, and there's a real gap between knowing cybersecurity and being able to pick the right answer when four options all look defensible. This is about bridging that gap with Example Cissp Exam Questions and similar practice material. The best prep questions aren't the ones that test whether you can recall a definition. They're the ones where you have to decide what a security manager should do first, even though you personally would handle it differently. I worked through a set of practice questions last year while prepping a junior analyst for his attempt, and we hit one that still comes to mind. The scenario described a company that had just discovered a zero-day vulnerability in their web application framework. The options were things like patch immediately, notify stakeholders, assess business impact, and update the risk register. The right answer was assess business impact, and my analyst kept choosing "patch immediately" because that's what he'd do in his SOC shift. It took us about forty-five minutes of back-and-forth before he grasped why the exam wanted the manager's perspective instead of the technician's instinct. That exercise used a collection of Example Cissp Exam Questions pulled from a widely circulated dump, and the discussion around each wrong answer ended up teaching him more than any flashcard ever did. Here's what I found about making that kind of material actually useful instead of just a memorization exercise.
How to Use Practice Questions Without Wasting Your Time
The problem with most CISSP prep materials is that they look like the exam but aren't. A genuine (ISC)² question forces you into the role of a generic manager, not a hands-on specialist. It asks what you should do, not what is technically correct. When you're working through Example Cissp Exam Questions, the single most important habit is reading every option before committing to an answer, because the first one that looks right is often the trap. Here's a practical breakdown of how I structure my practice sessions. Phase one is raw attempt without notes. You go through a block of questions, pick an answer for each, and move on. Don't check the explanation yet. This gives you a baseline of where your instincts land and what patterns you keep falling into. Most people are surprised by how many questions they get wrong on the first pass, even after studying for months.
Phase two is explanation analysis. Now you read every rationale, correct and incorrect alike. The key is understanding why each wrong answer exists. (ISC)² writers include distractors that are technically valid in some contexts, which is what makes these questions hard. If an option says something like "consult the policy first," it's wrong only because the scenario implies an immediate action override or because a different step logically precedes it. The explanation will usually tell you the ordering logic. Phase three is pattern tagging. I keep a simple spreadsheet with columns for question domain, my initial wrong answer, the correct answer, and the reasoning gap. After fifty questions, the gaps start clustering. You'll see that you consistently pick the technical answer over the managerial one, or that you keep choosing the most dramatic option when the exam wants the most measured one. This is where the real learning happens.
Get the Full Details
Domain-Specific Pitfalls I've Seen Repeatedly
Some domains of the CISSP exam have recurring traps that show up in almost every high-quality question bank, including those circulating under labels like Example Cissp Exam Questions. Security governance and risk management is where most people lose the most points. The exam wants you to think about alignment with business objectives, not about implementing the best technical control. If a question presents a scenario where you could spend six months building a perfect risk assessment framework or take two weeks to get leadership buy-in on a simplified version, the answer is always the latter. (ISC)² considers stakeholder engagement a prerequisite for anything else in that domain. I learned this the hard way on my own attempt — I chose the thorough approach on three straight governance questions and spent the rest of the exam second-guessing every managerial decision. Software development security has a trap where the answer involves the earliest phase of the SDLC, not the most technically complete one. If a question asks how to reduce defects in a new product line, the correct answer is often "add security requirements during initiation" rather than "implement SAST/DAST tools" or "conduct a code review." The exam treats requirements as the highest-leverage intervention, even though in practice most teams treat security as something to bolt on later. I've seen this exact pattern in nearly every sample set of Example Cissp Exam Questions, and it's one of the most consistent themes across the entire exam.
Incident response questions follow a strict sequence: detection and analysis, containment, eradication, recovery, and post-incident activity. People keep picking containment answers when the question actually describes a scenario where containment is impossible without first understanding the scope. The correct answer in those cases is always the preceding step. I worked through a specific example recently where the scenario involved ransomware spreading across file servers, and the options included "isolate the infected segment," "restore from backup," and "identify the initial access vector." The right answer was identifying the initial access vector because containment decisions depend on knowing the blast radius, which you can't determine without that analysis. That single question changed how I approach every incident response item afterward.
Where Practice Materials Fall Short
I need to be honest about what these resources can't do for you. First, no collection of Example Cissp Exam Questions can replicate the adaptive difficulty of the CAT format. The computer-adaptive test adjusts question difficulty based on your performance in real time, and that means the last twenty questions you see are structurally different from the first twenty. Most prep materials present everything at a single difficulty level, which gives you a false sense of readiness. Second, the actual exam includes performance-based items that don't appear in any question dump. These are simulation-style tasks where you configure a firewall rule, classify data sensitivity, or prioritize remediation actions. If your prep consists entirely of multiple-choice practice, you'll walk into those items unprepared regardless of how many Example Cissp Exam Questions you've worked through. Third, and this is the part most prep courses won't tell you: the exam tests your ability to think like a generic manager, and that mindset is hard to fake. You can memorize the ordering of incident response steps or the hierarchy of security controls, but when a question puts you in a genuinely ambiguous scenario with incomplete information, the "right" answer often feels wrong because it contradicts what you'd actually do on the job. I've had colleagues who scored above eighty percent on practice exams and still failed the real thing, simply because the practice questions were too clean and too well-scoped compared to what (ISC)² actually writes.

If you're serious about this exam, the best supplemental resource isn't another question bank. It's reading the official (ISC)² CBK guide chapter by chapter and doing the end-of-chapter review questions, because those follow the same authorship patterns as the actual exam. The third-party dumps, including those labeled Example Cissp Exam Questions, are useful for volume and pattern recognition but should never be your primary study source. Use them for the final two weeks before the exam, not for the first two months.
A Practical Study Sequence
Here's the order I recommend, based on what actually moved the needle for me and the people I've mentored. Start with the (ISC)² official study guide. Read one domain per week. Take the end-of-chapter questions seriously, even the ones you get right, because the explanations reveal the exam's internal logic. After finishing the guide, move to a commercial question bank and do timed blocks of twenty-five questions, reviewing every rationale thoroughly. Once you've completed two full passes through a question bank, start the pattern-tagging exercise I described above. Identify your persistent gaps and go back to the CBK chapters that cover those domains. Then do a second timed run, this time focusing on speed and the managerial lens. If your scores plateau, switch to the official (ISC)² practice exam if you have access to it, because that's the closest thing to the real CAT experience available.
The timeline for most people working full time is about ten to fourteen weeks. Anyone claiming they passed with two weeks of prep either already held the knowledge from years of management experience or got lucky with a low-difficulty exam form. Don't optimize for shortcuts. Optimize for building the right decision-making habit. I've watched people burn through dozens of question banks without improving because they were treating every question as a test of knowledge instead of a drill in perspective-taking. The CISSP is not a knowledge exam. It's a judgment exam disguised as one. Once you stop trying to prove you know the material and start practicing how a generic security manager would think through each scenario, the questions stop feeling like traps and start feeling like conversations you're already fluent in.