What Actually Happens When You Do a Facility Security Assessment
A lot of people treat facility security assessments like a box-checking exercise. They fill out a template, take some photos, and call it done. That approach misses the things that actually matter. A proper Facility Security Assessment Checklist isn't about the form itself. It's about understanding what you're looking for, where people cut corners, and why the results often don't match reality until an incident forces the gap open. I ran assessments for a mid-sized distribution campus once — three buildings, about 400 employees, mixed-use with warehouse and light office space. The template we were given covered cameras, locks, access control, lighting, and visitor logs. Standard stuff. We found every single item on paper. The actual vulnerability was something that didn't appear anywhere in the checklist. A service door that looked hardened — reinforced frame, deadbolt, magnetic lock — had been propped open with a cinderblock during a loading dock shift. The camera above it was angled correctly, but the recording was overwritten every 24 hours because someone had changed the retention setting from 30 days to 1 day. Nobody reviewed the config. The checklist asked if cameras existed. It did not ask if they were configured to capture anything useful.
How to Build a Facility Security Assessment Checklist That Actually Works
Start with physical access layers, not individual devices. Most checklists I see jump straight to door numbers and camera models. That's backward. You need to understand the sequence: perimeter, entry points, interior zones, and the spaces in between. A checklist that doesn't map those layers will produce a pile of disconnected observations instead of a coherent picture of how someone could actually get somewhere they shouldn't be. Here's what I use, broken into the sections that matter in practice: Perimeter assessment. This covers fencing, gates, landscaping, lighting, and any barriers between public space and the building. I check fence height and condition, gate locking mechanisms, clear zones around the perimeter (stuff growing into a fence or parked trucks sitting too close create blind spots), and whether exterior lighting meets the facility's stated standards. Street-facing side doors that aren't on the main route often get ignored. They're usually the weak point.
Entry control points. Every door, loading bay, and access portal needs to be logged. I note the type of lock or electronic system, how it's used daily, whether tailgating is physically possible, and what happens during power loss. I also check the door hardware itself — hinges, strike plates, frames. A cheap hollow-core door in a brick building is worse than nobody realizes. The checklist should ask about the door assembly, not just the lock on it. Access control systems. This is where most assessments go soft. Yes, list the card readers and the controller. But also check who has administrative access, when credentials were last audited, and whether there are unused accounts from former employees. I found a case where a terminated employee's badge still worked because the access list was never updated after an offboarding process that had no checkpoint. The system was working exactly as designed. The process around it wasn't. Video surveillance. Beyond camera count and placement, check recording retention, camera angles during normal operations, blind spot coverage, and whether the NVR or storage system has its own physical protections. Cameras mounted on the outside of a server room are useless if someone can unplug the switch behind them. Also verify that camera timestamps are synchronized. Mismatched timestamps make incident reconstruction nearly impossible.
Get the Full Details
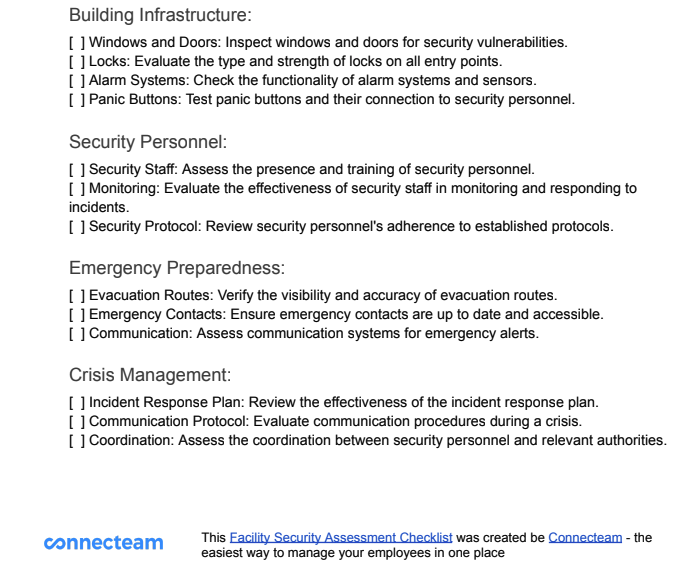
Interior access and zoning. Map the interior the same way you mapped the perimeter. Secure areas, restricted zones, mailrooms, server closets, break rooms that double as storage. I look for doors propped open, keys left in locks, and shared credentials between departments. A checklist item like "are restricted areas properly secured" is too vague. Specify: "are restricted area doors locked when unattended, and does the audit show any propped-open incidents in the last 30 days?" Lighting and visibility. Dark areas around a facility are a security problem even if the cameras cover them. Darkness invites behavior that cameras alone don't prevent. Check parking lots, walkways, side entrances, and the areas immediately outside perimeter doors. Measure foot-candles if you have a light meter. If you don't, at least note where shadows fall during typical shift changes. Utilities and infrastructure. Electrical rooms, HVAC units, data closets, generator pads. These are rarely on the checklist but are common entry paths. A roof access hatch with a basic padlock is a functional entry point. A basement door that opens into a crawl space behind the building is the same thing. The assessment needs to treat infrastructure as part of the security perimeter, not as background noise.
Procedures and human factors. This is the section people skip because it's harder to write down. How are visitors logged? Is there a verification step or just a signature? Are tailgating policies posted and enforced? Is there a process for reporting propped doors or suspicious activity? Check the actual logbook. Compare dates. Look for gaps where entries stop for a week or more. That usually means nobody is checking.
Things the Checklist Won't Tell You
The biggest blind spot in any facility security assessment is what happens during transition periods. Shift changes, deliveries, after-hours work, weekends. These are the times when security Posture degrades fastest and controls are least likely to be followed. I've seen facilities with excellent daytime compliance that completely fall apart after 5 PM. The fix isn't more cameras. It's figuring out who's actually present during those hours and whether they're following the same procedures. Another thing: checklists assume the facility is in its normal state. It rarely is. A construction project, a temporary reconfiguration, a new tenant moving in — these all change the threat model. If your assessment was done six months ago and a new doorway was added to the east wing, the old data is already wrong. Update or redo the section that's been modified. Don't assume nothing changed. There's also the problem of audit fatigue. After the third or fourth assessment, reviewers start seeing what they expect to see instead of what's there. I've caught myself skipping a door because I'd verified it the last two times. That's a failure of process, not judgment. The workaround is rotating who does the walkthrough and having someone else review the findings independently. Two sets of eyes catch more than one set of experts.

Limitations You Should Know About
A Facility Security Assessment Checklist will never give you complete coverage. It's a sampling tool. You can assess 80% of a facility in a day and still miss the one detail that matters. That's not a flaw in the method. It's the nature of physical security. You're measuring a dynamic environment with static snapshots. The checklist also rewards documentation over actual security. A facility with immaculate records but poor physical controls is easier to pass an assessment than a facility with decent controls and messy paperwork. Don't let the paperwork quality distract you from whether the actual locks, cameras, and procedures work when someone tests them. I once saw a facility score 94% on paper. A simple tailgate test at the main entrance showed that five people walked in without presenting credentials. The score was meaningless. Finally, assessments don't account for insider threats unless you build them to. The standard checklist assumes the threat is external. That's a reasonable default but an incomplete one. If your industry or facility size makes insider risk relevant, add credential audit trails, behavior anomaly flags, and access pattern analysis to the process. Otherwise you're only measuring one direction of vulnerability.
If you're looking for a downloadable version of the checklist structure I described above, I've kept a working copy that updates whenever I find gaps in the original. It's not a perfect tool. No checklist is. But it's better than the generic ones you find online, which mostly just list camera counts and door types without context.