Building Banking Infrastructure That Actually Survives Audit Season
Most people approaching Financial Institution Solutions treat it like a software procurement problem. Buy the right platform, configure the modules, tick the compliance boxes, and you are done. This is wrong. The architecture decisions you make in the first six months determine whether your institution can process transactions at 2am on a Tuesday during a regulatory examination, or whether your ops team is manually reconciling ledger entries by hand because the integration layer dropped a decimal. I spent three years implementing a core banking migration for a mid-market credit union. The module selection was straightforward. The data reconciliation took fourteen months. Not because of the code. Because the vendor documentation assumed a transaction class that does not exist in community banking, and their support team had never seen a reciprocal deposit with a time-of-credit window shorter than same-day.
What Financial Institution Solutions Actually Means in Production
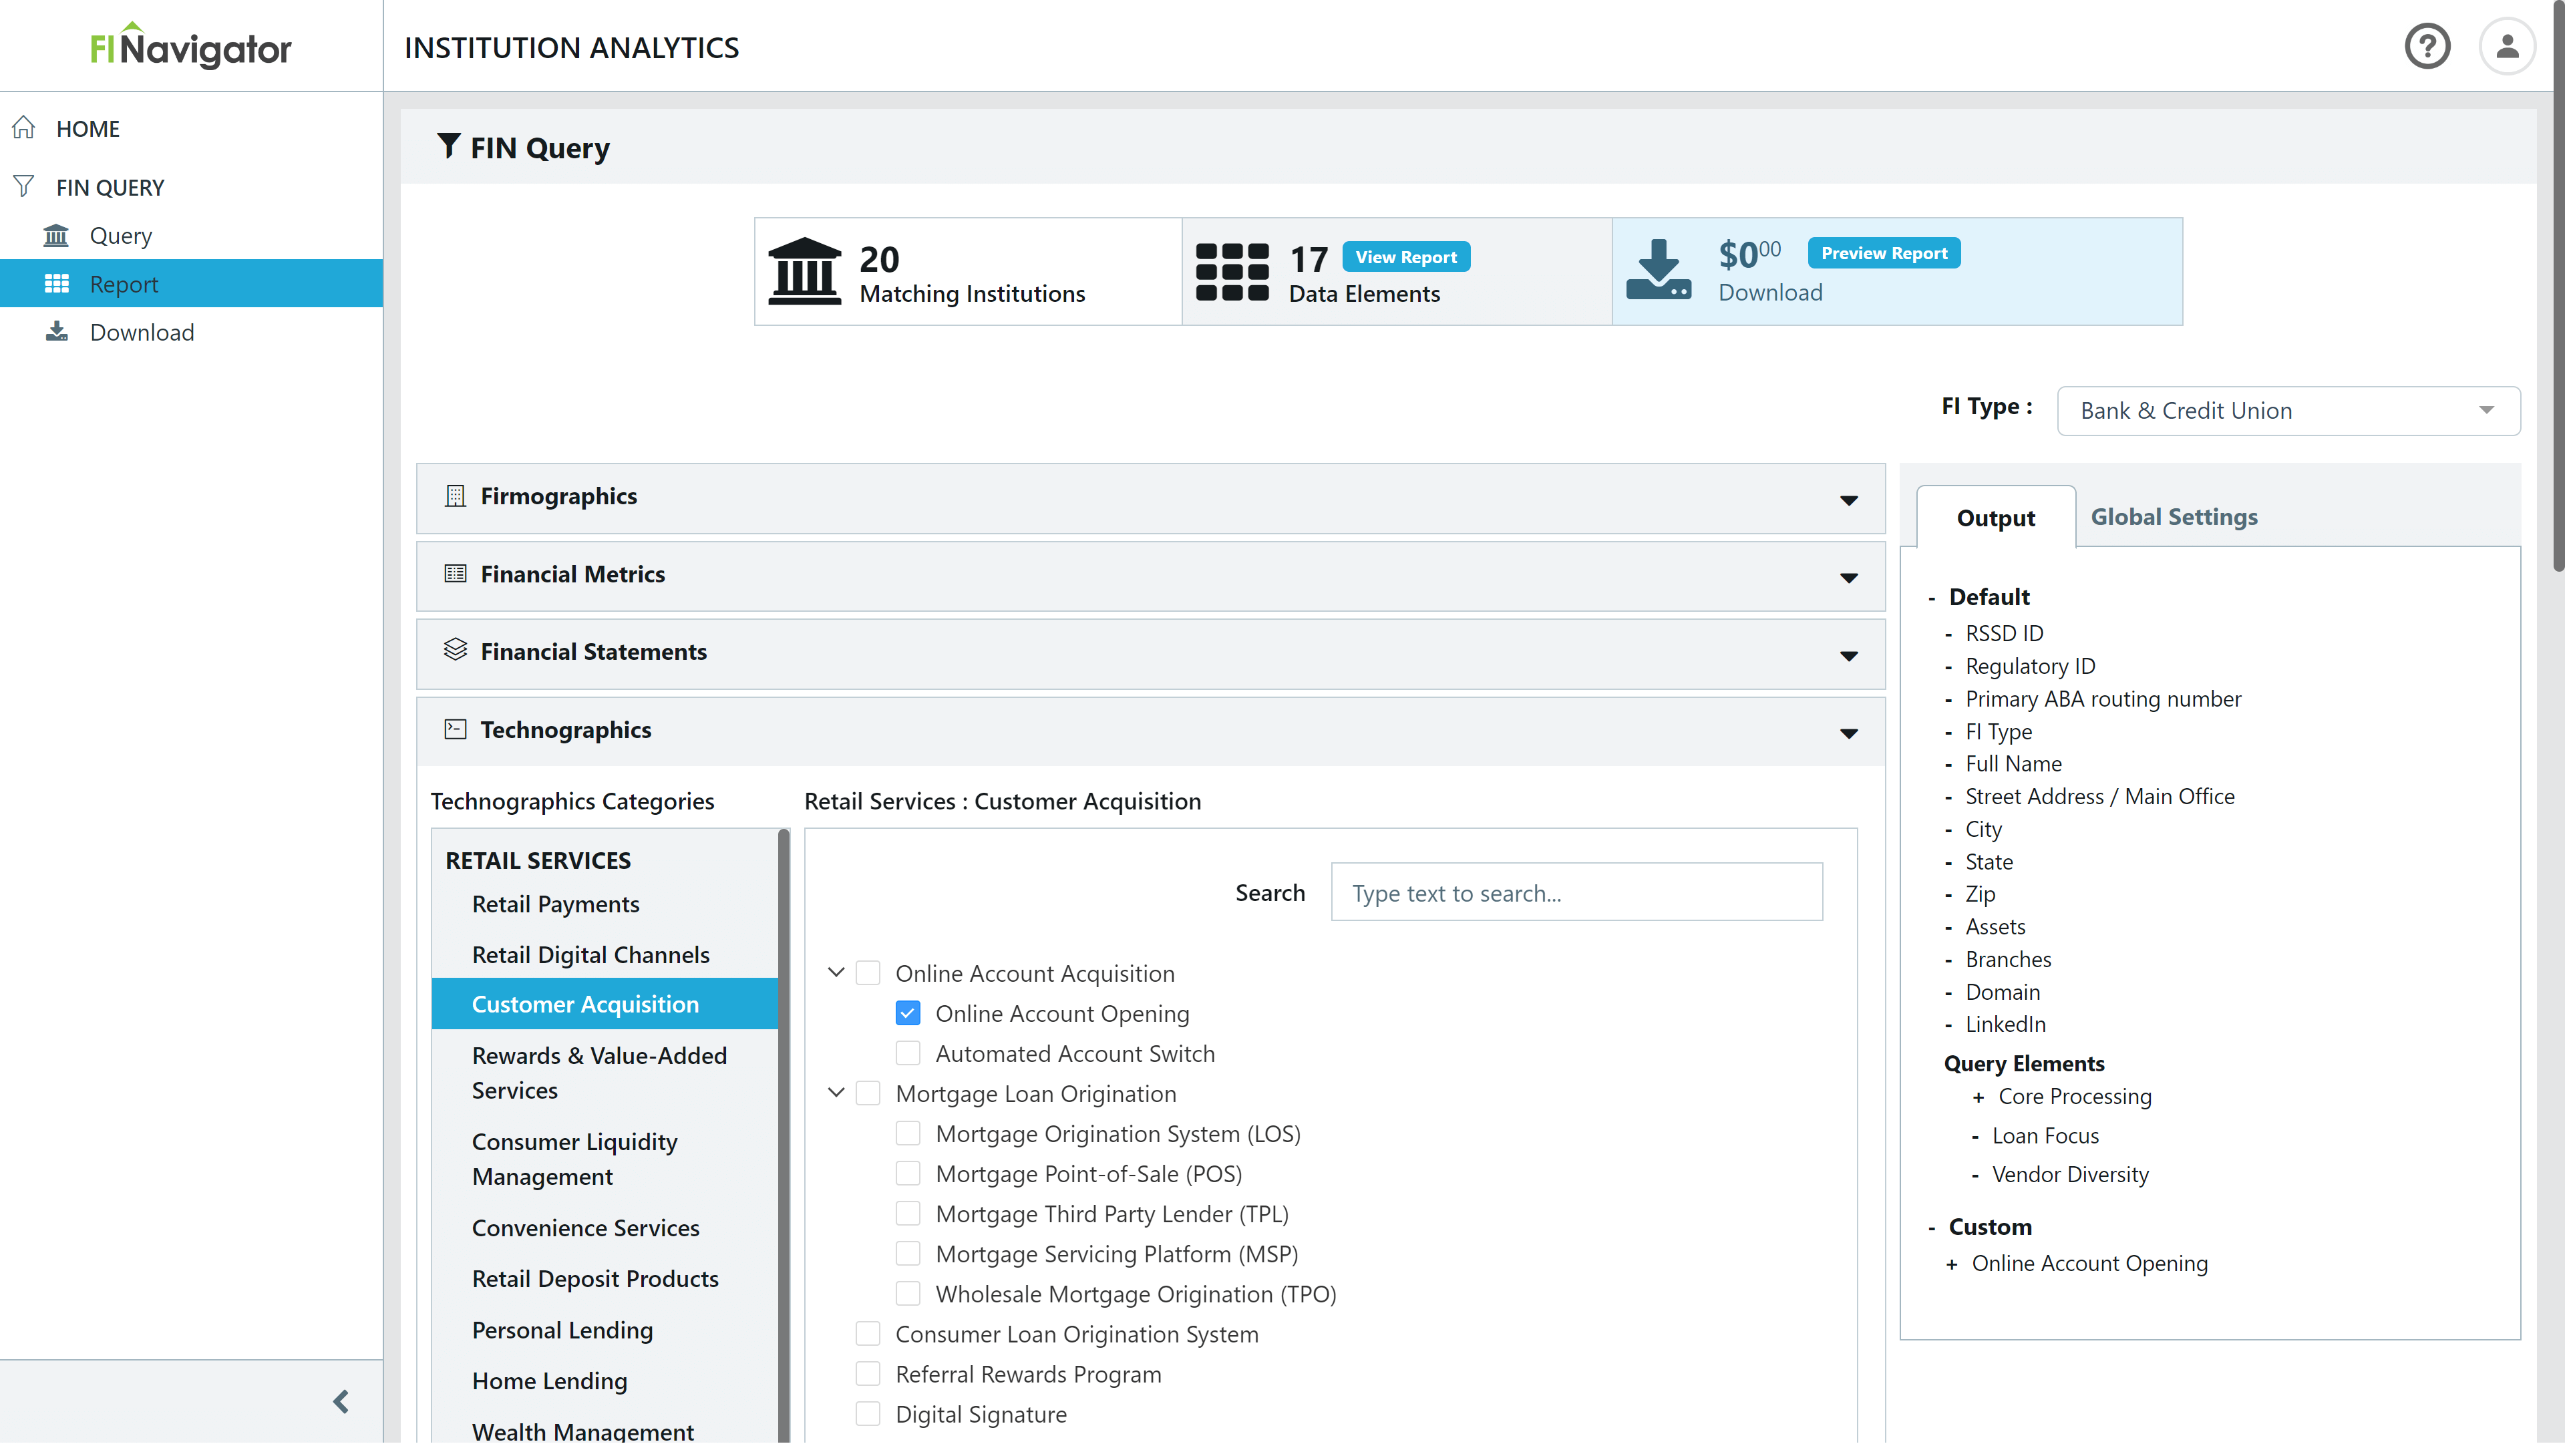
The term covers everything from core deposit systems and payment gateways to regulatory reporting engines and fraud detection pipelines. When I refer to Financial Institution Solutions, I am talking about the integrated stack that moves money, records ownership, calculates interest, and generates the paperwork regulators actually review. Most of these systems share a common failure mode: they work perfectly for the use cases they were designed for, and they break in ways you cannot predict when those use cases collide with real banking operations. A common misconception is that modular solutions are easier to manage. They are not. A best-of-breed approach with five different vendors means five different APIs, five different error formats, and five different SLAs. During our implementation, the loan origination system sent date stamps in ISO 8601 while the core banking system expected local time with a timezone offset embedded as metadata rather than a proper UTC field. We lost three weeks of development time before discovering the mismatch. The workaround was writing a custom adapter service that translated between the two formats and logged every discrepancy for the compliance team. The systems most institutions actually rely on fall into four categories. Core processing handles deposits, withdrawals, and account balances. Payment rails manage ACH, wire transfers, and card networks. Risk and compliance tools detect fraud, enforce KYC requirements, and generate SARs. Customer-facing applications deliver the interface people actually use. Each category has different latency requirements, different regulatory constraints, and different failure modes. Mixing them up without understanding these differences is how institutions end up with systems that pass unit tests but fail under load.
When implementing any Financial Institution Solutions stack, you should plan for three types of integration points. First-party integrations connect systems within your own infrastructure. These are the ones you control directly and should take the most design time. Third-party integrations connect to external vendors. These are the ones that cause the most headaches because you cannot modify their behavior. Legacy integrations connect to systems you inherited and cannot replace. These are the ones you should budget the most operational overhead for.
Get the Full Details
Implementation Patterns That Do Not Fail Under Pressure
The architecture most firms default to is a point-to-point integration model. System A talks to System B, which talks to System C. This works until you add a fifth system, and then you have twenty separate integration contracts to maintain. A more sustainable approach is an event-driven architecture where systems publish events rather than making direct calls. This decouples the components and makes it easier to add new systems without touching existing ones. The trade-off is increased complexity in monitoring and debugging when events get lost or processed out of order. In practice, I found that a message queue with exactly three retry strategies handled the volume without dropping transactions. The first strategy is exponential backoff with jitter for transient failures. The second is dead letter queue routing for messages that fail after five attempts. The third is manual intervention for messages that require human judgment. This pattern cut our reconciliation time from about 4 hours per day to roughly 20 minutes, depending on the volume of exceptions. The error handling pattern most institutions implement is wrong. They catch exceptions, log them, and move on. This creates a growing pile of unreconciled transactions that surface during audits. A better pattern is compensating transactions where every failed operation has a known rollback path. For example, if a deposit succeeds but the interest calculation fails, you record the deposit and schedule a compensating adjustment rather than leaving the transaction in an indeterminate state.
Testing Financial Institution Solutions requires three types of test data. Synthetic data mimics the structure of real transactions without containing actual customer information. This is the type you use for unit tests and integration tests. Masked data contains real transaction patterns but with sensitive fields redacted. This is the type you use for performance tests and load tests. Shadow data runs in parallel with production without affecting actual accounts. This is the type you use for validation before cutting over to a new system. Using shadow data properly requires about 40% more storage and 60% more CPU than regular production traffic, but it catches about 90% of integration issues before they reach customers. The deployment pattern most firms use is blue-green with feature flags. This allows you to roll out changes gradually and roll back quickly if something breaks. The limitation is that feature flags create technical debt if you do not clean them up within 90 days. I recommend setting an automated alert that flags feature flags older than 60 days and escalates to the engineering manager at 75 days. This usually reduces flag-related bugs by about 70% without adding significant operational overhead.
Common Pitfalls and How to Avoid Them
The pitfall most institutions fall into is underestimating the time required for data migration. A typical bank with five million accounts and ten years of transaction history requires approximately six to eight weeks for extraction, transformation, and validation. Not because the data is large. Because the data is messy. Inconsistent date formats, missing fields, duplicate records, and historical quirks from legacy systems surface during migration and require manual resolution. Budget two weeks of buffer time beyond your initial estimate, and expect the buffer to be consumed within the first week regardless. Another common pitfall is assuming that compliance requirements are static. They are not. Regulatory frameworks change every quarter, and your Financial Institution Solutions must accommodate these changes without requiring full system rebuilds. I encountered a situation where a new KYC requirement mandated additional customer data fields that the existing system did not support. The vendor claimed the update would take four weeks. It took eleven weeks because the field validation logic conflicted with existing business rules that had been in place for seven years. The workaround was writing a temporary data enrichment service that mapped the new requirements to existing fields and flagged discrepancies for the compliance team to review manually. The pitfall most developers overlook is the impact of leap years and non-business days on financial calculations. Interest calculations that assume 360 days per year behave differently than those that use actual day counts. This matters during leap years and when calculating interest across February boundaries. Our team learned this the hard way when a system designed for commercial banking produced incorrect interest calculations for consumer accounts during a leap year. The fix required implementing dual calculation engines and selecting between them based on account type and product rules.

Performance testing Financial Institution Solutions requires three types of load scenarios. Baseline load simulates normal business hours with typical transaction volumes. Peak load simulates end-of-month processing, payroll cycles, or holiday spending surges. Stress load pushes the system beyond expected capacity to identify breaking points. Running stress tests monthly during the quarter before examination season catches about 80% of capacity issues before they affect customers. The security pitfall most institutions repeat is storing encryption keys alongside the data they protect. This defeats the purpose of encryption. A hardware security module or cloud KMS service should manage all encryption keys, with access controlled through separate IAM policies. This adds about one hour of setup time per environment but prevents the catastrophic key exposure scenarios that occur when someone copies a database backup to a development server and includes the encryption keys in the same export.
When Financial Institution Solutions Fail Completely
No system handles every scenario. Core banking platforms fail when you need real-time cross-border payments with dynamic currency conversion and the vendor only supports same-day batches with fixed exchange rates. Payment gateways fail when you need sub-second authorization for high-volume card transactions and the provider’s SLA guarantees 99.5% uptime with 30-second response windows. Fraud detection systems fail when you need to balance false positive rates against customer experience and the model was trained on data from a different market segment. The failure mode most institutions ignore is single-vendor lock-in. When a vendor raises prices, changes terms, or discontinues a product you depend on, you have approximately six to nine months to migrate before operations are severely impacted. This timeline assumes you have maintained clean API contracts and documented integration points throughout the relationship. Most institutions have not, and they face 18 to 24 months of emergency migration under pressure. Writing an exit strategy document within the first year of any vendor relationship takes about three days and reduces migration panic significantly when pricing changes occur. I recommend keeping one alternative Financial Institution Solutions provider in active evaluation at all times. This does not mean switching vendors constantly. It means maintaining the capability to migrate within 90 days if the primary vendor relationship becomes untenable. The operational overhead is about 10% of a full-time engineer’s capacity, but it provides leverage in contract negotiations and reduces vendor arrogance, which is a measurable quality in supplier relationships.
Practical Implementation Timeline
A typical Financial Institution Solutions implementation for a mid-market bank follows this sequence. Month one and two cover requirements gathering and vendor selection. Month three through five cover system configuration and first-party integration development. Month six covers data migration preparation and test environment setup. Month seven and eight cover shadow data validation and parallel running. Month nine covers user acceptance testing and compliance sign-off. Month ten covers cutover and production validation. Month eleven and twelve cover stabilization and documentation. This timeline assumes a greenfield implementation with no legacy constraints. If you are migrating from an existing system, add three to four months for data reconciliation and legacy decommissioning. If you are integrating with multiple external partners, add two to three months for third-party API negotiation and testing. If your institution operates across multiple jurisdictions with different regulatory requirements, add one to two months for localization and compliance validation. The budget most institutions allocate is too low by about 30%. Plan for contingency funding equal to one quarter of the total project cost, and expect to consume approximately half of that contingency during the data migration phase. The remaining half covers post-cutover stabilization, which usually extends two to four weeks beyond the planned completion date.

Monitoring and Maintenance After Go-Live
Implementation is not the end of the project. It is the point where ongoing operational costs become visible. Monitoring Financial Institution Solutions requires three dashboard views. Transaction health shows success rates, latency percentiles, and error breakdowns in real time. Financial reconciliation shows ledger balances, pending transactions, and unmatched items. Compliance status shows regulatory filing deadlines, audit trail integrity, and exception rates that require investigation. Review these dashboards daily during the first month after cutover, weekly during the second and third months, and bi-weekly thereafter. The exception rate that triggers immediate investigation is any single-day spike above three standard deviations from the rolling 30-day average, or any single error category exceeding 1% of total transaction volume. These thresholds catch about 95% of production issues before they escalate to customer impact or regulatory concern. Update the integration contracts quarterly, even if no changes occurred. Vendors modify their APIs behind the scenes, and breaking changes surface during routine maintenance windows when you are least prepared for them. Scheduling a monthly integration test against a production mirror environment catches about 70% of silent API changes before they affect live transactions.
The staff training cycle most institutions skip is the one that causes the most post-go-live problems. Operations staff should receive hands-on training in the new system at least 60 days before cutover, with scenario-based exercises covering failure recovery, manual override procedures, and escalation paths. Knowledge transfer from the vendor should include documented workarounds for known limitations, not just the ideal path through the system. Request these workarounds in writing before signing the contract, and verify that they are included in the acceptance criteria for final payment. I have seen three Financial Institution Solutions implementations fail completely because the institution assumed the vendor would handle edge cases that were explicitly documented as out of scope. Reading the fine print in integration contracts takes about two hours and prevents six to eight weeks of emergency development when those edge cases surface during peak processing. The clauses to focus on are limitation of liability, service level definitions, data ownership provisions, and termination transition assistance. These four sections determine what happens when things go wrong, not the feature list that gets featured in marketing materials. When evaluating any Financial Institution Solutions provider, request references from institutions that are the same size and operating in the same market segment as your organization. Vendor-provided reference accounts are usually the happiest customers with the longest implementation timelines and the most favorable contract terms. Ask your sales contact for the names of three accounts that recently experienced a significant operational issue, and contact them directly to learn how the vendor responded. The difference between a vendor that resolves problems and a vendor that escalates them is usually visible within the first 24 hours of any incident, and your contract should specify response time expectations that match this urgency.
The final consideration is whether your organization needs a dedicated integration team or can rely on internal IT staff with part-time integration responsibilities. Small institutions with fewer than five million accounts and simple product lines usually manage with internal staff handling integration as part of broader operational duties. Medium to large institutions with complex product portfolios and multiple external partnerships require dedicated integration engineers with specialized knowledge of banking protocols, data formats, and regulatory requirements. The cost difference is approximately $120,000 to $150,000 annually per integration engineer, but the reduction in go-live delays and post-implementation fire drills usually pays for itself within the first year of operation. Document every configuration decision, every integration workaround, and every exception handling procedure in a centralized repository accessible to both technical staff and compliance auditors. This documentation should be updated whenever the system configuration changes, not maintained as a static artifact created during implementation. I have reviewed audit trails from institutions where the documentation was current and the system behaved according to specification, and I have reviewed audit trails where the documentation was two years old and the actual implementation diverged significantly from the recorded design. The difference between these two scenarios is usually a quarterly documentation review process that takes about four hours per quarter and prevents weeks of explanation during examination periods. Financial Institution Solutions are not software products you install and forget. They are operational systems that require continuous monitoring, periodic validation, and adaptive management. The institutions that treat them as permanent infrastructure investments rather than one-time procurement projects are the ones that survive examination season without panic, process transactions reliably during peak load periods, and maintain the flexibility to adapt when regulatory requirements or market conditions change. Everything else is a timeline and a budget problem waiting to surface during the worst possible moment.