Where To Actually Start When A Company Claims Everything Is Fine
The biggest mistake people make when beginning a financial investigation is assuming they need a clean dataset. You won't get one. The person running the operation knows where the bodies are buried because they buried them. Your job is to find the spots where someone moved earth recently. I spent three weeks on an engagement last year investigating a mid-market manufacturing company for suspected procurement fraud. The controller brought me a neatly organized ERP system with full audit trails, approval workflows, and segregation of duties that looked perfect on paper. It took me fourteen hours of manual journal entry review to find the discrepancy. Not because the data was hidden well, but because nobody had actually checked whether the approval workflow was being circumvented through manual overrides.
The Actual Process Of Financial Investigation And Forensic Accounting
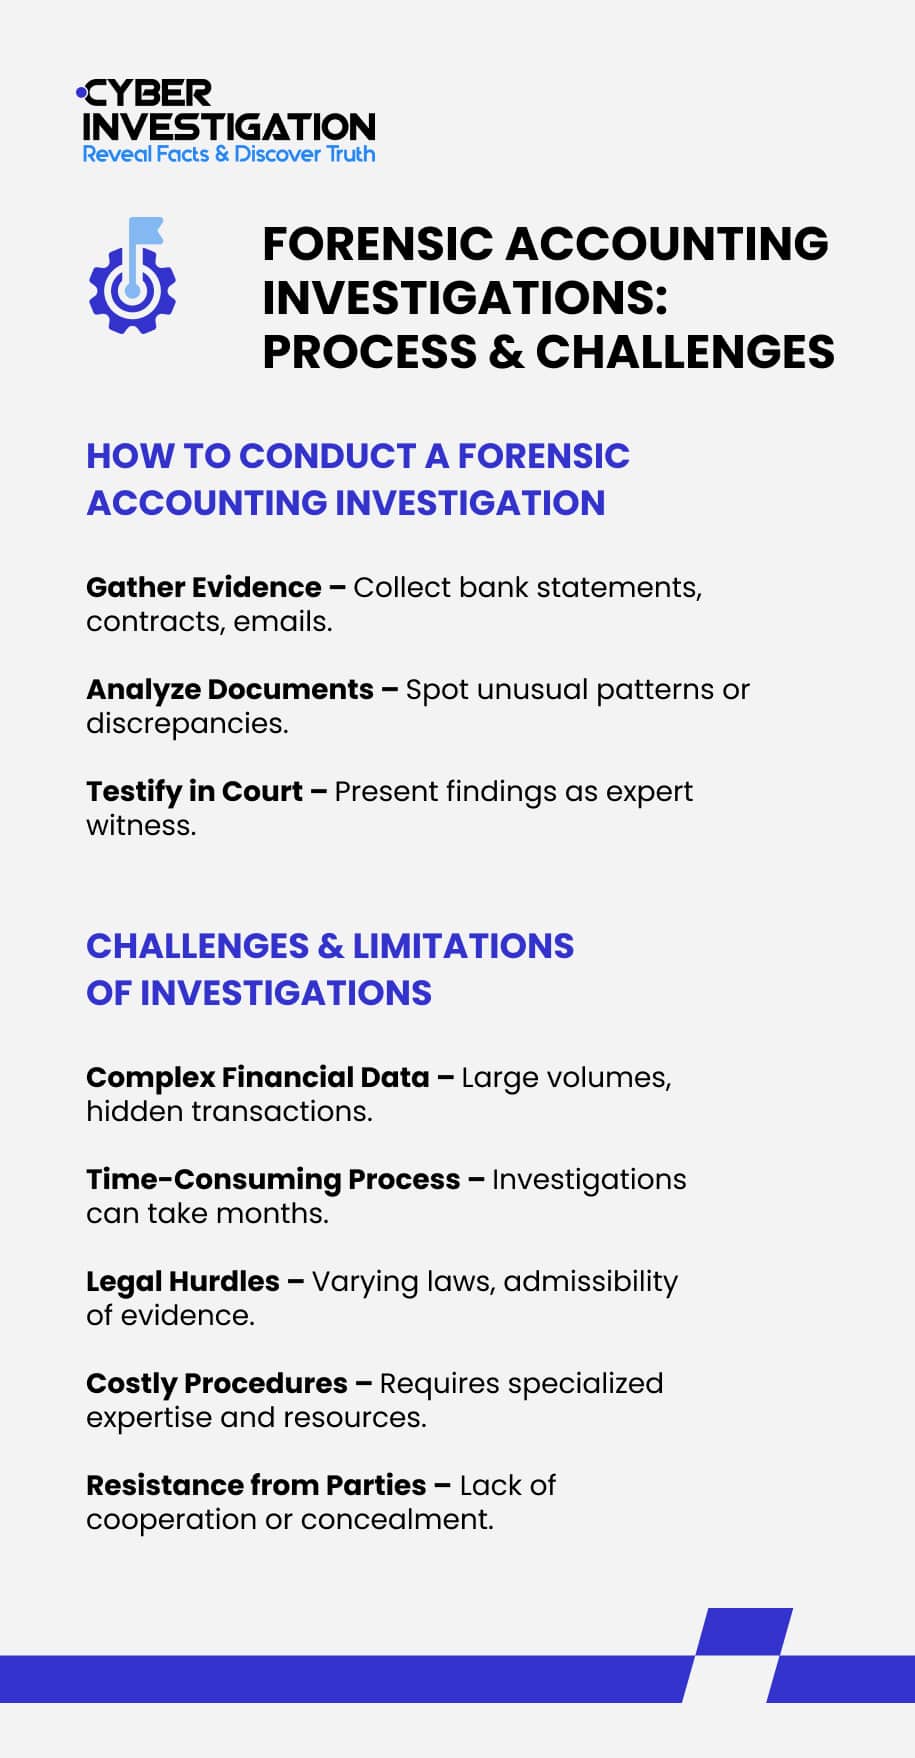
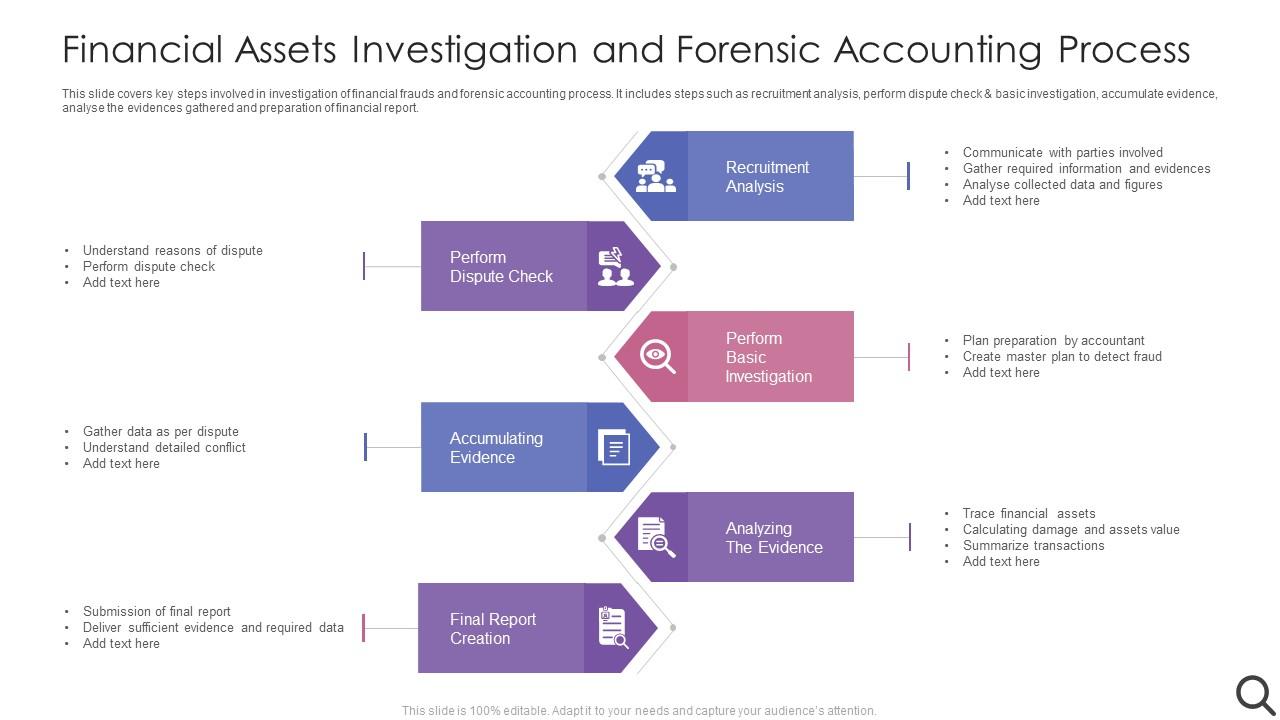
Forensic accounting is not the same as audit. Auditors look for material misstatements. Forensic investigators look for intentional misstatements designed to hide something. The difference matters because your testing approach changes completely when you are hunting for deception rather than error. Start by establishing the baseline. Pull three years of general ledger activity, vendor master files, and purchase order to invoice matching reports. Most people skip this and go straight to data analytics tools. That is backwards. You need to understand the normal shape of the numbers before you can spot the abnormal ones. A vendor who receives payments every 31 days is normal. A vendor who receives payments on the 31st day of every single month, including February, is worth a phone call. The core methodology breaks down into four phases, though they rarely happen in order in practice. First is planning and scoping, where you define the scope of potential loss and identify which accounts are most vulnerable to the type of fraud you are investigating. Second is data acquisition, where you collect and preserve electronic records in a forensically sound manner. This matters if the evidence will ever be presented in court. If it is just internal, you can be less formal, but you should still hash the files and document your chain of custody anyway. Third is analysis, where you apply techniques like Benford's Law analysis, duplicate payment testing, round-dollar transaction screening, and vendor address matching against employee addresses. Fourth is reporting, where you translate findings into language a judge or arbitrator can use.
Here is a specific example from my experience that illustrates why the standard approaches fail sometimes. A healthcare provider was suspected of billing fraud involving phantom patients. The standard approach would be to run a duplicate patient ID check and a zero-dollar transaction screen. Both came up clean. What I did instead was pull every encounter date and cross-reference it against employee PTO records. Three billing specialists were generating encounters on days they had logged vacation time. That was the only anomaly that appeared. The fraud wasn't in the data structure. It was in the access logs. This specific technique cut my investigation time from an estimated six weeks down to about eight days.
Get the Full Details

What People Get Wrong About Data Analytics In Forensic Work
Data analytics tools like ACL, IDEA, or even Excel with advanced pivot tables are useful, but they have a well-known limitation that almost every beginner ignores. They can only find what you ask them to find. If you do not know what question to ask, the tool gives you clean results and a false sense of security. A counter-intuitive insight that took me years to learn: the most profitable fraud investigations are often the ones where the data is messy. Clean data usually means someone has already done a pass at cleaning it up, which means they have already decided what stays and what goes. Messy data with gaps, inconsistencies, and duplicate records is more likely to reveal where the actual problems exist. I once found a $2.3 million embezzlement scheme hidden in what looked like a junk spreadsheet that nobody had touched in four years. The fraudster assumed it was too disorganized to be worth investigating. Another thing beginners consistently miss is the relationship between payment patterns and approval authority. Most ERP systems allow different approval thresholds based on transaction type, vendor category, or amount. When someone manipulates the vendor master file to reclassify a payment category, they often forget to update the approval routing. The result is payments that bypass secondary approval because the system now thinks they are routine operating expenses rather than professional services or consulting fees. Tracking these approval deviations is often more revealing than chasing the transactions themselves.
When Financial Investigation Does Not Work
There are real limitations to this field that anyone claiming otherwise is not being honest. First, if the suspect destroyed or deleted records, digital forensics can sometimes recover them, but not always. I have closed engagements where the IT department reformatted servers before I arrived and there was nothing left to analyze. The financial impact is unknowable in those cases. Second, forensic accounting alone cannot prove intent. You can show that money moved incorrectly, but intent requires corroborating evidence such as communications, witness testimony, or behavioral indicators. Without that, you have a discrepancy, not a crime. Third, the cost-benefit analysis often works against the investigator. A thorough forensic engagement for a mid-size company typically runs between $75,000 and $250,000 depending on complexity and duration. If the suspected loss is under $100,000, insurance recovery may be more efficient than a full investigation. That does not mean you should skip it entirely. Sometimes the purpose is not recovery but termination and process improvement. But it is worth being explicit about what the engagement is supposed to achieve before you sign the engagement letter. If you are looking to build skills in this area, the most practical path is gaining audit experience first, then specializing. Professional certifications like the CFE through the ACFE or the ABV through the AICPA carry weight. Software proficiency in SQL, Python for data analysis, and at least one major ERP platform is now essentially required rather than optional. The field is moving toward automated detection systems, but the people who design and validate those systems need hands-on experience with actual fraud schemes, not just theoretical knowledge.
The reality of working in this space is that most of the time you are not solving a mystery. You are doing tedious, repetitive work comparing records that someone intentionally made hard to compare. The satisfaction comes from finding the one inconsistency that explains everything else, usually after you have already spent two weeks convinced you were looking in the wrong place.