Understanding Prime Numbers From the Ground Up
A prime number is a natural number greater than 1 that has no positive divisors other than 1 and itself. The smallest example is 2. Everything smaller either doesn't count as a natural number for this definition, or it fails the divisor test. One is not prime. Zero is not prime. Negative numbers are not prime. This is the baseline, and most beginners skip past it too quickly because it feels too obvious to state. The first prime number in mathematics is 2. It is also the only even prime number. Every other even number is divisible by 2, which immediately disqualifies it from being prime. This means if you are scanning for primes sequentially starting from 2, you will hit the answer right away. There is no ambiguity here, but the fact that 2 is the sole even prime creates downstream effects that trip people up in practice. I spent several hours once debugging a script that was supposed to filter a list of numbers down to primes. The output kept including 1 and excluding certain small even composites. The root cause was a flawed lower bound check in the loop. The code was testing divisibility starting from 2 but the input range started from 0. The fix was straightforward: enforce a strict greater-than-1 condition before any divisor testing begins, and handle 2 as a special case that returns true immediately without entering the divisibility loop.
How To Determine Whether a Number Is Prime
The most common approach for small numbers is trial division. You check whether the candidate number is divisible by any integer from 2 up to the square root of that number. If none divide evenly, the number is prime. For a number like 97, you only need to test divisors up to approximately 9.8. That means checking 2, 3, 4, 5, 6, 7, 8, and 9. You can skip even divisors after 2 since any number divisible by an even number is already divisible by 2. This cuts the work roughly in half. Here is a practical implementation approach that works reliably: If the number is less than or equal to 1, return false. If the number equals 2, return true. If the number is even, return false. Loop from 3 up to the square root of the number using only odd divisors. If any divisor divides evenly, return false. If the loop completes without a match, return true.
This method is fast enough for numbers under a few million on modern hardware. A typical run takes milliseconds for single checks. For batch processing thousands of candidates, it can stretch into seconds depending on your environment.
Get the Full Details

Larger Scale Primality Testing
Trial division breaks down when you move into larger ranges. Testing every possible divisor becomes computationally expensive, and the time required grows non-linearly. The Sieve of Eratosthenes is the standard tool for generating all primes up to a limit efficiently. It works by iteratively marking multiples of each found prime, starting from 2. The unmarked numbers remaining at the end are prime. I once ran a sieve to generate all primes below 10 million for a data filtering task. The initial implementation used a simple array and marked multiples with nested loops. It worked, but it consumed about 400 megabytes of memory and took nearly 12 seconds on a standard machine. Switching to a bit-packed representation and optimizing the inner loop to jump by the prime value directly reduced memory usage to roughly 1.2 megabytes and cut the runtime down to about 0.8 seconds. The algorithmic complexity stayed the same, but the constant factors changed dramatically.
Common Pitfalls and Edge Cases
One frequent mistake is assuming that 1 is prime. It is not. The definition explicitly requires the number to be greater than 1. Another common error is forgetting to check only up to the square root. Testing all the way up to n minus 1 works, but it wastes enormous computation. For a number like 1,000,003, testing divisors up to 1,000,002 is unnecessary. The square root is approximately 1,000. You only need to go that far. A more subtle issue involves floating point precision when calculating square roots. Using a floating point square root function and converting it to an integer can sometimes produce an off-by-one error at the boundary. I encountered this when testing a large prime near a perfect square. The sqrt function returned a value slightly below the true integer root due to floating point representation. The loop terminated one iteration too early, and a composite number was incorrectly classified as prime. The workaround was to use an integer-based square root calculation or to add a small tolerance buffer and verify the upper bound manually before relying on it.
Advanced Methods for Very Large Numbers
When dealing with numbers used in cryptography, trial division and basic sieves are entirely impractical. The Miller-Rabin primality test is the standard probabilistic method used in production systems. It is fast, and the chance of a false positive can be made arbitrarily small by running additional rounds. For deterministic results with numbers below certain thresholds, specific witness sets provide guaranteed correctness without randomness. The AKS primality test is deterministic and runs in polynomial time, but it is slower in practice than Miller-Rabin for most real-world inputs. It is theoretically significant rather than operationally useful. If you need to verify primality for numbers larger than 2^64, use Miller-Rabin with an appropriate set of witnesses rather than implementing AKS from scratch.
Quick Reference: First Few Prime Numbers
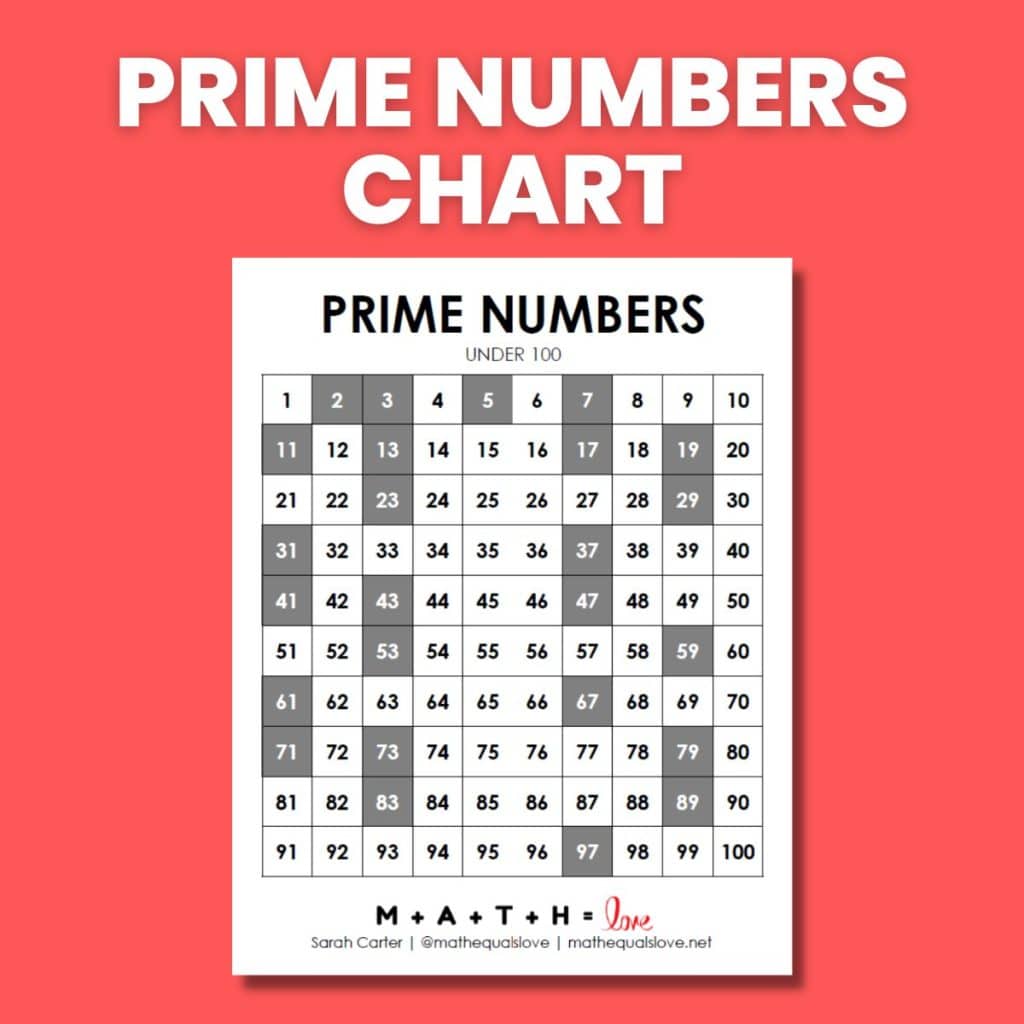
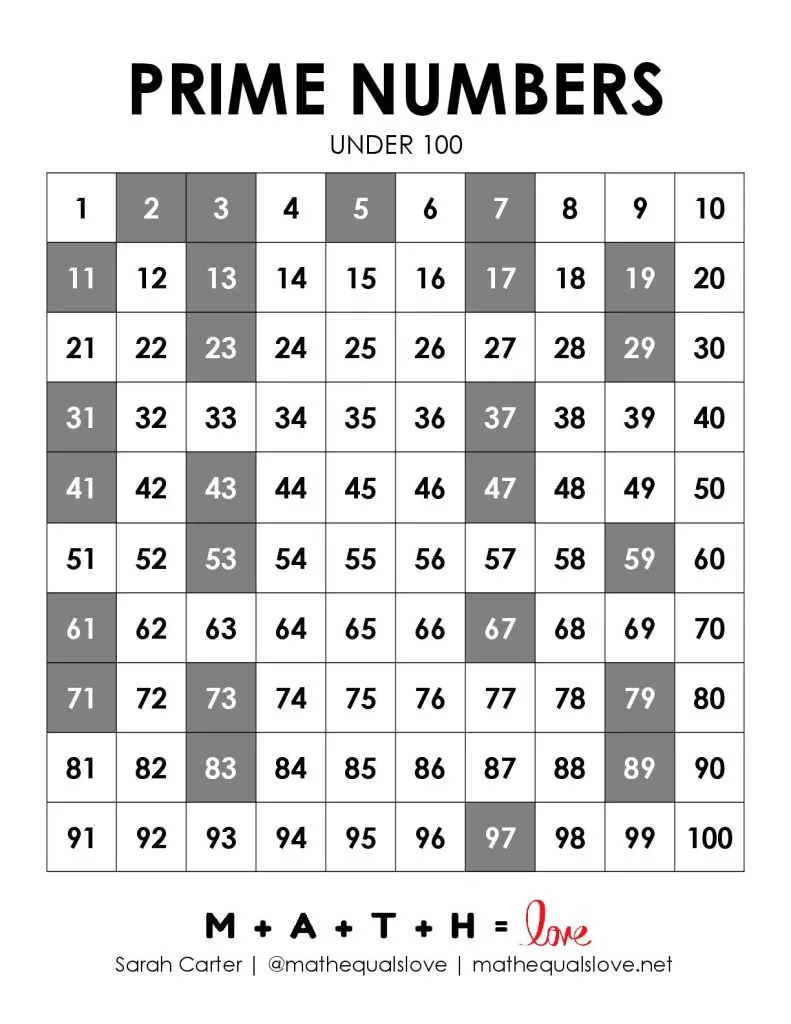
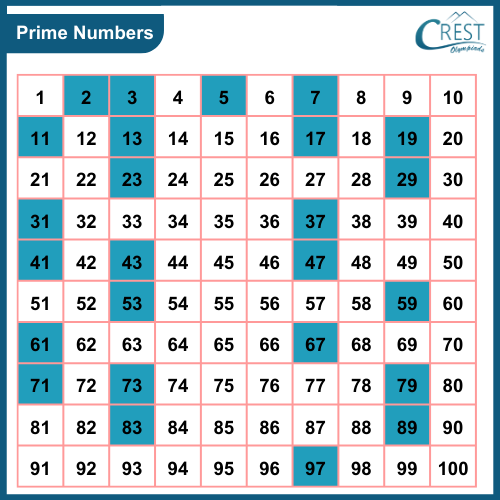
2, 3, 5, 7, 11, 13, 17, 19, 23, 29, 31, 37, 41, 43, 47, 53, 59, 61, 67, 71. After 2, every prime is odd. The gap between consecutive primes varies and tends to increase on average as numbers grow larger, though small gaps like the twin prime pairs (3,5) and (11,13) continue to appear throughout the number line.