So You Need to Investigate Fraud
Fraud investigation is less glamorous than the TV shows make it look. There is no dramatic montage, no sudden breakthrough at 2 AM. It is mostly patient, methodical work that involves a lot of digging through data you did not ask for and people who do not want to talk to you. If you are trying to do this properly, here is what the process actually looks like in practice.
Fraud Investigation A Step By Step Guide
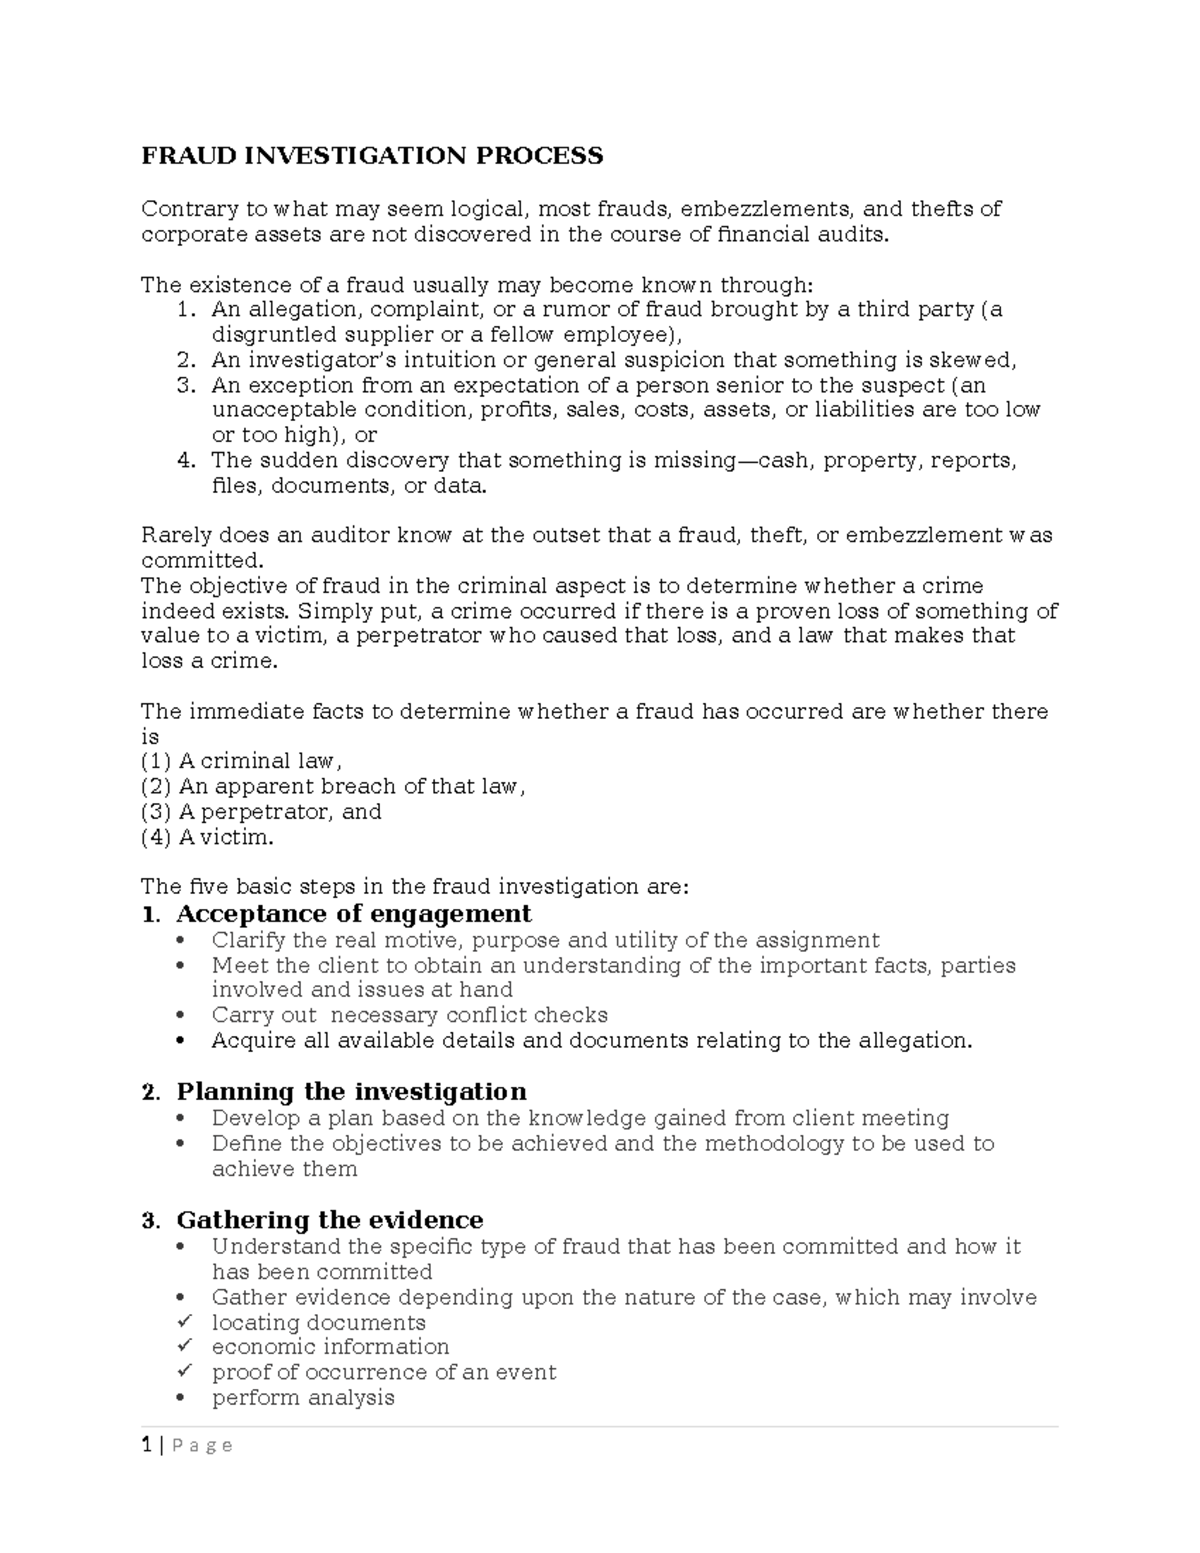
The Steps That Actually Matter
Most organizations skip straight to the evidence collection phase because it feels productive. That is a mistake. I have seen investigators go in blind and miss the obvious because they never bothered to understand what normal looks like in the system they were looking at. The real first step is scoping. Define what you are investigating before you touch anything. Is this a single employee suspected of expense fraud, a coordinated phishing campaign, or routine financial statement manipulation? The scope determines your entire approach. A narrow scope lets you go deep quickly. A broad scope means you will need a team and a lot of patience. After scoping, you interview the right people. Not the ones who look suspicious. The ones who understand the process. An accounts payable clerk who has been doing expense approvals for eight years will spot anomalies that a spreadsheet will never reveal. They know which vendors always round up, which managers always submit receipts late, which invoices always arrive on the same day every month.
Then comes evidence preservation. This is where people screw up. Chain of custody matters more than most investigators admit. If you are dealing with electronic evidence, make a write-blocked image of any storage media before you look at anything. Do not open files on the original device. I once spent three weeks rebuilding a case because I had opened an email file directly on a suspect's workstation and the defense successfully argued spoliation. The evidence was technically recoverable but the appearance of tampering killed credibility in court.
Get the Full Details

Data Analysis
Once you have preserved the evidence, you analyze it. Benford's law is useful for large datasets but it will miss sophisticated fraud. Real fraudsters know about digit distribution and adapt their schemes around it. You are better off looking at behavioral patterns. Repeat vendor changes. Payments just under approval thresholds. Transactions that happen on weekends or holidays. Invoices with identical descriptions submitted by different employees. A concrete example. I worked a case where a procurement manager was creating shell vendors. The scheme was clean enough that automated controls missed it. What gave it away was the email addresses registered for the vendors. They all had the same middle initial in the domain name, which matched the manager's middle initial. The amounts varied but the pattern was consistent. This took about four hours of manual cross-referencing after the initial tip came in. Automated tools would have needed a custom rule written to catch it.
Interviewing and Confrontation
Interviewing is the hardest part. You are talking to people who may be lying, terrified, or both. The Reid technique is mostly useless for internal investigations because it produces false confessions. Use the PEACE model instead. Plan the interview, Engage and explain, Account elicitation, Closure, and Evaluate. It takes longer but the information you get is more reliable and holds up better if the case goes to legal proceedings. When you do confront a suspect, never lead with your evidence. Let them talk first. Give them space to construct their narrative. Once they have committed to a version of events, the contradictions become much easier to point out. Leading with evidence just gives them a chance to adjust their story.
Reporting and Legal Considerations
Your final report needs to stand on its own. Someone who has never seen the case should be able to read it and understand exactly what happened and why you reached your conclusions. Include the methodology, the evidence reviewed, the interviews conducted, and the findings. Leave out the emotional content. Your job is factual accuracy, not drama. If you think prosecution is possible, consult legal counsel before you begin. Privilege considerations can change how you conduct interviews and document everything. An interview note that was prepared in anticipation of litigation may be protected. One that looks like routine internal documentation probably is not.
Where This Approach Breaks Down
Step-by-step guides always sound cleaner than the reality. Here is what they do not tell you. Small organizations often lack the infrastructure to do this properly. There is no dedicated IT forensics team, no secure evidence storage, no budget for external consultants. In those environments, you are working with whatever you have, which usually means a laptop, a USB drive, and a lot of guesswork. Another limitation. This process assumes you have access to the relevant data. In practice, data is often scattered across systems that do not communicate with each other. Legacy databases with no export functionality. Spreadsheets stored on personal drives. Paper records that were never digitized. I once spent more time tracking down where data lived than actually analyzing it. The workaround was engaging the IT department early, not as a backup step but as a parallel track from day one. External fraud is fundamentally different from internal fraud. This guide covers the internal investigation model. If you are dealing with organized crime, money laundering, or cross-border fraud, you need law enforcement involvement and specialized resources. No amount of good methodology will compensate for lacking jurisdictional authority.
Practical Tools That Actually Help
For smaller teams that cannot afford expensive forensic platforms, there are free or low-cost options. Autopsy is a solid open-source disk analysis tool. CSVHelper or the Analysis ToolPak in Excel handles basic data triage. For timeline reconstruction, Log2Timeline works reasonably well if you are comfortable with a command line interface. What helps more than any tool is understanding the business process. Fraud exploits gaps in procedure. If you know how the process is supposed to work, you know where the gaps are. And where the gaps are, that is where you should look first.