Why Most Fraud Risk Assessments Feel Like Busy Work
Most organizations approach fraud risk assessments the same way: open a template, fill in the fields, and hope the box gets checked during an audit. It does. That doesn't mean the assessment is useful. I've sat through enough of these to know that the gap between a documented assessment and one that actually changes how someone works is enormous. The template is easy. Understanding what the template is doing — and what it's not doing — is where people get tripped up.
Fraud Risk Assessment Template Pwc
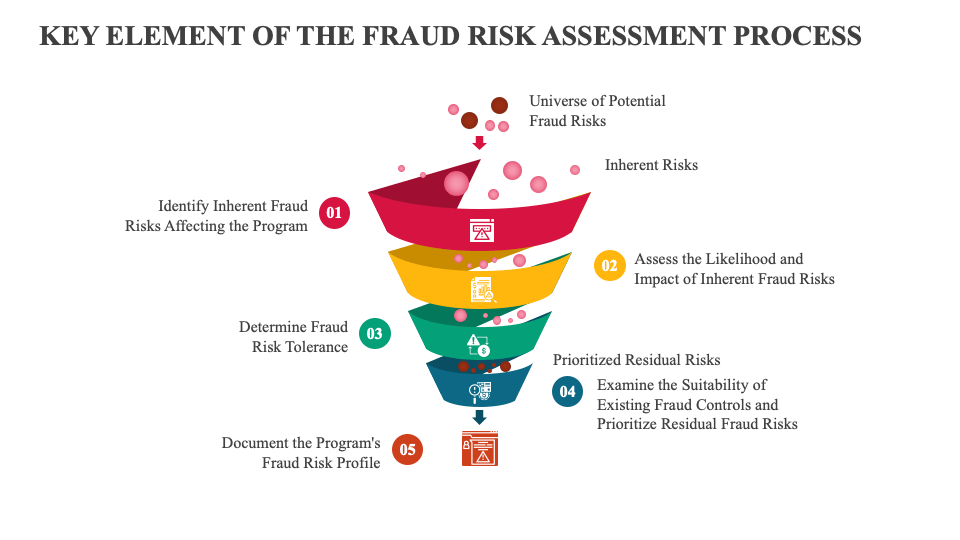
PwC's approach to fraud risk assessment templates is structured around three components: the fraud triangle (opportunity, incentive, rationalization), a scenario-based risk identification process, and a control evaluation matrix. The template itself is designed to move teams away from generic risk ratings toward scenario-specific analysis. Instead of labeling a process "high risk" because it involves payments, you're asked to identify which specific fraud scenarios could occur within that process and whether the current controls actually address them. The framework pulls from ISA 240 and the ACFE's guidance, but it's adapted for organizational use rather than audit compliance alone. That distinction matters because most templates you find online are written for external auditors, not internal teams who need to act on the results. Here's how the template typically breaks down in practice. You start with process mapping — identifying every area where fraud could reasonably occur, not where it could theoretically occur. Then you layer in scenario generation using the fraud triangle as a scaffold. Each scenario gets scored against likelihood and impact, but the scoring isn't arbitrary. The template pushes you to justify the score with evidence: prior incidents, control gaps, industry benchmarks, or data anomalies. Finally, you map existing controls to each scenario and rate their effectiveness, noting residual risk after controls.
The control mapping section is where most people rush. I've seen teams assign "effective" to a control simply because it exists on paper, even though nobody actually tests it quarterly or documents the testing. The template works against this if you let it, but only if you fill in the residual risk column honestly. I ran into a specific problem last year with a mid-market manufacturing client. They were using a PwC-style assessment template but had copied a generic template from a previous engagement without adjusting the scenarios. The template included procurement fraud scenarios — bid rigging, vendor impersonation, phantom vendors. The problem was this company operated on a sole-source supply chain model for specialized components. Vendor selection wasn't a competitive process. The bid-rigging scenario was completely irrelevant, and by keeping it in the assessment, they were wasting time analyzing controls that didn't exist and couldn't exist in their environment. My workaround was to strip out the misaligned scenarios first, then rebuild the assessment around their actual transaction types: inventory write-offs, change orders with subcontractors, and scrap sales. That shift cut the assessment timeline from three weeks to four days because we stopped analyzing the wrong processes. The template is only as good as the relevance of its scenario set.
Get the Full Details

There's a counter-intuitive point here that beginners miss. A lower number of high-scoring risks in your assessment isn't better than a higher number. It usually means your scenario identification is too narrow. During my work, I've found that well-run fraud risk assessments surface eight to fifteen distinct fraud scenarios per major process area. If you're scoring fewer than five, you're either protecting certain areas from scrutiny or you don't understand the business deeply enough to identify plausible scenarios. Both are common. Neither is acceptable if you're trying to actually reduce fraud risk. Another nuance involves the treatment of management override. The template typically includes a section for this, and most teams write one line about existing controls and move on. Management override is the single most common fraud enabler in my experience, and it's also the hardest to control. A control that prevents override in theory usually creates a control that is itself subject to override. The practical response isn't to add more controls — it's to strengthen detective mechanisms like anomaly detection in journal entries, review of unusual adjustment patterns, and mandatory rotation of those with override authority. The template should reflect this prioritization, and I've found that many standard versions don't emphasize it enough.
Working Through the Template Step by Step
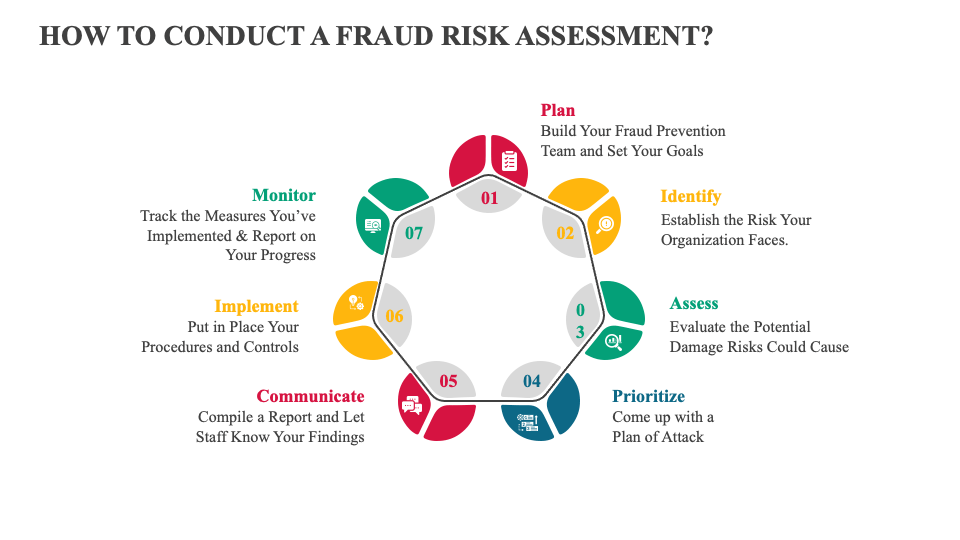
Start by identifying the processes under review. This means listing revenue, procurement, payroll, expense reimbursement, fixed assets, and any other area with material transaction volume. Don't include processes just because they existed in last year's assessment. If a process was eliminated or materially changed, note that and reassess from scratch. Next, conduct scenario brainstorming with people who actually work in those processes, not just managers. The person who processes vendor invoices every day will identify three to four fraud scenarios you'd never think of from a desk. I once had a payroll clerk point out that two employees had identical direct deposit accounts, which turned out to be a deliberate setup by a supervisor who was redirecting portions of their checks. The template would have caught this if the scenarios had included "collusion between supervisor and employee for payroll diversion," which the clerk immediately suggested but the manager-level participants would never have raised. After scenario generation, score each one using a consistent methodology. I use a 1-to-5 scale for both likelihood and impact, where the scales are explicitly defined so everyone uses them the same way. Likelihood considers control environment strength, historical data, and industry prevalence. Impact considers financial magnitude and reputational exposure. The product of likelihood and impact gives you a risk score, which you then map to a color-coded tier: red for immediate action, amber for near-term remediation, green for monitored but acceptable risk.
For each red and amber risk, document the specific controls currently in place. Rate each control as design effective, operating effectively, or ineffective. Design effective means the control, if executed properly, would prevent or detect the fraud scenario. Operating effectively means someone has actually been executing it consistently and documenting it. I've seen too many assessments mark controls as operating effectively when the documentation shows testing happened once a year or not at all in the past eighteen months. This is where the template can be manipulated without anyone noticing. Always check the evidence, not just the rating. Calculate residual risk by subtracting the control effectiveness rating from the inherent risk score. This gives you a prioritized list of what needs attention. The usual workflow from here is to assign owners, set remediation timelines, and establish monitoring triggers. The template should feed directly into your risk register, not sit in a separate document.

Common Pitfalls and What Actually Fails
The biggest failure mode I've seen is template reuse without contextual adaptation. Organizations download a template, populate it with last year's data, adjust the dates, and call it done. This produces a document that has no relationship to current risk. If your organization switched payment platforms, entered a new market, or underwent leadership changes, those events fundamentally alter the fraud risk landscape. The template is not a substitute for fresh analysis. Another failure is scoring everything as medium risk. When no risk is high, no risk is being taken seriously. If your assessment produces zero red-tier items across all processes, the scoring criteria are too lenient or the scenario identification is insufficient. I recommend calibrating scores against industry benchmarks before finalizing. Public data from ACFE case studies, regulatory enforcement actions, and sector-specific fraud surveys give you a reality check for your own scoring. The template also doesn't handle emerging fraud vectors well. Cryptocurrency payments, AI-generated invoice fraud, and synthetic identity schemes don't fit neatly into traditional scenario categories. I've had to add custom scenario sections to the PwC-style template to address these, with references to emerging typologies from FinCEN advisories and INTERPOL fraud reports. A static template will always lag behind the actual fraud landscape. Build in flexibility.
One practical detail that matters: frequency. An annual fraud risk assessment is the minimum, but for high-volume or high-risk processes, quarterly reviews of specific scenarios make more sense. I've recommended quarterly reassessment of procurement and revenue recognition processes for clients where transaction volume exceeds fifty thousand per quarter. The template structure supports this — you just need to schedule it and assign ownership upfront. If you're looking for the actual template structure, PwC publishes guidance materials and assessment frameworks through their professional services channels. The core template format typically includes tabs or sections for process overview, scenario identification, risk scoring, control mapping, residual risk calculation, and remediation tracking. Many organizations adapt this structure into Excel or integrate it into GRC platforms like ServiceNow, ARAM, or MetricStream depending on their existing infrastructure. The value isn't in having the template. It's in using it honestly, updating it when the business changes, and acting on the results. Everything else is documentation for a regulator who already knows you did it.