The actual process nobody talks about
Most people treat gap analysis and risk assessment as two separate exercises done at different times of the year. In practice that usually means the risk register gets updated while the gap analysis sits in a drawer because someone decided compliance was more important than architecture. I ran into this exact problem about three years ago when we were assessing a legacy payment system that had been patched eight different ways over four releases. The gap analysis showed us what was missing compared to our target state, but the risk assessment was built on documentation from two years prior. The two documents contradicted each other on at least six control points. The workaround was not complicated but it did require sitting down with the people who actually knew the system rather than the people who wrote the original architecture docs. I pulled the last three change logs, mapped each patch to the controls it touched, and flagged every area where the documented control no longer matched what was running in production. That cut the overlap between the two assessments from about thirty percent down to maybe eight percent. It also exposed two controls we thought we had in place that were essentially ghost controls, documented but never tested or maintained.
Why Gap Analysis And Risk Assessment should run as one workflow
When you treat them separately you get drift. The gap closes but the risk stays the same because the control environment shifted while nobody was looking. The opposite happens too, where a risk gets mitigated but you never update the target state documentation so the next gap analysis points at a wall that no longer exists. Running them together means every identified gap immediately feeds into the risk matrix and every high-risk item forces a review of the current state documentation. It adds roughly forty minutes to each cycle compared to doing them separately, but it eliminates the reconciliation step that otherwise eats two or three days later. Start with the current state documentation and tear it apart before you define the target. That sounds backwards but it saves a lot of time. Most organizations build their gap analysis against a clean room version of reality. They list what should exist and then look for holes. The problem is the thing they are comparing against does not match what actually runs. If you spend the first session walking through production configurations, active change tickets, and the last twelve months of audit findings, the gaps start revealing themselves without any framework pulling them out.
Step one, build an accurate current state
I use a combination of automated config pulls from the infrastructure layer and a focused interview round with system owners. The config data gives me the factual baseline. The interviews catch the undocumented workarounds. Every production system I have ever looked at has at least one workaround that appears nowhere in the documentation. In one case a database team had set up an automated nightly sync between two tables to bypass a licensing limitation. It worked fine until the licensing audit came around and the gap analysis had no record of it. Document everything including the known unauthorized modifications. Flag them clearly so they do not get treated as intentional architecture decisions in the next phase. This baseline phase typically takes one to two weeks for a mid-size environment, longer if you are dealing with fragmented ownership across multiple departments.
Get the Full Details
Step two, define the target state from evidence, not ideals
Target states tend to be written by consultants who have never touched the production environment. The result is a document full of requirements that cannot be implemented without a complete rewrite. A realistic target state is built from three sources: your own past successful implementations, the baseline configurations from systems that are performing well under similar conditions, and the industry frameworks filtered through your actual constraints. If your framework says you need multi-factor authentication on every internal system but your Active Directory infrastructure has not been upgraded since 2019 and the budget cycle is three years out, the target state should reflect a phased approach with clear milestones, not a flat requirement that triggers immediate failure across the board. Writing an unachievable target state is the single most common mistake I see. It makes the gap analysis look catastrophic and the risk assessment look useless because both are based on a fiction.
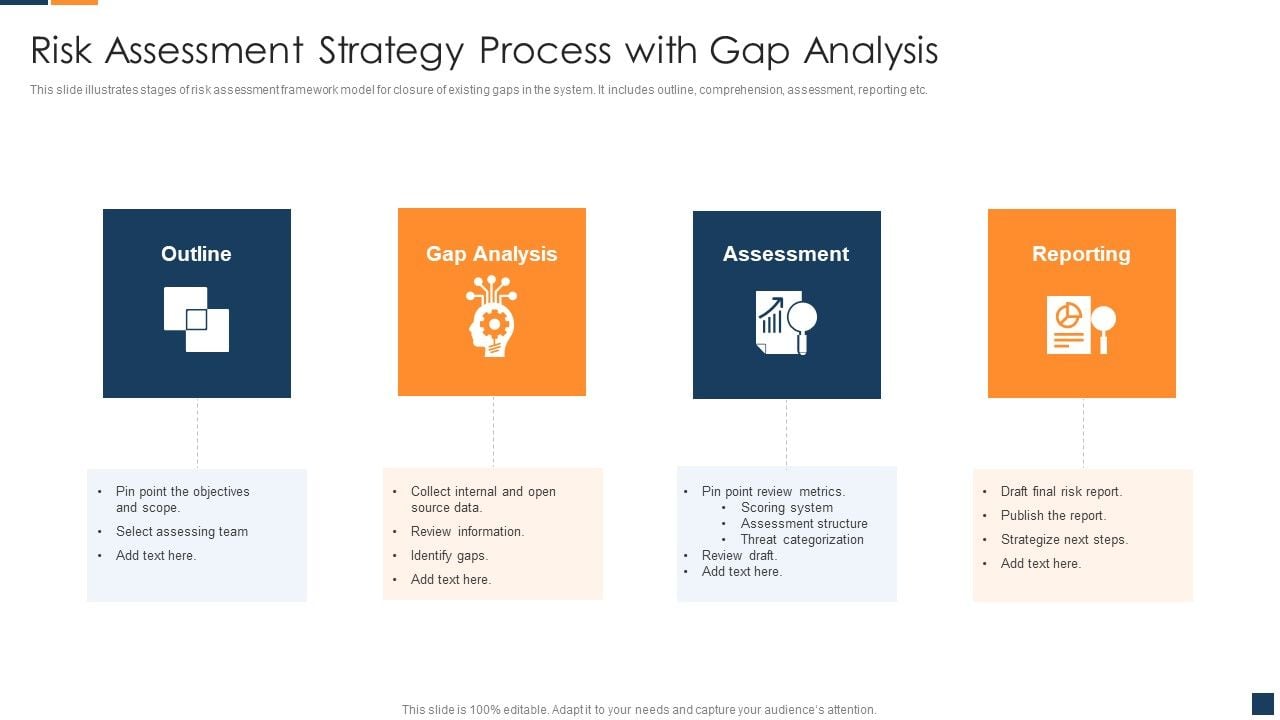
Step three, identify gaps and assess risk simultaneously
Here is where the combined workflow matters. For each gap you identify, immediately answer three questions: what risk does this gap expose, what is the likelihood given current controls, and what is the potential impact if it materializes. Do not finish the gap analysis first and then hand it off to the risk team. The likelihood and impact assessments change how you prioritize the gaps anyway. A missing encryption control on a staging server that handles no sensitive data is a gap, but it ranks near the bottom of the risk matrix. A gap in segregation of duties on the financial close process is a gap in a lower-profile area, but it carries far more risk. Treating all gaps equally is a waste of resources. The combined approach forces you to weight them correctly from the start.
Step four, map residual risk after mitigation options
Every gap has at least one mitigation path. The mitigation changes the risk score. You need to calculate both the inherent risk, what the exposure looks like before any mitigation, and the residual risk after applying the most practical control option. This is where people commonly mess up. They report the inherent risk as the final assessment and then wonder why leadership insists on action plans that never get funded because the numbers are inflated. In one engagement I worked on, the inherent risk on a third-party data handling gap was rated critical because the vendor contract did not include audit rights. The residual risk after adding alternative verification controls, periodic sample testing, and contractual right-to-verify language dropped the rating to medium. The gap was still real but the urgency changed dramatically and the budget request became achievable.

A counter-intuitive point most teams miss
Gap analysis tends to focus on what is missing. Risk assessment focuses on what could go wrong. The combination reveals something neither does alone: sometimes the biggest risks come from controls that exist but are actively broken. A firewall rule that looks correct in the documentation might have been overridden six months ago during an emergency change and never restored. A backup schedule shows as complete in the monitoring dashboard but the verification tests have been disabled because they were causing alert fatigue. These are not gaps. They are control failures disguised as coverage. The only way to catch them is to cross-reference the documented control with live evidence from the risk assessment side, and then go verify it in production. It requires access to production data and honest system owners. If your organization treats audit findings as punitive rather than diagnostic, the current state documentation will be sanitized and the whole exercise loses value. It also does not scale cleanly to environments with hundreds of independently managed systems without automation. I have seen manual gap and risk workbooks break down around forty to fifty assets. Beyond that you need tooling to track the relationships between gaps, controls, and risk registers. Spreadsheets work fine for smaller scopes. Another limitation is that the combined approach assumes you can allocate two weeks of focused effort. If you are forced to deliver results in five days, the baseline gets shallow and the risk assessments rely on assumptions rather than evidence. That is acceptable for a preliminary review but not for anything that will survive an external audit.
What to use and what to avoid
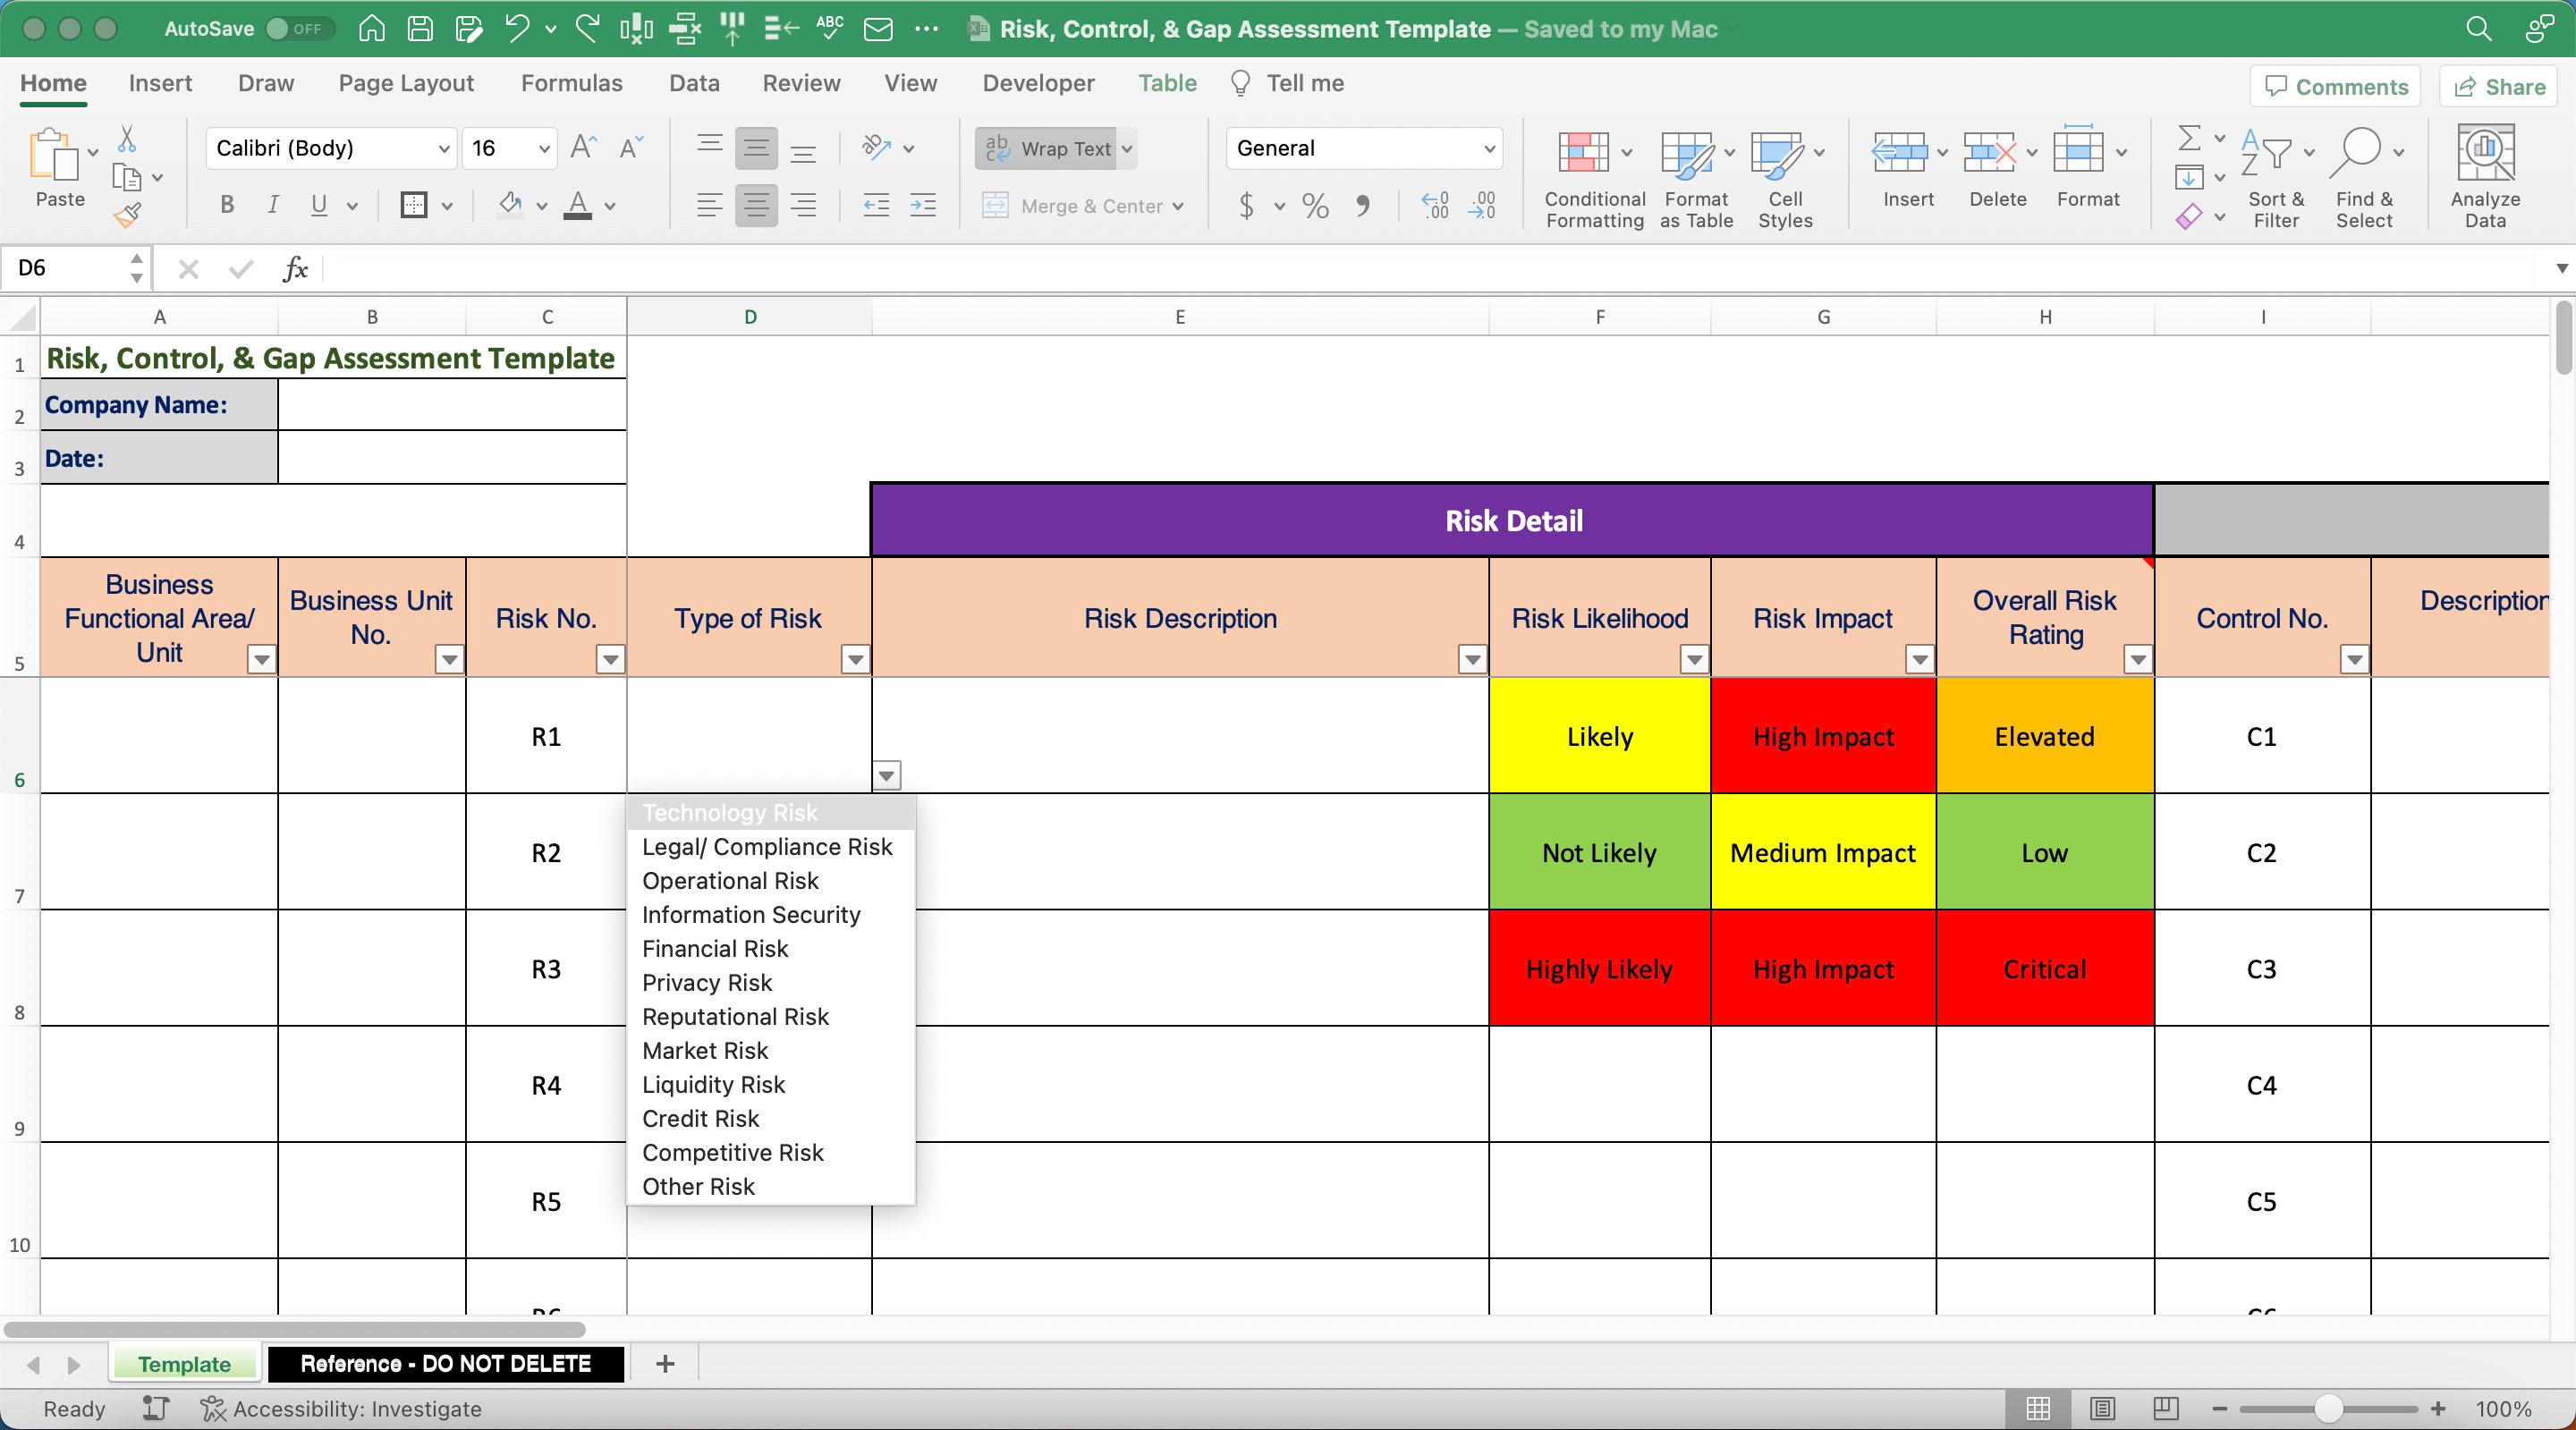
Keep the initial mapping simple. A spreadsheet or lightweight database with columns for asset, current control state, target control state, gap description, inherent risk, mitigation option, residual risk, and owner is enough to start. Add automation and integration later when you have a repeatable process. Avoid frameworks that demand extensive scoring models for every single gap. NIST CSF, ISO 27001 Annex A, and SOC 2 criteria all work as reference points. Use them to structure your thinking, not to fill out hundreds of rows of scoring grids that nobody reads after the presentation. The output should be a prioritized list of gaps with associated residual risk scores and owned remediation paths. That is it. Anything more elaborate usually becomes a document that gets archived and forgotten.
A quick note on cadence
Run a full combined assessment twice a year at minimum. Do a lightweight refresh after any major change, whether that is a new system deployment, a significant vendor transition, or a regulatory update that touches your control environment. The lightweight refresh takes about three days and covers only the affected areas. It keeps the baseline current without requiring a full cycle every quarter. The people who maintain this process effectively are the ones who treat documentation as living data and who accept that the current state will always be messier than the target state. The gap is the whole point. The risk assessment just tells you which gaps matter enough to fund the work to close them.