Why Most Gap Analysis Templates Fail Before They're Used
I've filled out dozens of these over the years, mostly for compliance audits and internal process reviews. The template itself is straightforward. The problem isn't the document. It's how people treat it. A Gap Analysis Template is just a structured way to compare where you are against where you need to be. Standard columns: current state, target state, the gap between them, and what needs to change. That's it. The complexity comes from filling it out honestly.
Gap Analysis Template Structure
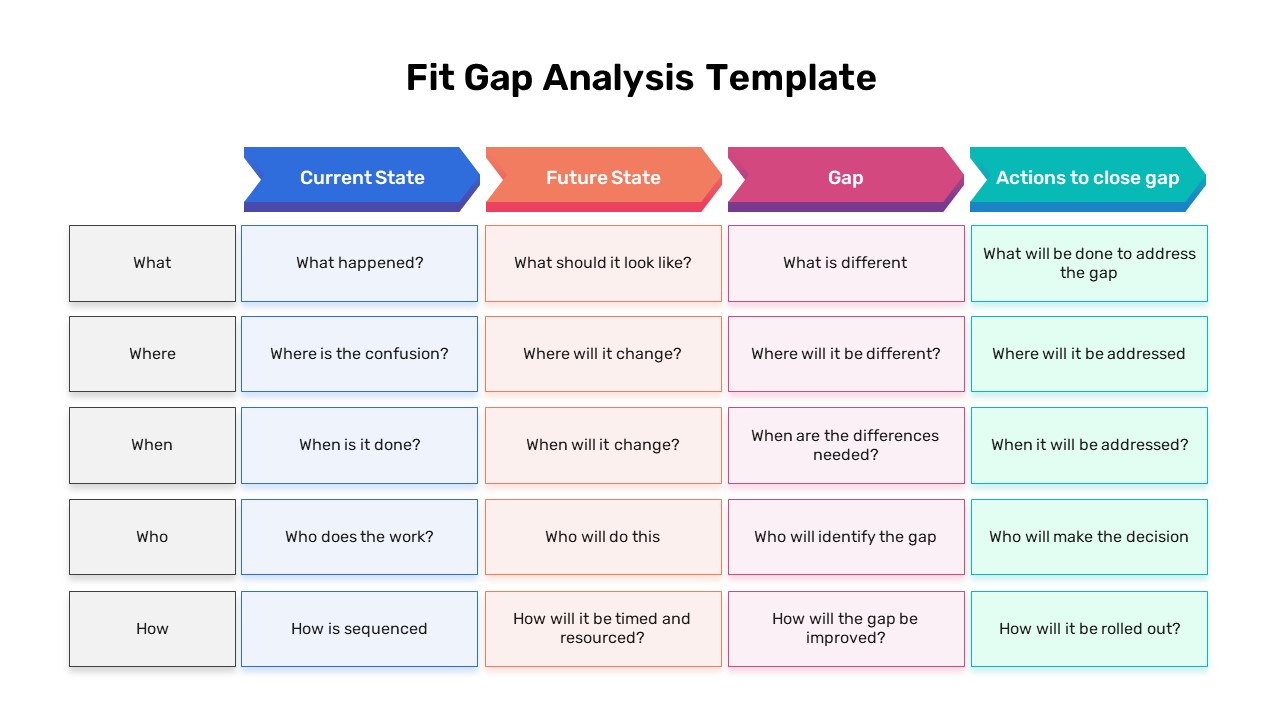
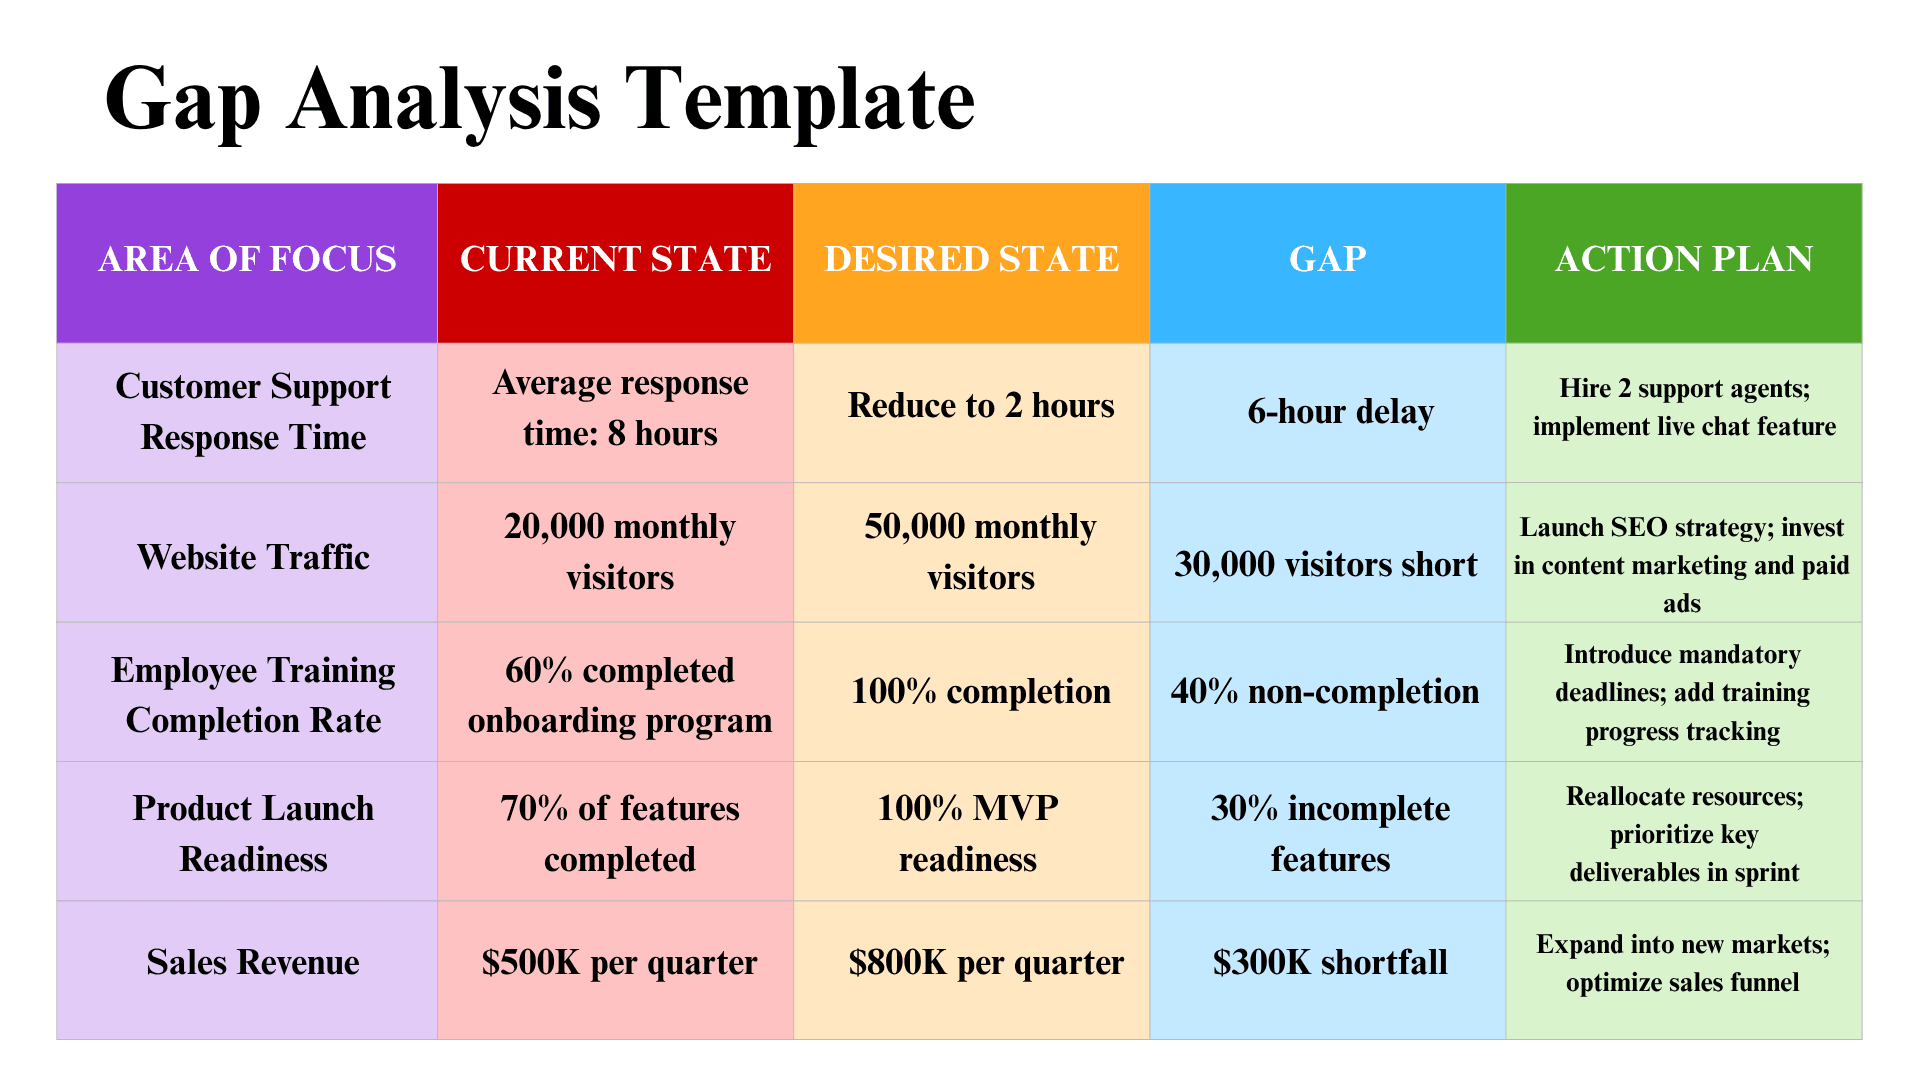
Here's what a working template actually looks like in practice. Not the fancy consulting version. The one people in my org end up using after we strip out the useless fields. The first column is process or control area. Be specific. "IT Security" is too broad. "Password rotation for admin accounts" is usable. Next column is current state — describe what actually happens, not what the policy says happens. I can't count how many templates I've seen with current state descriptions that were just copy-pasted from procedure documents. Those aren't current states. Those are fantasies. Then required or target state. This should reference an actual standard, regulation, or documented internal requirement. "Best practice" is not a requirement. "SOC 2 CC6.1 requires annual access reviews" is.
The gap description column is where most people rush. A gap isn't just "we don't do this." It's "current state lacks documented evidence of quarterly review, which is required by the annual audit scope under section 4.2 of our security policy." Concrete. Verifiable. That's the difference between a gap analysis that gets you somewhere and one that sits in a shared drive. Last column: remediation action. Not the gap fix. The specific action. Owner. Timeline. I used to leave this as a single column. Then I started splitting it into three sub-columns — action, owner, target date — and the whole document became actionable instead of decorative. That took about ten minutes to restructure and cut our follow-up meeting time from two hours to roughly twenty minutes per review cycle. The fifth column is risk rating. High, medium, low. But here's the thing most templates miss: define what high, medium, and low actually mean in your context. Otherwise you get one team marking everything as high and another team marking nothing above medium. I learned this the hard way during a PCI DSS gap analysis when our network team and our application team had completely different interpretations of severity. We ended up with a document that was internally contradictory and useless for prioritization. The workaround was spending thirty minutes upfront agreeing on criteria. "High means potential for data breach or regulatory fine. Medium means process failure with no direct data exposure. Low means documentation or procedural gap with limited operational impact." Thirty minutes saved us three weeks of back-and-forth.
Get the Full Details
What Nobody Tells You About Using This
The biggest mistake I see isn't structural. It's psychological. People treat gap analysis as a compliance checkbox instead of a planning tool. They want to prove there are no gaps, not find the real ones. This shows up as vague gap descriptions, overly optimistic remediation timelines, and risk ratings that don't match the actual exposure. Another thing: templates don't scale horizontally. A template that works for a twenty-person team falls apart at two hundred. The same framework, but you need different granularity. I've seen teams try to use a single document for enterprise-wide analysis across fifteen departments. It becomes unmanageable. Better to have a standardized template structure with separate instances per department or business unit, then aggregate findings at the program level. One specific edge case I ran into last year: we were mapping gaps against ISO 27001 controls, and the template didn't account for shared services. Our cloud provider handles patching for the underlying infrastructure. In the gap column, we could write "infrastructure patching performed by AWS — covered under shared responsibility model" but the template had no way to express that the gap wasn't really a gap. It was a dependency. I added a fourth status option to the risk column: "mitigated by third party." Made a note in the remediation field linking to the relevant contract clause. Took five minutes to implement and eliminated about a dozen false positives across that audit cycle.
Here's what the template can't do for you: it can't identify gaps you don't know exist. If your baseline understanding of the current state is wrong, your gap analysis is wrong. I've had this happen twice. Once because someone left the company and took institutional knowledge with them. Once because we documented a process from memory instead of observing it. Both times the gap analysis looked clean until an auditor asked to see evidence. The workaround is simple but nobody does it enough: validate current state by observation, not by interview. Watch the process happen. Check the logs. Look at the actual outputs. Five minutes of direct observation is worth more than an hour of asking people what they do. Also worth noting: gap analysis templates are notoriously bad at capturing temporal gaps. A control that existed six months ago and was removed yesterday shows up as "compliant" if you only look at the present moment. Include a column or footnote for recency if your environment changes fast. I add a "last verified" date to every current state entry. Makes drift visible immediately.
Practical Use Case
Last quarter I ran a gap analysis for our SOC 2 Type II readiness using this template. We had twelve workstreams, each owned by a different team lead. I distributed the standardized template, held a single kick-off call to align on definitions, and set a hard deadline for initial fills. The first submissions took about four days. Revision round — catching vague gaps and unrealistic remediation plans — took two more days. Final compilation and prioritization took half a day. Total effort: about eight person-days across the group. Without the template discipline, this would have stretched into weeks of parallel work with inconsistent output quality. The template you use doesn't need to be complex. It needs to be consistent. Consistency across teams, across cycles, across auditors. That's what makes it valuable. Not the number of columns. The fact that everyone means the same thing when they fill one out.