What Actually Happens When You Try to Implement What Gartner Calls Identity And Access Management
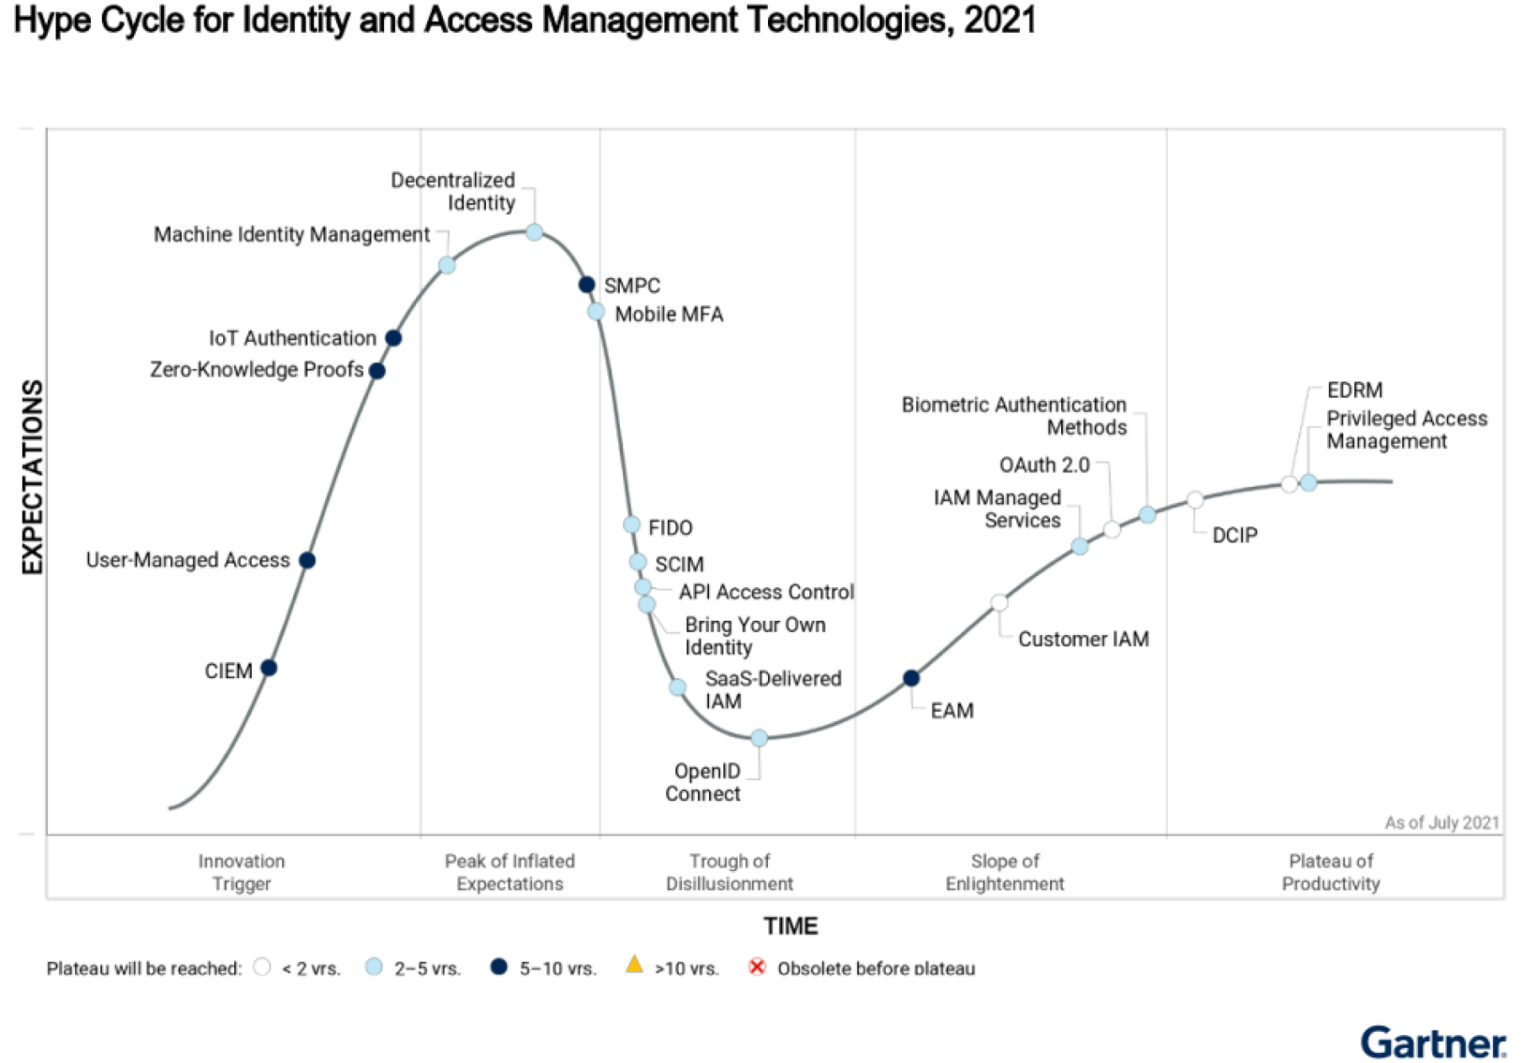
I spent about three years working on IAM rollouts across two different companies. The first one was a mess because nobody understood what they were actually buying into. The second one went better only because we stopped trying to boil the ocean and built the whole thing in layers instead of one giant migration. Gartner Identity And Access Management isn't a single product. It is a framework and a set of recommendations that vendors use heavily in their marketing. Understanding the difference between that and an actual implementation will save you a lot of money and a lot of headaches. Gartner covers IAM through several lenses: directory and identity services, privileged access management, customer identity and access management, access management and Federation, and the newer zero-trust angle they have been pushing since around 2020. Their Magic Quadrant for Identity and Access Management sees vendors like Okta, Microsoft, Ping Identity, SailPoint, ForgeRock, and CyberArk all positioned differently depending on which segment you are looking at. That alone tells you something important. There is no single Gartner-recommended tool. There is a set of capabilities they evaluate and score, and you need to figure out which ones actually matter for your environment before you talk to any vendor.
Gartner Identity And Access Management
When organizations start engaging with this material, the most common mistake is treating it like a catalog where you pick numbered options. It is not. It is a strategic document. The Gartner reports help you understand the landscape. They do not hand you a configuration guide. You still need to do the actual engineering work yourself. Here is what I usually suggest people do first: read the Gartner report for the specific category that matches your biggest pain point, not the broad IAM overview. If your problem is contractor access taking three weeks, look at the cloud access management section. If it is admin credentials being shared and poorly rotated, look at privileged access management. The reports are dense but they call out specific capability requirements for each sub-domain. Most people skip that part and jump straight to vendor names. The practical workflow for using Gartner material in a real project goes like this. You identify your primary IAM gap. You map that gap to a Gartner capability category. You then use the evaluation criteria from that category as a weighted scoring sheet for vendor demos. This turns a vague "we need better IAM" conversation into something with actual purchasing leverage. I have seen this cut demo time by about forty percent because you are asking the right questions upfront instead of letting vendors give their standard pitch.
One thing Gartner gets right and vendors rarely admit: the convergence of authentication and authorization is where most projects stall. You can buy a great SSO solution and still have zero idea who actually has what level of access to your databases. That is why Gartner pushes separate evaluations for identity governance, privileged access, and access management. People lump them together. Then they complain when the implementation does not solve their actual problem.
Get the Full Details
The Hard Parts No One Talks About
I ran into a very specific issue during a migration at a mid-size healthcare client. We were moving from a legacy LDAP directory with about forty thousand entries into a modern cloud identity provider, roughly Okta at the time, while maintaining access to several on-prem applications that used non-standard attribute mappings. The problem was not the sync itself. It was the group membership resolution. About twelve percent of the users had nested group memberships that went three or four levels deep, and the new system resolved those differently than the old one did. This meant access policies that worked for years silently changed behavior after migration. The workaround was to export the full group membership tree, write a script to flatten it and compare the resolved permissions before and after, and then manually reconcile the outliers. It took about two days of work. We built a validation checklist that flagged any user whose effective permissions changed by more than one tier. That became our go-to process for every subsequent IAM migration. The lesson here is that attribute resolution differences are almost always underestimated. Vendors will tell you their reconciliation is seamless. It is not. You need to audit the edges. Another counter-intuitive thing I learned the hard way: enabling multi-factor authentication everywhere at once is usually worse than a phased rollout. I watched a company enable MFA for all internal users in a single week. About eight percent of their workforce could not complete the enrollment process due to device incompatibility, language barriers, or simply not understanding the flow. Those users lost access to critical systems. The IT team spent three days on phone support instead of finishing the rollout. A staged approach, starting with high-privilege accounts and expanding outward, reduced that friction significantly. It also gave you time to adjust the support processes.
There is also the question of what Gartner does not cover well. Their IAM framework is strong on enterprise identity and weak on operational technology and IoT identity. If you manage industrial control systems, medical devices, or embedded hardware, you will find very little practical guidance there. In those cases, you are better off looking at NIST SP 800-162 or the IEC 62443 family instead of relying on Gartner to fill the gap. The zero-trust angle Gartner pushes is useful as a strategic direction but it gets misapplied constantly. Zero trust is not a product. It is a design philosophy that says you verify every access request regardless of network location. The problem is that most organizations already have IAM systems that do this at a basic level. What they are missing is context-aware risk assessment. Gartner calls this CARTA, continuous adaptive risk and trust assessment. Implementing a true CARTA model requires telemetry from multiple sources: endpoint health, user behavior analytics, application risk scoring, and network reputation. Without all of those feeding into a single decision engine, you just have another layer of friction that slows down legitimate users without actually improving security. If you are planning an actual implementation using Gartner as your guide, here is a realistic timeline. A standard mid-size deployment with cloud identity, SSO, and basic MFA takes about three to five months. Adding identity governance and automated provisioning for fifty or so applications can add another four to six months. Privileged access management on top of that is usually a separate project entirely. Trying to do everything at once is the fastest way to delay launch indefinitely. I recommend prioritizing SSO and MFA first, then identity governance, then PAM. This order gives you measurable security improvements early while you build the more complex pieces in the background.
The biggest bottleneck in almost every IAM project I have seen is not technical. It is organizational. Every department wants their applications onboarded. The IAM team can only handle a certain number of integrations per sprint. If you do not establish a clear intake and prioritization process upfront, you will spend months in committee meetings instead of building anything. I usually suggest setting a fixed cadence, like two new applications per sprint, and communicating that clearly to stakeholders. It sounds bureaucratic but it keeps the project moving. For documentation and further reading, the Gartner reports themselves are behind a subscription wall. Most libraries at universities and larger enterprises have access. If you work at a smaller organization, check whether your vendor reseller can provide summaries of the relevant sections. They often do, and it is a legitimate way to get the core recommendations without paying for a full subscription just for one report. Ultimately, Gartner Identity And Access Management material is best used as a filter, not a blueprint. It helps you understand the terrain. It does not drive the car. Your team still needs to do the mapping, the integration work, the testing, and the ongoing governance. Treat it that way and it will serve you well. Treat it like a shopping list and you will end up with a bunch of tools that do not talk to each other.