Using Gartner Magic Quadrant to Pick a Vulnerability Assessment Tool
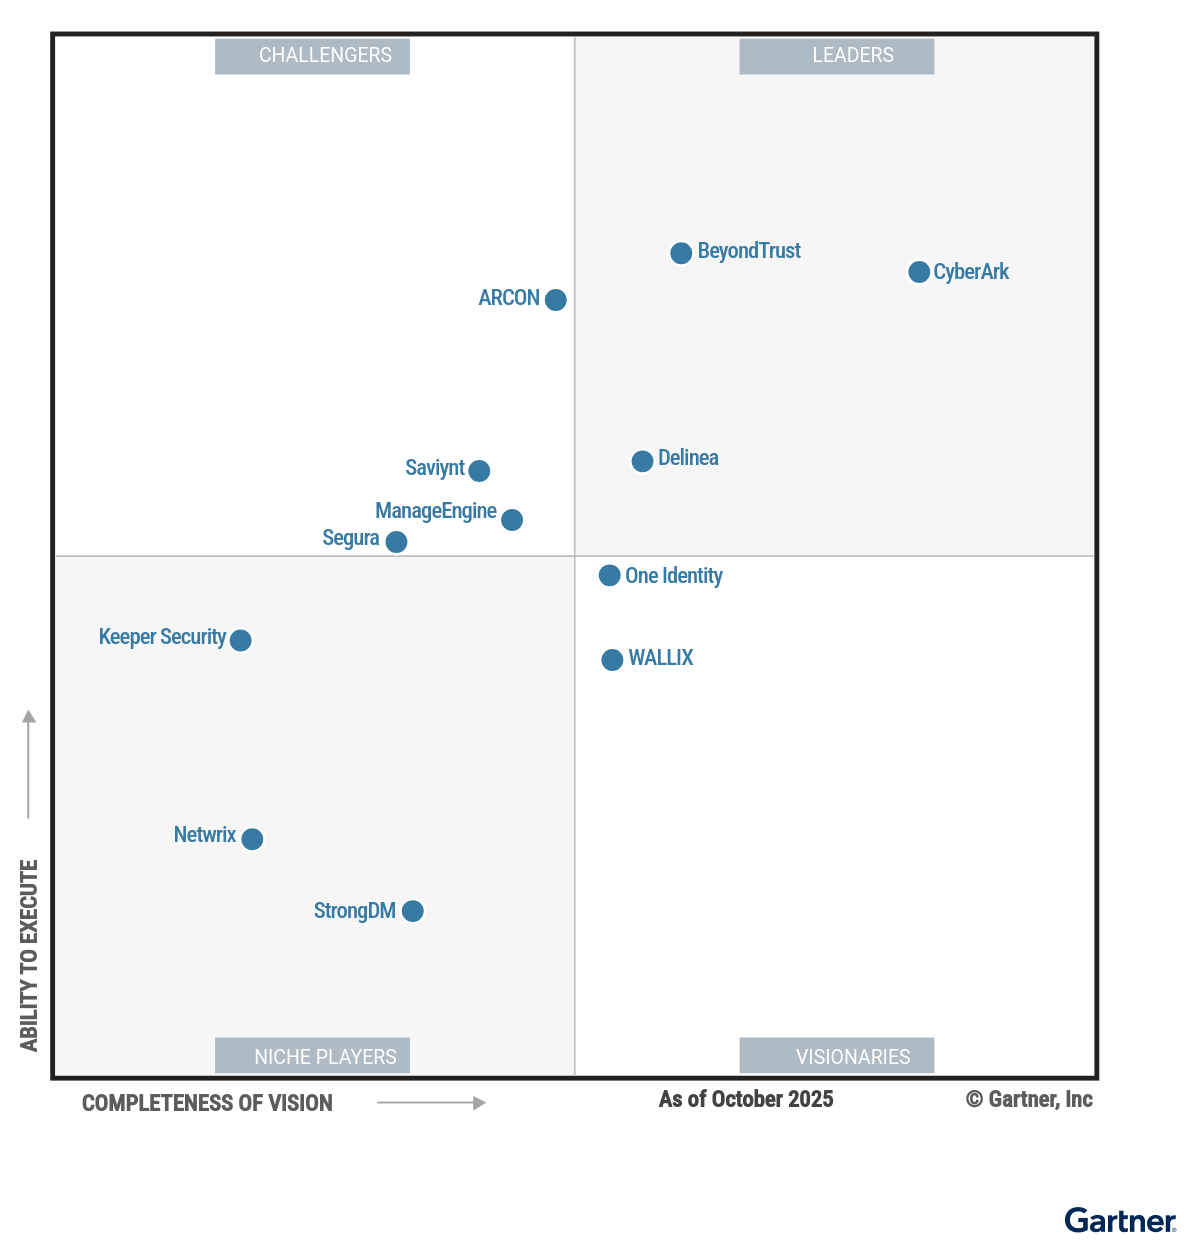
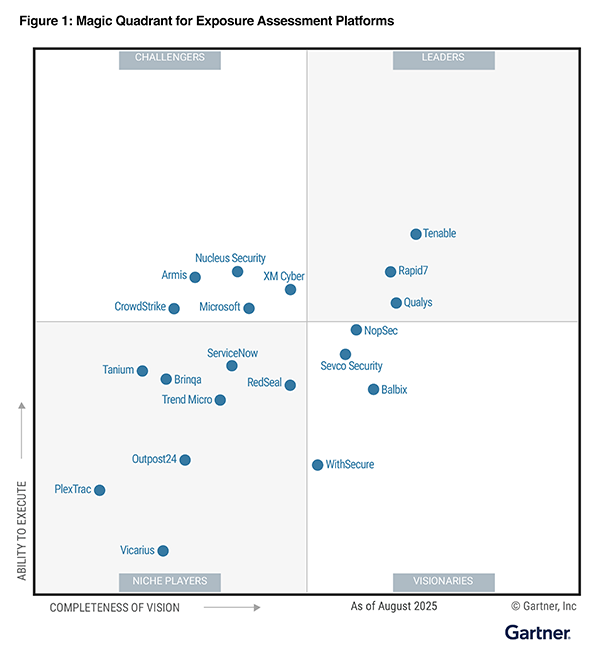
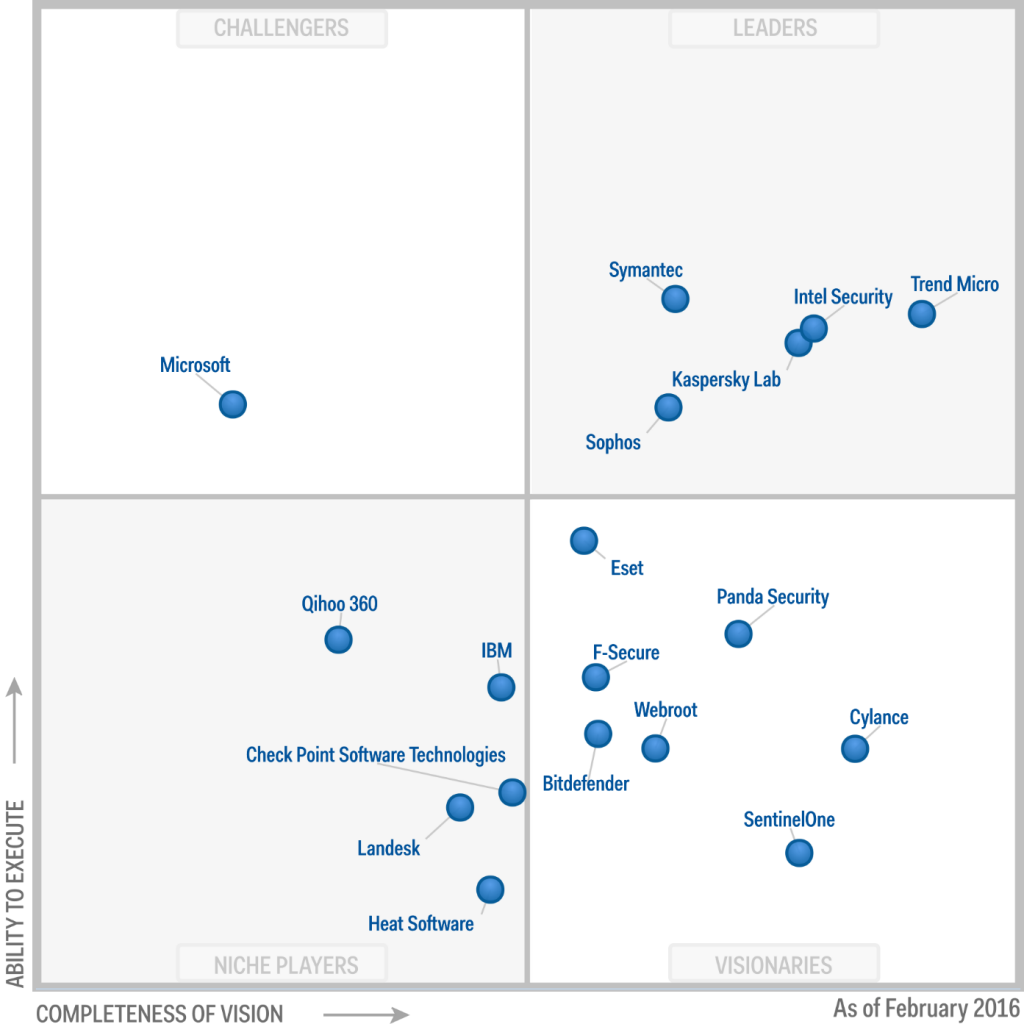
I've spent the last several years working with vulnerability management platforms across enterprise environments, and one thing that never changes is how leadership wants a data-driven recommendation when we're buying new tooling. Gartner's research reports, specifically their Magic Quadrant framework, have become the default reference point for those conversations. It's not always the most exciting process, but it does give you a structured way to narrow down vendors before the procurement team gets involved. The Magic Quadrant positions vendors across two axes: ability to execute and completeness of vision. For vulnerability assessment tools specifically, you're looking at products that scan networks, endpoints, web applications, or cloud infrastructure to find security weaknesses. The quadrant placement tells you something useful, though not everything.
What the Gartner Magic Quadrant Vulnerability Assessment Actually Covers
When Gartner publishes a report on vulnerability assessment or a closely related category like network detection and response, they evaluate dozens of criteria. These include scan accuracy, false positive rates, integration capabilities with existing security stacks, reporting quality, cloud coverage, and ease of remediation tracking. The exact criteria shift slightly year to year depending on what the market is focusing on. Vendors landing in the Leaders quadrant typically have strong execution combined with a coherent product roadmap. Challengers are executing well but may lack innovation or have a narrower focus. Visionaries score high on forward-thinking features but sometimes ship slower than they promise. Niche players serve specific use cases well but don't cover the full spectrum you'd need in a large organization. Here's what most people miss when reading these reports: the Magic Quadrant is not a ranked list from best to worst. It's a segmentation model. A vendor in the Leaders quadrant isn't necessarily the right fit for your environment, especially if your architecture, budget, or compliance requirements don't align with what they optimize for.
I encountered this directly when we were evaluating tools for a mid-size healthcare organization. The report had a well-known vendor placed firmly in the Leaders quadrant, and the initial recommendation was straightforward. But when I dug into the actual product capabilities, that vendor's platform had significant gaps in container scanning and didn't integrate cleanly with our Kubernetes environment. The quadrant placement reflected overall market presence, not our specific workload requirements. I ended up recommending a lower-placed vendor whose architecture happened to match our container-heavy infrastructure much better. The procurement team was skeptical at first, but the demo and proof of concept validated the choice, and we've been running with it for over two years now.
Get the Full Details
How to Actually Use the Report in Practice
Getting access to a Gartner Magic Quadrant report requires a subscription, which most organizations already have through their institutional access. If you don't, some of the key findings get summarized in press releases and analyst briefings, though you'll miss the detailed evaluation criteria and vendor comparisons. Once you have the report, here's how I approach it without getting lost in the noise. First, identify which specific category report is relevant. Gartner covers vulnerability assessment under different names depending on the year and market evolution. It may appear as part of a broader security testing platform category or sit alongside application security testing tools. Make sure you're reading the right one for your needs. Second, focus on the evaluation criteria section rather than jumping straight to the quadrant visualization. The criteria tell you what Gartner actually weighted in their assessment. If your organization cares more about cloud scanner coverage than on-premise network scanning, you'll want to see how heavily Gartner weighted those individual dimensions. This helps you understand whether the report's conclusions will hold up in your evaluation.
Third, cross-reference the vendor descriptions with your own requirements matrix. I typically build a simple scoring sheet covering scan types supported, integration APIs, remediation workflow support, compliance reporting templates, pricing model, and deployment options. Then I map each shortlisted vendor against it. The Magic Quadrant gives you the shortlist; your matrix does the final filtering. One practical detail that saves time: download the PDF version rather than reading the interactive web version if you plan to annotate it heavily. The PDF renders consistently across devices and lets you highlight text without losing your place when scrolling through dense vendor comparison tables.
Common Pitfalls I See Repeatedly
The most frequent mistake I encounter is treating the Magic Quadrant as a final buying decision rather than a starting point. It's market research, not a procurement recommendation. The report reflects Gartner's analyst judgment based on vendor submissions, customer references, and product demonstrations, but it does not test every tool against your specific environment. Another issue is ignoring the magic quadrant's date stamp. The vulnerability assessment market moves fast. New capabilities around agentless scanning, continuous monitoring, and cloud-native integrations emerge regularly. A report from twelve months ago may not reflect recent product shifts, especially for vendors in the Challengers or Niche Players quadrant who are actively trying to close gaps with Leaders. There's also the problem of category creep. Gartner has expanded some reports to include related capabilities like attack surface management and software composition analysis. If you're only evaluating pure vulnerability scanners, you might end up considering tools that have bloated into broader platforms you don't need and can't justify paying for.
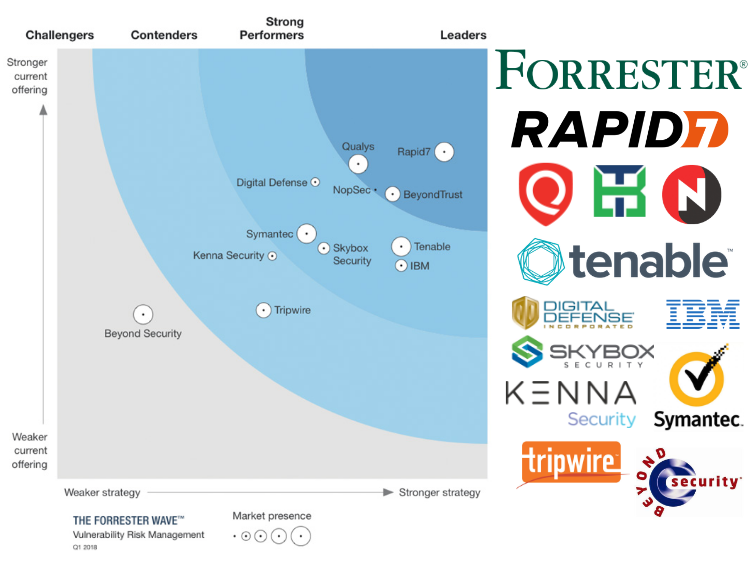
I also noticed that some organizations treat quadrant position as a signal of product maturity, but that's not always accurate. A vendor can be positioned as a Leader based on revenue and customer base while their actual product has known gaps in areas that matter to your team. Always verify claims with your own hands-on testing.
Supplementing the Report with Your Own Evaluation
After narrowing the field using the Gartner report, I always run a structured proof of concept before making a final decision. The typical process takes about two to three weeks and covers a controlled test environment with representative assets. You want to scan a mix of network infrastructure, workstations, and cloud resources if applicable, then compare how each tool handles the same targets. Key metrics to track during your proof of concept include scan accuracy on known vulnerability databases, time to complete a full network sweep, false positive rate on benign findings, quality of vulnerability descriptions and remediation guidance, and the effort required to integrate with your ticketing or incident response workflow. I usually score each vendor across these dimensions and weight them according to organizational priorities. The final vendor selection rarely comes down to a single factor. It's usually a combination of product fit, total cost of ownership including licensing and staffing, vendor stability and support quality, and how well the tool adapts to your existing security operations processes. The Gartner Magic Quadrant Vulnerability Assessment report gives you a credible foundation for that discussion, but it doesn't replace the due diligence that comes from testing the tools yourself.
If your organization doesn't have Gartner subscription access, there are alternative research sources like Forrester Wave reports and independent review platforms that cover similar ground, though the methodology and criteria weighting will differ. The principle remains the same: use the research to inform your shortlist, then validate with your own testing before committing budget.