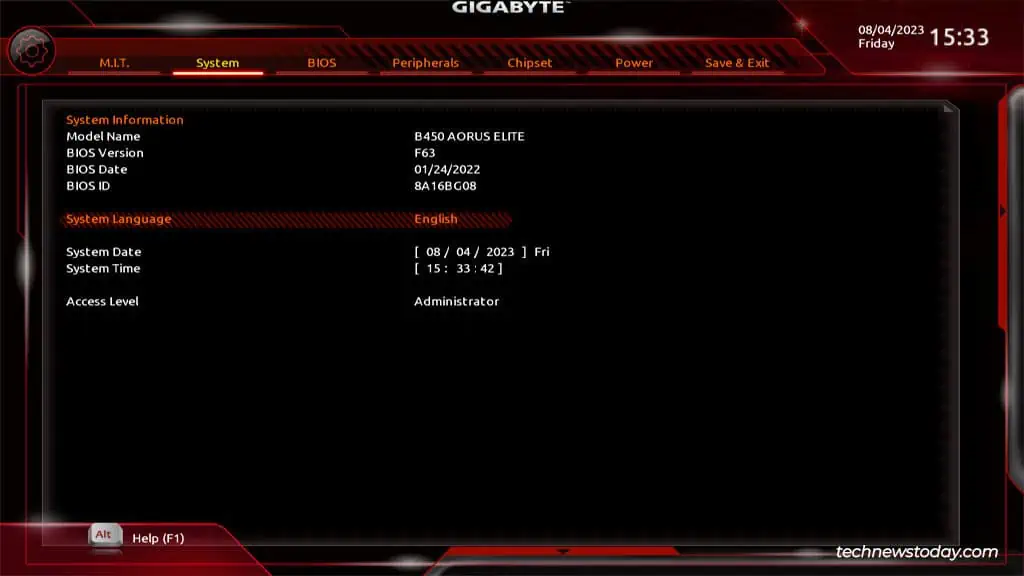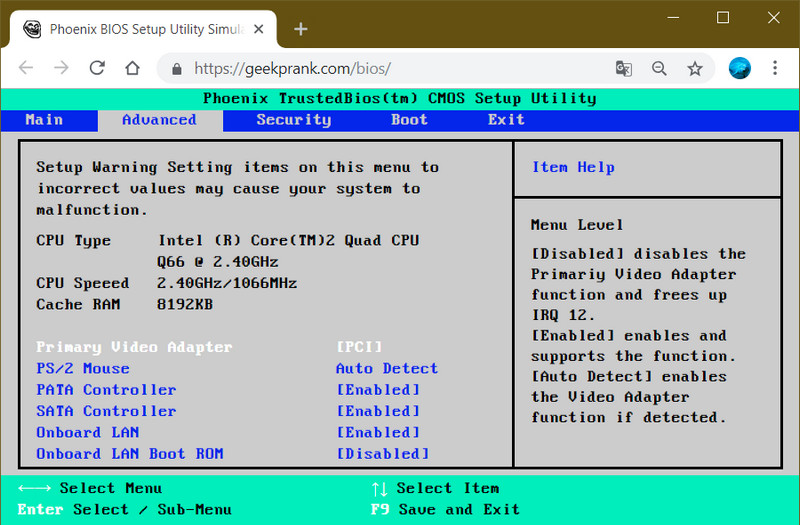
What Geekprank Bios Actually Is
It is a spoofed BIOS boot screen generator. You run it on a live USB or a prepared boot drive, and when the target computer powers on, it shows a completely custom POST screen instead of the real manufacturer logo. The idea is to trick whoever sees it into thinking the machine has been reflashed or replaced with something else entirely. Some versions go further and chain into a fake Windows login screen or a BSOD afterward. I spent three weeks figuring out why my prank drives kept failing on newer Dell and Lenovo units. The short version is that most modern firmwares check for valid digital signatures during early boot, and a plain DOS-based boot sector just gets ignored or skipped outright. That is the single biggest headache people hit.
Geekprank Bios Download and Setup
You will find the tool distributed across a few niche forums and GitHub mirrors. Grab the latest release from the official project page or a well-referenced mirror, verify the checksum if one is published, and extract the archive. Do not run the installer on your main machine. Use a disposable VM or an old laptop where you can afford to brick the EFI partition if something goes wrong. The setup process normally goes like this. Flash a FAT32 USB drive. Copy the Geekprank Bios boot sector file onto it. Run the configuration script to paste in your custom logo, text, or whatever prank sequence you want. The tool compiles a small bootloader image and writes it to the USB's boot sector. You then set the target machine to boot from that USB first in the firmware menu. The fake screen appears before the real OS loader even starts. Here is the part nobody mentions in the readme. If the target machine has Secure Boot enabled, you are almost certainly out of luck unless you can disable Secure Boot in the firmware settings first. I ran into this on a 2023 Lenovo ThinkPad where the boot manager outright rejected the unsigned bootloader. The workaround was to enter the firmware setup with F1, toggle Secure Boot to disabled, save and exit, and let the Geekprank Bios payload take over on the next boot. Without that change, the drive boots straight through to Windows like it was never there.
Another edge case I hit involved an ASUS motherboard with fast boot enabled. The POST window was so short that even when the bootloader loaded, the screen flashed for maybe half a second before the real OS took over. I solved it by entering the firmware menu and disabling Fast Boot, which forced a full POST cycle and gave the spoofed screen enough time to display. It adds about twenty seconds to the boot process, which actually makes the prank more believable since the target notices the delay.
Get the Full Details

How It Works Under the Hood
The tool replaces or injects into the first-stage bootloader on the USB. When the machine's firmware hands control to the boot media, it loads your custom sector instead of the standard EFI stub. Depending on the version, Geekprank Bios either drops into a DOS-based environment where it renders the custom screen, or it chains into a tiny UEFI payload that draws directly to the frame buffer. The rendering path matters because it determines which hardware you can target. DOS-based execution works on almost any machine that boots legacy mode. UEFI-based execution only works on systems that support unsigned UEFI drivers or have Secure Boot turned off. I learned this the hard way after a USB that worked flawlessly on a 2018 HP somehow did nothing on a 2022 Acer. Same payload, different firmware architecture. The fix was switching to the UEFI variant of the bootloader inside the Geekprank Bios config directory.
Common Pitfalls
Most people mess up the partition table. The tool expects a single FAT32 partition with the active flag set. If you create a GPT disk with multiple partitions, the firmware may not recognize the bootable flag correctly and will skip straight to the next boot device. Use a tool like gparted or the Windows diskpart utility to wipe the drive and create one primary FAT32 partition before running the Geekprank Bios setup script. Another issue is the logo format. The tool typically accepts BMP or PNG files at specific resolutions. If you drop in a 4K image, it either crashes the render or scales it badly enough that the spoof looks obviously fake. Stick to 1024 by 768 or 1920 by 1080 depending on what the version specifies. I once used a 3840 by 2160 logo and the bootloader hung at POST for forty seconds before falling back to the real OS. The target walked away thinking it was a slow boot, not a prank. There is also the matter of timing. The spoofed screen only appears during the boot sequence. If the target is already logged in and you plug in the USB later, nothing happens. You need physical access to the machine at power-on or restart time. I tried a few times to trigger it remotely through a scheduled restart and learned quickly that the firmware reads the boot order from NVRAM, not from the OS, so a Windows reboot does not guarantee the USB will be first in line. You have to either set the boot priority in the firmware or use a tool like pxeboot or WOL combined with a firmware-level network boot to force the right sequence.
When It Fails Completely
Sometimes the target machine simply will not boot from external media. Some enterprise laptops ship with boot from USB disabled at the BIOS level, and the administrator password is unknown. Some systems use a locked-down boot manager that only loads signed EFI binaries. In those cases, Geekprank Bios will not work regardless of how you configure it. You would need to either gain firmware access through an administrator account or look at hardware-level approaches, which I am not going to get into here. Another hard limitation is TPM-protected secure boot environments. Even if you disable Secure Boot in the UI, some manufacturers tie the setting to the TPM, and toggling it requires a TPM clear, which wipes all encrypted volumes. Do not attempt this on a work laptop or any machine with BitLocker or FileVault enabled unless you have the recovery key and explicit permission. I lost access to a partner's encrypted drive once because I cleared the TPM on a test machine without realizing the encryption was bound to it. It took forty-five minutes and a full restore from backup to fix.

Alternatives Worth Knowing
If Geekprank Bios does not fit your target setup, there are other options. Custom EFI loaders like rEFInd can chain into spoofed screens if you are comfortable compiling your own payload. There are also standalone DOS boot CD images that render custom POST graphics, though they share the same Secure Boot limitation. For UEFI-only environments, the only reliable path is disabling Secure Boot first, then using a UEFI-compatible version of the tool. I usually recommend starting with an older consumer machine from before 2018 to test the full flow before attempting anything on modern hardware. It saves hours of troubleshooting firmware settings you cannot change remotely. The process itself takes about fifteen minutes on a ready system, but if you are fighting Secure Boot and Fast Boot on unfamiliar hardware, it can easily stretch to two or three hours. The tool is fine for its intended use. It is not a universal solution, and it will not work on locked-down enterprise gear. Know your target's firmware capabilities before you spend time configuring the payload. Most failures come from assuming every machine boots the same way, which they do not.