Using Geekprank Hacker Prank Simulator Without Looking Like a Fool
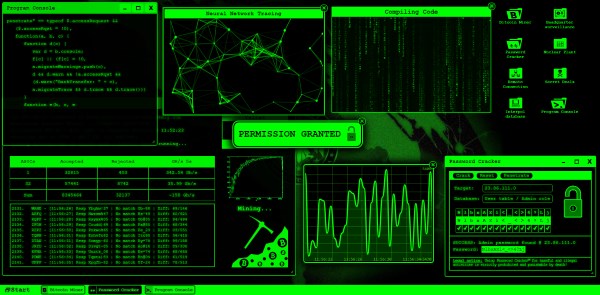
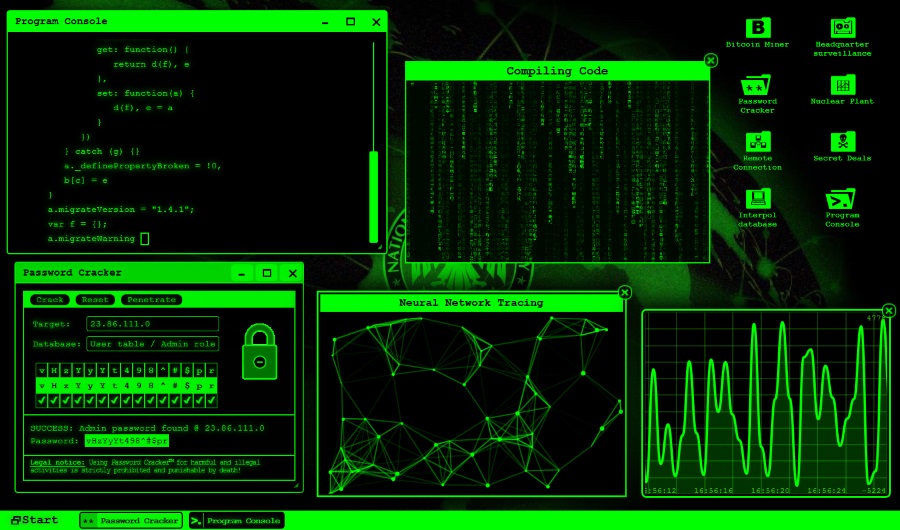
The tool runs in a browser. You open it, pick a scenario, and hit start. It's that simple, and that's also why it gets messy fast. I've set this up for people at parties, in offices, and once on a buddy's monitor while they were trying to finish a presentation. It works, but only if you understand what you're actually running. You don't download anything for the main version. It's hosted at geekprank.com and loads directly in your browser. There are different themed interfaces: a hacker terminal, a Matrix-style rain, a fake blue screen, and the one most people ask about, the simulated hacking screen that makes it look like someone is breaking into an account or system in real time. You set a target username or message, customize the text, and hit prank. The page goes fullscreen. Code scrolls. Progress bars fill. It's designed to look convincing from three feet away, which is about how close someone gets before they realize it's just JavaScript running a loop. The core mechanism is straightforward. The page renders a canvas or DOM-based animation that cycles through pre-written script blocks. Fake IP addresses generate randomly. Terminal-style text scrolls faster than anyone can read it. Progress bars animate with arbitrary percentages. Some versions let you insert a custom message that appears at the end, like "YOU ARE HACKED" or a personalized threat. That's it. It's a visual effect, not actual code execution of any kind.
I learned the hard way that the fullscreen API doesn't always cooperate on Chrome when the page isn't launched from a direct user gesture. My first attempt at this back in 2021 I opened the link on a laptop, tabbed away to check something, and came back to find the browser had dropped out of fullscreen mode. The victim was staring at a tiny non-fullscreen window and basically seen the whole thing. Not ideal. The workaround is simple but easy to miss: you have to trigger the fullscreen command from a click event on the page itself, not from an external shortcut or keyboard combination. Set it up on a separate device if you're doing this remotely, or make sure you click the actual prank button with the mouse before walking away. A keyboard-initiated fullscreen call gets blocked by the browser as a anti-popup measure, and nobody warns you about that.
The Scenarios and What They Actually Do
There are usually four or five prank types available depending on which page version you land on. The hacker screen shows scrolling code with a target account being "breached." The virus warning screen mimics a Windows alert telling you your computer is infected and needs to call a support number. The matrix screen gives you the green falling characters from the movie. The face recognition one pretends to scan someone's face and declare them a criminal. Each one runs identically under the hood, just with different visual assets. Most people grab the hacker screen and customize the text before launching. You can type in a name, a fake location, and whatever message you want displayed when the progress hits one hundred percent. The customization box is usually small and easy to overlook. Some versions have a limit of about two hundred characters, so keep it short. Longer messages get truncated or break the layout, which defeats the whole point. One thing beginners miss is that the speed setting matters more than the text. The default scroll speed looks obviously automated to anyone who's worked with actual terminals. Cranking it up to the fastest setting makes it look more authentic because real debugging sessions and packet captures scroll unpredictably fast. The slow version just looks like a screensaver. If you're going for the scare factor, max out the speed and minimize the amount of readable text so people can't catch words as they fly by.
Get the Full Details

There's also a timing consideration nobody talks about. The progress bar on most versions runs for roughly thirty to sixty seconds before it loops back or hits completion. That means if someone interrupts you mid-prank, you have maybe twenty seconds before they see the reset or the ending screen. Plan accordingly. The ending screen is where the custom message appears, and if it's something embarrassing rather than scary, you've just ruined the joke.
What People Get Wrong
The biggest mistake is assuming this works on mobile phones the same way. It doesn't. The fullscreen API behaves differently on iOS and Android, and many of the animations are optimized for desktop resolutions. On a phone it often just looks like a weird webpage that won't expand. If you want to prank a phone, use a different tool or find a mobile-specific version. I tried this on an iPhone once and spent five minutes watching a tiny non-responsive page instead of pulling off the prank. Wasted time and zero laughs. Another issue is browser tabs. Some versions require the page to stay in the foreground tab to maintain performance. Switch to another tab and the animation throttles down to save resources. The scrolling slows to a crawl, the progress bar freezes, and the whole illusion falls apart. Keep the prank tab active and don't alt-tab away unless you want the effect to lag visibly. There's also the sound question. Some versions include audio, some don't. If it has sound, it's usually a generic typing or server noise track that loops. It can be useful for adding atmosphere, but it can also blow out speakers if someone has headphones on. Test the volume before launching, or mute it entirely and rely on visuals. Audio makes it obvious immediately that something is playing rather than actually happening.
Limitations and When It Completely Fails
This tool has real limitations. It only runs while the browser tab is open. Close the tab and it stops. Refresh the page and you start over. It does not actually access any systems, send packets, or interact with networks. Anyone who knows what they're looking at will spot the static HTML structure within seconds. The fake IP addresses don't resolve to real locations in any meaningful way, and the "hacking" animations are purely cosmetic loops. It also requires internet access to load. If you're at a location with poor connectivity, the page might not render properly, or assets could fail to load and leave you with a broken interface. Downloading the page as a local HTML file is possible on some versions, but not all, and the local copy might not include all the assets or scripts needed for full functionality. If you need something more robust for recurring use, consider hosting a local copy on a USB stick or configuring a simple Apache server. That eliminates the internet dependency and gives you more control over the timing and appearance. But for one-off pranks, the web version is fine if you account for the constraints above.

Where to Access It
The primary entry point is geekprank.com. Navigate to their hacker prank section, select your scenario, customize the text fields, and launch. The process takes about two minutes from open to fullscreen. No registration, no payment, no software installation. Just a browser and a target who's sitting nearby. If the main site is down or you want an offline version, a few mirrors and forks exist on GitHub, but they vary in quality and may be outdated. The official site updates its templates periodically, so the most current version is always the best starting point. Check the comments or feedback section on the site for any known issues with specific browsers or operating systems. I've used this dozens of times over the years and it still gets genuine reactions when set up correctly. The key is understanding the mechanics, not just hitting the button and hoping for the best. Know the fullscreen gotchas, speed up the animations, keep the tab active, and don't overcomplicate the message. A clean thirty-second panic beats a confused two-minute exploration every time.