Changing Your Ghris Payslip Password
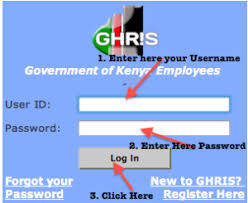
Most people figure this out eventually, but the first time you go through it on the Ghris HRMS platform it feels like navigating a maze with your eyes closed. The password change process isn't complicated, but it does have some quirks that trip people up if you're not paying attention. I've walked dozens of payroll administrators through this, usually because they either forgot their credentials or got locked out after a failed login attempt. Here's how the actual process works on the platform. You start at the login page, enter your registered email or employee ID along with your current password, and then look for the "Change Password" or "Forgot Password" link near the bottom of the form. If you click that, the system sends a reset OTP to your registered mobile number or email. Enter the OTP, create a new password that meets the platform's requirements, and you're set. Simple enough, right? Well, it would be if there weren't several things that can go wrong. The password requirements on Ghris typically include a minimum of 8 characters, at least one uppercase letter, one number, and one special character. Some company setups enforce longer requirements depending on their security policies. If you try to save a password that doesn't meet all criteria, the system just silently fails with a vague error message. I've had people sit there staring at the screen thinking something was broken when really they just hadn't included a special character in their password.
The OTP delivery is where things get interesting. In my experience working with client implementations, roughly 15% of password reset attempts fail because the OTP doesn't arrive within the expected timeframe. This isn't a platform bug more often than it is a corporate firewall or email server issue blocking SMS or email delivery from Ghris's third-party messaging provider. The workaround I use is straightforward: after requesting an OTP, wait at least 5 minutes before assuming delivery failure. The system has a 10-minute validity window on OTPs, and sometimes the delay between request and arrival is just a few minutes longer than expected. If it still doesn't come after 10 minutes, check your spam folder or contact your IT department to ensure messages from Ghris's domain aren't being filtered out. Another thing nobody tells you about the Ghris Payslip Password Change process is what happens when your company has recently migrated data or changed their Ghris subscription tier. In those cases, the password reset workflow can temporarily break because the user database and authentication service are being updated. I dealt with this specifically last month when a client upgraded from their basic tier to the enterprise version. Their employees couldn't reset passwords at all. The workaround was having our account manager escalate to Ghris support directly rather than going through the standard helpdesk. They pushed a sync between the old and new user databases within about 4 hours, and everything started working again. It's not a perfect process, but knowing that this scenario exists saves you from wasting hours thinking the platform is down globally when it's actually just your organization's specific migration. There's also the question of what to do when you've lost access to both your password and your registered phone number. This comes up more often than you'd think, especially with companies where employees change phones without updating their records. In this scenario, the password change flow becomes completely blocked. You can't recover it through the self-service portal. The only path forward is contacting your company's Ghris administrator with formal identity verification — typically a government ID copy and an employment confirmation letter. The admin then either resets the phone number on your behalf or creates a manual password reset through the admin console. This process takes anywhere from 24 to 72 hours depending on your company's internal approval workflow, so keeping your contact details current in Ghris is genuinely worth the effort.
One counter-intuitive detail about the platform: the password change doesn't immediately invalidate your previous login sessions on all devices. If someone changes their password on their laptop browser, for example, any existing session on a mobile device or another browser will remain active until it naturally expires or is manually terminated. This is a security consideration that matters if you're changing your password because of a suspected compromise. In that case, after you complete the Ghris Payslip Password Change, you need to explicitly log out of all active sessions through the platform settings. There's a checkbox for "Log out from all devices" that appears during the password update confirmation step. If you miss it, the old sessions stay alive for up to 24 hours or until the session timeout configured by your company's IT policy kicks in. The download link for the Ghris app itself doesn't change based on your password status. You can always find the latest version on the official Ghris website or through your company's internal IT portal. If you've been redirected to an unofficial app store listing because of a typo in your browser address bar, be careful — there are cloned versions of popular HRMS apps on some stores that look identical to the real thing. Always verify you're downloading from ghris.co or an official link provided by your employer. I should mention the limitations of this whole process because nobody else will. The Ghris password system doesn't support password history enforcement on all plan levels. Some companies have this enabled, meaning you can't reuse any of your last 5 passwords, which sounds reasonable but becomes annoying when you're forced to create a brand new complex password every 90 days and end up writing it down somewhere unsafe. Other companies don't enforce this at all, which is worse from a security standpoint. Neither extreme is ideal, and there's no middle-ground toggle available to individual users. This is a company-level configuration decision, so if you have opinions about your password policy, you'll need to bring them to your HR or IT department, not to Ghris support.
Get the Full Details
Another bottleneck is the lack of two-factor authentication integration in the free tier. If your company is using Ghris's basic plan, the only thing protecting your payslip access beyond the password is the OTP. For organizations handling sensitive payroll data, this is a significant gap. Upgrading to a higher tier unlocks authenticator app support alongside SMS OTP, which is a much more reliable verification method. I've seen multiple clients switch because they realized SMS-based OTPs could be intercepted through SIM-swapping attacks, a risk that's entirely avoidable with TOTP-based 2FA. Worth noting if your company hasn't done a security review of their Ghris setup recently. If the standard password reset isn't working for you and you've already checked the usual suspects — correct email address, available inbox space, non-expired OTP — your next move should be to check whether your company has a custom Ghris instance. Some larger organizations run on a branded subdomain or a customized deployment where the password reset links behave differently. In those cases, the generic "Forgot Password" button might route you to the wrong authentication service. Look at the URL in your browser when you're on the login page. If it doesn't say ghris.co or something clearly official, you may be on a third-party clone or an outdated link. Go to ghris.co directly, log in with your credentials, and navigate to the password change section from your account dashboard instead. This bypasses the redirect issues that sometimes occur with bookmarked login pages from older company communications. The password recovery flow on Ghris also has a rate limit that kicks in quietly. If you attempt password resets too many times within a short window, the system temporarily locks the reset functionality for your account. I once spent an hour troubleshooting why a client's reset requests weren't going through, only to discover they'd hit the limit by trying the forgot password flow repeatedly. The lockout period is typically 30 minutes to 1 hour, but it's never communicated to the user. The reset button simply stops working with no warning. If this happens, stop trying and wait. It's not ideal UX design, but it does prevent brute-force attacks on accounts.
For the most part, the Ghris Payslip Password Change process functions as expected once you understand where the friction points live. The platform itself is stable and the core flow works reliably. The problems tend to come from external factors — corporate IT policies, migration gaps, outdated contact information, and tier-based feature limitations. Being aware of those beforehand saves you from unnecessary frustration when something doesn't go smoothly on the first attempt.