Building a GLBA Risk Assessment That Actually Holds Up
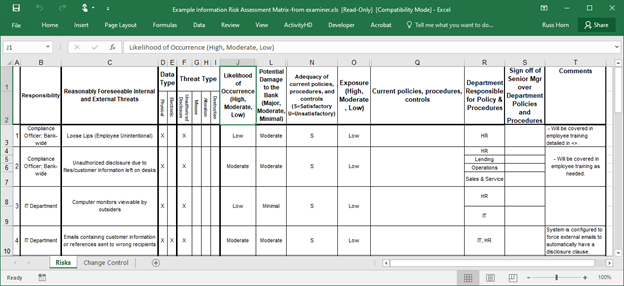
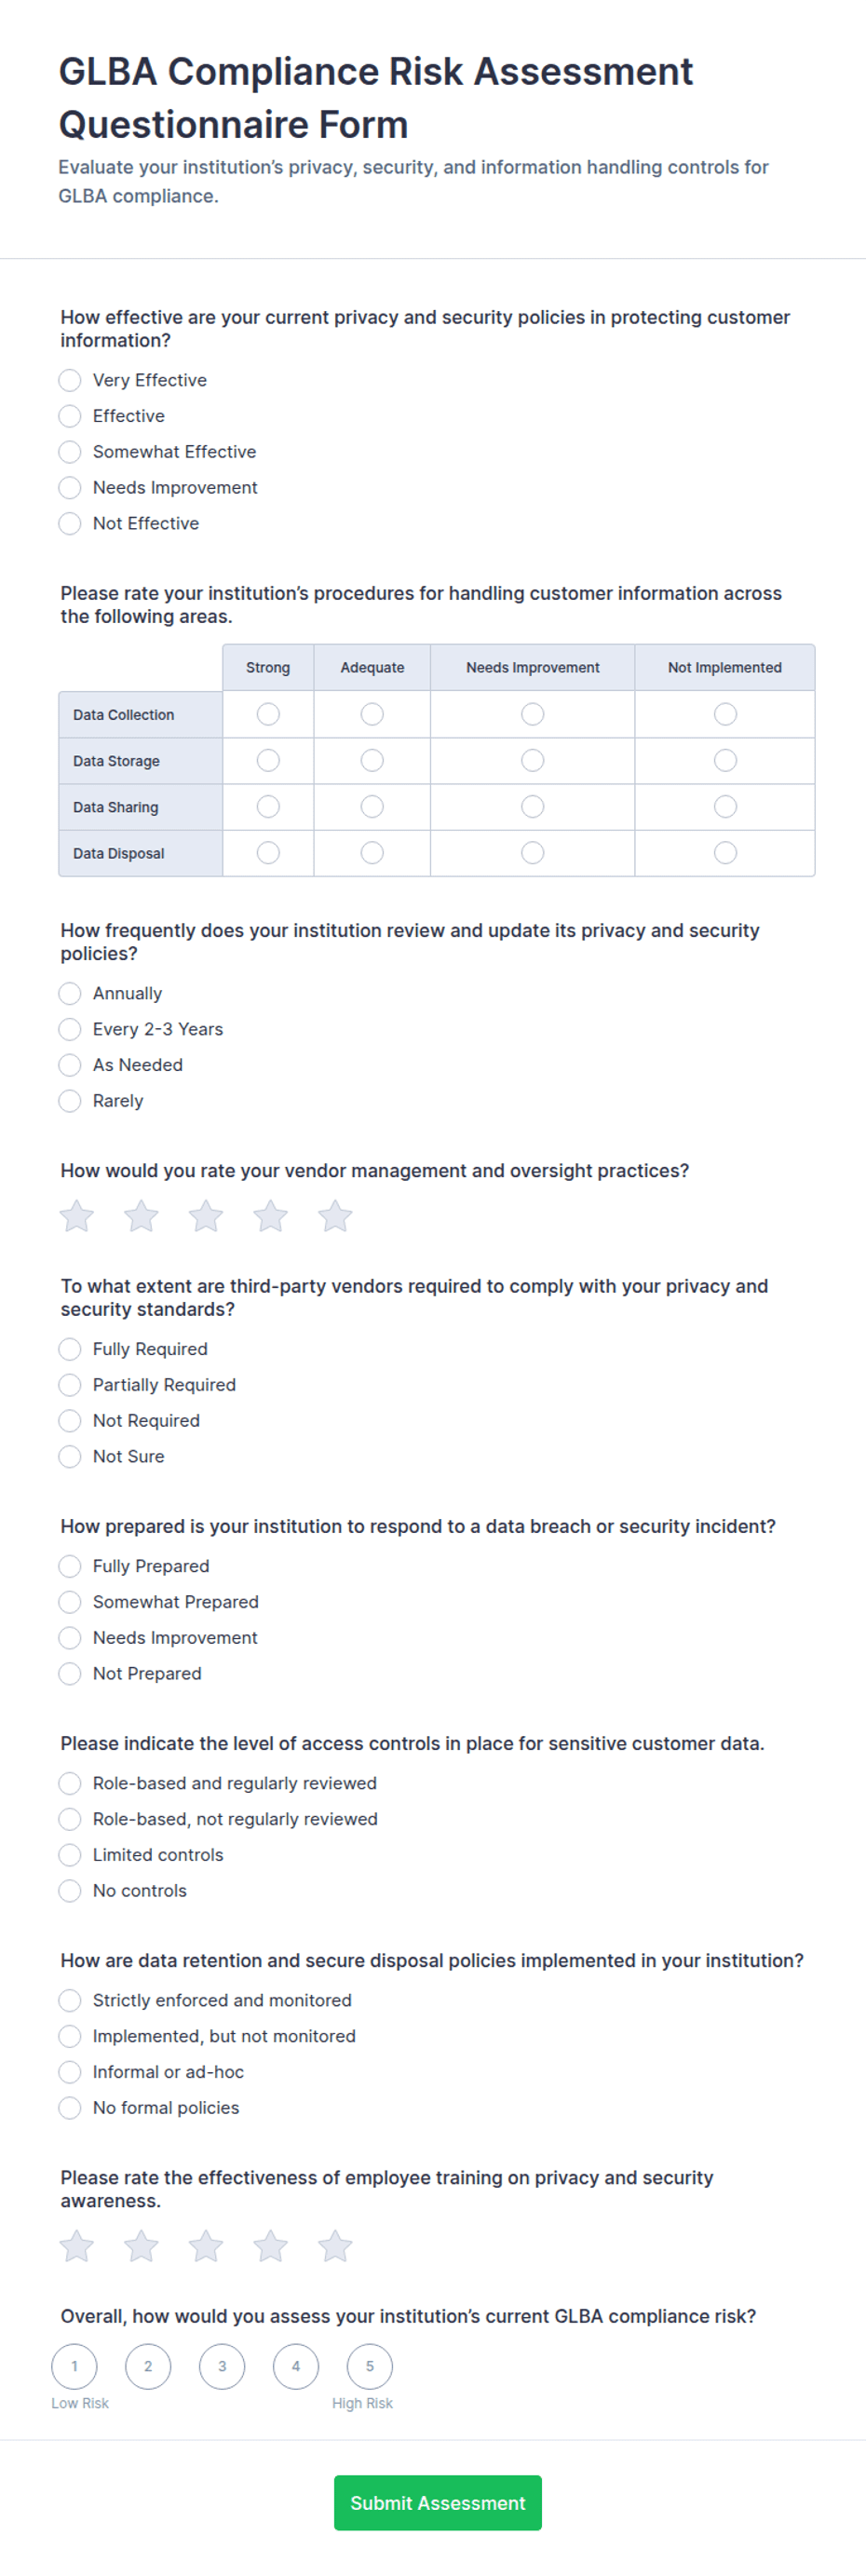
The Gramm-Leach-Bliley Act requires financial institutions to maintain a written information security program, and the risk assessment portion is where most people trip. A spreadsheet-based Glba Risk Assessment Template Excel can work if you build it correctly, but most templates I've seen online are missing critical fields that auditors actually look for. Here's how to approach it without wasting weeks on a document that falls apart during review. You need columns for asset identification, threat categorization, vulnerability mapping, likelihood scoring, impact scoring, and residual risk after controls. That sounds standard until you realize most free templates stop at likelihood and impact. The gap is the residual risk calculation and the control mapping section. Without those, you're documenting risks but not demonstrating you understand what you're doing about them. I built my first proper GLBA risk assessment in 2018 using a downloaded template from what felt like a compliance resource site. Six months later, an auditor asked me to show how we had mitigated each identified risk and I couldn't because the template had no mitigation column. I spent three days rebuilding it from scratch with conditional formatting, data validation, and a controls matrix that linked directly back to assessment entries. The whole thing took about eight hours instead of the two hours it should have taken initially.
What Your Template Needs to Cover
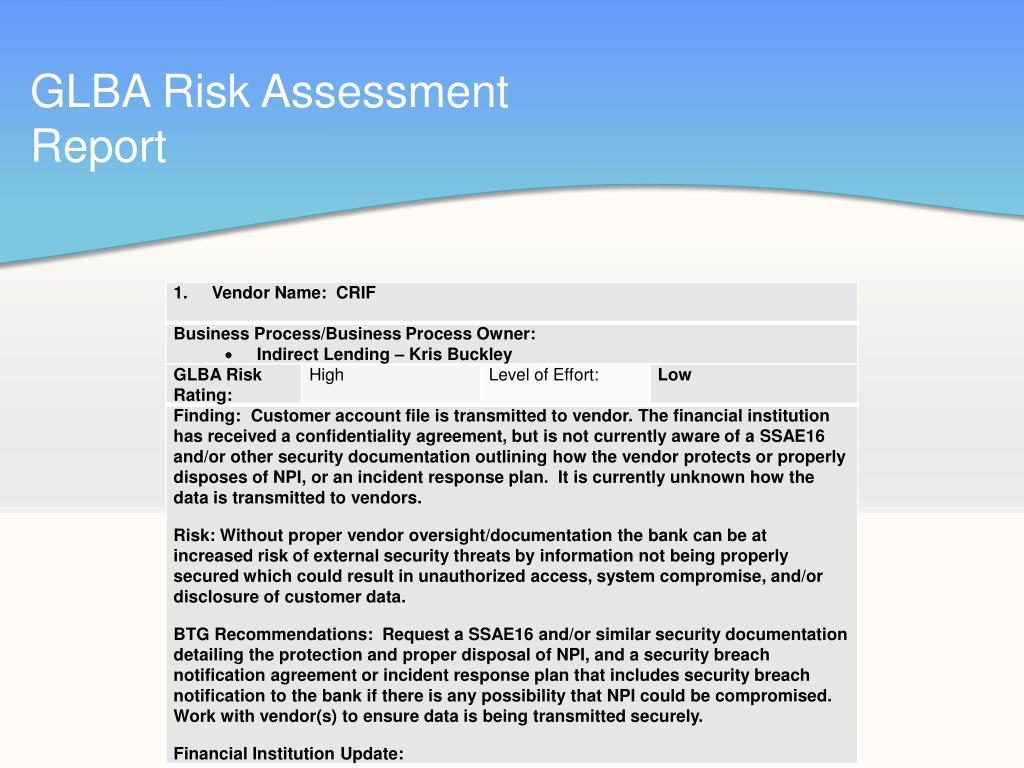
GLBA doesn't prescribe a specific format, which means you have flexibility but also zero guidance on what passes scrutiny. The Safeguards Rule expects a risk assessment that identifies "reasonable and appropriate safeguards." That language matters because it means your assessment has to demonstrate reasonableness, not just completeness. Your template needs a section for nonpublic personal information identification. You need to catalog what NPI you collect, process, and maintain. This includes customer information as defined under Regulation P. Most people skip the PPI versus NPI distinction and just lump everything together, but regulators have started asking about this during examinations. You also need a vendor management component. GLBA risk assessments must address third-party service providers who handle customer information. I once encountered a credit union that had mapped 47 vendors in their assessment but hadn't verified which ones actually received NPI. The auditor flagged this immediately because they couldn't distinguish between vendors that processed payments and vendors that had access to customer data. We ended up adding a vendor NPI exposure column with a Yes/No dropdown and a follow-up verification date field.
Scoring Methodology That Won't Get Challenged
Most templates use a simple 1-to-5 scale for likelihood and impact. This works fine internally but creates problems during audits because there's no documented justification for the scores you assign. I recommend adding a score rationale column where you note the basis for each rating. A single sentence explaining why a particular system gets a likelihood of 4 instead of 3 is enough. Here's a counter-intuitive point that most people miss: you don't need sophisticated statistical probability modeling for GLBA compliance. The rule is about reasonable safeguards, not actuarial precision. A basic qualitative scoring matrix with clear documentation behind each score is more defensible than a complex quantitative model with unverifiable assumptions. I've seen institutions get more questions from examiners when they tried to build elaborate mathematical risk formulas than when they used straightforward qualitative assessments with solid supporting documentation. The scoring matrix should cross-reference likelihood against impact to produce a risk level category. Low, medium, high, and critical give you enough granularity for a small to mid-size financial institution. Anything beyond that and you're spending more time defending your scoring criteria than managing actual risk.
Get the Full Details

Automation Features Worth Adding
Excel has enough functionality built in to make this template manageable for ongoing use. Conditional formatting can automatically color-code risk levels based on your calculated scores. Data validation prevents people from entering text in numeric columns, which causes more formula errors than you'd expect. A VLOOKUP or XLOOKUP function can pull control descriptions from a separate controls register so you aren't manually retyping information. I set up a dashboard sheet that pulls summary statistics from the main assessment using COUNTIF formulas. It shows total risks by category, count of critical risks requiring executive attention, and the percentage of identified risks that have documented mitigation plans in place. Management reviews this dashboard monthly and it reduces the risk assessment discussion from twenty minutes to about four during board meetings.
Where Spreadsheet Templates Fail
A spreadsheet-based Glba Risk Assessment Template Excel works well for organizations with under 200 risk items and stable operating environments. Once you exceed that threshold or have frequent changes to systems and processes, manual updates become error-prone. I've seen risk assessments become stale because someone updated one row but forgot to refresh the summary calculations. The formulas themselves stay correct but the underlying data becomes unreliable. Another limitation is version control. Spreadsheets don't track changes natively unless you enable shared workbook features, and those features often cause corruption. I recommend using file naming conventions with dates and maintaining an archive of previous versions rather than relying on Excel's built-in change tracking. One institution I worked with lost an entire quarter's assessment data when a corrupted shared workbook overwrote the master file. If your organization grows beyond what a spreadsheet can handle cleanly, there are dedicated GRC platforms that support GLBA risk assessment workflows with automated reminders, audit trails, and integrated vendor management. But those tools cost anywhere from $15,000 to $50,000 annually depending on institution size, and many community banks and credit unions find the spreadsheet approach sufficient when built properly.
Practical Setup Steps
Start by listing every system that stores, processes, or transmits nonpublic personal information. Don't estimate. Actually inventory the systems. During a recent engagement, I found a pension fund that had documented fifteen systems in their risk assessment but their actual network showed forty-three assets handling customer data. The gap created a compliance blind spot that exposed them to regulatory action. Next, identify threats for each system. Threat categories under GLBA typically include unauthorized access, data breach, system failure, and natural disasters. Map vulnerabilities to each threat. A vulnerability isn't the same as a threat. The firewall having outdated signatures is a vulnerability. A targeted attack exploiting those outdated signatures is the threat. Then apply existing controls and calculate residual risk. This is the step most people rush through. Your template should force a comparison between inherent risk (risk before controls) and residual risk (risk after controls). The difference tells you whether your controls are actually effective or just documented on paper.
A Specific Edge Case Worth Noting
Cloud-based services create assessment complications that basic templates don't address. When a financial institution uses a cloud provider like Amazon Web Services or Microsoft Azure, the risk assessment needs to account for shared responsibility models. The institution remains responsible for protecting NPI even though the cloud provider manages infrastructure security. I encountered a situation where an institution had marked all cloud infrastructure risks as "mitigated" because their provider was SOC 2 Type II certified. The auditor rejected this because SOC 2 certification doesn't automatically satisfy GLBA requirements for specific safeguard documentation. The workaround was adding a cloud risk sub-section that referenced the provider's attestation reports and documented the specific controls the institution maintained independently. The template needs a column for regulatory references so you can cite which safeguard requirement each risk addresses. GLBA sections, FFIEC guidelines, and state-level requirements all add different expectations. Having the reference mapped directly to each risk item makes it much easier to demonstrate compliance coverage during an examination.
Final Notes on Maintenance
Set a review schedule into your template. GLBA expects periodic reassessment, and annual review is the standard expectation. Add a next review date column that triggers alerts when dates approach. An assessment that hasn't been reviewed in eighteen months raises questions during audits regardless of how thorough the content is. Keep the template version number and last update date visible on the first sheet. Auditors check these things without always telling you they're checking them. A template without version information looks improvised rather than managed, and that perception affects how every other section of your assessment gets evaluated.