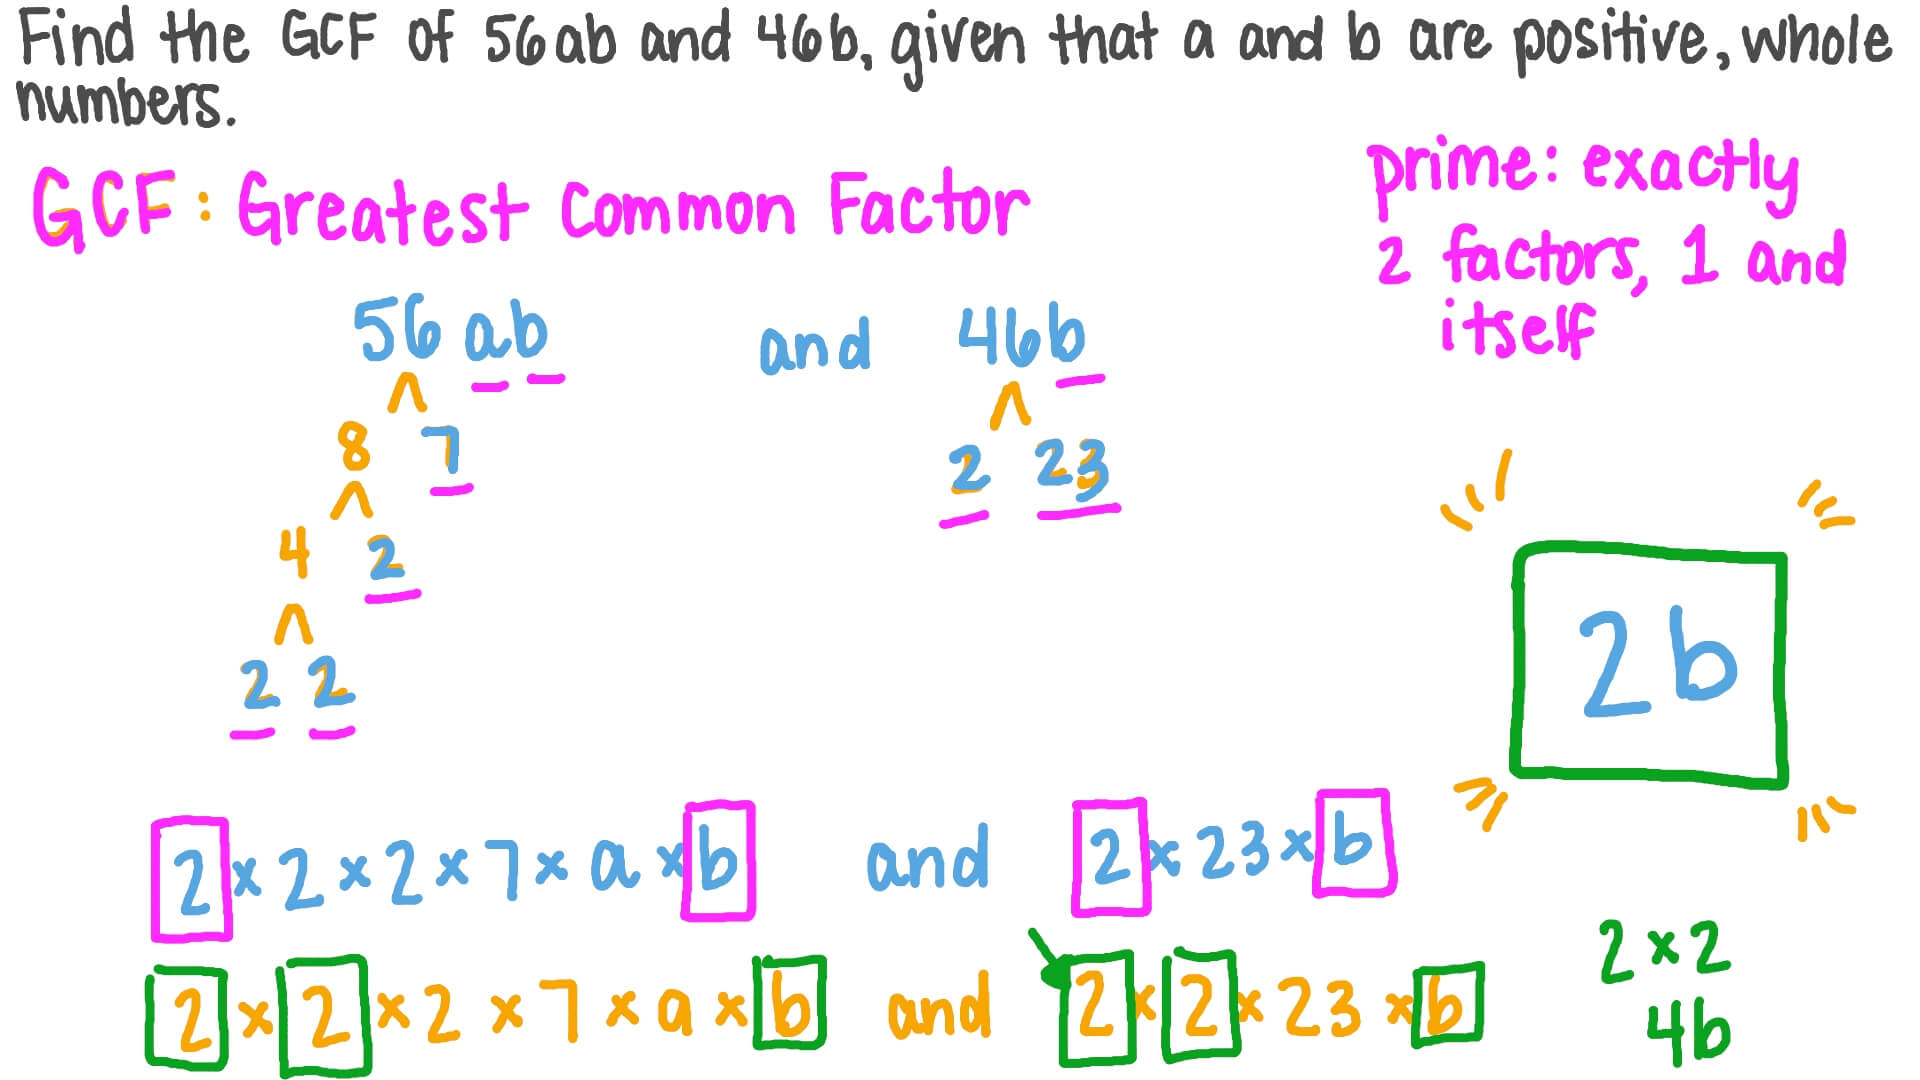
Understanding GCF Through Real Problems
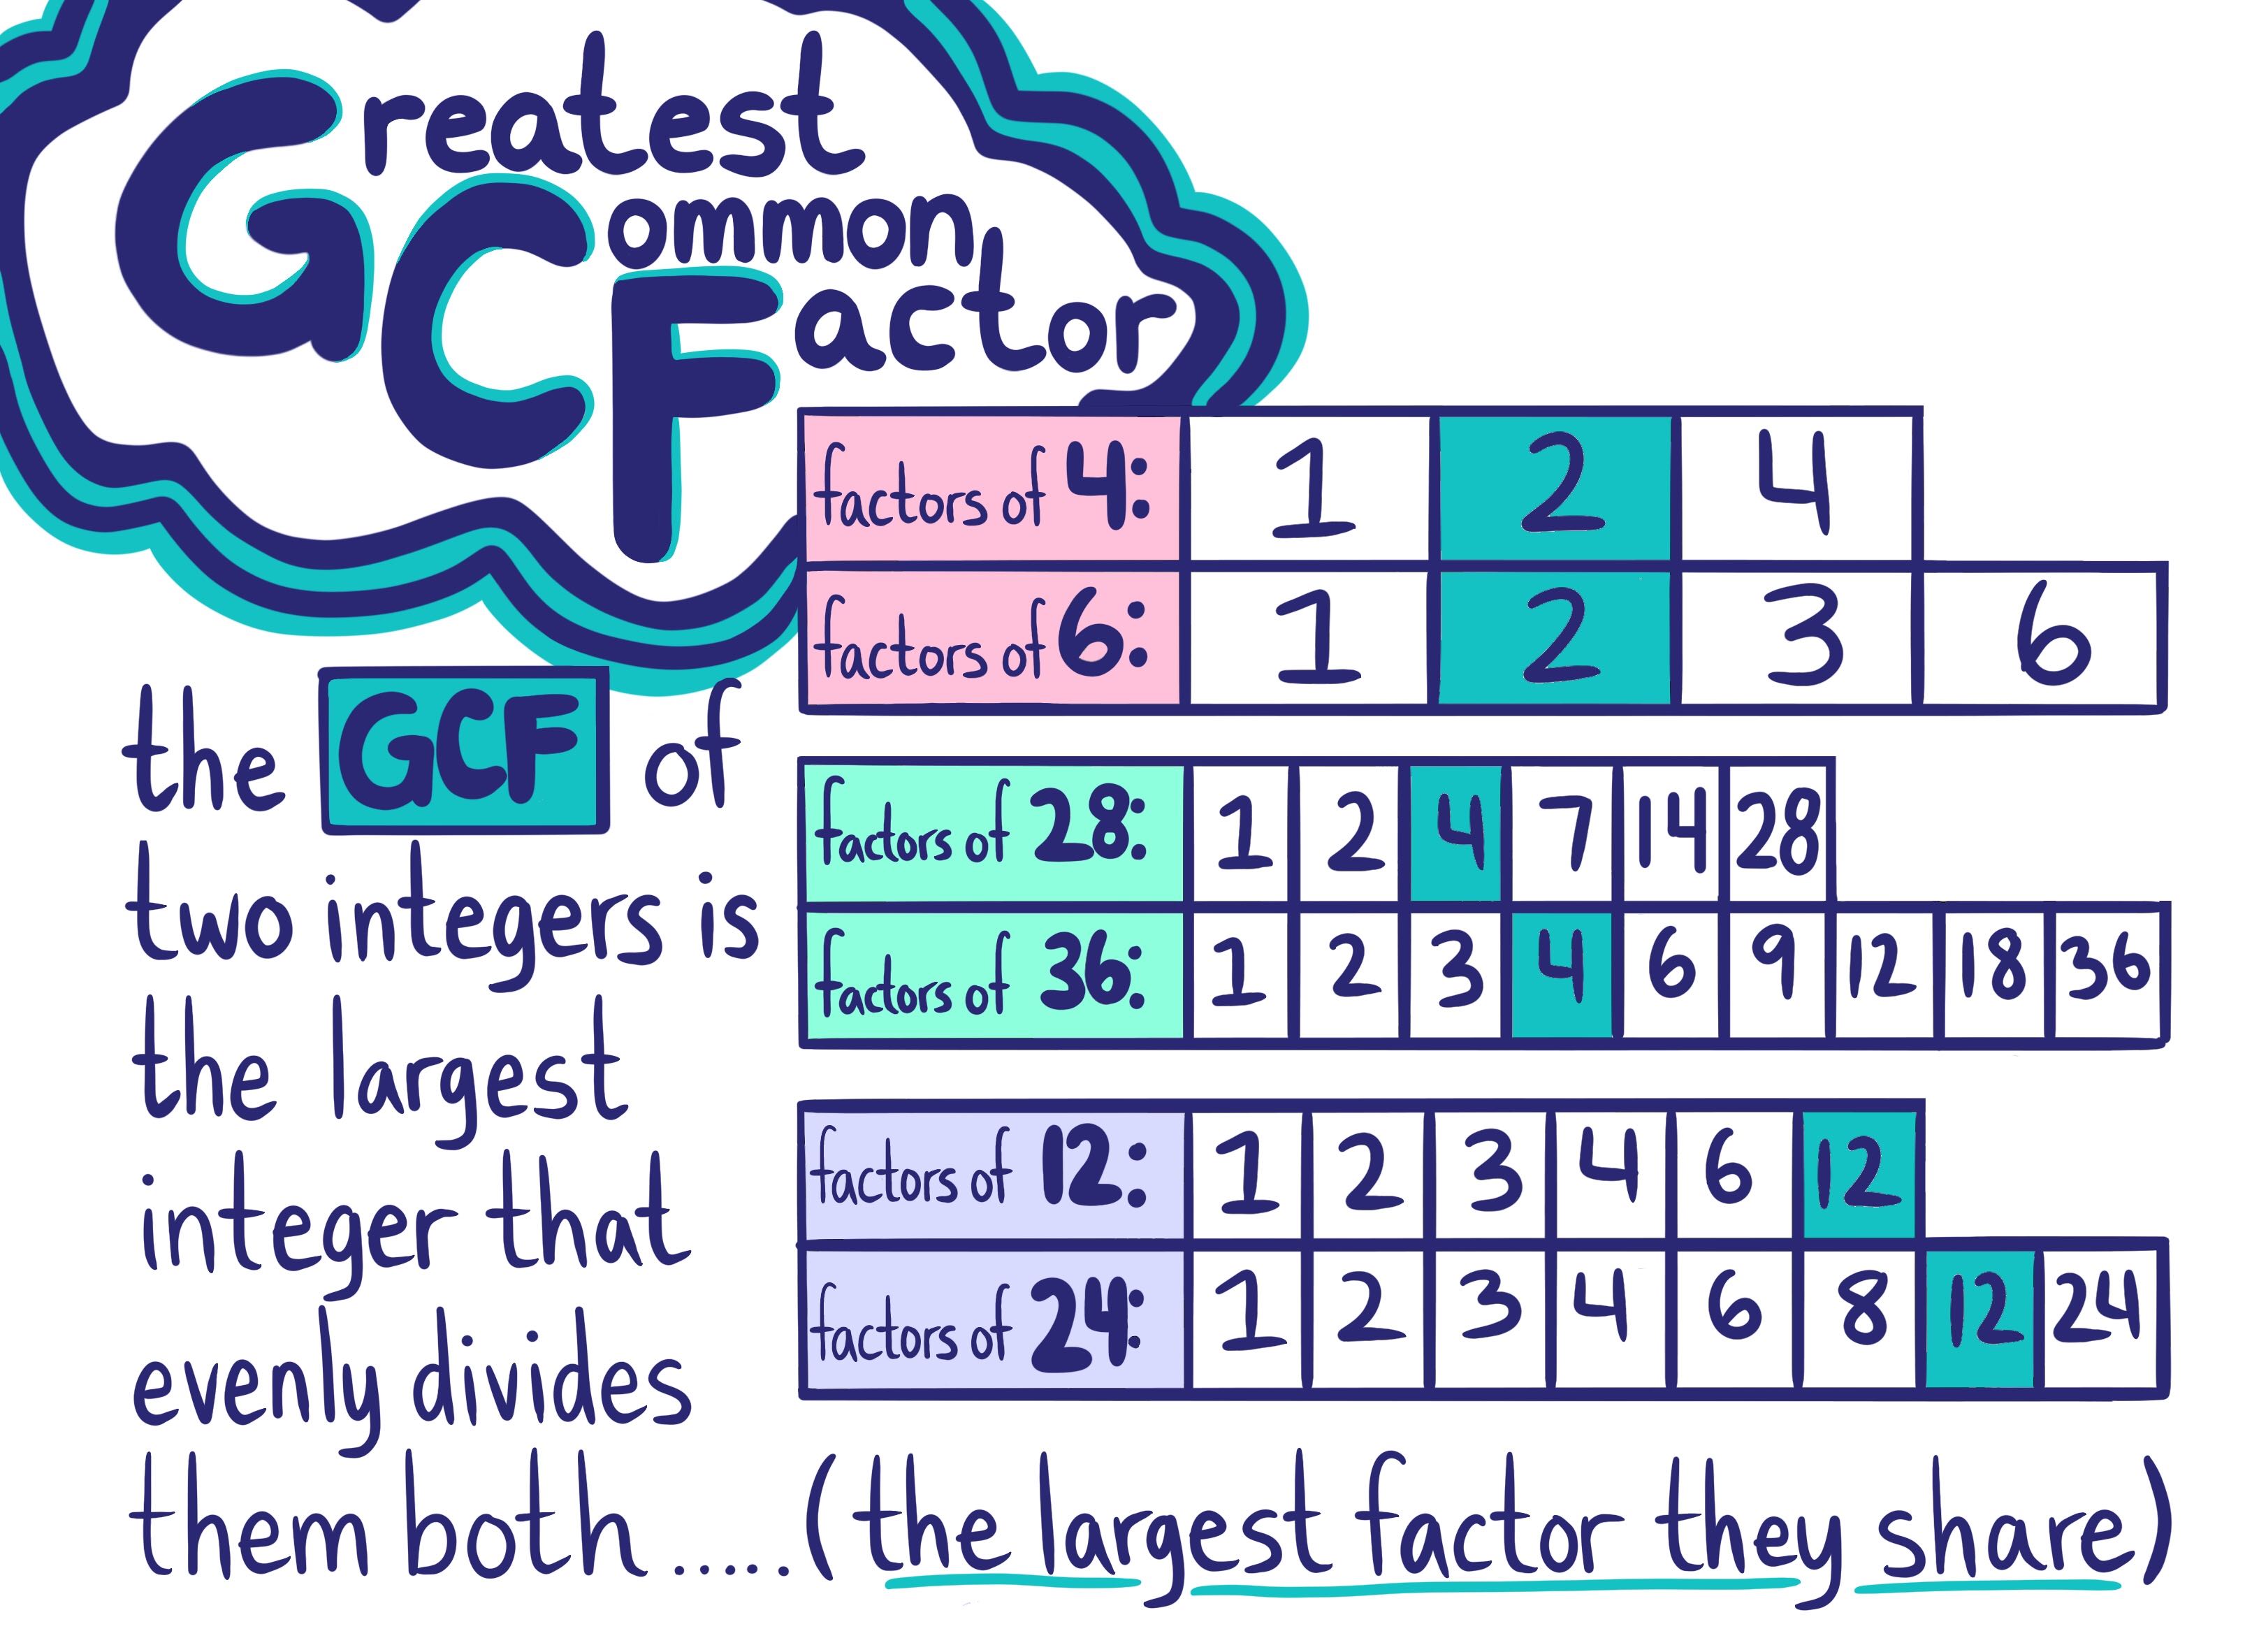
I spent years working with fraction reduction in engineering calculations before I ever really understood what was happening under the hood. The greatest common factor, or GCF, isn't just some math class requirement. It shows up constantly when you're simplifying ratios, working with periodic signals, or trying to find common denominators without cranking through brute-force lists of every single factor. Here is how it actually works in practice, and why most people approach it wrong.
Prime Factorization Method
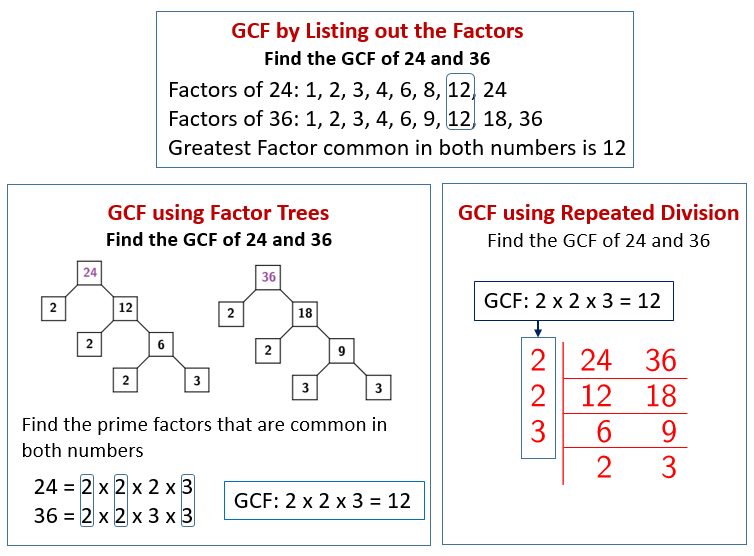
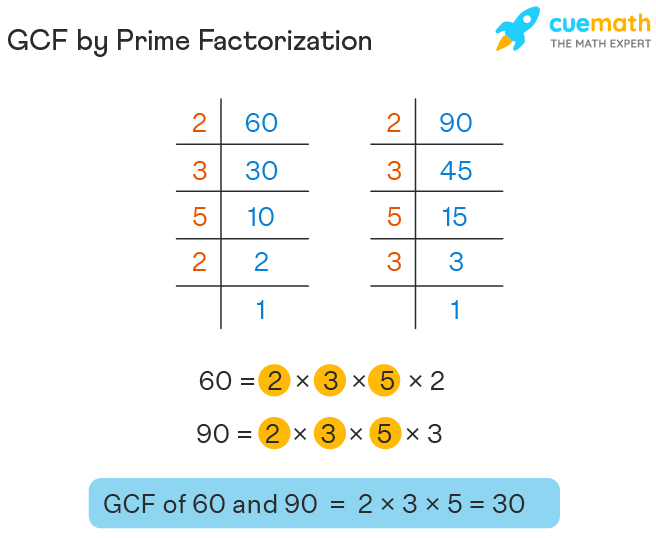
The most reliable way to find the GCF of two or more numbers is through prime factorization. You break each number down into its prime components, then identify which primes appear in all of them. The GCF is the product of those shared primes, each raised to the lowest power you see across the inputs. Take 48 and 180 as an example. The prime factorization of 48 is 2 × 2 × 2 × 2 × 3, or 2 × 3¹. The prime factorization of 180 is 2 × 2 × 3 × 3 × 5, or 2² × 3² × 5¹. The primes that appear in both are 2 and 3. The lowest power of 2 is 2². The lowest power of 3 is 3¹. Multiply those together, and the GCF is 2² × 3 = 12. For Greatest Common Factor Examples like this, the method holds up well. But there is a better way when you are dealing with large numbers.
The Euclidean Algorithm
The Euclidean algorithm is what most people actually use without realizing it. It relies on a simple property: the GCF of two numbers also divides their difference. You repeatedly replace the larger number with the remainder of dividing the larger by the smaller, until the remainder hits zero. The last non-zero remainder is your GCF. Let me walk through finding the GCF of 1071 and 462. Divide 1071 by 462. That gives 2 with a remainder of 147. Now divide 462 by 147. That gives 3 with a remainder of 21. Divide 147 by 21. That gives 7 with a remainder of 0. Stop. The GCF is 21. This method is dramatically faster than prime factorization for large numbers, and it is the basis for most computer implementations. I encountered a case once where I needed to find the GCF of two numbers around 10^9 for a signal processing project. Prime factorization would have taken minutes. The Euclidean algorithm finished in microseconds. The difference is not marginal.
Get the Full Details
Common Pitfalls and Edge Cases
One thing beginners miss is that the GCF of 0 and any number is that number itself. The GCF of 0 and 0 is undefined. If you are writing code to compute this, you need to handle those cases explicitly, or your algorithm will loop forever or return garbage. Another issue is that people often confuse GCF with LCM. They are related, but not interchangeable. The product of two numbers equals the GCF multiplied by the LCM. So if you know one, you can derive the other. This relationship is useful when you need to simplify fractions quickly or find common periods in periodic functions. I worked on a project where we were synchronizing three different sampling rates: 44100 Hz, 48000 Hz, and 96000 Hz. The goal was to find the smallest buffer size that would align all three without truncation. The answer came from the GCF of those rates, which turned out to be 300 Hz. That meant every 300 milliseconds, all three signals would realign perfectly. Without knowing how to compute the GCF efficiently, that calculation would have been painful.
GCF with More Than Two Numbers
Extending the Euclidean algorithm to three or more numbers is straightforward. Compute the GCF of the first two, then compute the GCF of that result with the third number, and so on. The operation is associative, so the order does not matter. For example, to find the GCF of 12, 18, and 30, start with GCF(12, 18) = 6. Then compute GCF(6, 30) = 6. The final answer is 6. This property is why you can chain the algorithm in code without special handling. Most library implementations take a slice or list of numbers and reduce them using the binary GCF operation.
When GCF Fails or Becomes Impractical
The Euclidean algorithm works beautifully for integers. It breaks down when you move to polynomials, Gaussian integers, or other algebraic structures without modifying the approach. For polynomials, you need the Euclidean algorithm adapted for polynomial division, which involves leading coefficients and degree tracking. There is also a practical limitation when numbers exceed typical integer bounds. Fixed-size integer types in most programming languages cap out at 2^63 - 1 for signed values. Beyond that, you need arbitrary-precision arithmetic libraries, and the algorithm still works, but memory and speed become concerns. I ran into this when processing cryptographic parameters in the 2048-bit range. The algorithm completed, but it took several seconds instead of microseconds. For most everyday uses, this is not a problem. If you are working with very large datasets or need to compute GCF repeatedly, consider precomputing small prime tables or using a sieve-based approach to speed up factorization. This usually cuts the process down from O(log min(a,b)) per query to something closer to constant time after the initial setup, depending on your data distribution.
Practical Applications
Fraction simplification is the most common use. To reduce 48/180 to lowest terms, divide both numerator and denominator by their GCF, which is 12. You get 4/15. Simple, but essential when you are displaying results or comparing ratios. Signal processing and audio engineering use GCF extensively. Sample rate conversion, buffer alignment, and phase synchronization all depend on finding common factors between frequencies. The 300 Hz example I mentioned earlier is not hypothetical. It came from real work on an embedded audio system. Cryptography relies on GCF calculations too, though usually in the form of the extended Euclidean algorithm for computing modular inverses. RSA key generation, for instance, requires finding the multiplicative inverse of the public exponent modulo (n), which reduces to a GCF computation.
If you need to implement this yourself, the recursive version is concise but risks stack overflow on deeply nested calls. The iterative version is safer and equally efficient. Here is a minimal implementation pattern: function gcd(a, b) while b != 0: temp = b; b = a mod b; a = temp; return a This pattern appears in everything from competitive programming to industrial control systems. The logic is the same regardless of language or platform.
Tools and Resources
Most mathematical software packages include GCF functions. Python's fractions module has a gcd function. Mathematica uses GCD[]. Java's BigInteger class includes a gcd method. If you need a standalone tool, there are online calculators and command-line utilities, though I generally prefer embedding the calculation directly into my code rather than relying on external tools. For educational purposes, visualizing the Euclidean algorithm with geometric rectangles can help. Each step corresponds to tiling a rectangle with the largest possible squares. The side length of the smallest square that completes the tiling is the GCF. This visualization makes the algorithm feel less abstract and more concrete. Understanding GCF thoroughly saves time across multiple domains. Whether you are simplifying fractions, synchronizing signals, or generating cryptographic keys, the underlying computation is the same. Mastering the Euclidean algorithm and knowing when to reach for prime factorization instead will serve you well. The edge cases and failure modes I mentioned earlier are worth keeping in mind, especially when scaling up to production systems or working with unusual number types.