Working With Federal Architecture Standards in Practice
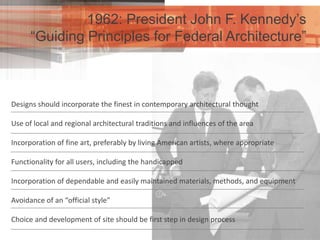
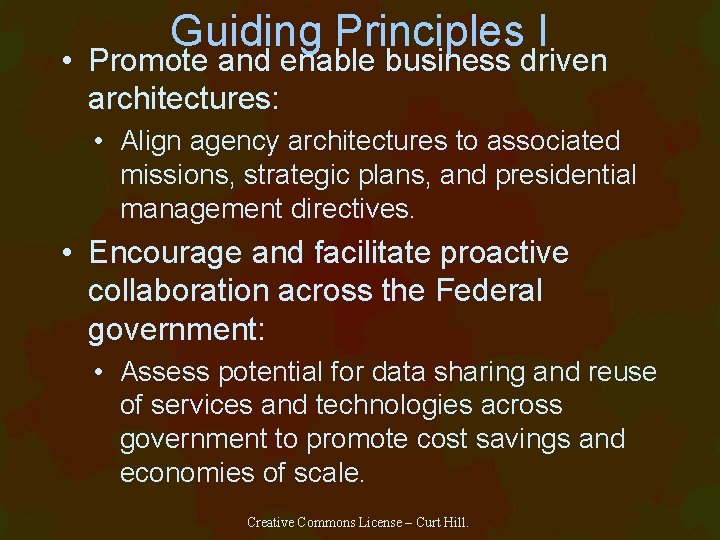
I spent about three years dealing with federal technology procurement and compliance work, mostly around cloud migration and API integration projects. The Guiding Principles Of Federal Architecture aren't just documents you read once and file away. They shape how every technical decision gets reviewed, and they're enforced through actual procurement language, not just guidance. The core framework comes from several sources: the Federal Enterprise Architecture, GSA's technology principles, OMB circulars on IT investment, and more recently the "Federal Technology Acquisition Reform" push. If you're coming from the commercial side, the biggest shock is usually that these principles are legally binding through contract clauses, not optional best practices.
The Actual Principles That Matter Day to Day
Here's what I've found actually drives decisions in real projects: Use default open. This one kills more proposals than any other. Systems that can't expose data in open formats get sent back. I once watched a perfectly functional analytics platform lose a contract round because it stored everything in a proprietary binary format with no export path. The workaround? The vendor added a PostgreSQL export endpoint and resubmitted within two weeks. Don't underestimate how much time this alone saves during review. Prioritize reusability over customization. Federal architecture explicitly favors solutions that can be adopted across agencies. Custom builds get scrutinized heavily. I saw a state government analytics tool rejected for an IRS project simply because it was tailored to one specific workflow. The agency wanted something modular. Customization is fine if you can prove the custom component doesn't prevent others from using the base system.
Security as a baseline, not a feature. FedRAMP authorization isn't optional for cloud systems handling certain data types. But here's the thing most people miss: having a moderate impact authorization doesn't mean you're done. You still need continuous monitoring, annual assessments, and incident reporting within specific timeframes. I learned this the hard way when a contractor assumed their authorization covered the full lifecycle. It didn't. We had to pull the system for three weeks while we rebuilt our monitoring pipeline. Data portability requirements. This is the principle that catches people off guard most often. You have to be able to move your data out on demand, in a usable format, within a contractually specified timeframe. Usually 30 days. I once negotiated a clause where a vendor tried to limit extraction to a single API call per day with a 100MB cap. That got struck from the contract immediately. The standard is something closer to bulk export capability without artificial throttling.
Get the Full Details

Where People Get Stuck
The most common failure point I see is around the interoperability principle. Agencies require systems to communicate through standard APIs — usually REST or GraphQL with OpenAPI specifications. But then the technical team builds internal services with custom protocols and expects integrators to adapt. This doesn't work. The review board will flag it, and you'll need to rework the integration layer before proceeding. Another trap: documentation expectations. Federal projects require architecture decision records, data flow diagrams, security threat models, and performance benchmarks before construction begins. I've seen teams try to rush through these with template responses. Reviewers can tell. One project I worked on had their security assessment rejected because the threat model used generic risk categories instead of mapping threats to specific components in their architecture. The fix took five days of detailed component analysis.
The Practical Workaround I Use
When I'm evaluating whether a solution will actually pass federal architecture review, I run it through a simple checklist I've built up from experience: Can the data exit the system in under 30 days in an open format? Does the architecture support modular deployment across multiple agency environments? Are the API contracts documented with OpenAPI specs? Is there a clear path to FedRAMP authorization if cloud-hosted? Can you produce an architecture decision record for every major component choice? If the answer to any of these is no, you're going to need a mitigation strategy before you even submit a proposal. And by mitigation, I don't mean a promise. I mean a documented plan with specific technical steps and timelines. Vague commitments get flagged during the technical evaluation phase.
A Specific Problem I Encountered
During a health data exchange project, we hit an edge case with the interoperability principle that nobody had really addressed. The agency wanted FHIR-based data exchange, but their legacy systems used HL7 v2 messages. Converting between the two in real time without introducing data loss sounded straightforward until we actually mapped the field sets. A lot of custom coding fields in HL7 v2 didn't have clean FHIR equivalents, especially around provider taxonomy codes. The workaround was to build a transformation layer that mapped common fields automatically and flagged uncommon ones for manual review within the UI. This meant the system could process 85% of messages without human intervention while still meeting the interoperability requirement. The remaining 15% went through a review queue with audit trails. It added about two months to the timeline but kept us compliant. Worth noting: this kind of partial-automated solution is acceptable under the principles as long as the manual path is documented and the data integrity is maintained throughout.
What This Framework Doesn't Do Well
I need to be honest about the limitations. The Guiding Principles Of Federal Architecture excel at setting direction but are vague on implementation specifics. Different agencies interpret them differently. GSA's version of "use default open" can mean something slightly different from what HUD requires. This isn't necessarily a flaw — it allows flexibility — but it means you can't just memorize one set of rules and apply them universally. Another limitation: the principles favor established technologies and proven patterns. Innovative approaches that don't yet have federal adoption histories face higher scrutiny. I've seen genuinely better technical solutions lose out to older systems simply because the older systems had existing FedRAMP authorizations and proven deployment records. The principles claim to encourage innovation, but the evaluation process penalizes risk. Finally, compliance overhead is real. A typical federal architecture review adds somewhere between 15 and 25 percent to project timelines compared to equivalent commercial work. The additional documentation, security assessments, and procurement compliance steps aren't bureaucracy for its own sake — they serve legitimate oversight purposes — but they do slow things down. If you're evaluating whether to pursue federal work, factor that into your resource planning from the start rather than discovering it mid-project.