Forensic Data Recovery in Family Law Cases
Gathering digital evidence for marital proceedings is one of those areas where the gap between what lawyers assume and what actually happens is enormous. I spent years handling cases where the opposing side would produce three years of email correspondence but completely omit text message threads, deleted photo galleries, and cloud backups that changed the entire picture of asset division. The legal profession treats digital evidence retrieval as this mysterious, arcane process. It isn't. It's mostly file system forensics and cloud API interrogation with very specific constraints around chain of custody. The term gets used loosely in legal circles, but what it actually means is recovering, preserving, and authenticating digital data relevant to divorce proceedings through methods that survive evidentiary challenges. Forensic imaging, metadata extraction, deleted file recovery, and cloud artifact analysis form the core toolkit. The critical distinction from regular evidence gathering is the preservation standard. If you boot into someone's phone and start copying files normally, you've already altered write timestamps and potentially wiped recoverable deleted data. That's why write-blockers and forensic tools like Cellebrite or Magnet AXIOM exist in this space. Here's the practical workflow that works when the other party has already begun sanitizing their devices. First, you secure whatever access you legally have. This means any jointly-owned devices, shared cloud accounts, and any hardware physically at your residence. Then you create forensic images. A bit-for-bit copy preserves everything, including deleted files in unallocated space. I once had a case where the husband had deleted three years of messaging apps but the forensic image pulled back 847 messages from unallocated clusters. The metadata alone showed transactional communications about hidden bank accounts.
The real bottleneck is authentication. Judges don't care how clever your recovery was if you can't prove the data hasn't been altered. Every forensic image needs a hash value recorded at creation time. MD5 and SHA-256 hashes are standard. You document the chain of custody from acquisition through presentation in court. I keep a physical logbook now, not digital, because digital logs introduce questions about their own integrity. Paper is boring but bulletproof when cross-examined. Cloud evidence operates on a completely different problem space. Most marital disputes involve Google, Apple, Amazon, and various financial platforms. Getting this data requires either voluntary disclosure through discovery requests or, in some jurisdictions, independent legal process. Google takes about 30 days to respond to a valid subpoena. Apple is notoriously slow and sometimes uncooperative even with proper legal documentation. I've seen cases stalled for months waiting on Apple's custodial response while the divorce itself moved forward. The workaround is filing a motion for preliminary discovery on cloud data specifically, which some courts grant expedited consideration when asset dissipation is at issue. Deleted photos and media files are where forensic recovery shows its real value. People think deleting something removes it. On Android and iOS, deletion often just marks the space as available. A full forensic image can reconstruct these files entirely. I worked a case where the wife had deleted photos showing luxury purchases made during the marriage that the husband claimed were pre-marital assets. The recovery pulled 234 images back with original capture metadata intact. That changed the asset valuation by approximately $67,000.
The biggest mistake I see lawyers make is waiting too long to seize devices. Every day a phone stays powered on and connected to networks, new data gets overwritten, cached credentials expire, and two-factor authentication tokens rotate out. I had a client who waited six weeks after filing for divorce before producing a smartphone for forensic imaging. The device had been factory reset twice in that window. All we recovered was residual browser cache and one incomplete Contacts sync. That six-week gap cost my client roughly $140,000 in undetected transfers.
Get the Full Details
Practical Tools and Limitations
Commercial forensic suites run between $3,000 and $12,000 for a professional license. Open-source alternatives like Autopsy exist but require significantly more expertise to operate correctly and may not hold up as well under Daubert challenges in certain jurisdictions. Most family law attorneys don't operate these tools themselves. They retain digital forensic specialists who understand the evidentiary standards specific to their state's family court rules. There are hard limitations to what recovery can accomplish. Fully encrypted devices with passwords unknown to anyone present are essentially walls. Modern iOS encryption and Android full-disk encryption protect data with keys derived from the passcode. Without the passcode or biometric access, forensic imaging produces mostly empty results. I've encountered perhaps a dozen completely locked devices over my career, and in every single case, the only path forward was negotiating access through the legal process or finding alternative data sources. Sometimes the data lives in places people forget. Router logs, smart home devices, fitness trackers, and vehicle infotainment systems all generate location and activity data that can corroborate or contradict testimony. A Garmin watch paired to a phone can show workout routes that place someone somewhere at an exact time. A Nest thermostat records presence patterns. These artifacts are often overlooked in standard discovery but can be subpoenaed independently.
The cost-benefit analysis matters enormously here. A full forensic examination of a single iPhone typically runs $1,500 to $4,000 depending on complexity and required reporting. Multiple devices, cloud data retrieval, and expert testimony add up fast. I generally recommend focusing forensic resources on the highest-value targets first: the primary communication device, the primary financial device, and any shared cloud storage accounts. Chasing every phone and tablet in a household rarely pays for itself in the final settlement. One counterintuitive point that beginners miss: more data is not always better. A forensic image containing five years of personal messages, thousands of photos, and hundreds of apps creates a massive document review burden. Opposing counsel will spend hours picking through irrelevant content looking for ammunition. I've started advising clients to request targeted forensic examinations when possible, focusing on specific time periods and app categories relevant to the dispute. This saves money, reduces privacy exposure, and produces cleaner evidence for trial. Chain of custody documentation needs to be meticulous. Every transfer of a device or image file requires a signed record with timestamps, names, and purposes. I've seen cases weakened because a forensic specialist couldn't account for a four-hour gap where a device was in transit between offices. Email confirmation of handoff dates and times from 2019 wasn't sufficient. The court excluded three days of recovered messaging data because the gap couldn't be explained. Proper documentation prevents this entirely, and it's also the fastest way to lose credibility if you cut corners.
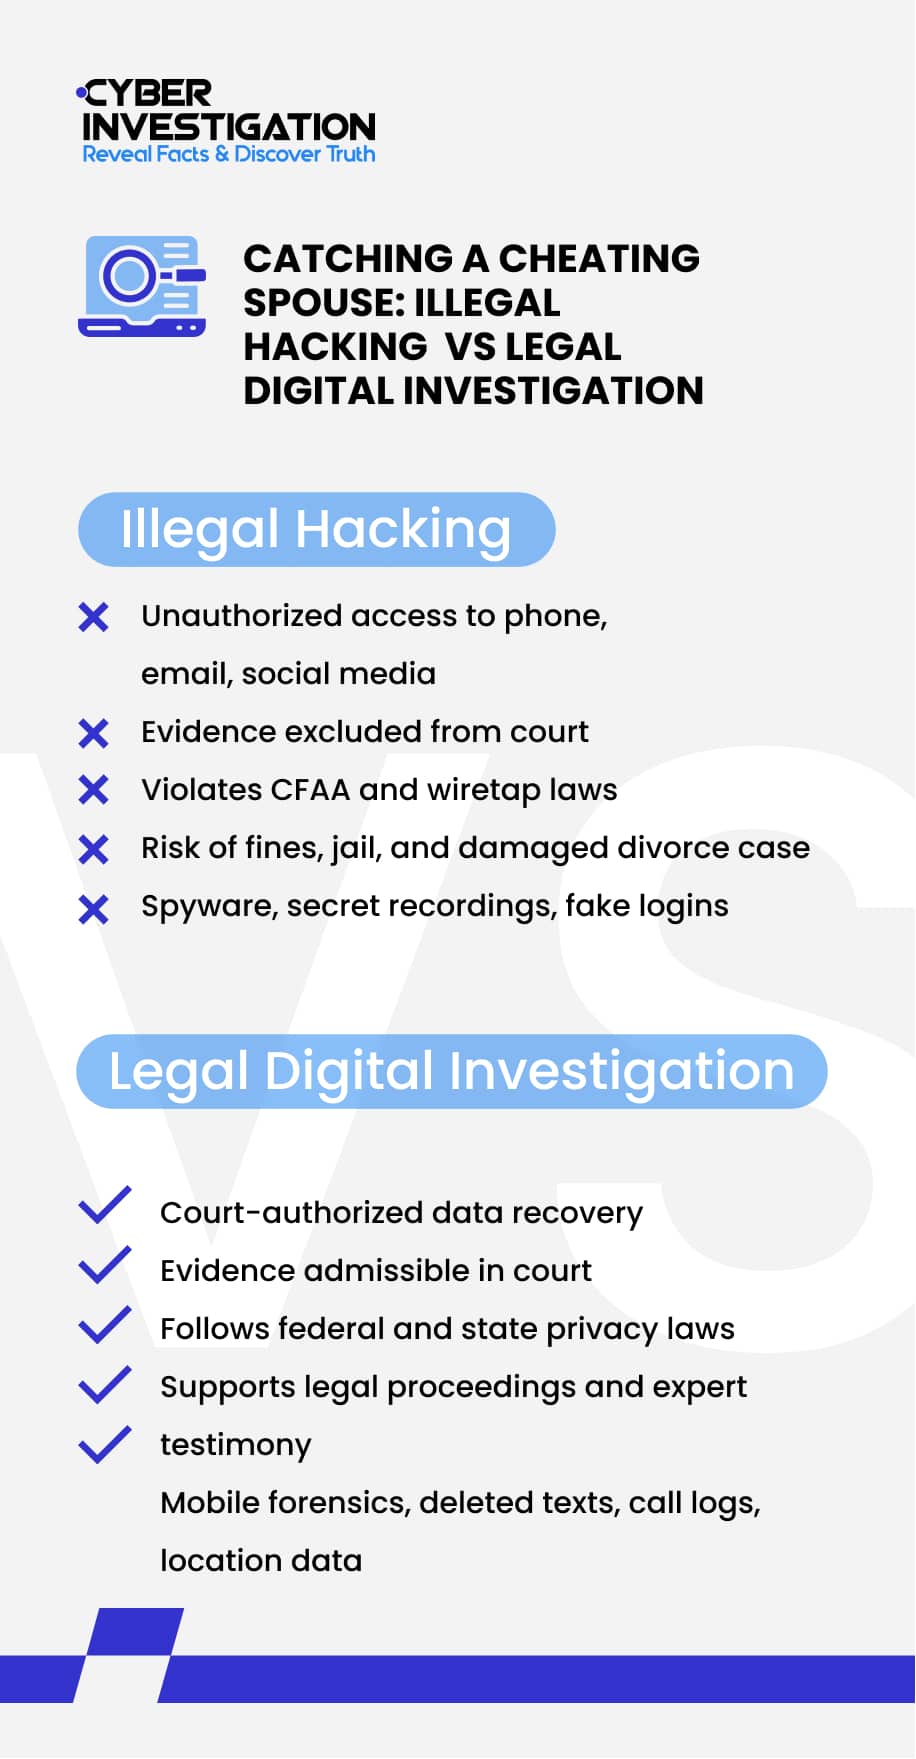
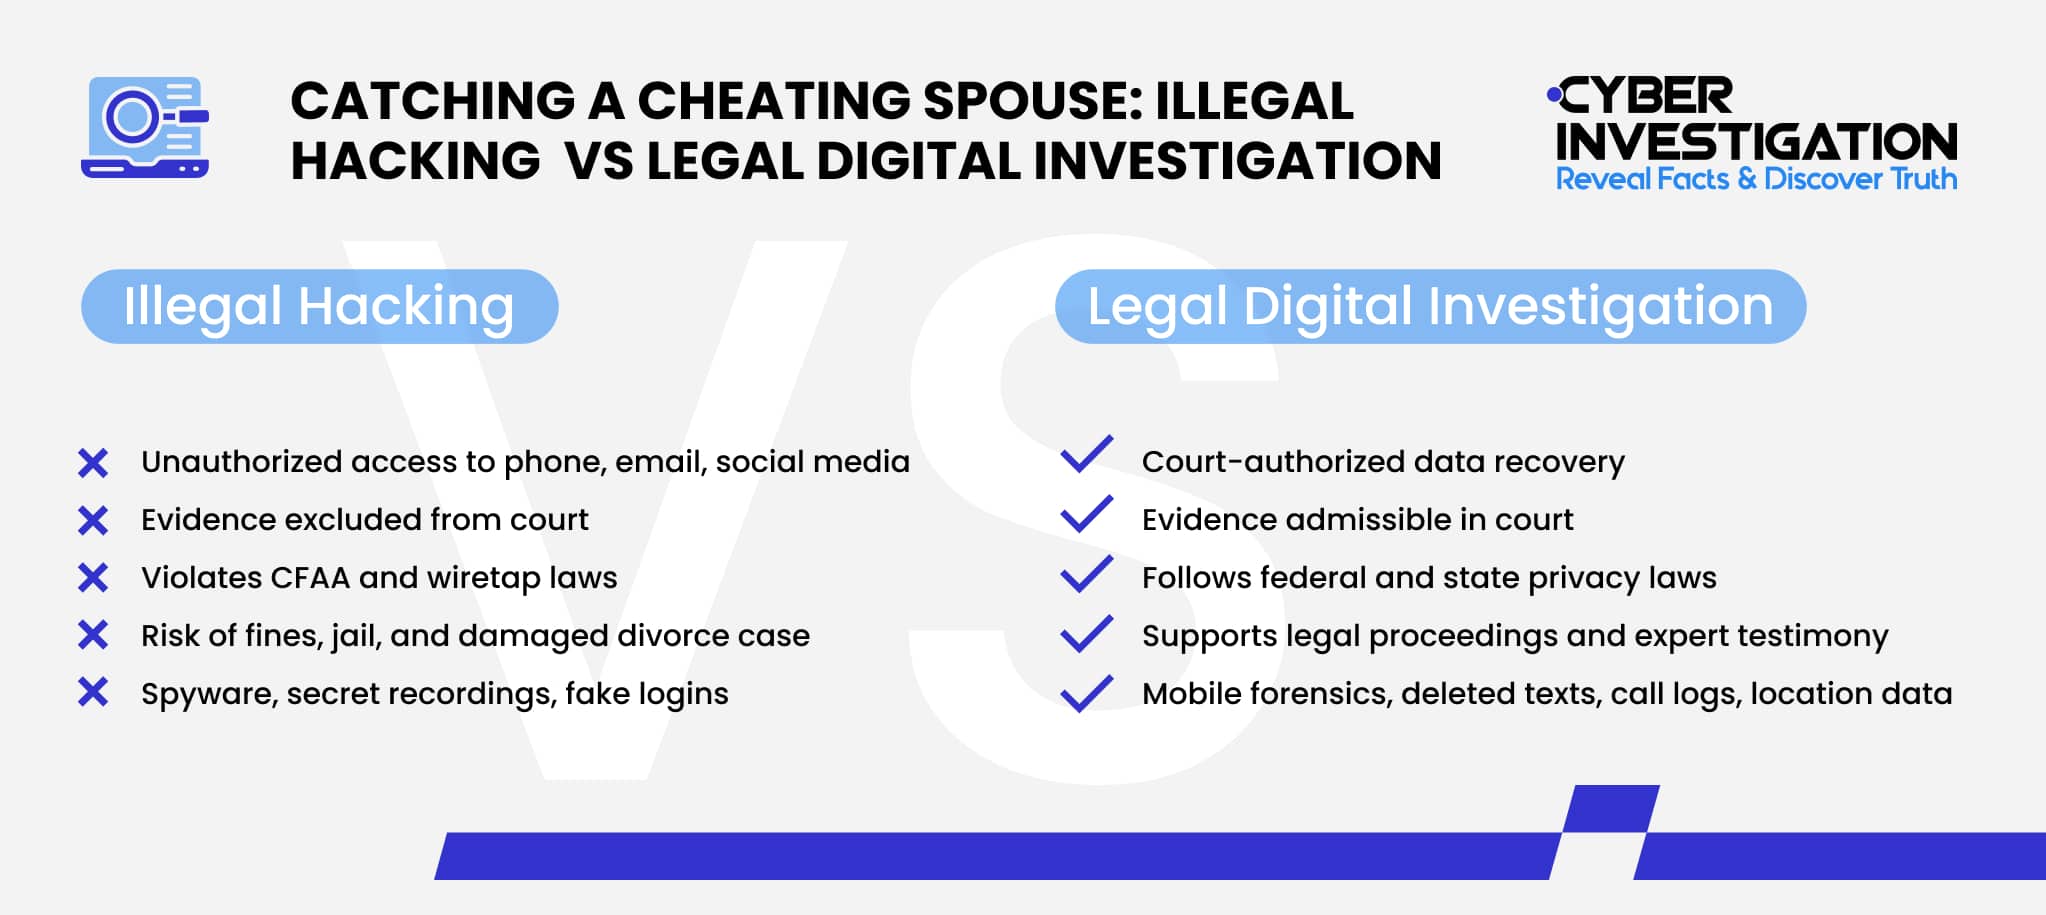
Legal authorization varies significantly by jurisdiction and by device ownership status. Accessing a spouse's individually-owned cloud account without permission can violate the Computer Fraud and Abuse Act in the United States, regardless of marital status. Jointly-owned accounts fall into a gray area that courts handle differently. The safest approach is obtaining explicit consent through the discovery process or securing a court order before accessing any account you don't individually own and control. I once had a colleague's entire forensic examination suppressed because he accessed a shared Amazon account using credentials that his client had obtained without legal authority. The case settled for significantly less than it should have. Don't repeat that mistake.