What Actually Happens When You Try to Procure Technology
Most people treat technology purchasing the same way they treat office supply purchasing. They run an RFP, compare unit prices, pick the cheapest vendor, and hope the implementation doesn't blow up. That approach works fine for printer toner. It fails spectacularly for anything that touches your infrastructure stack. I've been doing this long enough to recognize the pattern early. A procurement team will come to me with a spreadsheet comparing three cloud hosting providers based purely on monthly compute costs. They're missing the egress fees. They're missing the data transformation costs. They're missing the compliance audit requirements that one provider can't fulfill without you building it yourself. By the time anyone notices, you're already six months into a contract and the CFO is asking why the bill is triple the forecast.
The Core Framework of a High Tech Procurement Strategy
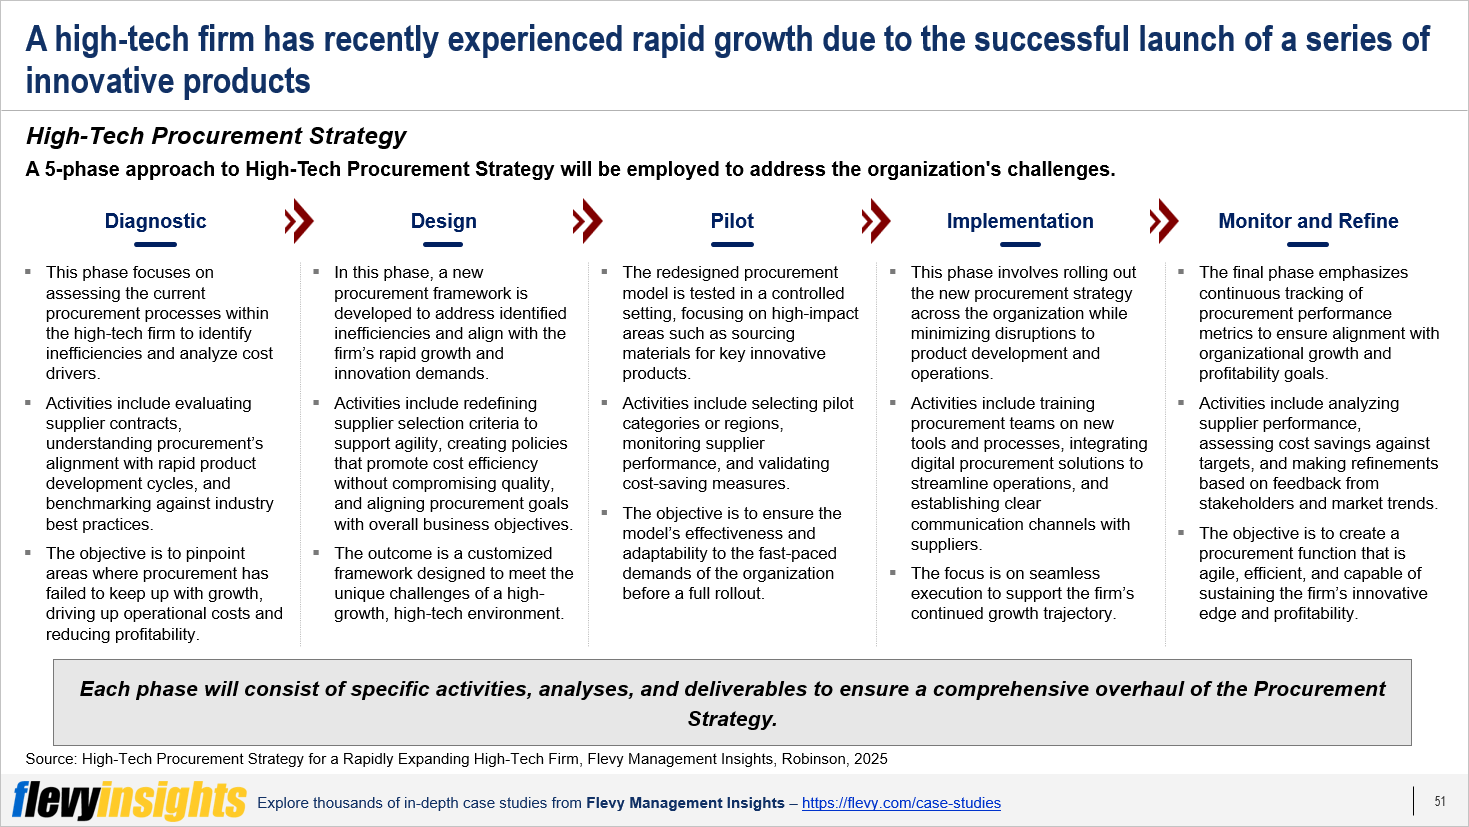
At its simplest level, a High Tech Procurement Strategy means you stop treating technology purchases as transactions and start treating them as long-term operational commitments. The distinction matters because the financial and technical consequences of a bad hardware purchase echo for five to seven years. A bad software selection can linger even longer since migration is its own form of organizational trauma. The framework has several layers that most organizations skim over: Total Cost of Ownership, not unit price. This is the one that gets ignored most often. TCO includes licensing, implementation, integration, maintenance, training, compliance, and decommissioning. I once reviewed a proposal where the hardware was 40% cheaper than the alternative. When I pulled the TCO across a seven-year horizon including rack space, power, cooling, refresh cycles, and the mandatory third-party support contract that the manufacturer requires after the warranty period expires, the cheaper option was actually 23% more expensive overall. The spreadsheet didn't lie. The question is whether anyone was looking at the right rows.
Vendor lock-in assessment. Every technology decision creates dependency. The question is whether that dependency is lock-in or just convenience. There's a meaningful difference. Open-source software with a commercial support layer is dependency, not lock-in, because you can switch providers. Proprietary formats with no export path are lock-in. Cloud providers that don't offer native data export in a portable format are lock-in. I learned this distinction the hard way when a mid-sized SaaS platform changed its API pricing model overnight and our integration costs jumped by four hundred percent because we'd built everything against their proprietary endpoints instead of standard protocols. Security and compliance as procurement criteria, not afterthoughts. SOC 2 reports, pen test results, data residency requirements, encryption standards — these should all be evaluated before you negotiate price. Too many teams sign contracts and then discover during the security review that the vendor can't meet their regulatory obligations. At that point you either walk away and waste months or accept the gap and carry the risk. Neither option feels good. Scalability and flexibility provisions. Your procurement terms should account for what happens when the business grows or pivots. Can you scale without renegotiating? Is there a data portability clause? What happens to your licenses if you merge with another company or spin off a division? These questions seem abstract until you're facing an acquisition and realize your software contracts have change-of-control provisions that trigger renegotiation.
Get the Full Details
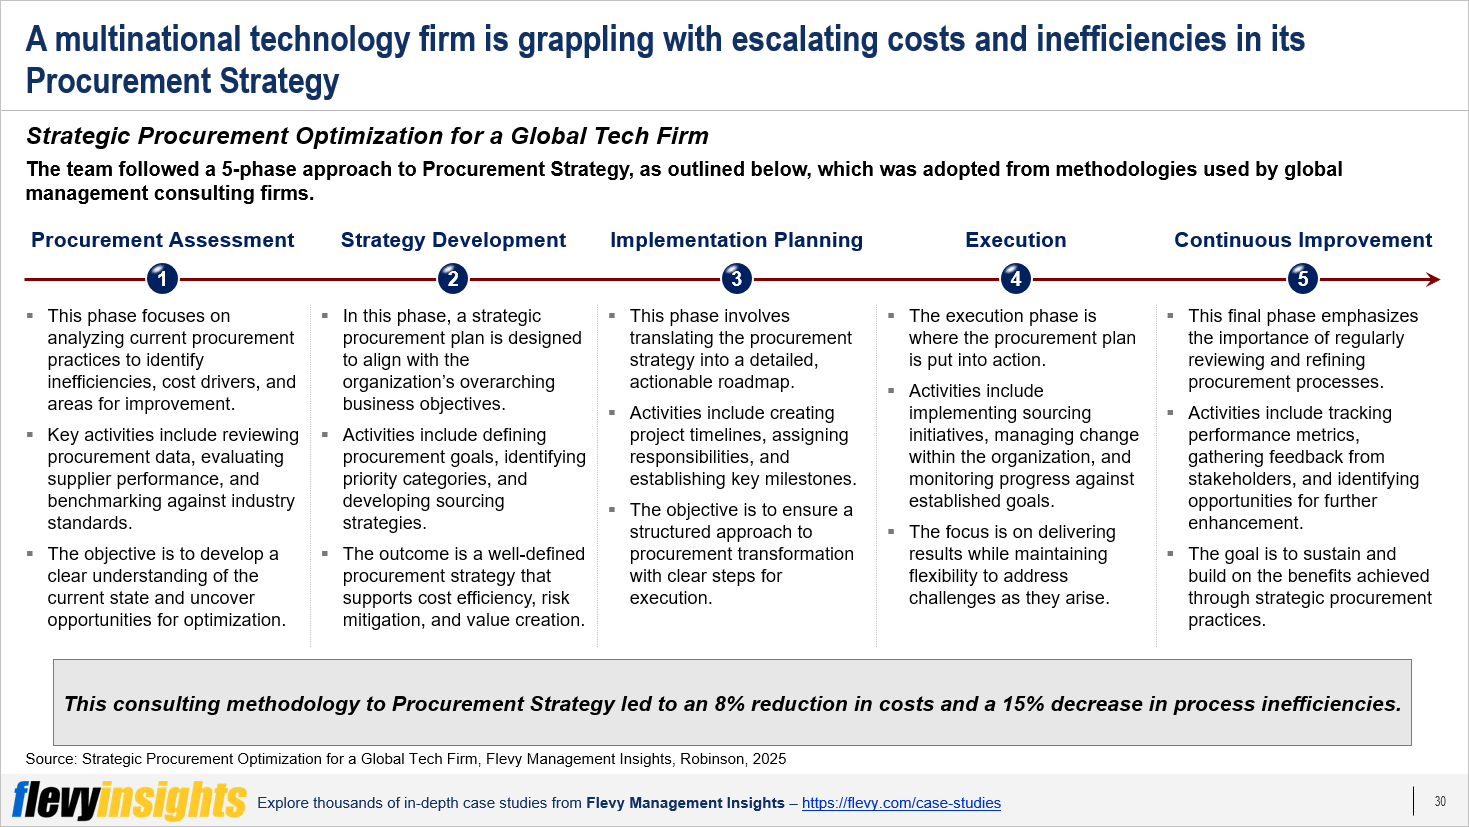
Where This Actually Breaks Down in Practice
I want to share a specific situation because it's the kind of thing that doesn't show up in any procurement textbook. We were procuring a fleet of networking equipment from a major vendor. The RFP process was thorough. The TCO analysis was solid. The security review passed clean. The contract had favorable terms on everything we could measure. Three weeks after deployment, the vendor announced a firmware update that introduced a bug affecting a specific switching module in our configuration. The fix required a hardware replacement. The module was on a sixteen-week backorder. Our production environment ran degraded for eleven weeks because we hadn't negotiated a spare parts guarantee or a performance penalty clause for extended outages in the procurement terms. The workaround was painful. I had to pull a similar switch from our disaster recovery site, which meant our DR readiness went from documented to theoretical for roughly two months. Meanwhile the vendor was sending quarterly update emails about how they were aware of the issue and working on it. I ended up embedding one of my engineers with their support team for a week to accelerate the hardware replacement. The relationship survived but not profitably for either side. The lesson wasn't that the procurement process failed. The process was adequate. The lesson was that the procurement terms needed to account for post-deployment risk allocation, not just pre-deployment evaluation. After that, every contract I've been involved in includes specific provisions for spare parts availability commitments, minimum SLA penalties tied to hardware shortages, and vendor escalation paths that don't route through general support. It's a small addition to the contract language but it changed how seriously vendors take the relationship.
Practical Steps for Building Your Approach
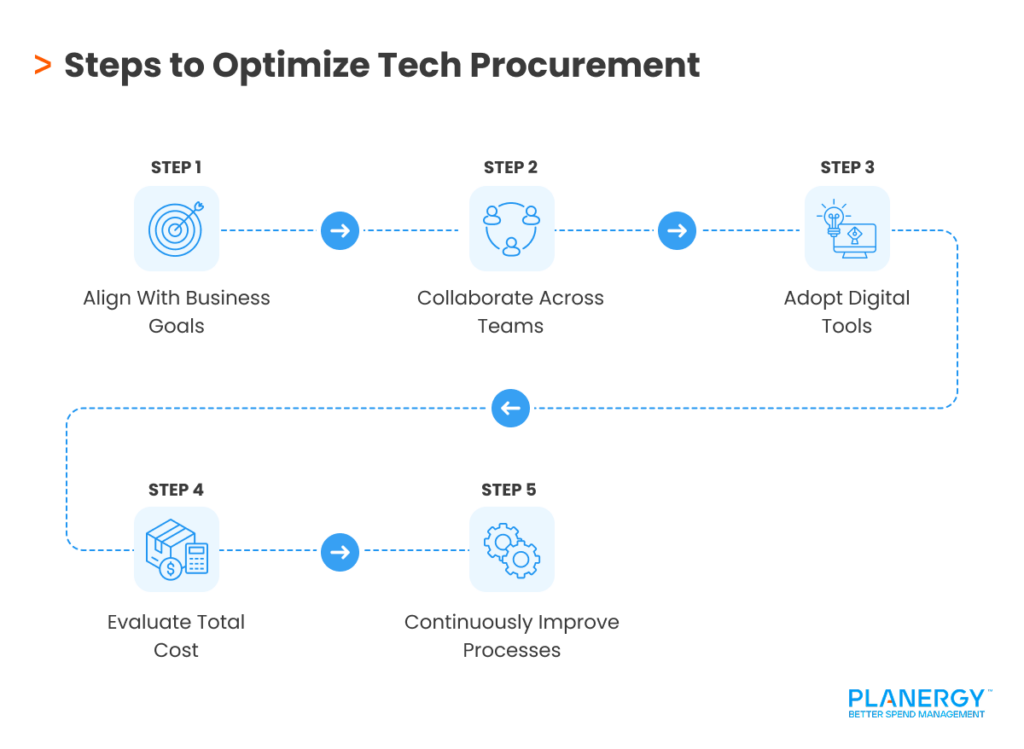
Start by cataloging what you actually use. You can't procure intelligently if you don't have visibility into your current technology footprint. I've seen organizations attempt procurement modernization while still running applications on outdated operating systems that the vendor no longer supports. The foundation has to be sound before you build the process. Build a cross-functional evaluation team. Procurement alone will optimize for price. IT alone will optimize for features. Security alone will optimize for compliance. You need all three perspectives in the room before you issue any RFP, or you'll get a result that satisfies one department and creates problems for the others. The best deals I've seen were negotiated with representatives from finance, engineering, operations, and compliance all reviewing the same documents simultaneously. Write the contract language yourself. Vendor contracts are drafted to protect the vendor. This isn't unusual or sinister, it's just how it works. If you accept the standard agreement, you're accepting terms that were written assuming you'd have no leverage. I always have my team rewrite the key sections — liability caps, indemnification, termination clauses, data ownership, service credits — before we put them on the table. The negotiation takes longer but the resulting contract is actually usable. The version our legal team sent back from one enterprise software deal removed twelve separate clauses that would have given the vendor unilateral rights to change pricing terms. Twelve clauses. Those would have cost us millions over a five-year term.
Implement a continuous review cycle. Procurement isn't something you do once and then forget. Technology landscapes shift. Vendor financials change. Your business needs evolve. Set quarterly reviews for major contracts. Check whether the SLAs you're getting still match what you pay for. Look for alternative solutions that have emerged since you signed. The market moves faster than most contract cycles acknowledge. The uncomfortable truth is that a well-designed High Tech Procurement Strategy will never feel exciting. It will involve spreadsheets, legal documents, security questionnaires, and difficult conversations with stakeholders who want the shiny new thing today. The people who get good at this develop a kind of quiet competence. They learn to spot the subtle pricing structures that hide cost growth. They know which vendors are reliable partners and which ones treat contracts as sales theater. They build relationships that make problem-solving easier when things go wrong, which they inevitably will. What I can tell you with confidence is that the organizations that treat technology procurement as a strategic function rather than an administrative one consistently end up with better outcomes. Not dramatically better. Consistently better. The margin of difference usually comes down to whether someone asked the right questions before signing instead of after deploying.