Working Through HIPAA And Privacy Act Training Materials
You pick up the training module, log in, and immediately hit a wall of dense regulatory language that doesn't actually tell you what to do when a situation comes up. This is the universal experience. The materials cover the rules well enough on paper but often fail to connect them to the daily reality of handling patient information in a clinical or administrative setting. Understanding the gap between what the regulation says and what you actually need to do is where most compliance failures start. I spent several years managing training programs across multiple healthcare organizations, and the most common problem I saw was that staff would pass the compliance quizzes without actually internalizing anything. They clicked through, selected the answer that sounded most correct, and moved on. Six months later, someone would share a patient file over an unencrypted email and wonder why there was a breach notification on their desk.
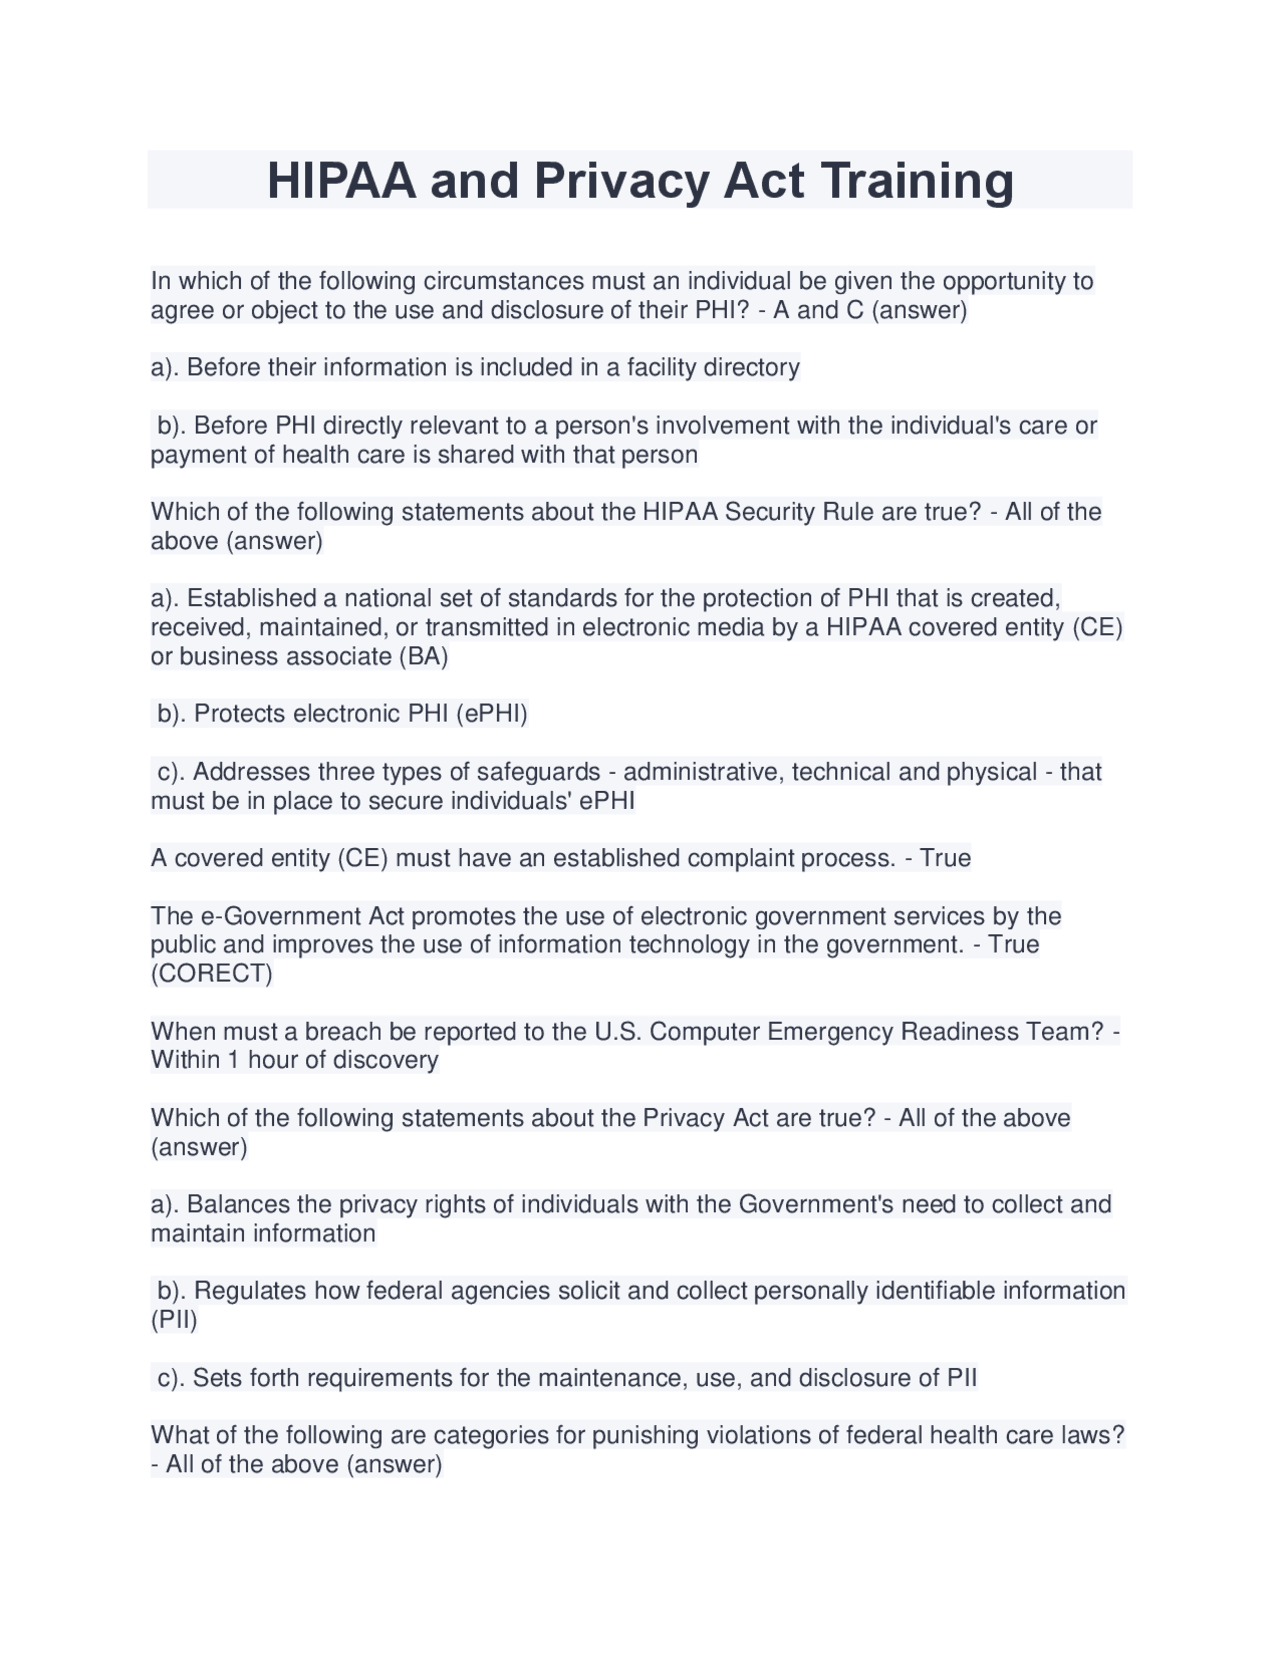
Hipaa And Privacy Act Training Answers That Actually Work
The core issue isn't that the training content is bad. It's that most programs treat compliance as a checkbox exercise rather than a behavioral change program. The HIPAA Privacy Rule establishes what constitutes protected health information and when it can be disclosed. The Privacy Act of 1974 covers federal agencies and their handling of records about individuals. In practice, these overlap in ways that create confusion for anyone working across both public and private sectors. Here is what I learned about making training stick. First, ground every scenario in actual work situations rather than abstract examples. When I redesigned a training module, I started pulling real breach reports from HHS enforcement actions and turning them into multiple choice questions. The results were immediately different. Staff engaged with the material because it reflected the kind of mistakes people actually make. Second, stop testing memorization. Quiz questions that ask "What is the minimum necessary standard?" are useless if nobody can apply that concept to a specific task like sending a referral to a specialist. Instead, present a scenario and ask what the person should do. Did you receive a request for lab results from a patient's new physician? Do you send everything or just the requested test? The answer seems obvious until you're dealing with an EHR system that auto-populates discharge summaries with old medication lists and nobody catches the error before it goes out.
Third, address the intersection of state and federal law. This is where I encountered my most persistent problem. A clinic I worked with had a policy that seemed compliant with HIPAA but violated a stricter state privacy law regarding mental health records. The training material only referenced federal standards. When a subpoena came in, the office manager followed the written policy and nearly committed a violation. The workaround was straightforward once we identified it — we created a crosswalk document mapping each relevant state law to its federal equivalent and built that into the training workflow. It took about three weeks to compile and saved us from repeated compliance gaps. The most counter-intuitive thing about this training is that the hardest part isn't learning the rules. It's remembering to apply them when you are tired, rushed, or under pressure. A nurse on a busy shift sending a quick message to a covering colleague about a patient isn't thinking about PHI boundaries. She is thinking about patient safety. Both matter. Training needs to acknowledge that tension instead of pretending it doesn't exist. There are limitations to even the best training program. It cannot prevent intentional misconduct. It cannot eliminate human error in high-volume environments without structural changes like access controls and audit trails. And it becomes obsolete quickly because guidance from HHS changes frequently. If you are relying solely on an annual training module to keep your organization compliant, you are missing the ongoing reinforcement that actual compliance requires.
Get the Full Details
A more effective approach combines initial training with periodic scenario refreshers, clear reporting pathways for employees who are unsure about a situation, and regular audits that feed back into the training content. Organizations that do this tend to have fewer violations not because their staff are smarter but because they have normalized the habit of checking before acting.