What a HIPAA Certification Practice Test Actually Looks Like
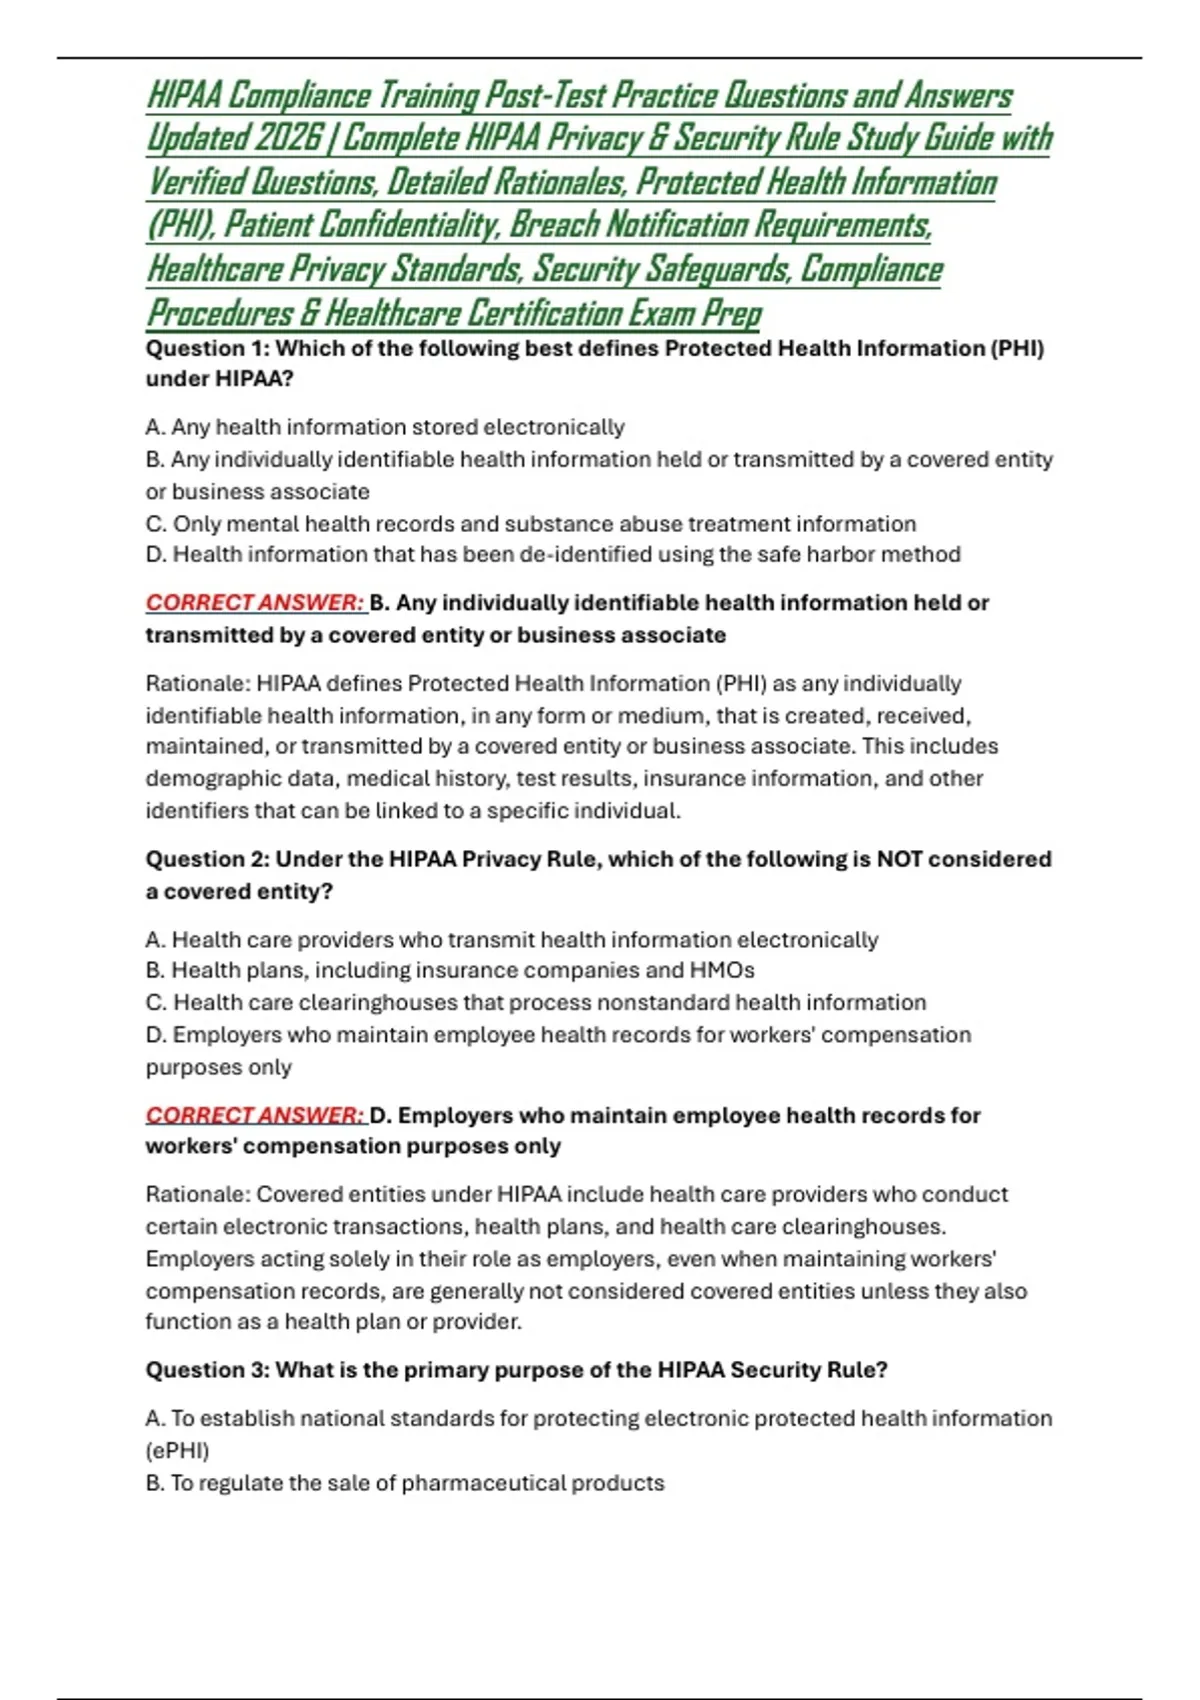
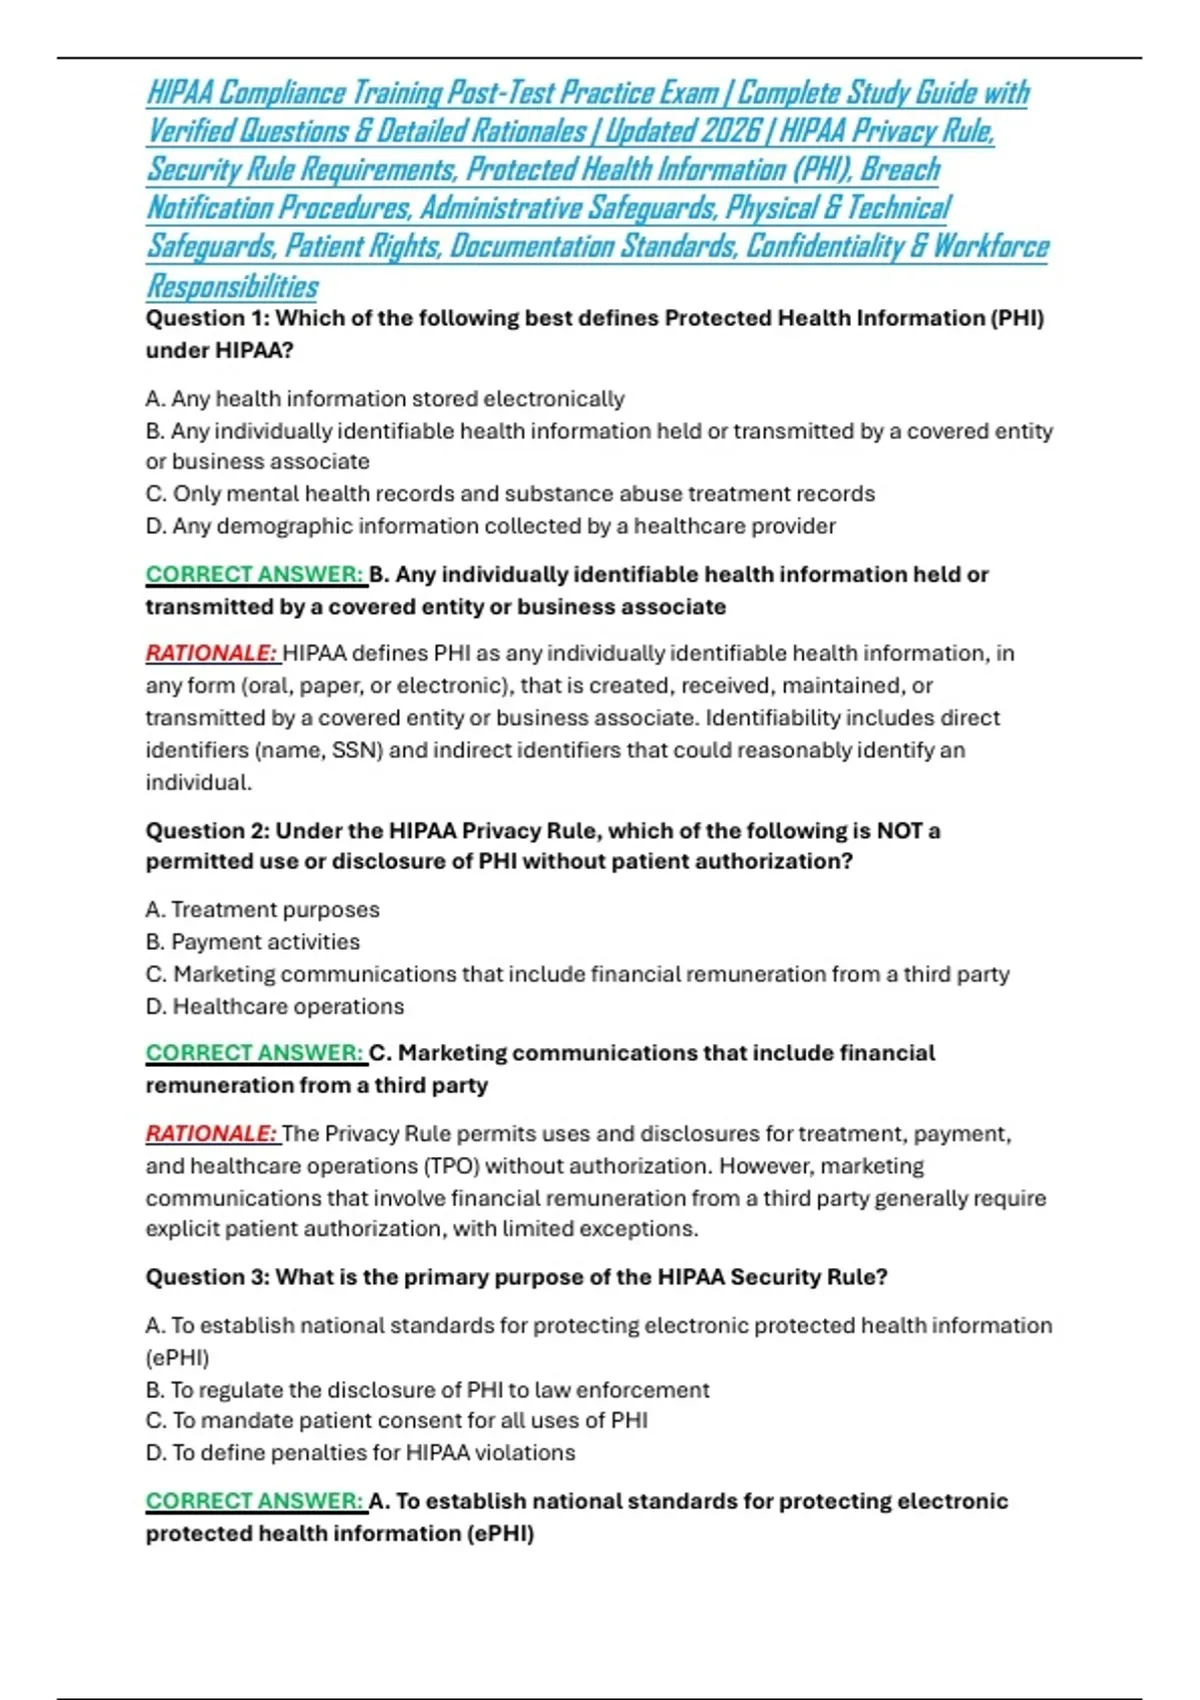
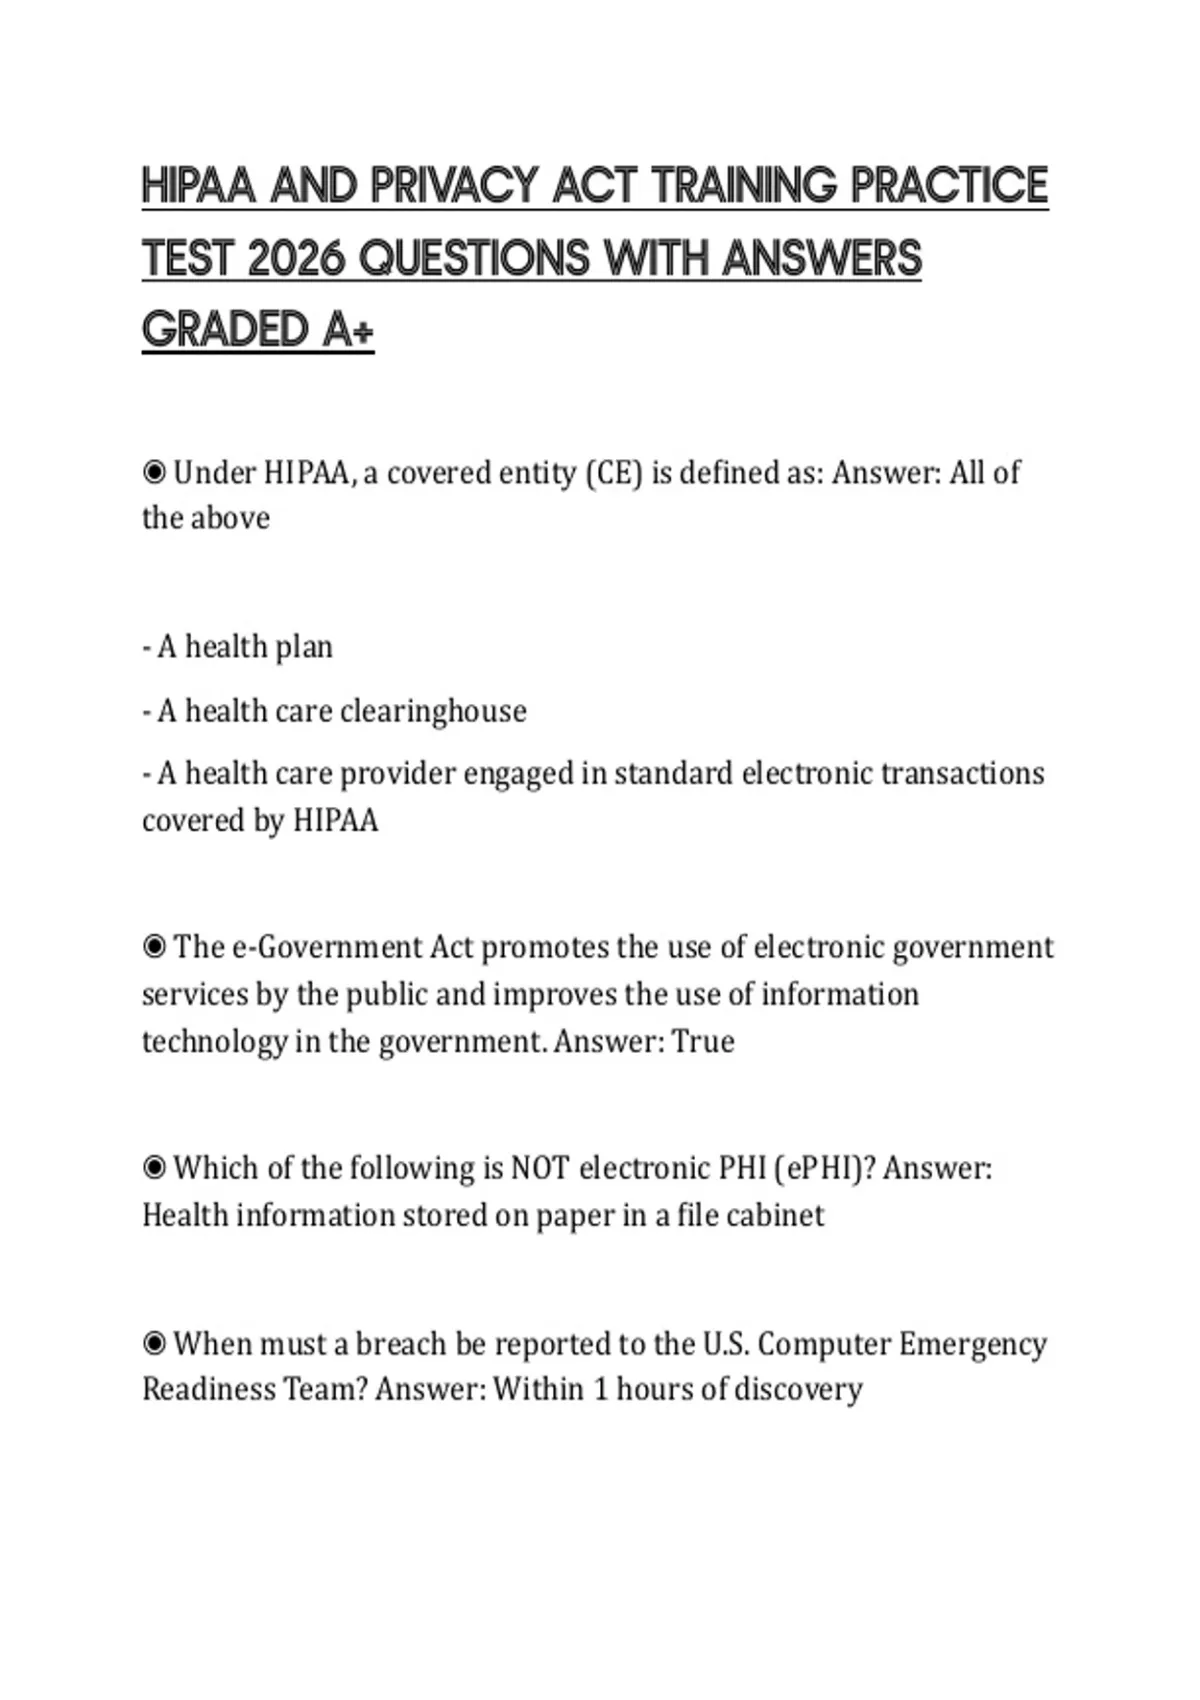
The certification exam doesn't ask you to recite the statute verbatim. It presents a scenario—usually a short paragraph describing a workplace situation—and asks which response best complies with HIPAA requirements. The answers often look plausible. One will be the right one, another will be partially right but miss a detail, and the rest will sound confident but violate a specific rule. I spent three years auditing healthcare facilities for compliance, and I watched staff members get tripped up on questions that seemed straightforward until you read the wording carefully. The practice test is useful, but not all of them are created equal. Some are accurate, some are outdated, and some are outright misleading because they simplify nuanced regulations into false binaries.
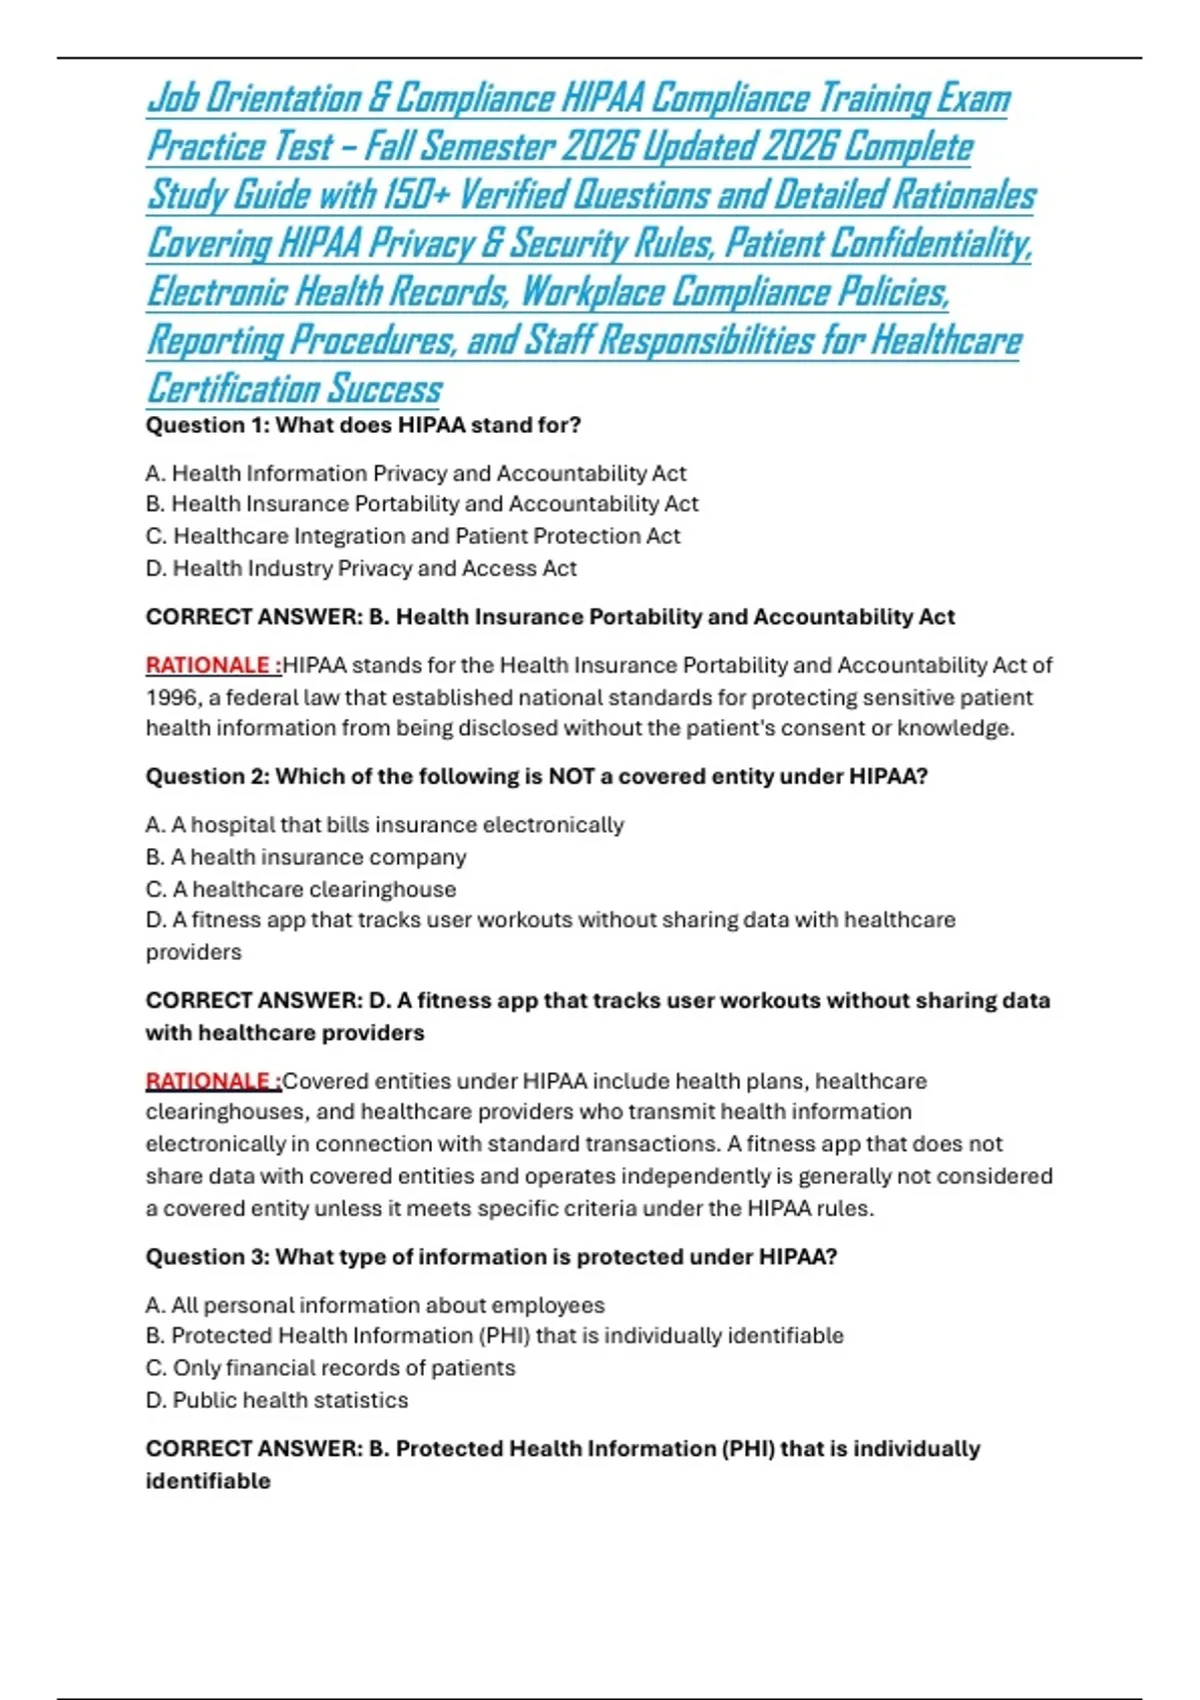
Hipaa Certification Practice Test
A legitimate practice exam covers the Privacy Rule, the Security Rule, the Breach Notification Rule, and portions of the Omnibus Rule. It tests your ability to apply those regulations to real situations, not just memorize definitions. You will see questions about minimum necessary disclosures, patient rights to access their records, business associate agreements, and incident response procedures. The format is usually multiple choice with four options, though some exams include scenario-based clusters where one question references the same case study. Here is a realistic edge case I ran into repeatedly: practice tests often present questions about sharing information with family members. The correct answer usually hinges on whether the patient has the capacity to make healthcare decisions and whether sharing aligns with the patient's expressed preferences. Many practice questions oversimplify this to "never share without consent," which is wrong. HIPAA permits sharing with family involved in the patient's care when the patient is present and does not object, or when you can reasonably infer consent from the circumstances. I once caught a colleague failing a practice question on this topic because the answer key treated it as an absolute prohibition. The real exam does not. When I designed training materials, I made sure to flag this distinction explicitly rather than letting people memorize an incorrect simplification. Counter-intuitive insight number one: the Security Rule applies almost entirely to electronic protected health information. If your organization handles paper records only, you are still subject to the Privacy Rule, but the technical safeguards in the Security Rule—access controls, audit controls, integrity controls, transmission security—simply do not apply to you. People conflate the two constantly. Practice questions will test whether you know which rule governs which situation. If you assume everything falls under one umbrella, you will pick wrong answers on questions about encryption requirements or contingency planning for non-electronic systems.
Counter-intuitive insight number two: breach notification has a specific four-factor risk assessment you must apply before deciding whether an inadvertent disclosure constitutes a breach. The factors are the nature and extent of the PHI involved, the unauthorized person who received it, whether the PHI was actually viewed or acquired, and the extent to which the risk has been mitigated. A common mistake on practice exams is selecting "report everything" when the question describes a low-risk scenario—like a nurse accidentally discussing a patient's condition in an elevator where no patient was present and no identifying information was shared beyond a first name. That may not meet the threshold for a reportable breach depending on the assessment. The exam wants you to show you understand the four-factor test, not just memorize a blanket reporting rule. The downside of practice tests is that they are only as good as their source material. The HIPAA certification exam is administered by a few different organizations, each with its own question bank. Some vendors sell practice tests that are outdated pre-2009 material, before the HITECH Act amendments. Others pull questions directly from the official exam and resell them, which violates testing policy and gives you false confidence because you have already seen the exact wording. I recommend treating any practice test as a study aid, not a prediction tool. If a provider claims their questions are "identical to the real exam," that is a red flag. Another limitation: practice tests rarely capture the full scope of the actual exam. The real certification covers more ground than most commercial practice sets offer. You should expect questions on state privacy laws that are stricter than HIPAA, patient authorization requirements, marketing and fundraising restrictions, and the specifics of what constitutes a business associate relationship. A practice test that only covers the Privacy Rule and ignores the Security Rule is incomplete. Look for comprehensive coverage, or better yet, use the official study guide from the certifying body and supplement it with practice questions from a reputable source.
Get the Full Details
What works in practice is mixing study methods. Read the actual regulation text—not a summary. The language is dense but precise, and the exam tests precision. Then take practice questions under timed conditions. Afterward, review every answer you got wrong and trace it back to the specific regulatory section. If you are weak on breach notification, study that section thoroughly before moving on. Do not just memorize the correct answer; understand why the other options are wrong. That is where the real learning happens. For download links and current practice test materials, check the official website of the certifying organization you plan to use. They typically provide sample questions and study guides directly. Third-party resources exist, but verify their currency and accuracy before relying on them. The regulations change, and outdated practice tests can actively harm your preparation by reinforcing incorrect interpretations. The bottom line is that a HIPAA Certification Practice Test is a tool, not a guarantee. Use it to identify gaps in your knowledge, not to confirm what you already know. The exam rewards careful readers who understand the nuance behind the rules. It punishes people who memorize shortcuts. Study the regulation, practice with quality questions, and expect to encounter scenarios that force you to think through the four-factor analysis rather than recall a soundbite.