The Reality of Doing a HIPAA Risk Assessment Without Paying for Software
Most covered entities and their business associates will grab a free template and expect that to satisfy NIST SP 800-30 Rev. 1 or the OCR audit protocol expectations. It doesn't, not really, but it's a starting point. I've gone through about fourteen of these per year across different practice sizes, and the pattern is always the same: people fill in the spreadsheet, assume compliance, and then get caught on technical safeguards because the template never asked about them.
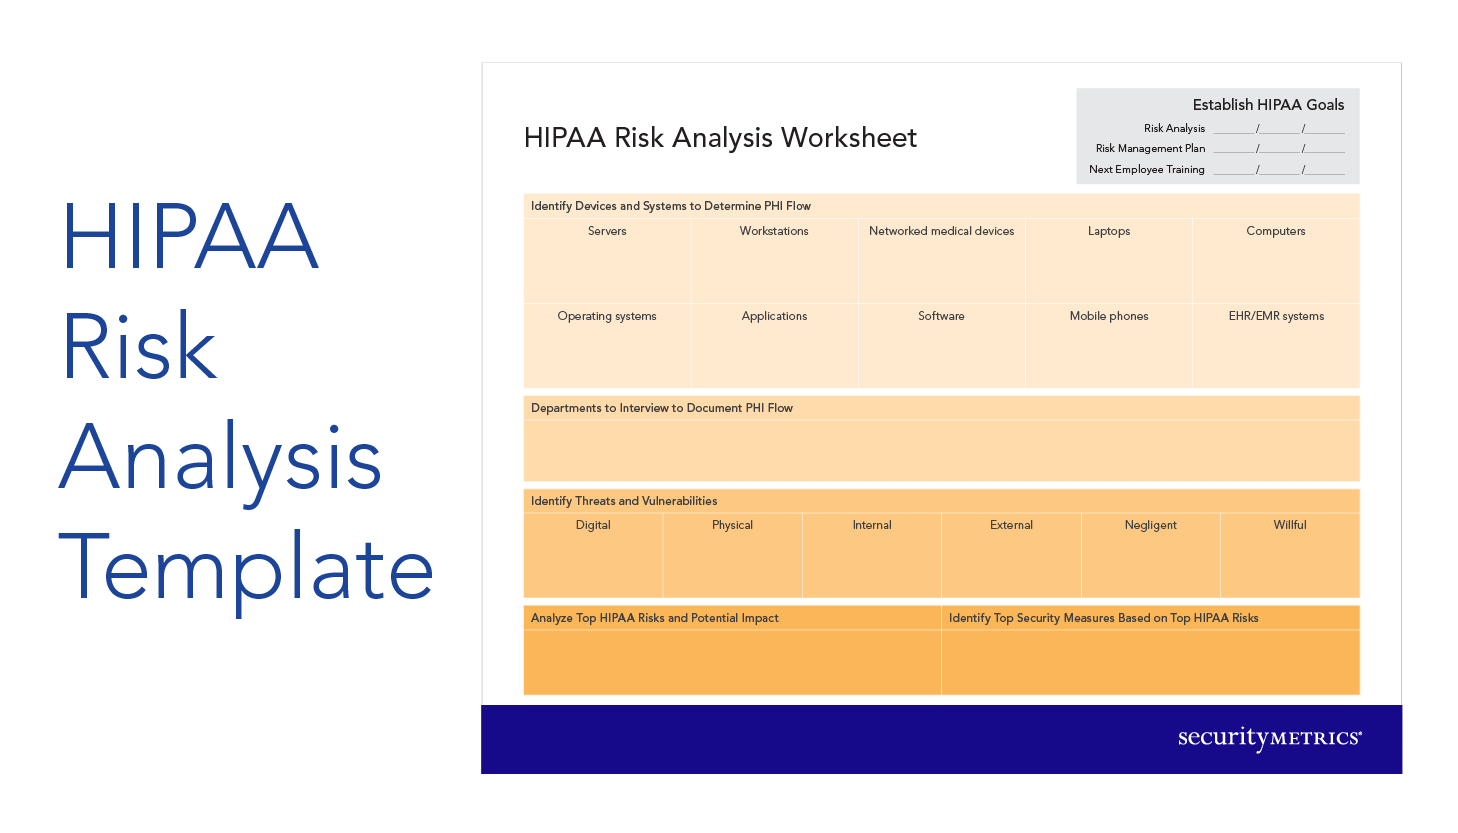
The core document you're looking for is a risk assessment template that captures the five required elements under the Security Rule's Risk Analysis rule (45 CFR §164.308(a)(5)): accurate identification and valuation of threats and vulnerabilities, a process for determining likelihood and potential impact, a method for documenting findings, a remediation plan, and ongoing monitoring. A
Hipaa Risk Assessment Template Free
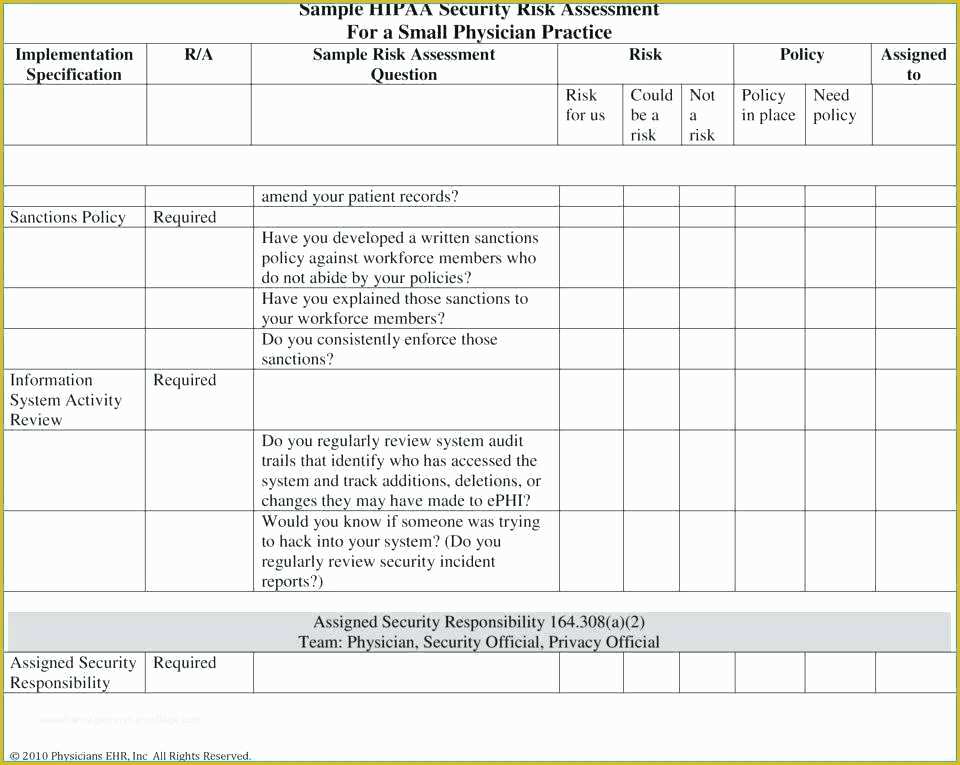
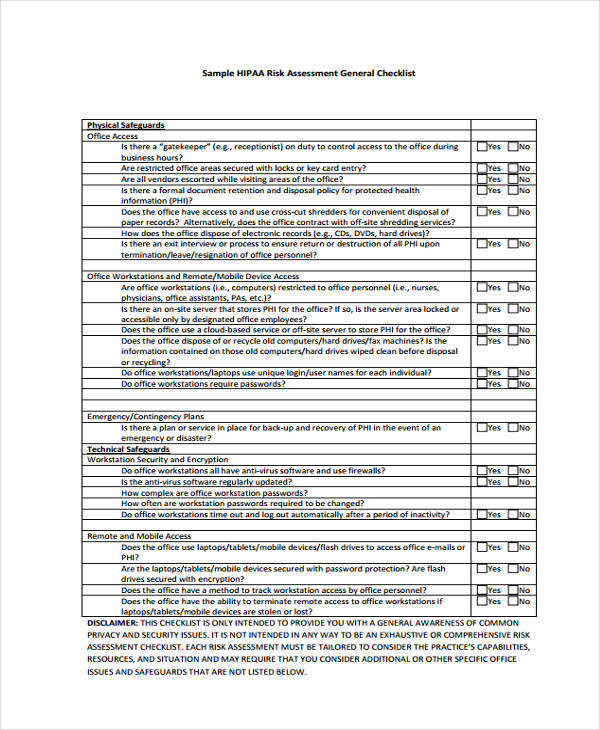
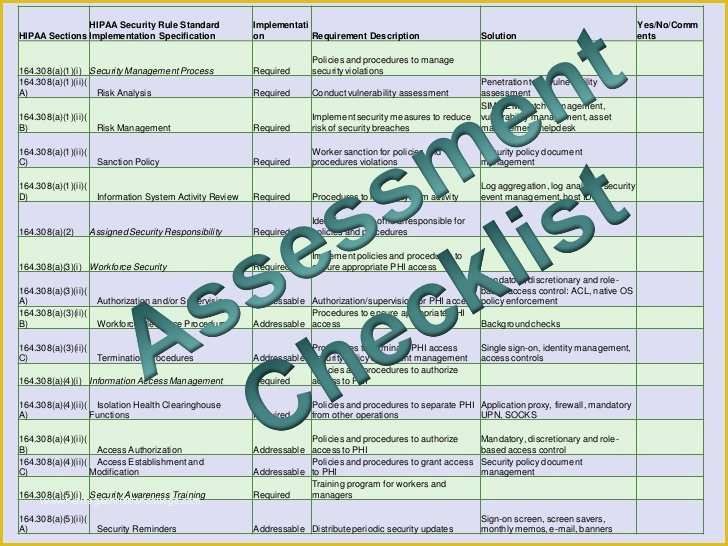
spread-sheet typically includes columns for asset identification, data type, threat source, vulnerability, likelihood rating, impact rating, risk level, existing controls, residual risk, and a corrective action field. That structure is functional for a small clinic or a solo practitioner with maybe twenty endpoints and a single cloud EHR. It breaks down the moment you bring in multiple business associates, remote work, mobile devices, or any kind of legacy system that the template can't categorize.
I ran into this about three years ago with a multi-site dental group. They were using a basic free template and everything looked green until I found that their offsite backup was an unencrypted USB drive kept in the office manager's desk drawer. The template had no row for removable media stored outside of inventory tracking. I added a section for portable storage and shadowed their backup rotation for two weeks. We logged every drive, assigned a unique identifier, and tied it to a physical access log. That alone generated twelve new findings that the original template would have missed entirely.
The counter-intuitive thing about these assessments is that the risk matrix itself matters less than the asset inventory underneath it. You can't calculate a realistic likelihood score if you don't know how many unpatched Windows 7 machines are still on the network or whether your cloud provider actually encrypts data at rest. I've seen organizations rate every risk as low because the template asked for a subjective percentage rather than forcing them to verify whether the control existed at all. OCR audits penalize that pattern because it signals the assessor didn't do the actual work.
Here is how I actually run through this when I'm not just stamping a form.
Step one: define scope and inventory assets. List every system that creates, receives, stores, or transmits ePHI. That includes laptops, phones, printers with hard drives, cloud services, VoIP systems, and even fax machines on the network. Write down the data type on each one. You will be surprised how many of these you forgot about.
Step two: map threats and vulnerabilities against NIST SP 800-30 categories. Threat sources fall into four buckets: natural, environmental, human accidental, and human malicious. Vulnerabilities are the weaknesses that let those threats succeed. A template will give you checkboxes, but you need to look at your actual environment. For example, phishing is a common threat, but the real vulnerability is often that your email filtering doesn't catch domain impersonation attacks until after someone clicks. Document that specifically.
Step three: score likelihood and impact. Likelihood uses a scale like rare, unlikely, possible, likely, almost certain. Impact uses categories like minor, moderate, major, catastrophic. The matrix produces a risk level: low, medium, high, critical. Don't let the spreadsheet auto-calculate this without reviewing each cell. I have seen templates default every finding to low because the person entering the data didn't understand the difference between a theoretical threat and a documented incident from the past year. Past incidents change the likelihood number entirely.
Step four: document existing controls and identify gaps. This is where the free templates usually stop being useful. The template lists hypothetical controls like encryption and access controls but never asks you to prove they are actually enabled and configured correctly. Go check. Look at the settings in your EHR, your VPN, your MDM, your backup software, your security information and event management tool. If you don't have SIEM, configure cloud audit logs at minimum. Record what you find.
Step five: calculate residual risk and build a remediation plan. Residual risk is what remains after you apply your current controls. If a risk stays high after controls, you need a remediation plan with an owner, a deadline, and a budget line. I always add a column for cost estimate and affected business processes because that is what actually gets approved. A risk treatment that doesn't include dollars and timeline is just a wish list.
Step six: get sign-off and schedule review. The rule requires management sign-off. Not a rubber stamp. The responsible official needs to read the document and accept or reject the risk decisions. After that, you revisit the assessment at least annually, after any significant change to the environment, or after an incident. I recommend a mid-year refresh even if nothing changed because threats evolve and your asset list probably did.
There are practical problems with relying exclusively on a free template. First, they don't update. The OCR guidance and NIST publications shift over time, and a static PDF from 2019 will miss newer threat categories like supply chain compromise and API-level vulnerabilities in third-party integrations. Second, free templates treat every organization the same. A hospital with fifty thousand patients faces materially different risk than a solo telehealth provider, but the template asks identical questions. Third, there is no audit trail. If an auditor asks why you rated a particular risk as medium, you need to point to evidence. A spreadsheet with no version history and no attached screenshots of control configurations is not defensible.
I usually take a free template and rebuild it inside a structured tool. I import the columns, add mandatory evidence links for each finding, and force a comment field before any risk score can be saved. It takes about an extra hour to set up but it cuts the time an auditor spends questioning your methodology down to almost nothing. For the actual template itself, the HHS website hosts reference materials that include sample assessment forms you can adapt. There are also reputable vendors who publish free versions of their paid tools with reduced feature sets. Those are generally better maintained than a random download from a forum.
If you run a small practice and want to start immediately, download a NIST-aligned template, populate the asset inventory section first, and spend more time on steps two and four than anyone else does. The risk scores come later.
Gallery Hipaa Risk Assessment Template Free
57 Hipaa Security Risk assessment Template Free | Heritagechristiancollege
Hipaa Risk Assessment Template | Free Sample, Example & Format Template
Hipaa Risk Assessment Template | Free Sample, Example & Format Template
57 Hipaa Security Risk assessment Template Free | Heritagechristiancollege
Hipaa Risk Assessment Template | Free Sample, Example & Format Template