The Spreadsheet That Saves Your Compliance Team
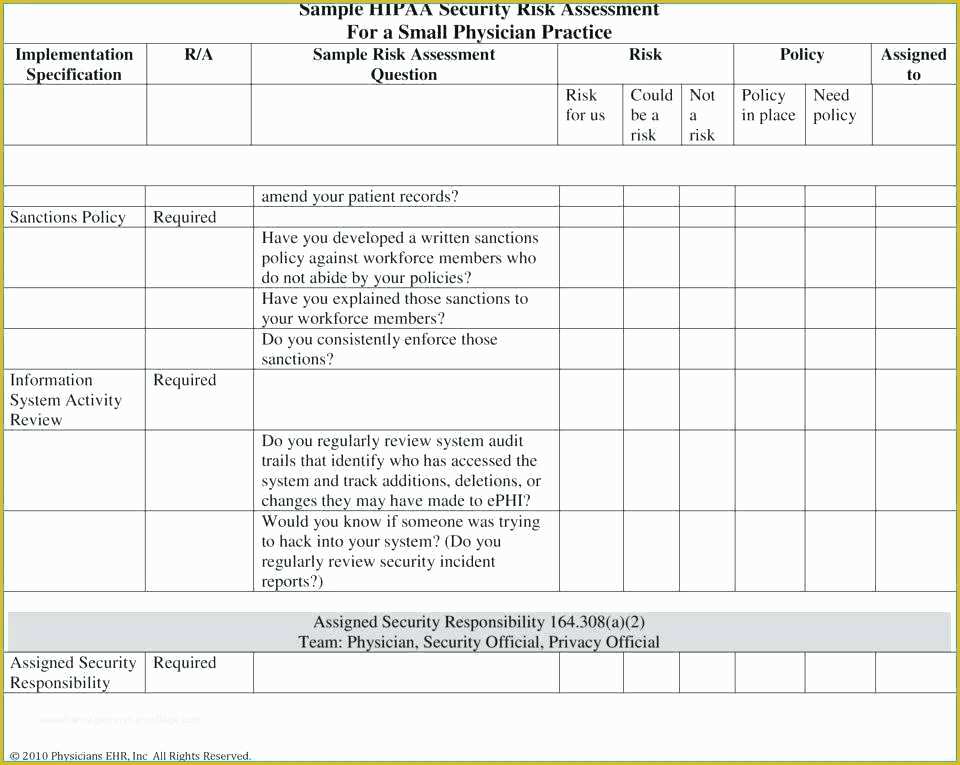
I spent three days last year trying to figure out why our annual risk assessment kept drawing a blank from our auditor. The issue wasn't that we hadn't done the work. It was that we were using a convoluted custom template built by our IT team in 2018, and it missed entire categories of risk that the newer guidance explicitly called out. We ended up switching to the HHS/AHRQ toolkit and cut our assessment time down to about two days for a mid-size practice. The difference wasn't philosophy. It was structure. The HHS and AHRQ toolkit is fundamentally a set of Excel spreadsheets. It walks you through identifying where electronic protected health information lives across your environment, evaluating the safeguards currently in place, and scoring the likelihood and impact of potential threats. The scoring isn't subjective guesswork if you actually fill out the reference tables they provide, but it does require honest answers. A lot of people skip the reference tables because they think they already know the answers. That's where things fall apart. Here is how the process actually works in practice. You start by mapping your ePHI flow. Not just your servers. Your vendors, your mobile devices, your backup systems, the contractor who updates your billing software remotely. The toolkit asks you to list each node where ePHI is created, received, maintained, or transmitted. Then for each node, you go through the threat categories: unauthorized access, malware, natural disaster, workforce error, and so on. You score each threat based on the likelihood and the potential impact if it occurs. The tool then calculates a residual risk score after you factor in existing safeguards.
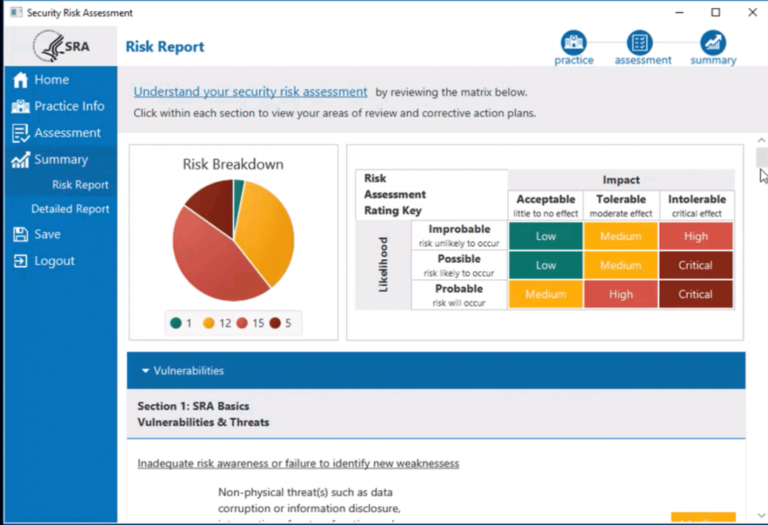
One thing beginners consistently mess up is the gap analysis section. The spreadsheet tells you what controls are required under the Security Rule, but it doesn't automatically tell you which ones you're missing. You have to manually mark each control as implemented, partially implemented, or not implemented. I used to just mark everything as implemented to speed things along. That habit got me burned when an auditor asked me to demonstrate evidence for our access control procedures and I had nothing to show for half the checklist items. Now I only mark a control as implemented if I can produce a dated policy document, a system configuration screenshot, or a completed training record that supports it. It takes longer but it actually holds up. The download link for the official toolkit is on the HHS website under the Office of the National Coordinator for Health IT section. It is free. The current version includes separate spreadsheets for small practices, medium organizations, and large entities, so pick the one that matches your scale. Using a hospital system's template for a ten-person clinic will just create noise and unnecessary questions. There is a common misconception that this tool gives you a final risk level and you are done. It does not. The output is a risk profile that you then have to triage. The tool will tell you that your lack of endpoint encryption on field staff laptops carries a high risk score, but it will not automatically prioritize that over the fact that your backup encryption keys are stored in the same cabinet as the servers themselves. You still need to do that prioritization step yourself. That said, the tool does include a default risk matrix you can adapt, and it saves significant time compared to building that matrix from scratch.
Another nuance that trips people up involves the vendor section. The toolkit asks about business associate agreements and third-party risk, but it does not automatically pull in your BAA inventory. I keep a separate spreadsheet tracking every BAAs I have on file with expiration dates, and I cross-reference it against the tool's vendor questions before finalizing. Without that cross-check, you can easily miss a vendor whose agreement expired two years ago and is still processing ePHI. That gap alone would fail an audit. The tool has real limitations. It was designed primarily for healthcare organizations, not for technology companies that build HIPAA-covered systems. If you are a software vendor assessing risk for a product that handles ePHI, this toolkit will not map cleanly onto your threat landscape. You would be better off using the NIST 800-30 risk assessment framework and then mapping the results back to HIPAA requirements. The HHS toolkit assumes you are a provider or health plan evaluating your own operations, not a SaaS company evaluating your platform. Another limitation is that the scoring is intentionally conservative. The tool tends to push you toward high risk on anything involving remote access or mobile devices, which is fair given the threat environment, but it means you will end up with a lot of red on your risk profile even if you are reasonably secure. The workaround is to document your mitigations thoroughly in the notes field for each risk item. A well-documented mitigation with evidence reduces your effective residual risk in the auditor's eyes even if the raw score stays high.
Get the Full Details

For organizations that want something more automated, there are commercial platforms like Drata, Vanta, and Securly that claim to handle HIPAA risk assessments as part of a broader compliance program. They integrate with your cloud infrastructure and can pull configuration data automatically. They are not free, and they work best if you are already running other compliance frameworks like SOC 2 or ISO 27001. If you are a small clinic trying to complete your annual risk assessment without a compliance budget, the HHS spreadsheet is still the most practical starting point. The biggest piece of advice I can give is to run through the toolkit once without trying to make it look good. Write down the ugly answers first. The ones where you know you are non-compliant or partially compliant. Then go back and fix the gaps before anyone else sees the document. An assessment that reveals nothing is worse than an assessment that reveals everything, because the former gives you a false sense of security and the latter gives you a roadmap.