Building a HIPAA Staff Manual When You Actually Have to Comply
Most template downloads you find online are garbage. They copy-paste regulatory text without adding any operational language, so your staff reads three pages of definitions and then goes back to doing whatever they were doing before. A proper staff manual isn't about reciting the law. It's about giving people clear instructions for the specific situations they'll actually encounter in your practice. I spent about six months last year overhauling our compliance documentation after an internal audit flagged that our existing handbook had section references that didn't match our current software stack. The old version referenced a fax system we'd decommissioned two years prior and listed three points of contact who no longer worked here. That alone is enough to make an auditor raise an eyebrow. The fix wasn't harder than it sounds, but it did require going line by line through every document instead of relying on a downloaded template.
Hippa Template For Staff Manual
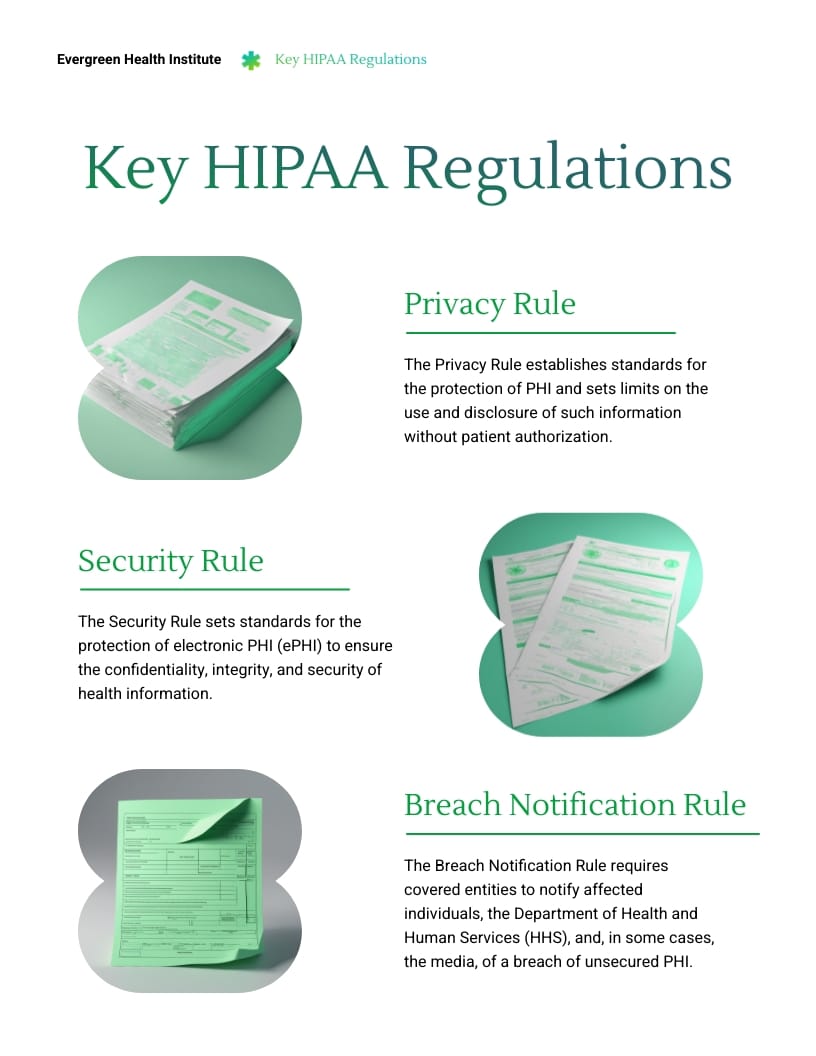
When you're looking for a starting point, the term you'll actually run into is a HIPAA staff manual template, though people commonly type it as "Hippa Template For Staff Manual." It functions as a skeleton. The template gives you headers like Privacy Rule, Security Rule, Breach Notification Rule, and sanctions policy, but none of that matters if the content inside doesn't match your environment. Your electronic health record system, your email setup, your physical access controls, and your business associate agreements all need to be reflected in the manual or it's essentially fiction written down. Here is what I actually include in ours, in the order I put it in: Workforce orientation requirements, including that every new hire signs acknowledgment of the manual within 30 days of start date. This is a HHS OCR expectation even though the regulation does not state a specific number of days, and I recommend keeping it at 30 because auditors usually look for a defined window. Physical safeguards section covering lock policy, workstation use, and screen positioning. Technical safeguards mapped directly to the tools we use, like our EHR access controls, encryption standards for portable devices, and audit log review procedures. Administrative safeguards including role-based access definitions and the process for granting and revoking permissions. Business associate agreement handling, which most templates underplay. A breach notification workflow with actual timelines and escalation paths. Sanctions policy that names real consequences rather than vague language about disciplinary action. And incident response procedures that specify who does what when a potential breach occurs.
The section I see people consistently mess up is the business associate handling part. You need a procedure for obtaining signed BAAs before any vendor accesses ePHI, a register where those agreements are tracked with expiration dates, and a process for reviewing changes to vendor relationships. I keep this in a shared spreadsheet with columns for vendor name, service type, BAA signature date, renewal date, and the internal owner responsible for that relationship. When our billing vendor changed their hosting provider last year, the old template-based manual had nothing about that scenario, so we updated it inline and noted the change log entry next to the relevant section. That level of maintenance is what separates a compliant document from a decorative one. One edge case I ran into involved a part-time contractor who accessed patient records through our EHR using a shared clinical workstation. The question was whether that workstation count as a mobile device under our policy, since it was stationary but could theoretically be unplugged and moved. The rule is clear that any device capable of accessing ePHI falls under mobile device encryption requirements, but the wording in most templates makes this ambiguous. My workaround was to add a definition clause to the manual stating that any network-connected or locally authenticated workstation used for clinical purposes is subject to the same encryption and access controls as portable devices, regardless of whether it moves. This closed the loophole and gave our IT team a clear policy to enforce during spot checks. Another thing that trips people up is the difference between a policy and a procedure. The policy says encryption must be used on portable devices. The procedure explains how to turn on FileVault, where to find the encryption key, and who to contact if a device is lost. Templates often collapse these into one paragraph, which makes the document useless for training purposes. Keep them separate. Use the policy sections to define requirements and the procedure sections to describe steps. Your staff needs to know what to do when something happens, not just what the rule says.
Get the Full Details
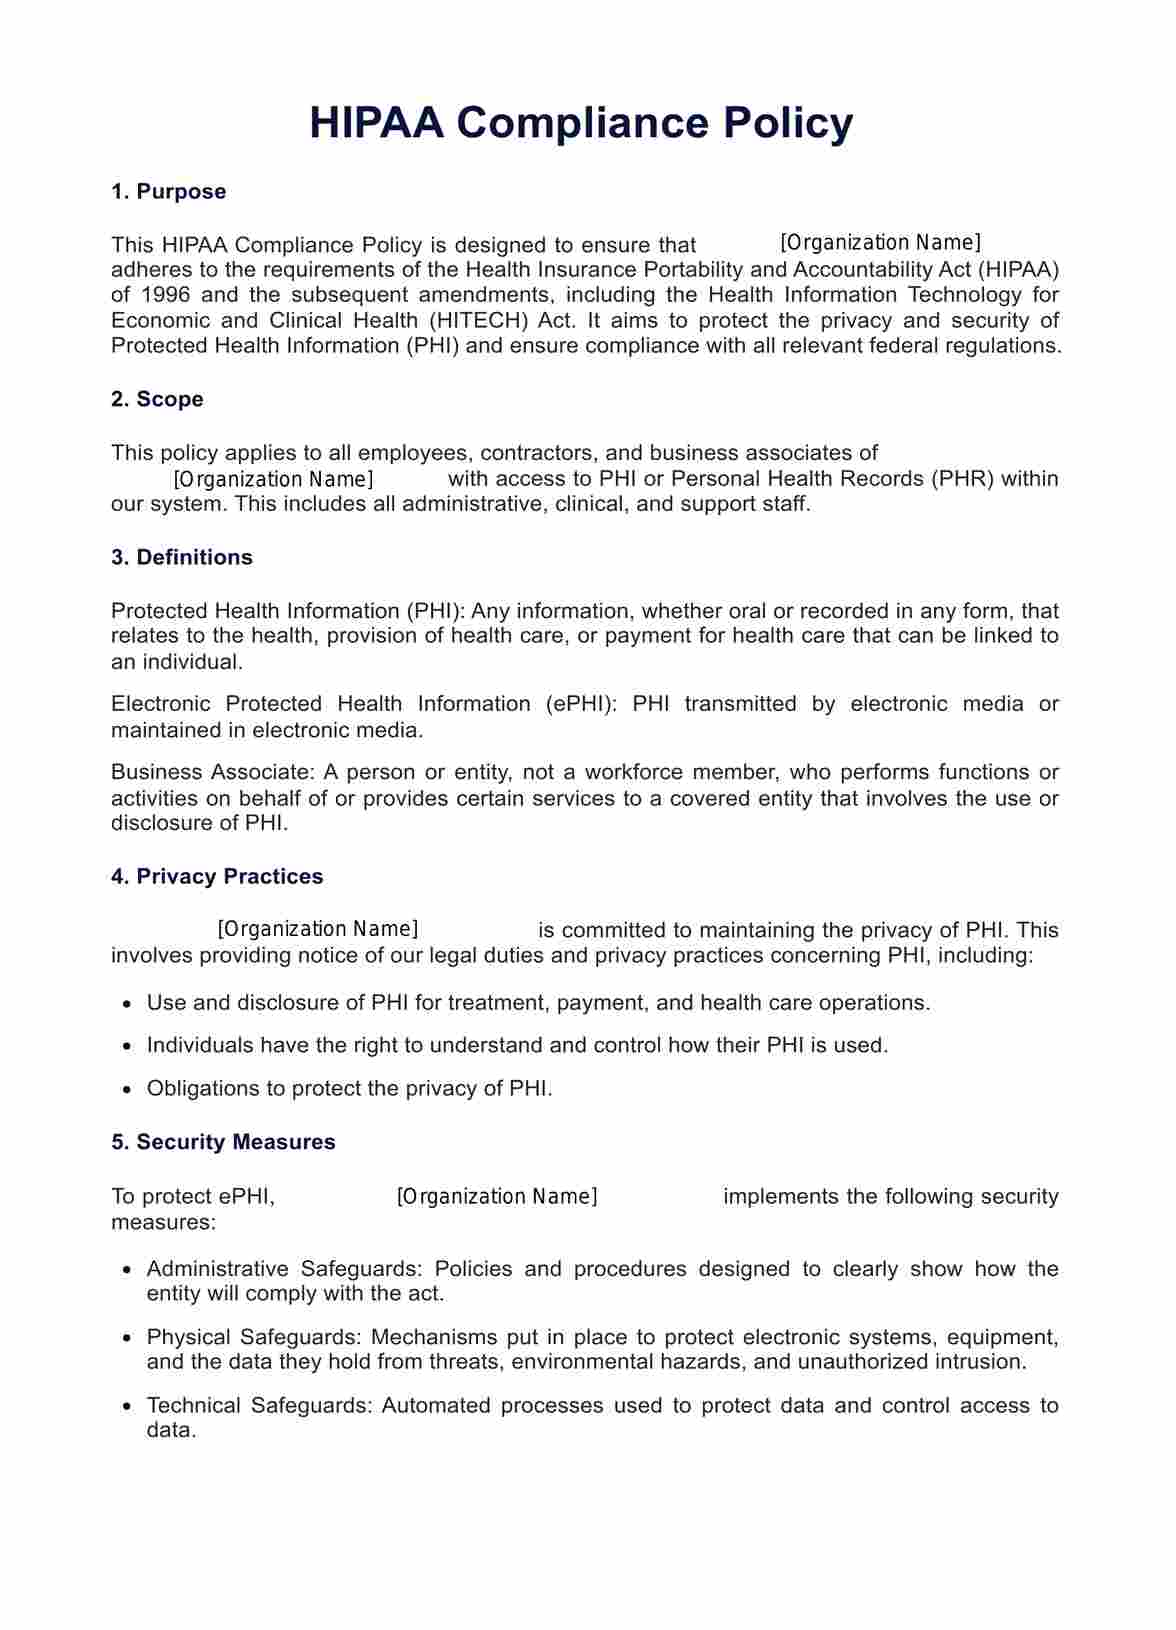
The Security Rule implementation specification table is where most manual templates derail. HHS organizes the specifications as addressable versus required, and addressable does not mean optional. It means you either implement the specification or document why you cannot and adopt an equivalent alternative measure. I once saw a manual that listed addressable controls as suggestions with checkboxes that nobody ever checked. That is not defensible during an audit. Every addressable specification in your scope needs either an implementation record or an alternative measure justification on file. Training content should not be generic. If you tell staff to "handle PHI responsibly," that is not training. It is a wish. Effective training specifies scenarios: what to do if you receive a fax intended for another provider, how to verify a caller's identity before releasing information, where to store printed labels, what constitutes a reportable incident. I built our annual training module around twelve realistic scenarios pulled from actual near-misses in our own practice. The material was boring to write but the engagement during training sessions improved noticeably because people recognized the situations. There are real limitations to any template approach. A downloaded template cannot account for your specific technology stack, your staffing structure, or your risk analysis findings. It cannot replace your actual Risk Analysis, which is a separate required document under the Security Rule. It cannot substitute for your incident response plan or your contingency plan. Using a template as a standalone solution will leave gaps large enough that a breach investigation would expose them immediately. The template is a framework, not a compliance product.
If you need a place to begin, the HHS website provides guidance documents that map directly to the rule requirements. Many compliance vendors sell templates that cost between eighty and three hundred dollars, but the content in most of them is public domain regulatory text rearranged into sections. I have seen some well-organized versions that include fill-in fields and procedure outlines, and those can save you a few hours during the first draft. Just expect to spend more time adapting it than saving time by downloading it. The manual should be a living document. Version control matters more than people realize. I use a simple header on each section showing the effective date, revision number, and the person who authored the change. When we updated our email encryption procedure after switching providers, the change log showed exactly what was different, which made the audit trail clean and reduced questions during review. Without that tracking, you end up with outdated procedures that still have current dates stamped on them, which is worse than having no manual at all. Retention of the manual and all associated policies is required for six years from the date of creation or last effective date, whichever is later. Store copies in both digital and physical form if possible. Digital copies should be backed up with access restricted to authorized personnel only. Physical copies, if maintained, should be stored in a locked cabinet separate from active patient files to avoid unnecessary exposure.
Write the manual for the people who will actually read it. Short sentences. Specific examples. Clear ownership assignments. If a section requires a manager to approve something, name the role, not a person. People leave. Roles stay. The manual should outlive every individual who works here.