What You Actually Need To Know Before Booking One
A security threat assessment is not a single event. It is a process that ranges from a few days to several months depending on the scope of the environment you are putting it through. Most people think they are getting a simple report, but the reality involves reconnaissance, vulnerability analysis, risk mapping, and validation that takes time regardless of how aggressive your vendor is. For a small business with a handful of servers, a modest web application, and basic network infrastructure, you are looking at roughly two to four weeks from kickoff to final report. That includes the initial scoping call, asset discovery, the active testing window, and the review period where your team validates findings before the final deliverable goes out. Mid-market organizations with hybrid cloud environments, dozens of internal applications, and third-party integrations typically fall into the six to ten week range. Enterprise assessments can stretch to four to six months, especially when you factor in regulatory requirements like SOC 2 Type II or HIPAA compliance workflows that require documented evidence at every phase.
The timeline is rarely fixed because it depends on how cooperative your environment is. If your networking team needs three days just to open firewall rules for the assessment tools, that adds up fast. If your developers have to schedule maintenance windows for every staging server, you are looking at additional delays that have nothing to do with the actual assessment work. I once ran an assessment for a fintech client where the entire timeline ballooned from six weeks to fourteen because their production database was not properly segmented from their development environment. The assessors could not safely run vulnerability scans against the dev database without risking data contamination, so we had to spend an entire week isolating the networks before we could even start the technical phase. That kind of infrastructure mess is far more common than people want to admit.
The Phases And What Controls The Schedule
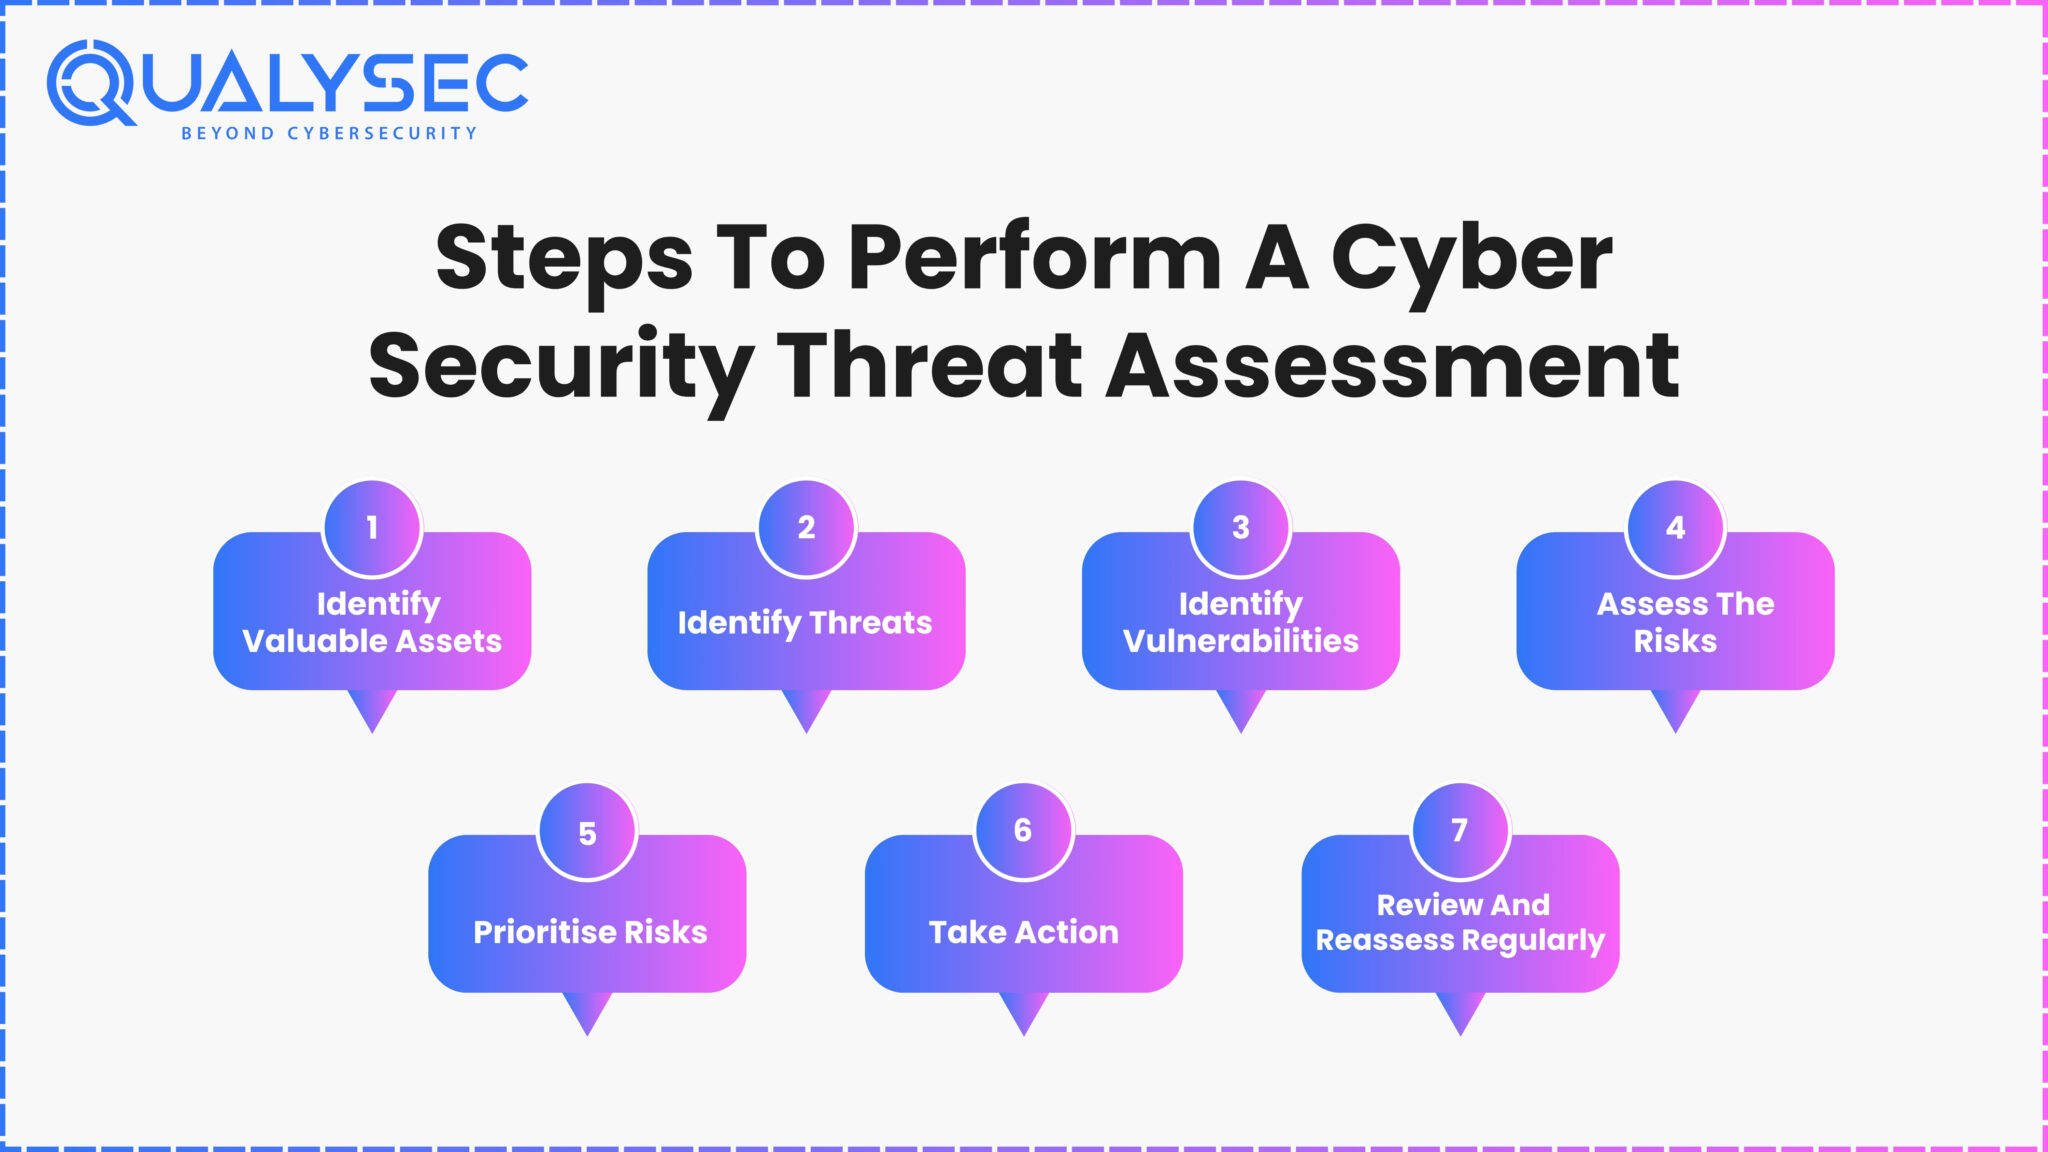
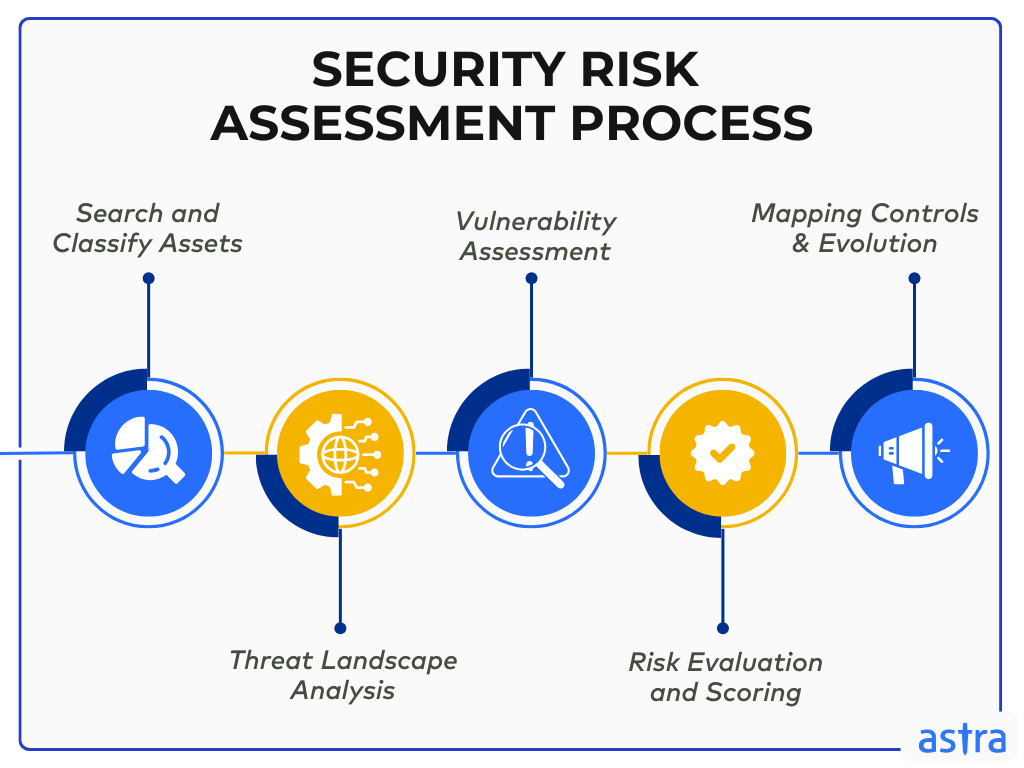
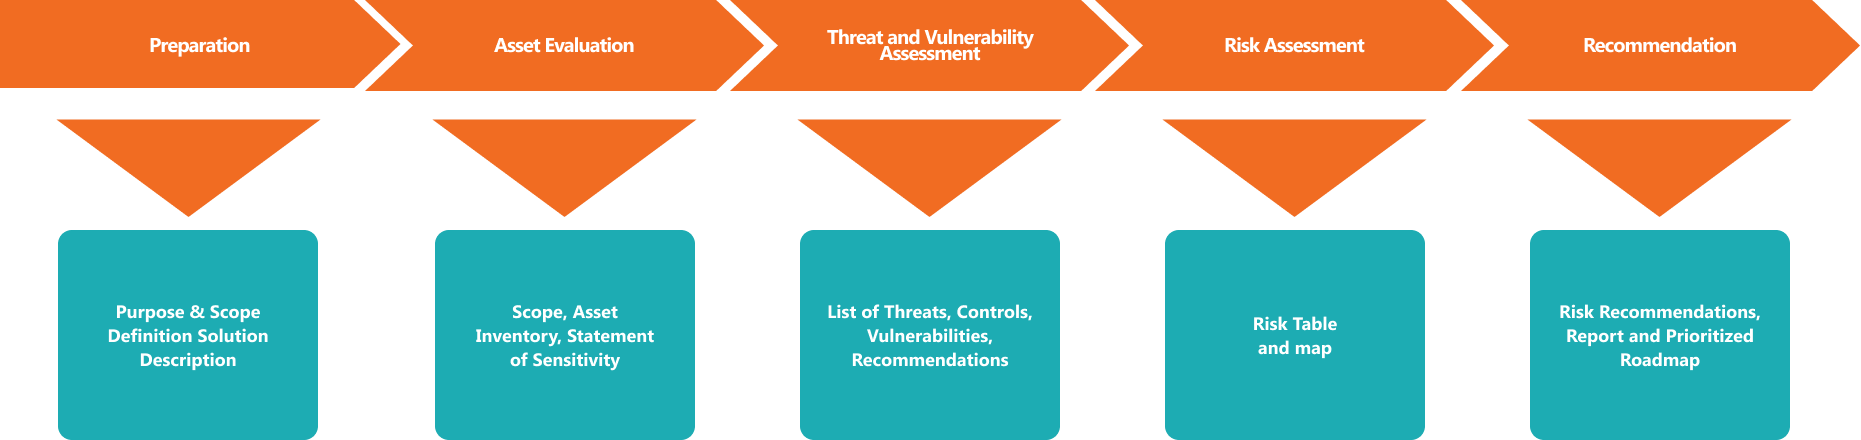
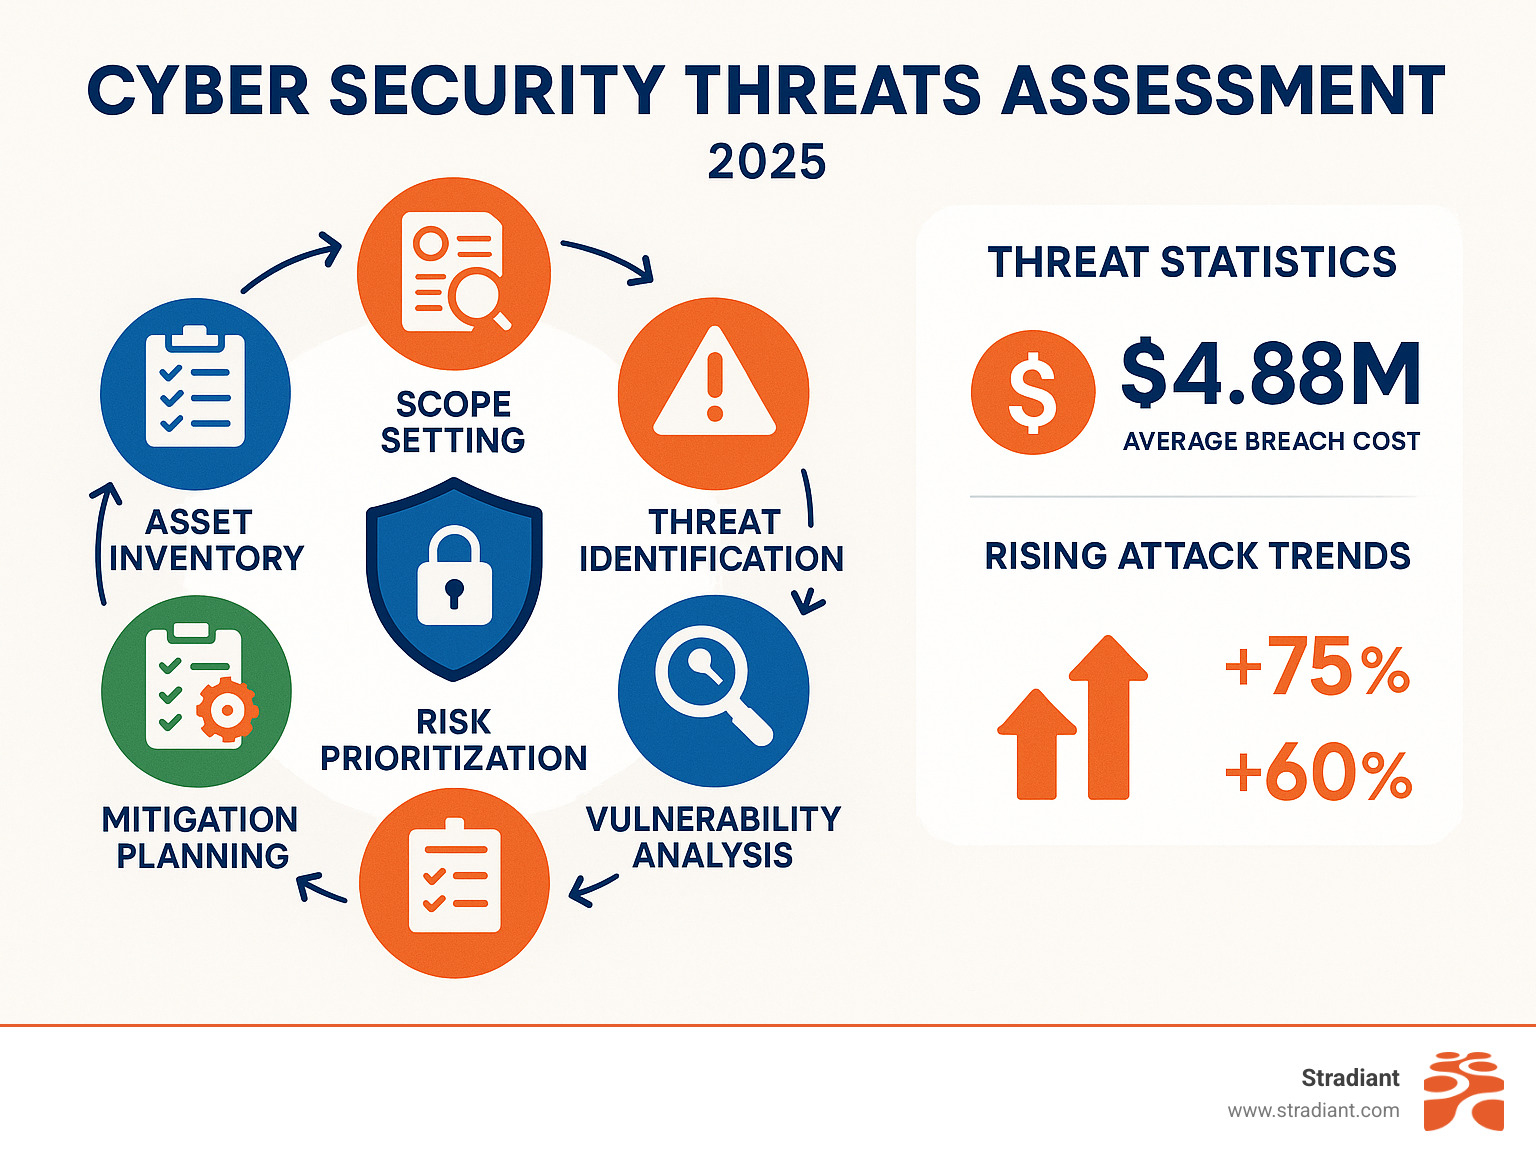
Every assessment follows roughly the same structure, though the naming conventions vary between vendors. The first phase is scoping and planning, which usually takes one to two weeks. During this time you define what is in bounds and what is out of bounds, establish communication protocols, agree on testing windows, and confirm that you have written authorization for every system involved. The reconnaissance phase can take anywhere from three to ten business days. Assessors gather information about your public-facing assets, enumerate subdomains, map external attack surfaces, and build a baseline of what they are working with. This is where many organizations underestimate the time required because they assume a basic scan will suffice. It does not, especially if you have a large attack surface with multiple CDNs, third-party services, and regional deployments. Vulnerability analysis is the longest phase for most engagements. It typically spans two to four weeks depending on the depth of testing. This is where the actual exploitation attempts happen, alongside manual verification of automated scan results. Skilled assessors spend significant time confirming whether a flagged vulnerability is a true positive or a false alarm, and that manual validation is what separates a decent assessment from a thorough one.
Get the Full Details

Risk mapping comes next and generally takes one to two weeks. At this stage the assessor correlates all identified vulnerabilities with business impact, likelihood of exploitation, and existing controls. A misconfigured S3 bucket in a non-production environment gets a completely different risk rating than the same misconfiguration in your primary customer database. This is where experience matters, and it is also where some rushed assessments cut corners by letting automated tools generate risk scores without human review. The final phase is reporting and remediation support, which adds another one to three weeks. You should expect a draft report, a walkthrough meeting, and time for your team to ask clarifying questions before the final version is released. Some vendors include post-assessment support for thirty to sixty days, which is useful but often billed separately.
Common Pitfalls That Extend The Timeline
The biggest delay factor is poor preparation on the client side. I have seen assessments delayed by weeks because the organization did not have an updated asset inventory. If you cannot tell your assessors which IP ranges belong to you and which are managed by a third party, they cannot scope the engagement properly, and that ambiguity directly inflates the timeline. Another frequent issue is lack of dedicated point of contact. If your IT team is handling assessments on top of their regular responsibilities, response times to assessor questions will drag. A single unanswered email about a firewall exception can stall an entire phase for days. Assigning one person with authority to make decisions during the assessment window usually prevents this problem. Third-party dependencies are a hidden timeline killer. If your application relies on external APIs, payment processors, or SaaS platforms, the assessor needs permission from those providers to test integration points. Some vendors respond within hours. Others require formal requests that take two to three weeks to process. This is completely outside your control, but it is entirely within your control to ask your assessors early whether any third-party testing is included in the scope.
I learned this the hard way on a healthcare compliance assessment where we discovered three weeks into the engagement that the electronic health records vendor would not authorize any penetration testing on their platform. The entire assessment had to be restructured around the remaining systems, and we lost a full month of scheduled work. Had we confirmed third-party testing permissions during the scoping phase, we could have either secured that authorization upfront or removed it from the scope to begin testing immediately.
What Experienced Assessors Know That Beginners Miss
One counter-intuitive insight is that a shorter timeline is not always better. Organizations that push for an accelerated assessment often get a surface-level review that misses deeper logic flaws and architectural vulnerabilities. A rushed two-week assessment will likely catch the low-hanging fruit and obvious misconfigurations, but it will not have time to explore complex attack paths that require sustained manual analysis. Another thing that is not obvious: the quality of your pre-assessment documentation has a direct correlation with the accuracy of your risk ratings. If you provide detailed architecture diagrams, data flow maps, and documented existing controls before the assessment begins, the assessor can allocate time to finding actual gaps instead of spending half the engagement trying to understand your environment. This alone can reduce the reconnaissance and risk mapping phases by several days. There is also a misconception that automated scanning replaces manual testing. It does not. Automated tools can identify known vulnerability signatures, but they cannot replicate the decision-making of a human assessor who understands context, business logic, and the specific threat landscape relevant to your industry. The best assessments use automation as a starting point and dedicate the majority of their budget to manual analysis. If a vendor is promising a comprehensive assessment on a two-week timeline with minimal manual effort, that is a red flag.
When An Assessment Timeline Is Completely Wrong For You
Some organizations do not actually need a full security threat assessment. If you are a small startup with a single web application hosted on a managed platform, have no sensitive data processing, and are not subject to regulatory requirements, a formal assessment might be overkill. A focused vulnerability scan combined with a basic security configuration review could serve your needs in a fraction of the time and cost. Conversely, if you are operating in a high-risk industry like finance or healthcare and handle protected data, a standard assessment timeline may be insufficient. You might need continuous threat monitoring, regular red team exercises, and periodic reassessment rather than a one-time engagement. The initial assessment is still necessary, but treating it as a single event rather than part of an ongoing program is a mistake that many organizations make. Another scenario where the standard timeline breaks down is when you have legacy systems that cannot accommodate modern assessment tools. Older mainframe environments, custom industrial control systems, and isolated networks sometimes require specialized testing approaches that add significant time. I worked with a manufacturing client whose PLC systems could not run standard vulnerability agents without risking production downtime, so we had to design a passive monitoring approach that extended the assessment by three additional weeks.
The practical takeaway is that the timeline you are given should reflect your actual environment, not a vendor's standard package. If someone is quoting you a one-size-fits-all duration without asking detailed questions about your architecture, data handling, regulatory obligations, and third-party dependencies, you are probably not getting an accurate estimate. A proper scoping conversation takes time upfront, but it prevents costly surprises later.