The Problem With How People Actually Write Business Rules
Most business rules end up as vague sentences in a wiki page that nobody reads and nobody can implement. I've seen rule documentation that looked fine in a slide deck fall apart the moment you tried to map it to actual SQL or code. The gap between what the business thinks a rule means and what the system actually does is where projects go sideways. Start by understanding that a business rule is simply a statement of a constraint, calculation, or decision that the organization requires to operate. That's it. No ceremony. The kind of people who say "a business rule is the heartbeat of operational integrity" have never had to turn a rule into a production workflow that actually executes on time. Here's the practical method I use. Write the rule in plain language first. Not in a formal DSL, not in pseudocode, just English. Something like: "A customer receives a discount if they've placed more than five orders in the last 90 days and their total spend exceeds $2,000." Then you break it apart into components. Identify the entity (customer), the condition elements (order count, time window, spending threshold), and the outcome (discount applied).
The next step is defining the scope and the exception path. Every rule you write needs to account for what happens when things don't match the normal case. What if a customer has exactly five orders? What if an order was placed on day 91 of the window? What if they get a partial refund after qualifying for the discount? These edge cases are what separate usable rules from theoretical ones. I remember one specific project where we documented a rule for calculating loyalty points: members earn one point per dollar spent, capped at 5,000 points per month, with a multiplier of 1.5x for premium tier members. The rule seemed straightforward until we had to implement it. The problem was return processing. A customer would spend $3,000 in a month, earn 3,000 points, then return $1,500 worth of goods the next week. The rule documentation didn't specify whether the point deduction should happen immediately or at the end of the billing cycle. The engineering team implemented immediate deduction, but the finance team expected end-of-cycle adjustment. Both teams had read the same document and made different assumptions. The workaround was to add an explicit clause to every rule that covers temporal sequencing of state changes, and I now treat that as a mandatory field in our rule template. It costs maybe 30 seconds to write but it prevents weeks of rework later. The structure I recommend for documenting a rule is consistent but simple:
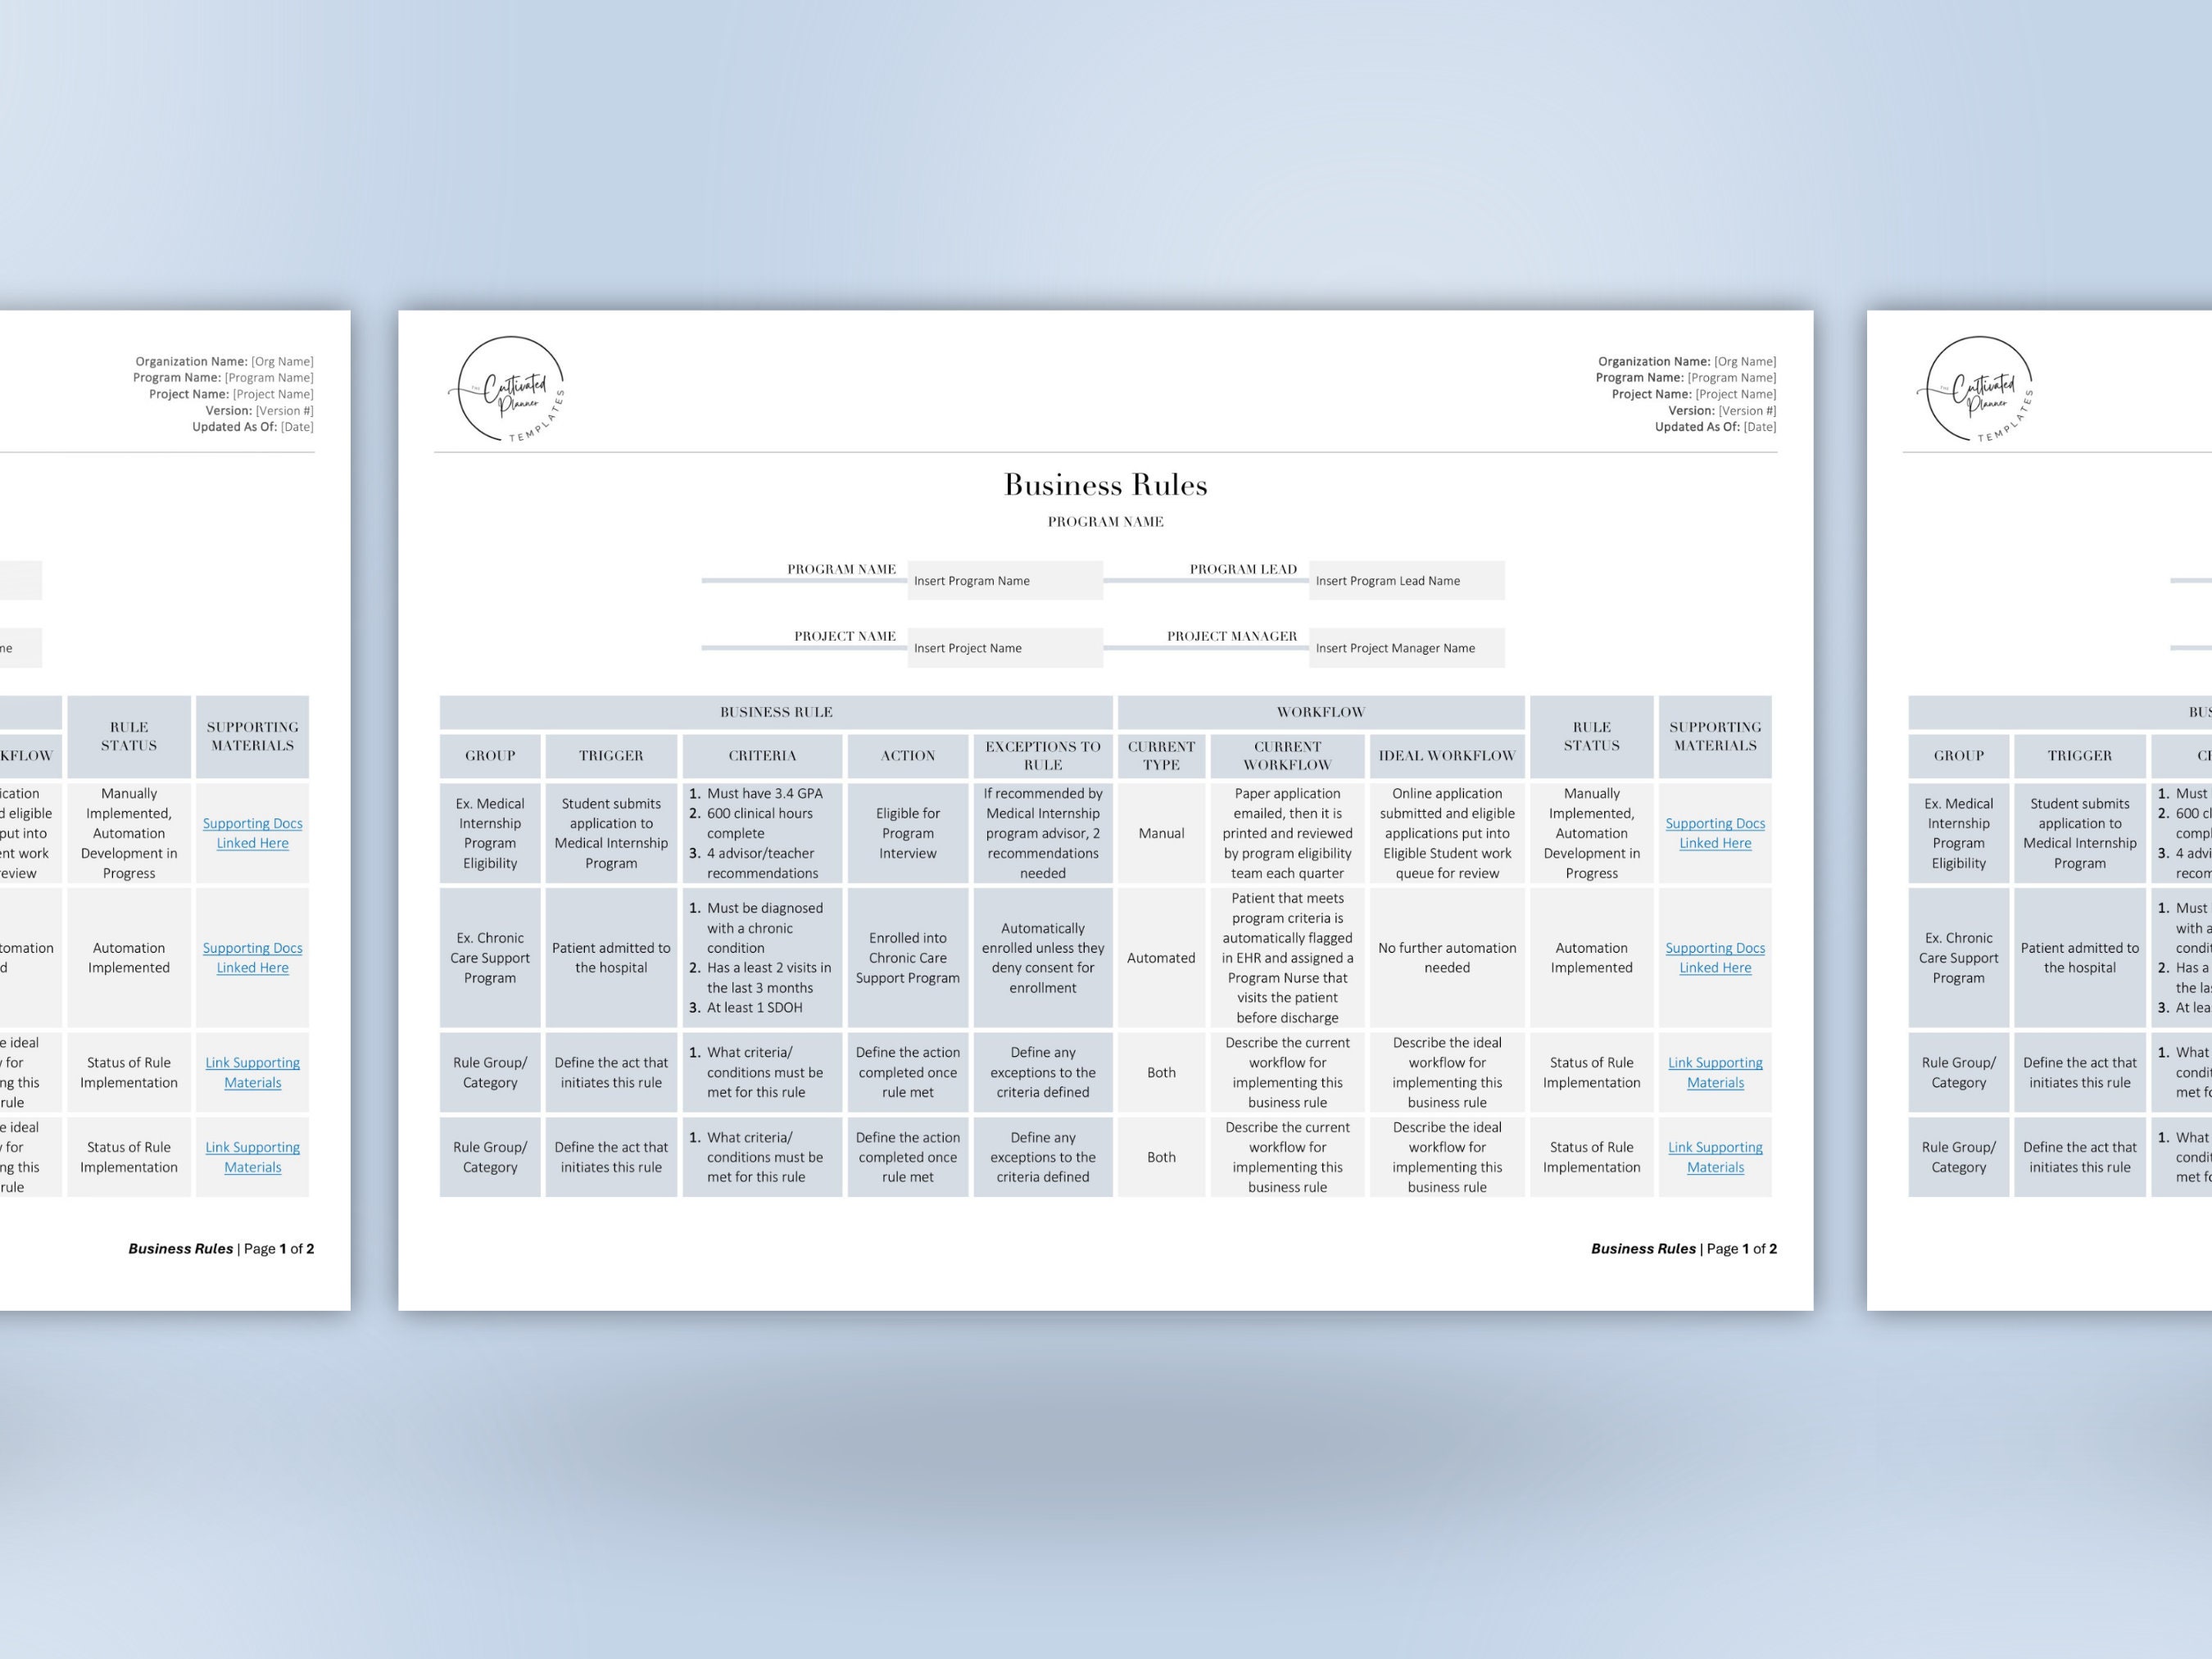
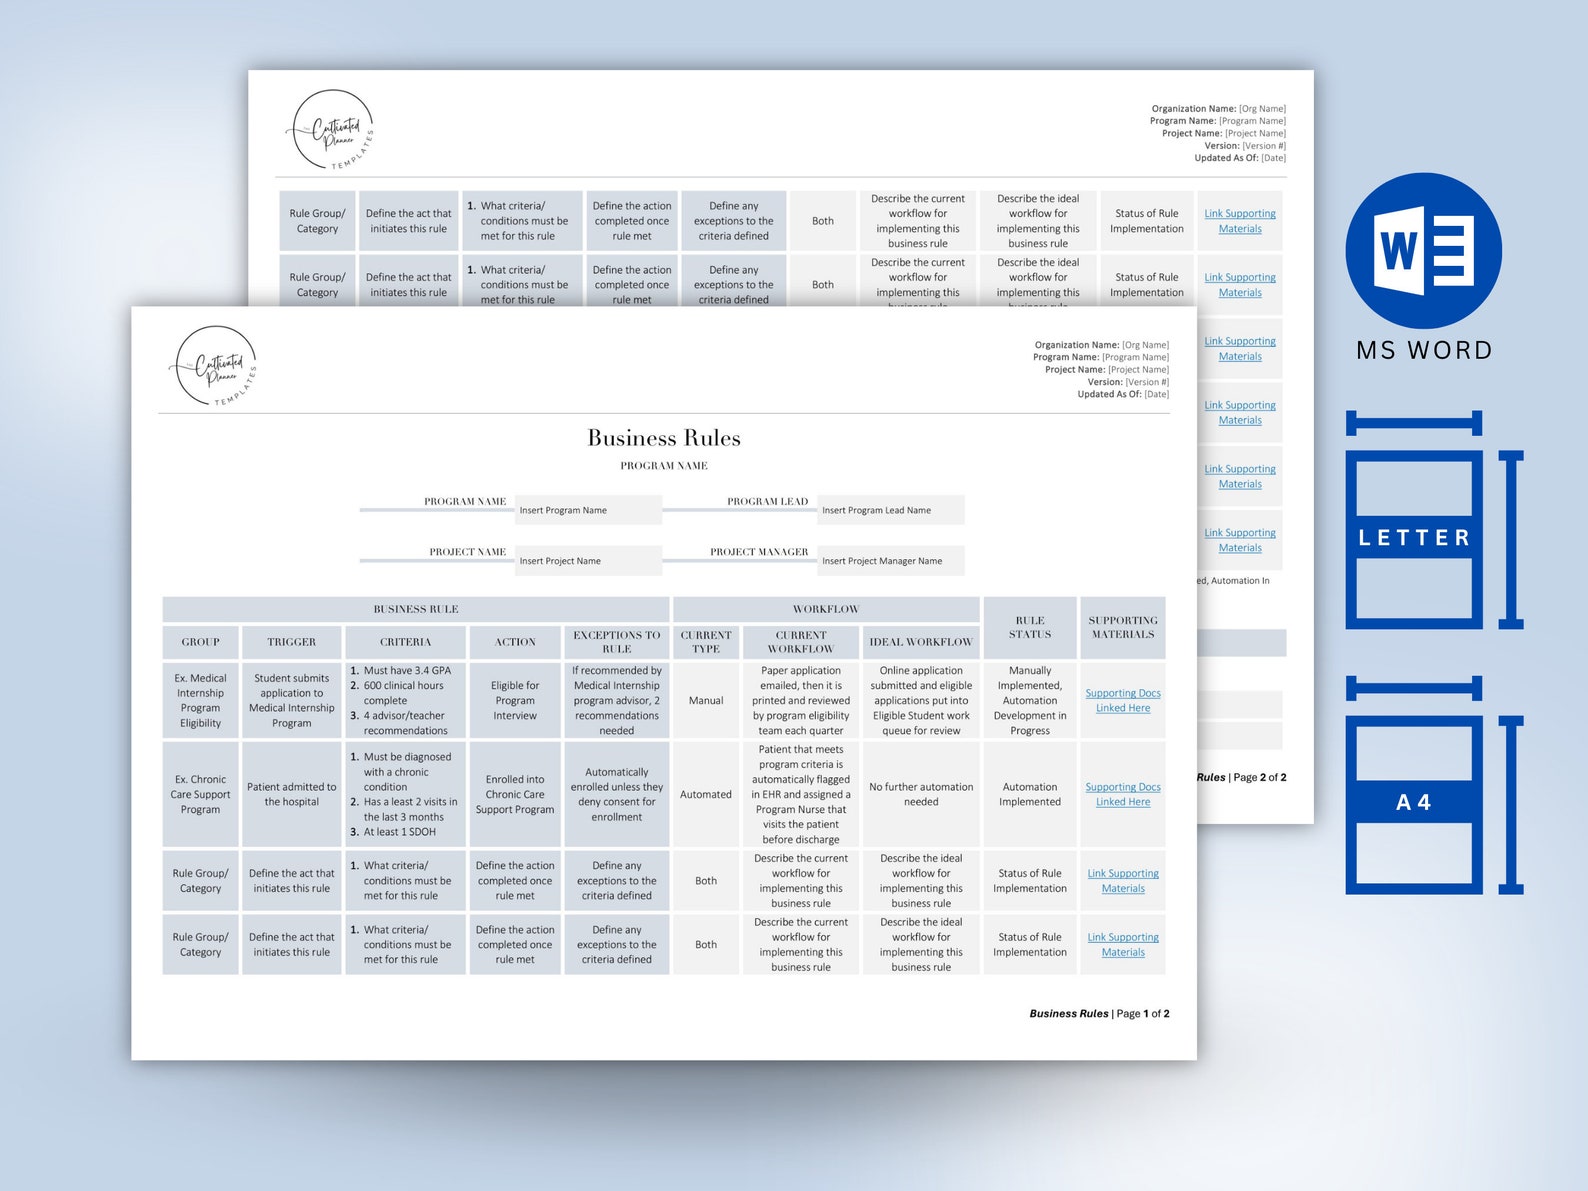
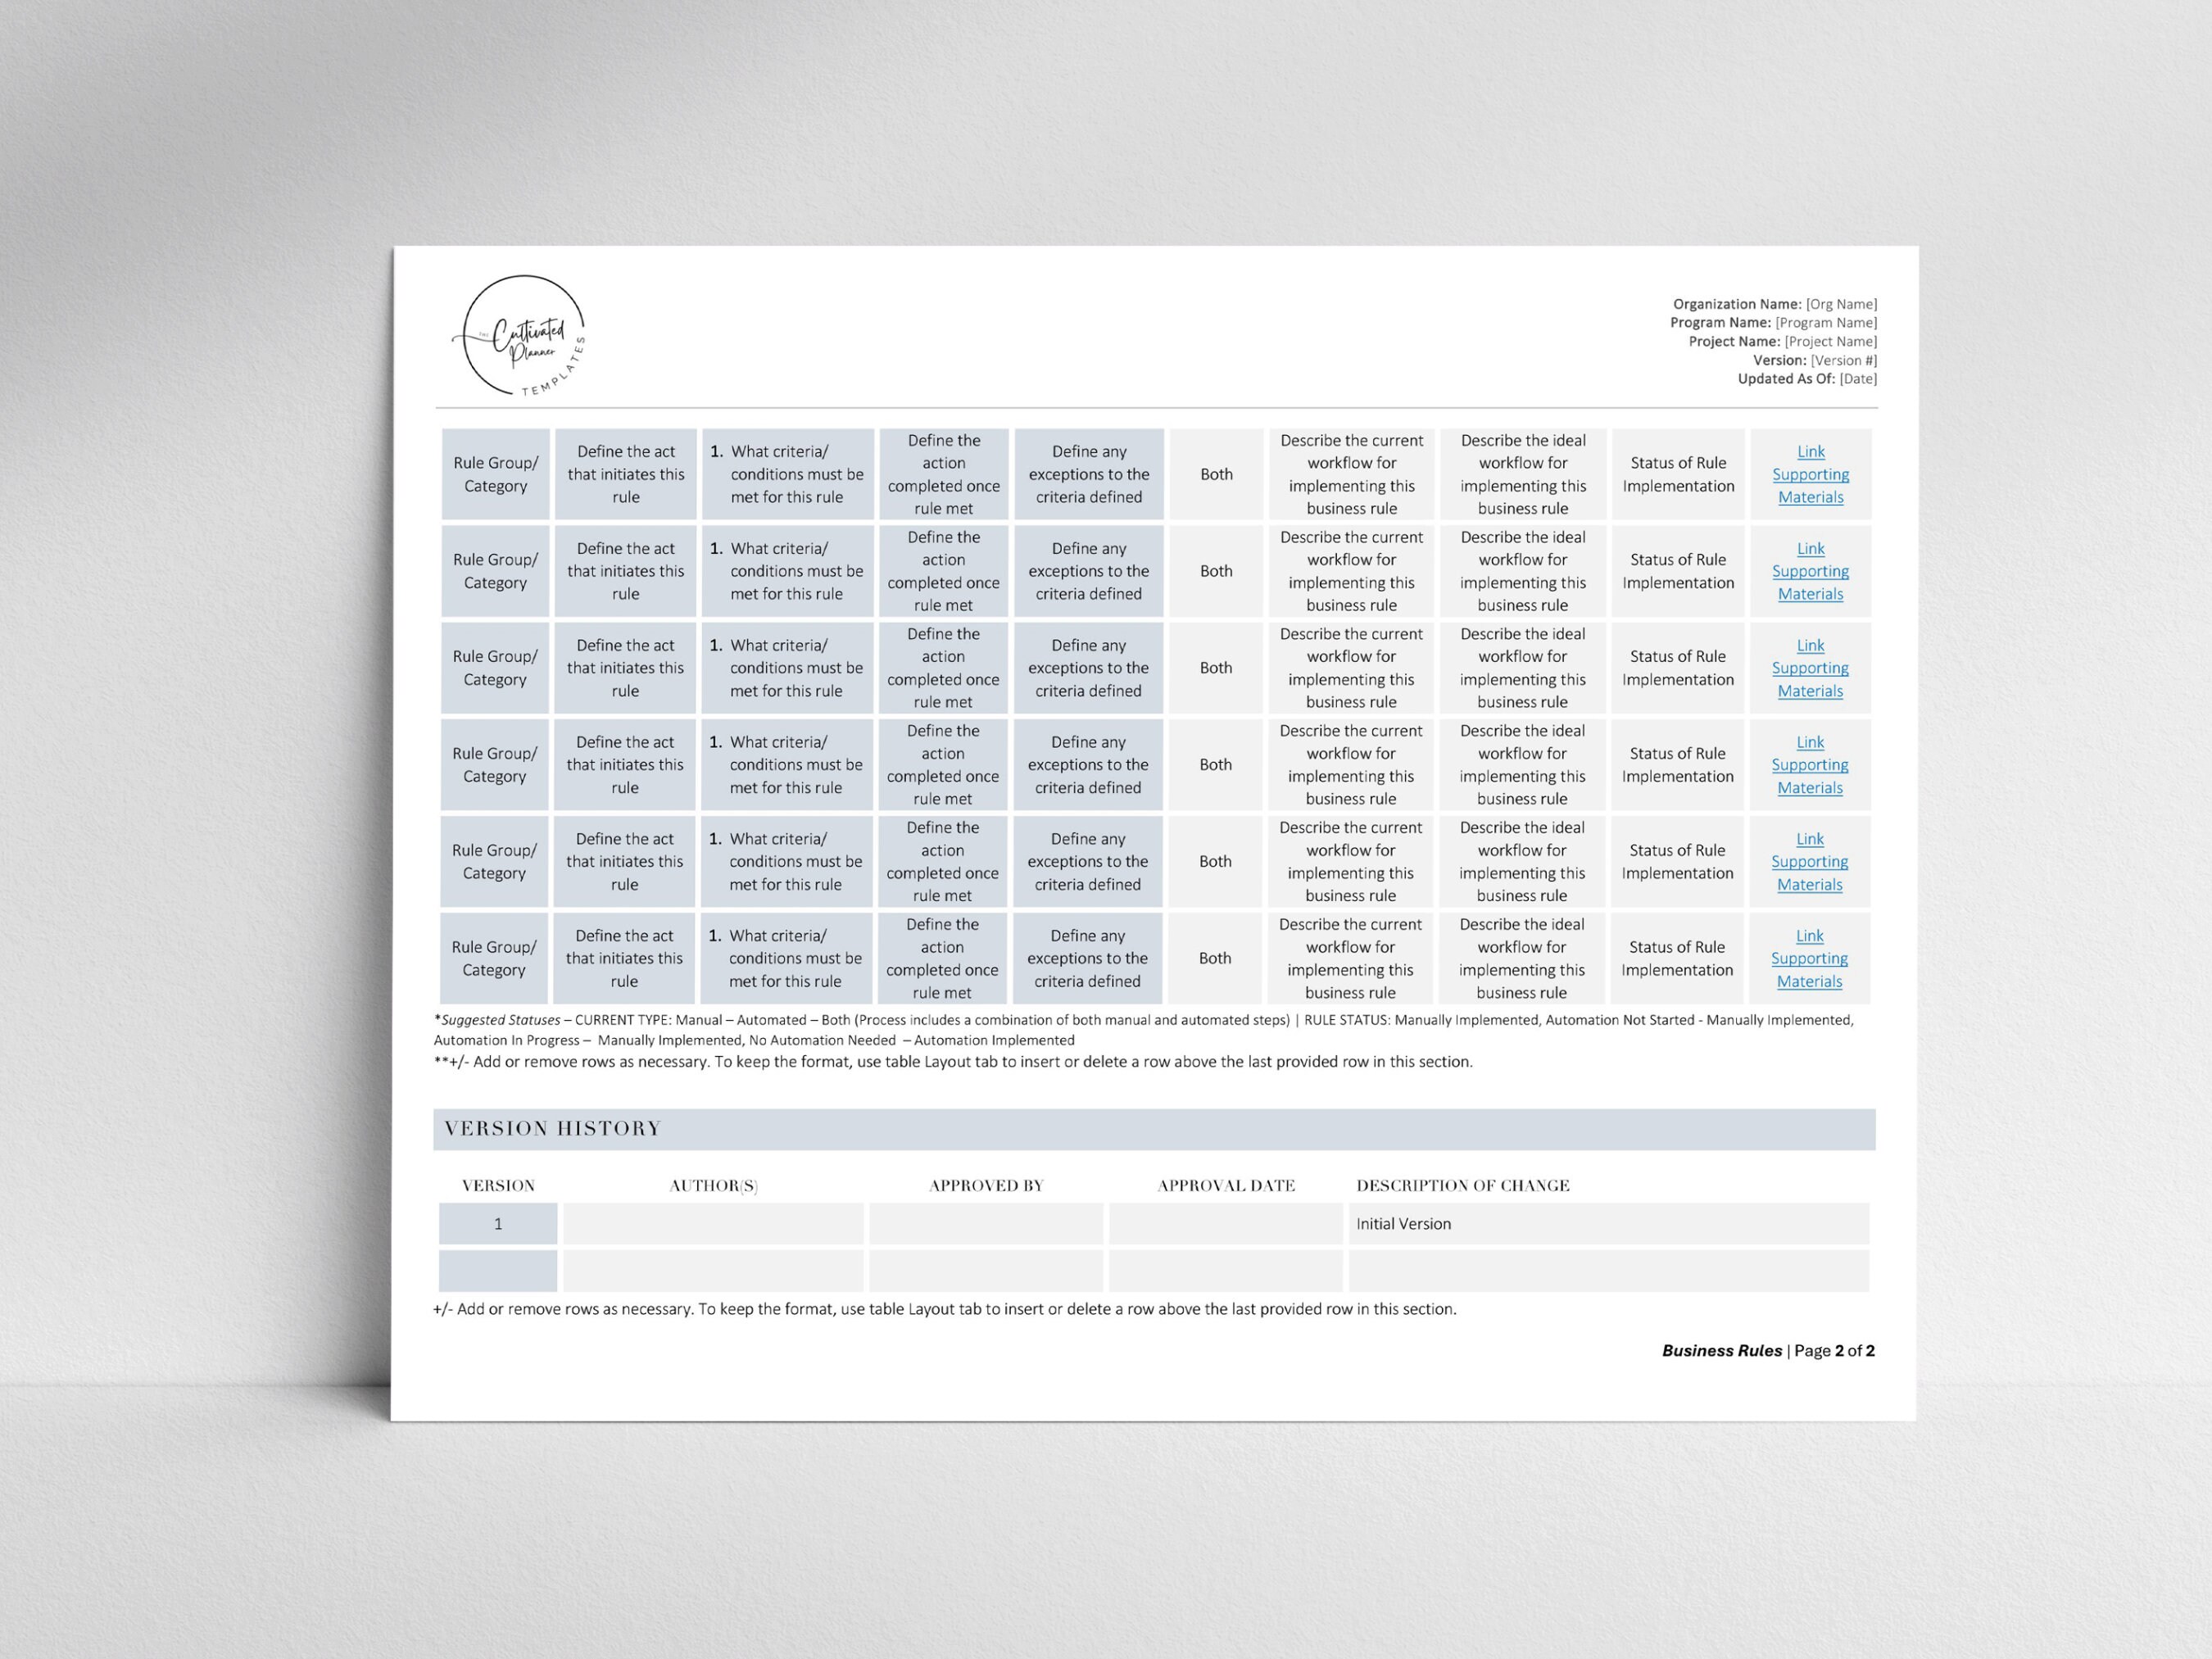
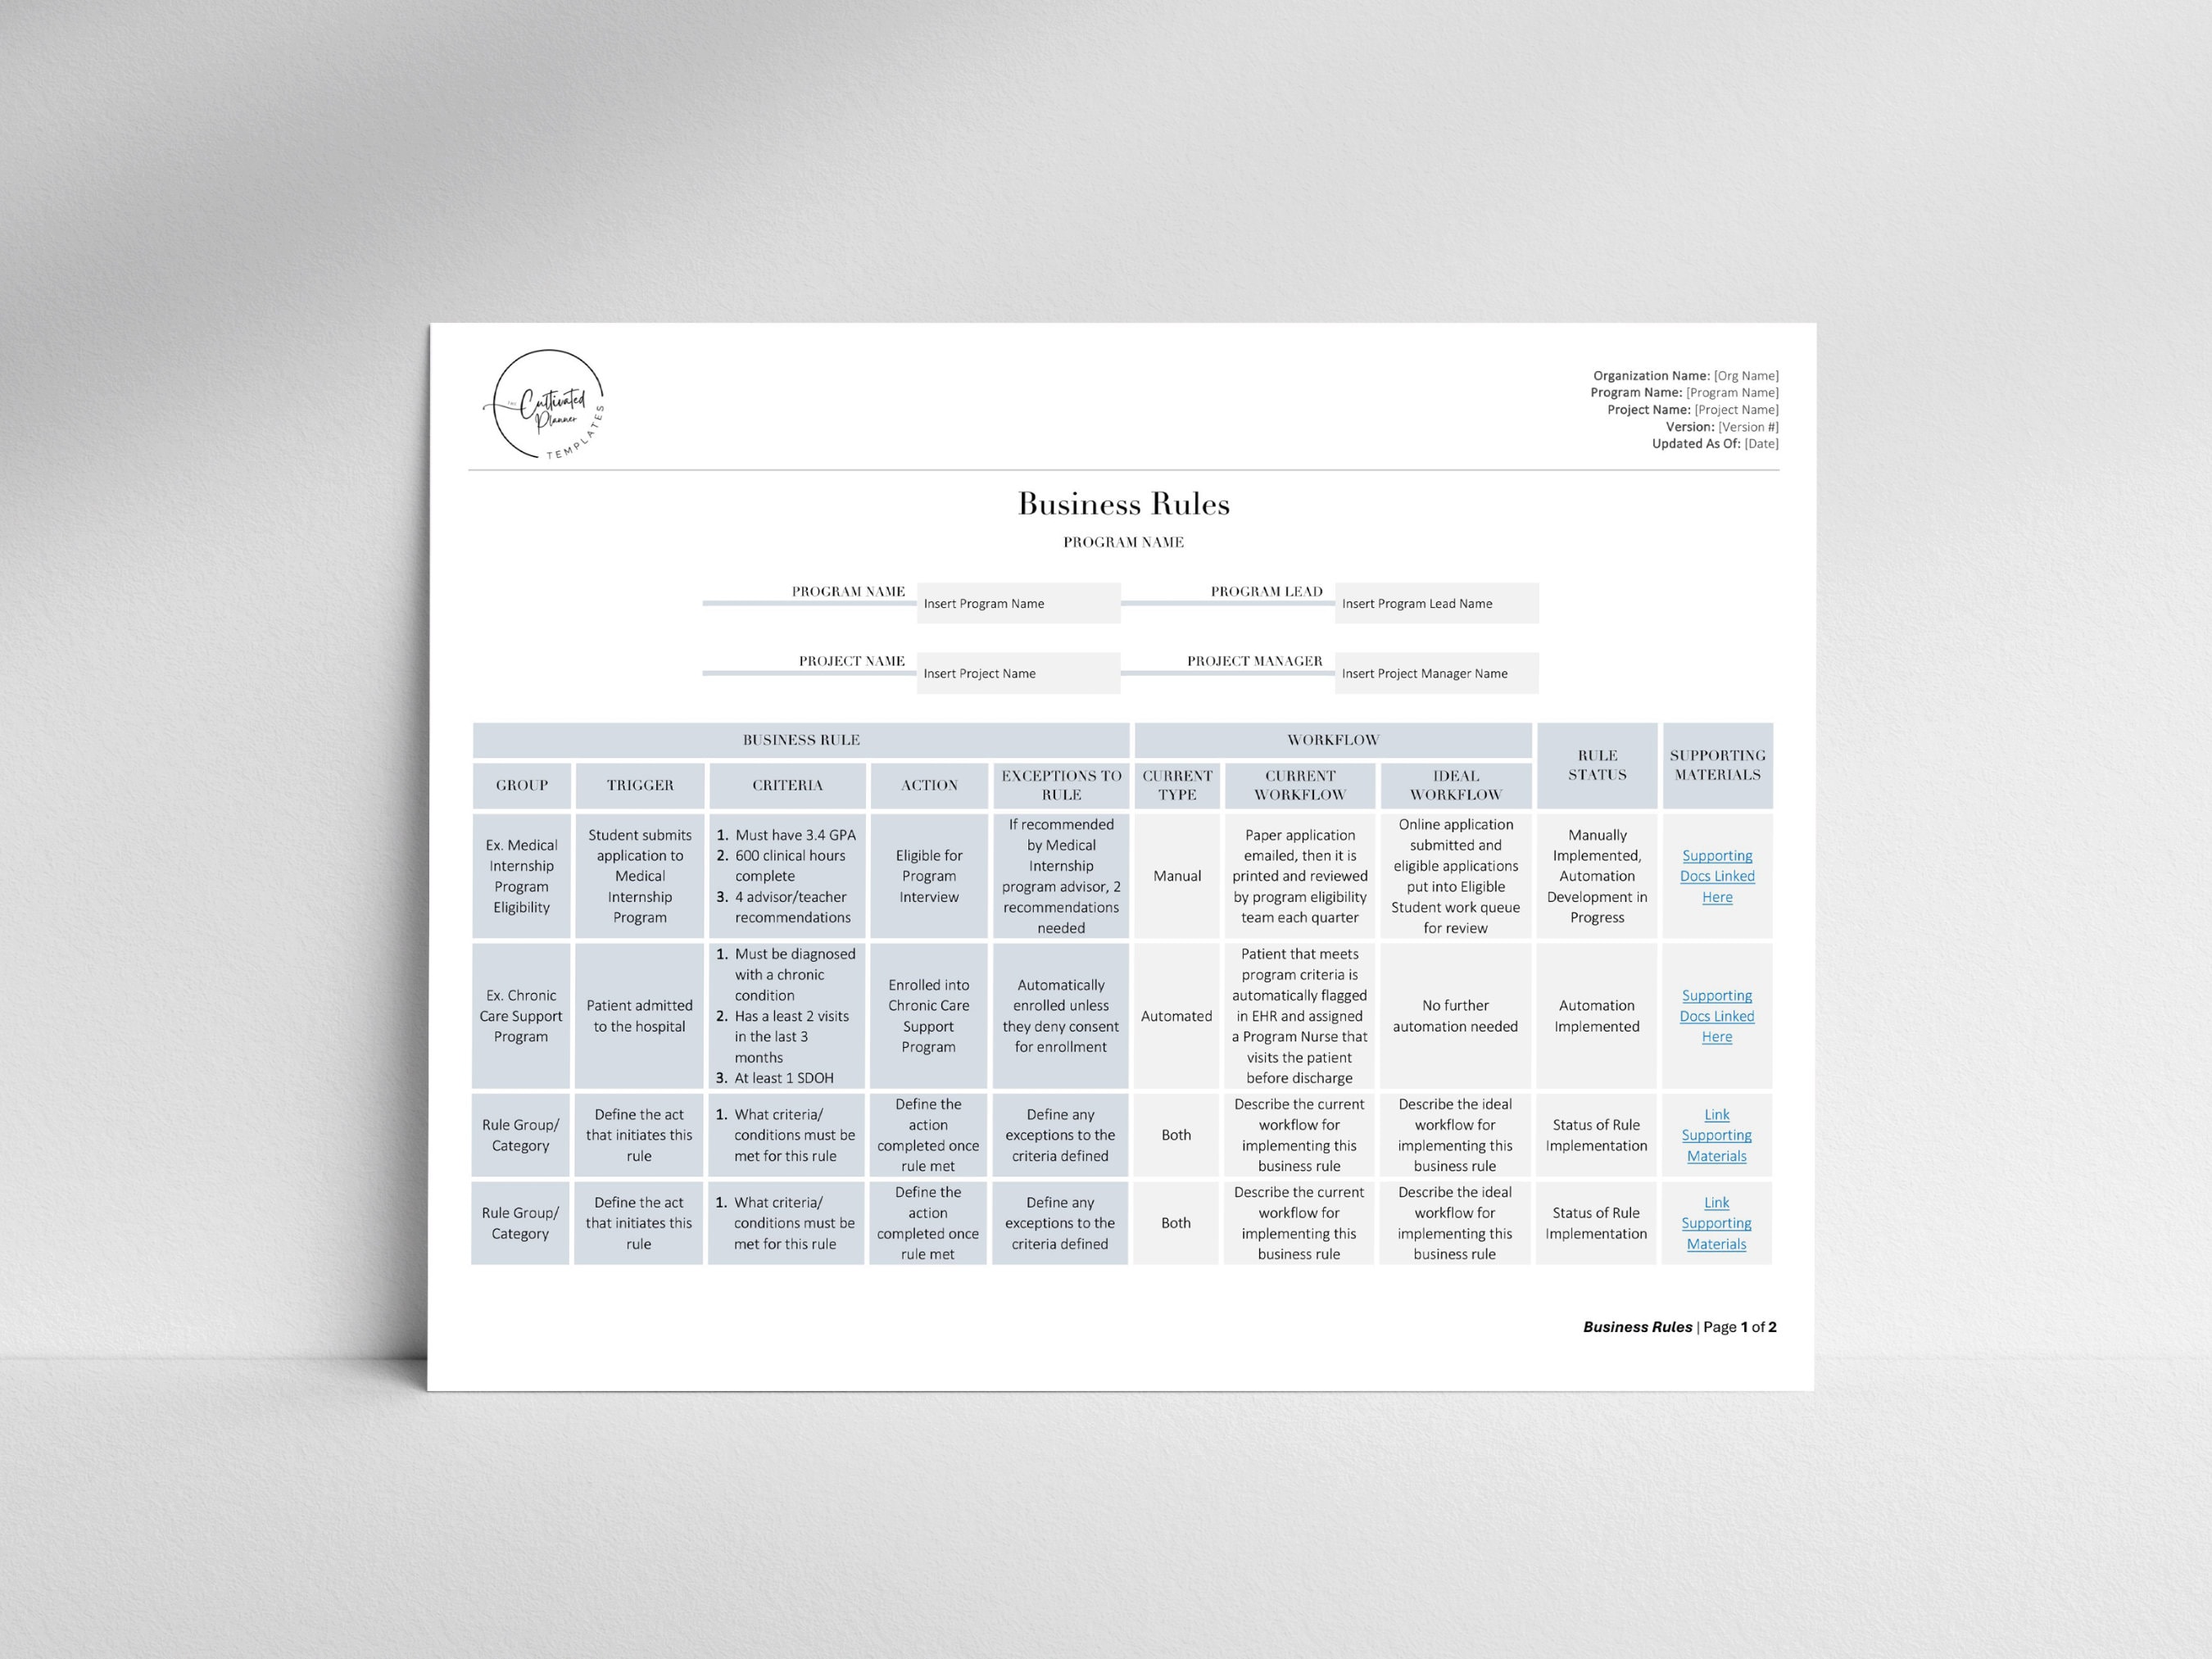
Rule identifier: A unique key, like DISC-0047. Don't skip this. Without an identifier, you'll lose track of which version is live, which one was deprecated, and which one someone forked into their own system three months ago. Statement: The plain language version. One sentence, maximum two. Conditions: The inputs the rule evaluates. Each condition should be independently testable. Avoid compound conditions that can't be unit-tested.
Get the Full Details
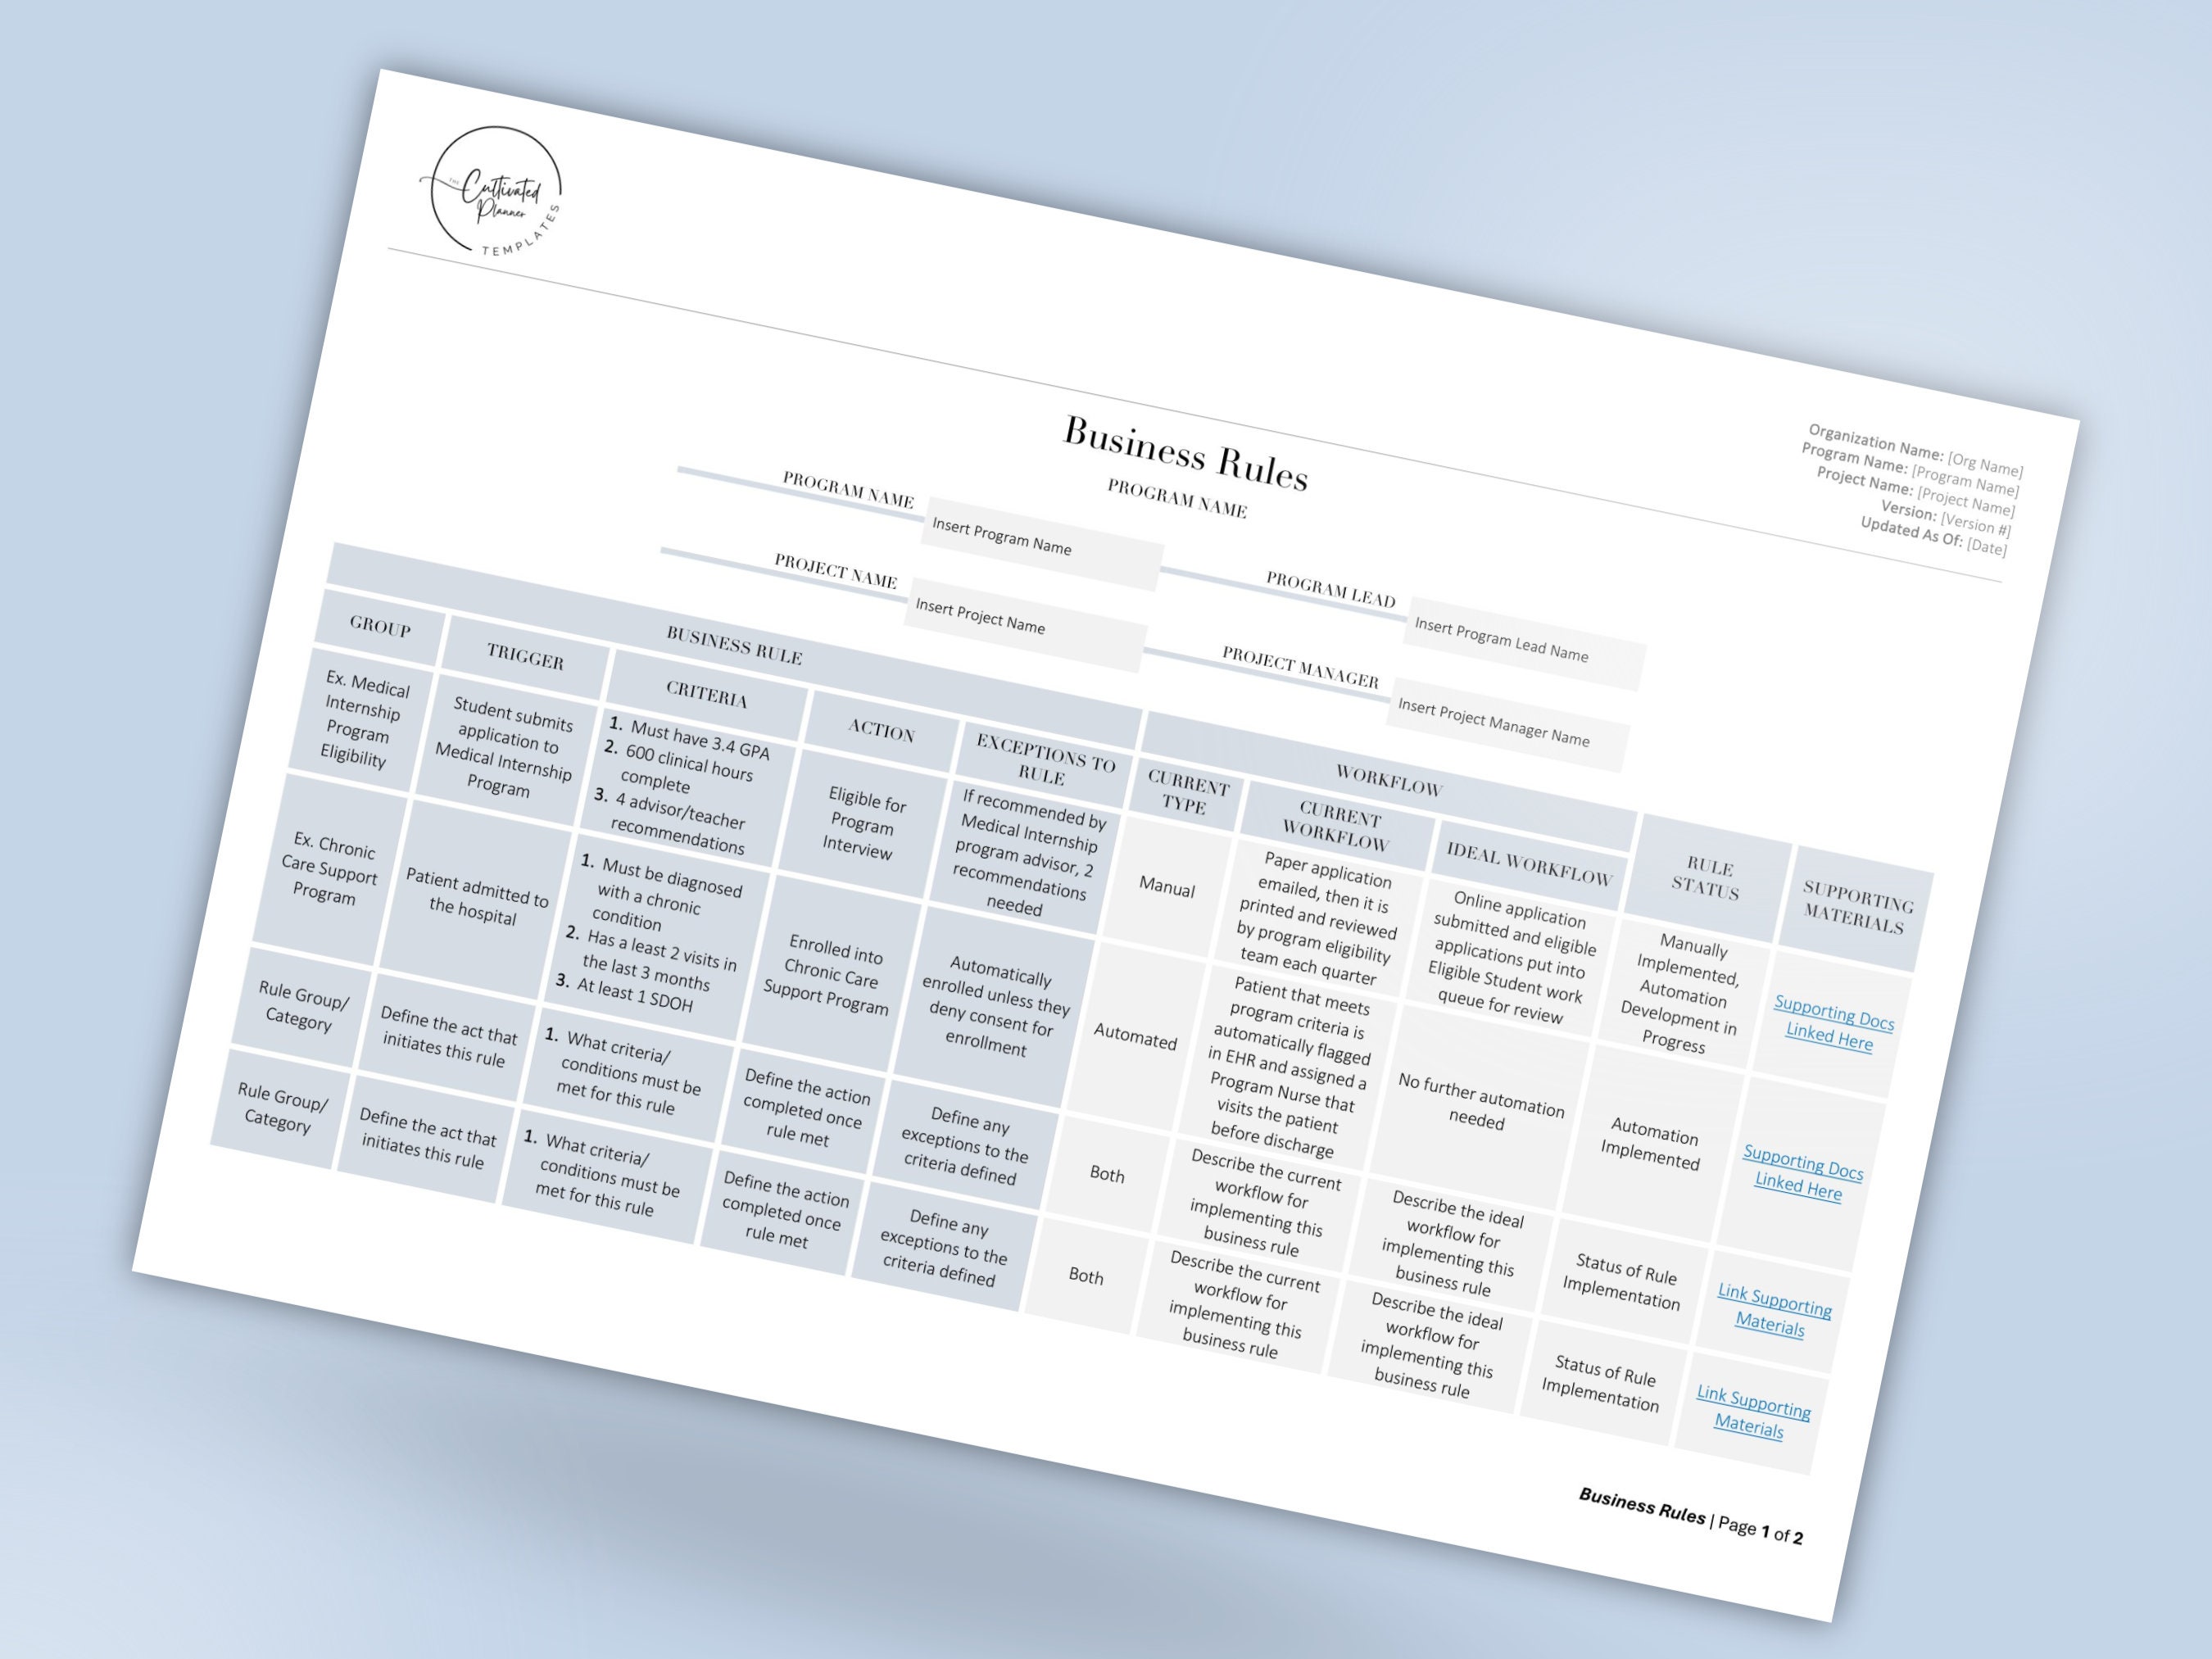
Outcome: What changes when the conditions are met. This could be a data modification, a notification, a workflow transition, or a rejection. Priority: When multiple rules can fire on the same event, which one takes precedence. This is the part almost nobody documents but it's the thing that causes the most bugs in production. Exception handling: What happens when the rule can't be evaluated. A missing field, a null value, a data type mismatch.
One counter-intuitive thing about writing business rules is that simpler often means more rules. You'd think you'd want one big complex rule that handles everything, but in practice a single rule trying to cover multiple scenarios becomes impossible to test and nearly impossible to debug. When a rule fails in production, you need to know exactly which part of it failed. If it's a monolithic decision tree with 40 branches, you're flying blind. Splitting it into smaller focused rules gives you observability and makes it easier to update one rule without accidentally breaking another. Another thing people miss is that not every requirement is a business rule. A user story about a dashboard feature isn't a rule. A reporting format isn't a rule. A business rule has to be something that can be evaluated as true or false given a set of inputs and produces a deterministic outcome. If you can't write a test for it, it probably isn't a rule. I've seen teams document things like "the checkout page should be intuitive" as rules. That's a design goal, not a rule. You can't execute that in a system. There's also the question of where rules live. Some organizations put them in a dedicated rules engine like Drools or BRMS. Others keep them in code. Some in configuration files. If your rules change daily, a rules engine gives you the flexibility to update without deploying. But rules engines add complexity. They require a separate deployment cycle, different testing strategies, and often a specialized skill set. For most small to mid-size applications, keeping rules in the codebase with good documentation is faster and cheaper. The trade-off is that changing a rule requires a code deploy and review, which takes longer but also gives you version control and auditability.
A common pitfall is treating rules as permanent. I worked on a project where we had a rule that had been in production for four years, but it was originally written for a different regulatory environment and the business had moved on. Nobody had reviewed the rule in years. It was still being enforced and it was silently blocking legitimate transactions. The business didn't know because the rule was buried in documentation that wasn't linked from anywhere obvious. Make it a practice to set review dates on every rule. Six months for high-frequency rules, a year for low-frequency ones. An expired review date is a signal that someone needs to re-evaluate whether the rule still matters. Another issue is rule collisions. When you have hundreds of rules across different domains, they can interact in ways you didn't anticipate. A pricing rule might conflict with a discount rule. A fraud check might override an approval workflow. I've seen systems where two teams wrote rules independently without knowing about each other, and the result was a transaction that got approved and rejected simultaneously depending on execution order. The solution is a central registry and a collision matrix. When you write a new rule, you explicitly declare which other rules it might conflict with and what the resolution strategy is. This takes extra time upfront but it saves serious debugging time later. The tooling you use matters less than the discipline you apply. You can write great rules in Confluence, Google Docs, or a spreadsheet. What matters is that every rule has a unique identifier, a clear statement, testable conditions, a documented exception path, and a review date. Without those four things, you're not writing rules, you're writing hopes.