Getting Started With the IBM Proventia Manual
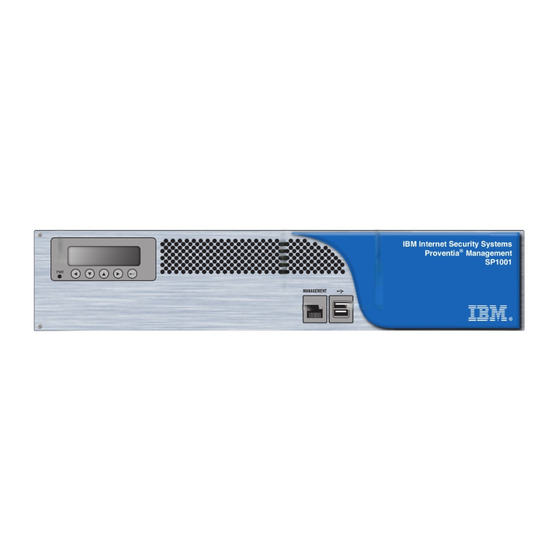
Most people looking for the Ibm Proventia Manual are either deploying the system for the first time or troubleshooting an existing installation that stopped working after a patch. Both situations feel the same: you open the PDF, click on a section, and immediately hit a wall because the documentation assumes you already know how everything connects. That is just how it is. The manuals are thick, sometimes contradictory across versions, and not organized the way your brain works when something is on fire. IBM no longer hosts the Proventia manuals prominently on their current site since the product line was sunset years ago. The documents still exist on IBM's older archive pages, on third-party hardware documentation sites, and sometimes on the IBM Support portal if you have an active account. Start by searching the exact model number plus "configuration guide" rather than just the product name. You will get faster results because the generic search pulls up every manual from every Proventia product ever made, which is not helpful. I typically go to the IBM Archive or old support doc libraries and look for the specific product code printed on the device label. When you do find the manual, ignore the table of contents. The TOC is organized by topic, not by workflow. Instead, jump straight to the chapter titled "Initial Configuration" or "Getting Started" and work backward from there if you need deeper detail. That approach saves you maybe an hour of scrolling compared to reading cover to cover, which nobody actually does.
What the Manual Covers and What It Misses
The IBM Proventia Manual walks through hardware installation, network placement, SNMP configuration, policy definition, and integration with Tivoli Security Information and Event Management. It covers the core functionality well enough for a standard deployment. But it does not cover the things that actually break in production. I have seen configuration sections that assume you are using standard VLAN tagging, which meant nothing to me when my client had an exotic switched environment with 802.1ad stacking. The manual told me exactly nothing about that scenario. Another thing the manual leaves out entirely is how Proventia handles asymmetric routing. If your network design sends traffic in one direction through the sensor and back out through a different path, the inline prevention mode will silently drop connections without generating any useful alert about why. I spent about three days chasing this on a client network before I realized the issue. The workaround was switching that particular sensor to promiscuous detection mode and letting the existing firewall handle the blocking instead. It is not an ideal fix, but it stopped the packet loss. The manual never mentions this behavior in any section I read.
Common Pitfalls When Following the Manual
The first major pitfall is the default rule set. The manual shows you how to enable protection profiles, but it does not warn you that the default profiles are extremely aggressive in prevention mode. I have wiped production connectivity twice by following the guide verbatim on the first attempt. The safe approach is to load the profile in monitoring mode only, let it run for at least 48 hours, review the false positive log, and then switch to prevention. Do not skip that step. It will cost you more time upfront than the 15 minutes you save by going straight to prevention mode. The second pitfall is certificate management. The Proventia web interface uses self-signed certificates by default, and the manual explains how to replace them. What it does not explain is that after you import a new certificate, some browser sessions retain the old certificate hash in their TLS stack until they are fully closed and reopened. I walked into a meeting once where the CISO was trying to log in from three different machines and couldn't get past the certificate warning on two of them. Restarting the browser on those machines fixed it immediately. The manual treats certificate replacement as a simple swap operation. It is not.
Get the Full Details

Integration and Real-World Usage
If you are integrating Proventia with Tivoli or another SIEM, the manual provides the syslog format specifications and the SNMP trap definitions. Use those. They are accurate. But do not expect the documentation to walk you through log parsing rules or correlation logic for your specific environment. You will need to write your own parser scripts or configure your SIEM manually. I typically build a custom parser that extracts the signature ID and source IP from the syslog message and maps it to a severity rating based on my own organization's risk framework. The default logs dump everything with a generic severity level that is useless for filtering. One thing most people miss: the Proventia web console supports batch policy deployment. The manual describes individual device management in detail but barely mentions the batch feature. If you are managing more than five sensors, learning the batch operations saves significant time. I cut my typical deployment cycle from about two hours per site to roughly twenty minutes by using batch scripts instead of clicking through the web interface device by device. The learning curve is steep because the documentation for batch operations is thin, but the payoff is real.
Limitations You Should Know About
Proventia is discontinued. IBM has moved users toward QRadar and other newer platforms. The manual itself will not tell you this, but it is important context. Hardware support, firmware updates, and signature database downloads have all been retired. If you are working with legacy infrastructure that still runs Proventia, you are operating on borrowed time. The manuals are technically accurate for the versions they cover, but they cannot help you with problems that arise from running deprecated software on modern networks. Threat signatures from 2024 and later simply do not exist for this product line. If your organization is still relying on Proventia for active protection, the honest recommendation is to begin a migration plan. Use the manual to keep the existing system stable in the interim, but do not invest time in learning advanced features that will not matter once the product is fully retired. Focus on baseline configuration, reliable monitoring, and documenting whatever custom workarounds you develop while the system is still running. Those workarounds become part of your institutional knowledge and may inform how you design the replacement system.