Most Risk Registers Are Useless Decoration
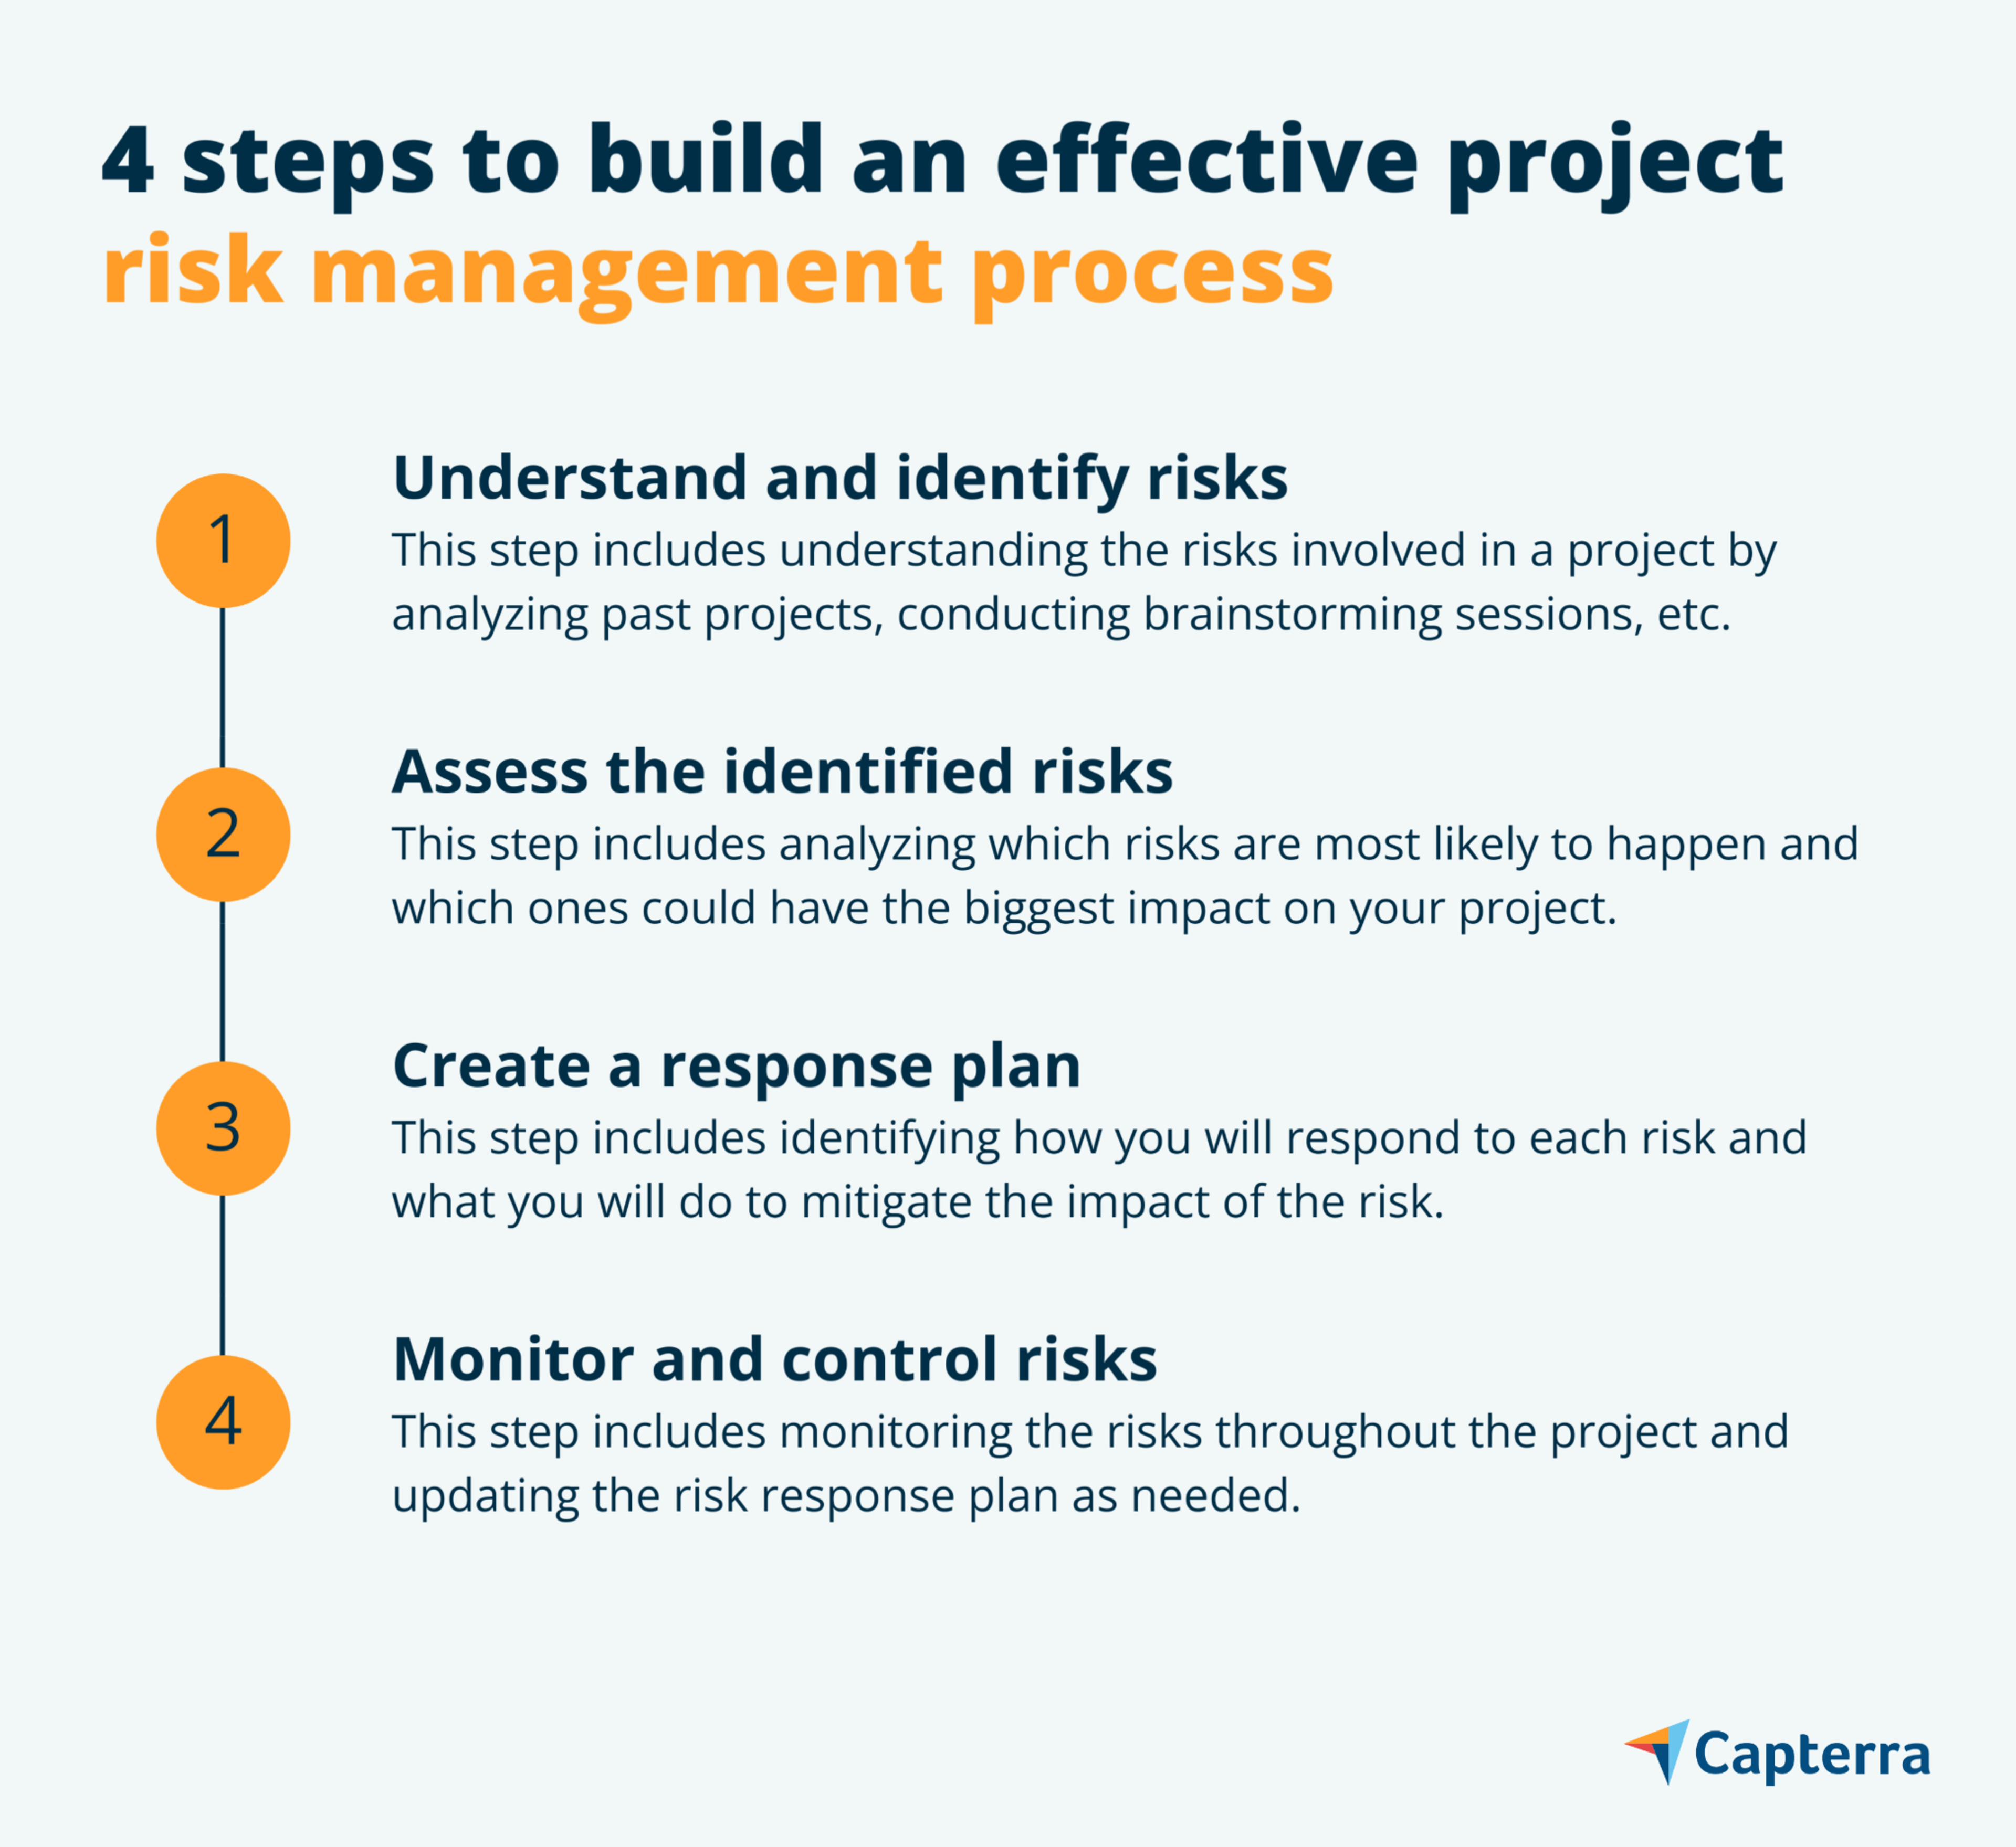
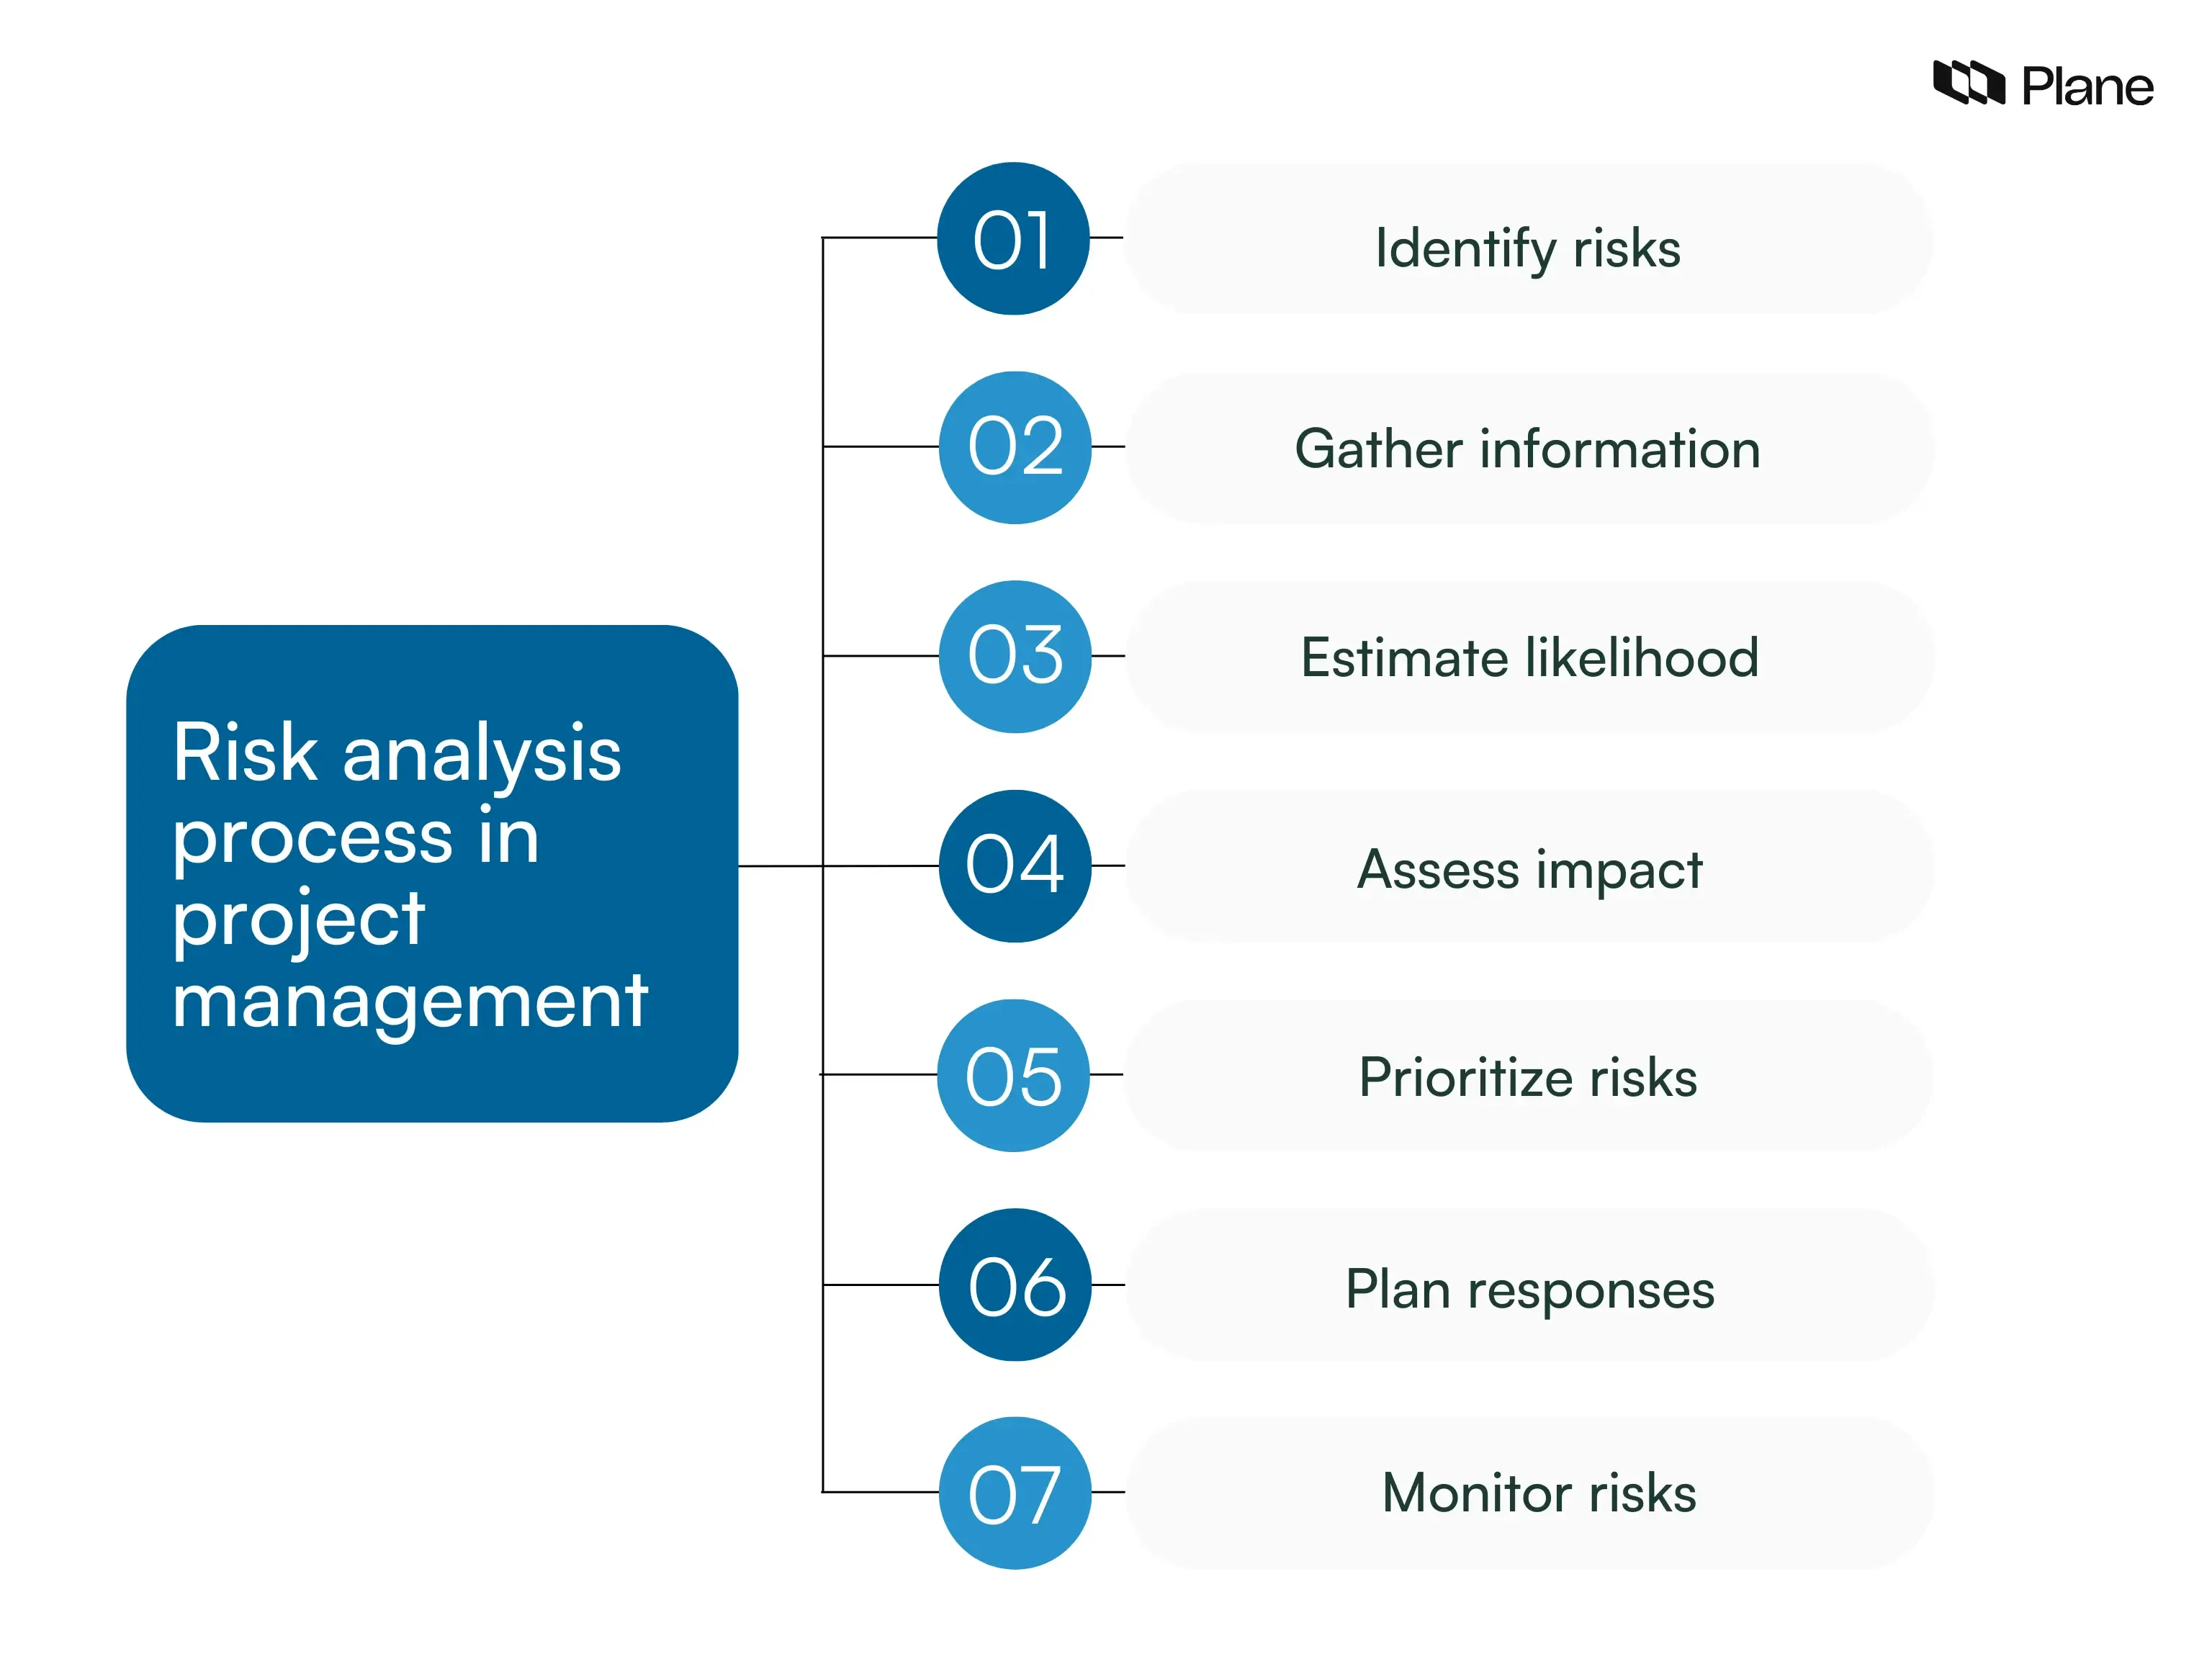
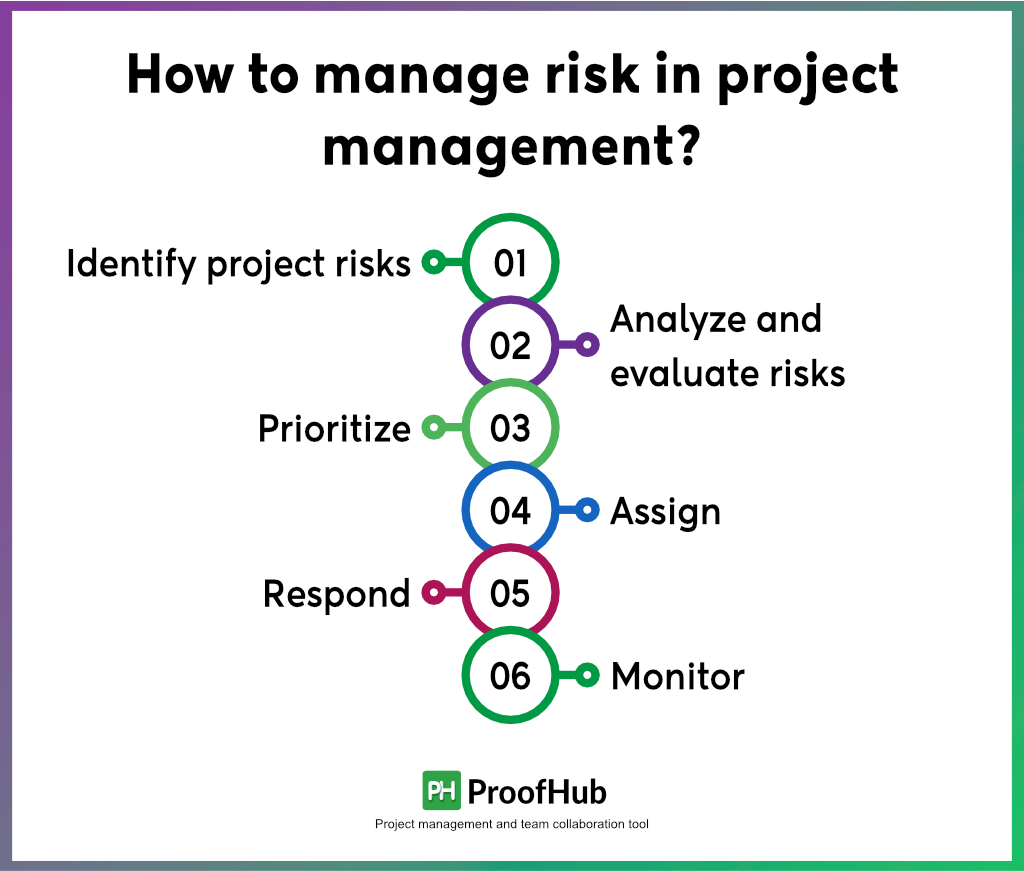
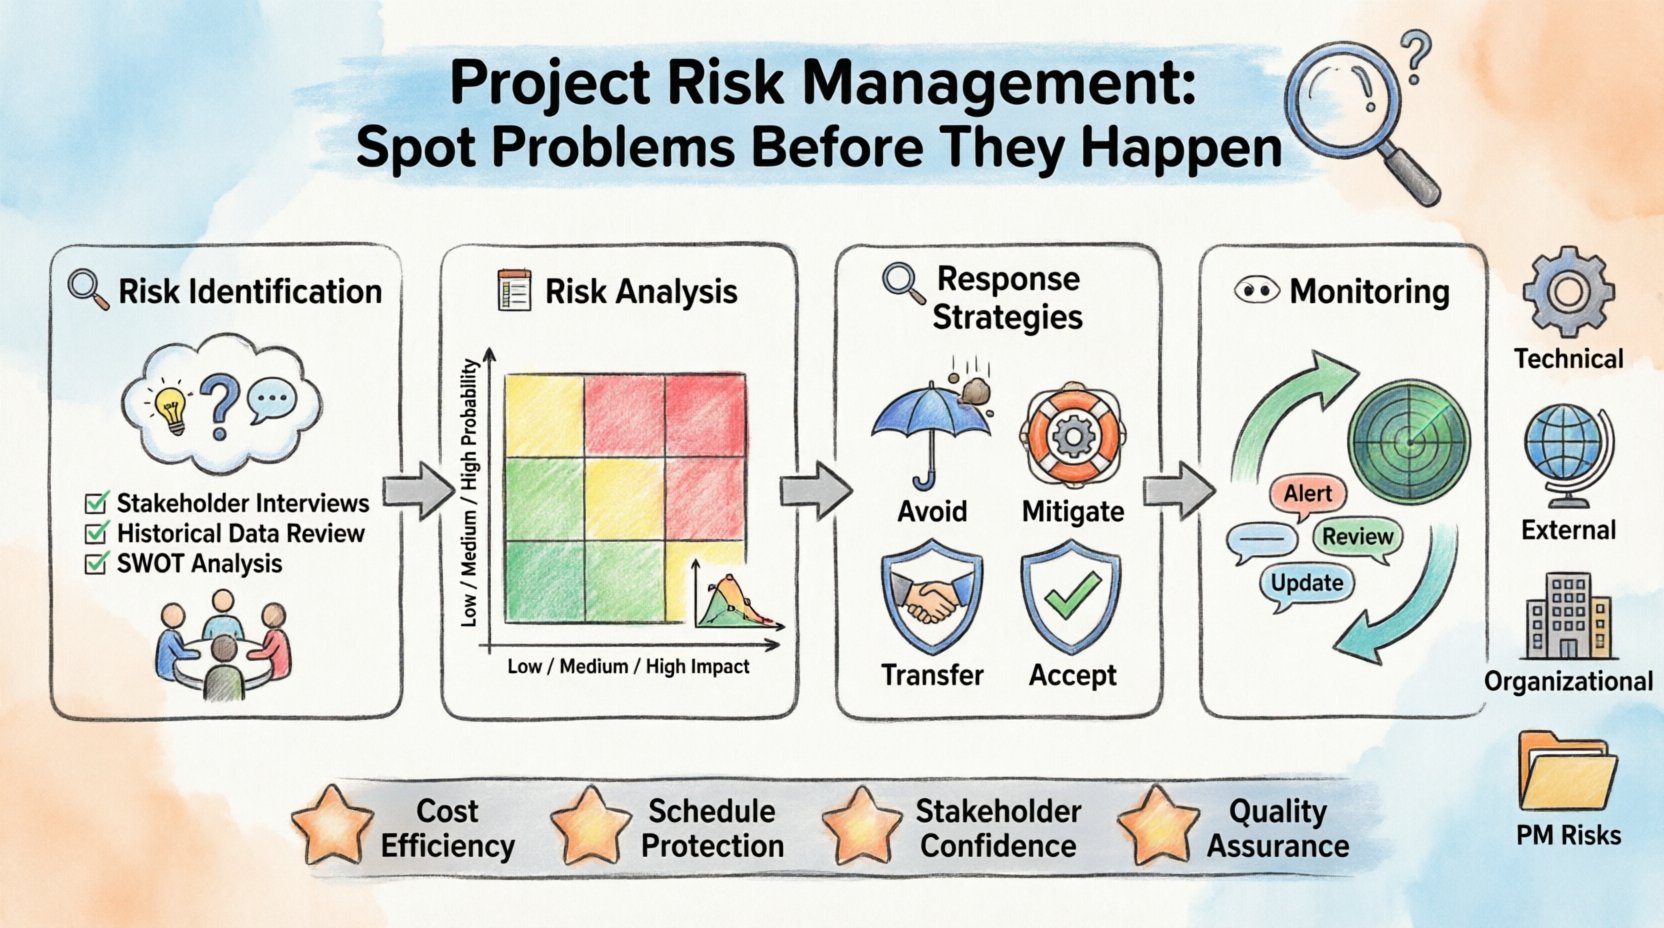
I've seen it hundreds of times. A project kicks off, someone fills out a twelve-page risk register with beautifully typed entries like "key team member may leave" or "vendor delivery could slip," assigns them probability scores, and then nobody looks at it again until something goes wrong. Then everyone acts surprised. Identifying And Managing Project Risk isn't really about documentation. It's about the uncomfortable conversations you have before you know whether a problem is real or just noise. Start with a pre-mortem, not a brainstorm. I don't mean the standard workshop where people politely name generic threats. I mean sitting down with the team and asking them to write the project's failure story as if it already happened. "It's six months out. The project failed. Here's exactly how." That exercise forces people past surface-level concerns and into the specific mechanics of how things actually break. You'll get answers like "the API integration we assumed was simple turns out to require a database migration the vendor won't support" instead of "integration risks." Those are the entries worth capturing. Once you have the list, score each risk on two axes only: impact and likelihood. Skip the other fancy scoring matrices. The multiplicative models create a false sense of precision. A risk rated "7 out of 10 severity" based on some weighted formula involving stakeholder influence and temporal proximity is just opinion dressed in math. Pick a simple 1-to-5 scale for both. Multiply them. Rank. Move on.
For every risk above a threshold score, define a mitigation and an fallback. Mitigation is what you do to reduce probability or impact. Fallback is what you do when the mitigation itself fails. Too many plans only have one of these. They have a mitigation and no fallback, which means when the mitigation breaks — and it usually does — you're suddenly unprepared for a second-order problem. I once worked on a healthcare data migration where the primary risk was the source system's export format changing mid-project. We built a mitigation: a dedicated engineer who would maintain the parsing logic and update it whenever a schema drift occurred. The fallback was supposed to be "manual data mapping by the analytics team." What we didn't account for was that the analytics team was fully committed to a separate reporting deliverable with a hard deadline. When the source system did change — and it did, in week fourteen — our fallback was fictional. The workaround was that I pulled two contractors from a non-critical path for a five-day sprint, burned through budget contingency, and got the migration done. After that, I made it a rule: every fallback plan must have a named person and a confirmed time commitment before the risk is ever considered "managed."
Common Mistakes That Make Things Worse
The biggest one is treating risk identification as a one-time event. Risk registers are living documents. If yours hasn't been updated in three weeks, it's already stale. New risks emerge from dependencies, from decisions made in other workstreams, from the actual work revealing assumptions that were wrong. I set a recurring fifteen-minute slot in our sprint planning where someone goes through the top five risks and updates their status. Not the whole register. Just the top five. That keeps the signal visible without turning it into administrative overhead. Another mistake is confusing risk with issue. A risk is something that might happen. An issue is something that has happened. When a risk materializes, it stops being a risk and becomes an issue, and it should be moved immediately into your issue tracker with a clear handoff. Keeping it in the risk register after it's happened just creates confusion about who owns it and what the current state actually is. There's also the trap of over-mitigating low-probability risks while neglecting the moderate-probability ones that are actually likely to bite you. I once watched a project spend three weeks building elaborate monitoring and alerting for a risk that had a 5% chance of occurring, while a separate risk with a 60% chance — based on known vendor instability — sat in the register with a single bullet point saying "monitor closely." That's not risk management. That's anxiety management.
Get the Full Details

When This Approach Breaks Down
The method I described works well for medium-complexity projects with identifiable stakeholders and predictable timelines. It breaks down in environments where the scope is genuinely unknown — research initiatives, product discovery phases, anything where the problem itself isn't well defined yet. In those cases, the pre-mortem exercise produces either nonsense or fiction because people literally can't imagine what could go wrong when they don't know what they're building. For those situations, shorter planning horizons with frequent checkpoint reviews are more effective than any risk register. You manage uncertainty by reducing the distance between decision and feedback, not by predicting the unpredictable. Quantitative risk analysis using Monte Carlo simulation sounds rigorous but requires input data quality that most teams simply don't have. Feeding a simulation with estimated ranges that are guesses dressed as data gives you a false precision output that looks scientific but is garbage. Use it only when you have actual historical data to calibrate against. Otherwise, stick to qualitative scoring and explicit assumptions documentation. The bottom line is that identifying and managing project risk well mostly comes down to discipline. Keep the register small and current. Name the people responsible for fallback plans. Update scores when conditions change. And don't confuse a thorough-looking document with actual risk reduction. The projects that survive aren't the ones with the best risk registers. They're the ones where someone noticed the warning signs early enough to actually do something about them.