Setting Up Proper Segmentation Between Your Public and Private Networks
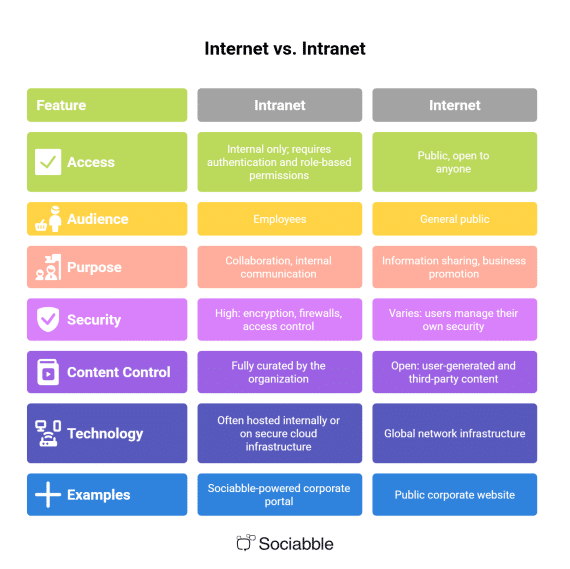
The first thing most organizations get wrong is assuming that a firewall alone constitutes a security perimeter. It doesn't. The real work starts with understanding how traffic actually moves between your external-facing infrastructure and your internal systems. I spent three weeks last year dismantling a configuration where a junior admin had opened a port range on a DMZ firewall to "help with remote access testing," which effectively turned the intranet into a public resource. You'd be surprised how often that happens. At its core, Internet security deals with protecting data and systems exposed to the broader network, while intranet security focuses on controlling access within an organization's private infrastructure. The tricky part is the boundary between them. That transition zone — the DMZ, the edge gateway, the point where internal DNS hands off to external resolvers — is where most breaches actually originate. It's not the flashy ransomware headline. It's usually a misconfigured reverse proxy or an expired certificate that someone ignored for six months. The practical method I use starts with a full inventory of every network segment, every open port, and every service that touches both the internet-facing side and the internal side. I map it all out on paper before touching a single configuration file. This process typically takes a small team about two days for a mid-size environment, but skipping it will cost you far more in incident response later. There is no shortcut here.
One counter-intuitive insight that took me years to accept: the more strictly you secure the external perimeter, the more attention you should pay to lateral movement inside the intranet. I once worked with a company that had a fortress-level perimeter defense and zero internal segmentation. Someone phished a developer, got onto a laptop, and moved laterally across the entire internal network in under forty minutes because there were no internal firewalls and all machines were in the same VLAN. The perimeter held perfectly. The inside was completely open. Implement micro-segmentation between departments even if your org chart suggests trust. Marketing doesn't need to reach the database server. The guest Wi-Fi should never see the VPN tunnel. Set up separate VLANs, apply ACLs between them, and verify the ACLs actually block traffic the way you expect them to. I use a simple approach: for every new VLAN pair, run a connection test from a compromised host and confirm the expected denial. If it passes when it shouldn't, the misconfiguration is your problem now instead of a hacker's opportunity later. Regarding tools, most environments run fine with pfSense, FortiGate, or a Cisco ASA on the perimeter, paired with something like Wazuh or a SIEM for internal monitoring. The specific tool matters less than consistent logging. I can't stress this enough — if you're not collecting logs from your edge firewall and your internal switches at the same granularity, you're flying blind during an incident. Expect to spend roughly four hours per week on log review and rule tuning. It's not glamorous, but it catches things like port scans from internal hosts that should never be making outbound connections.
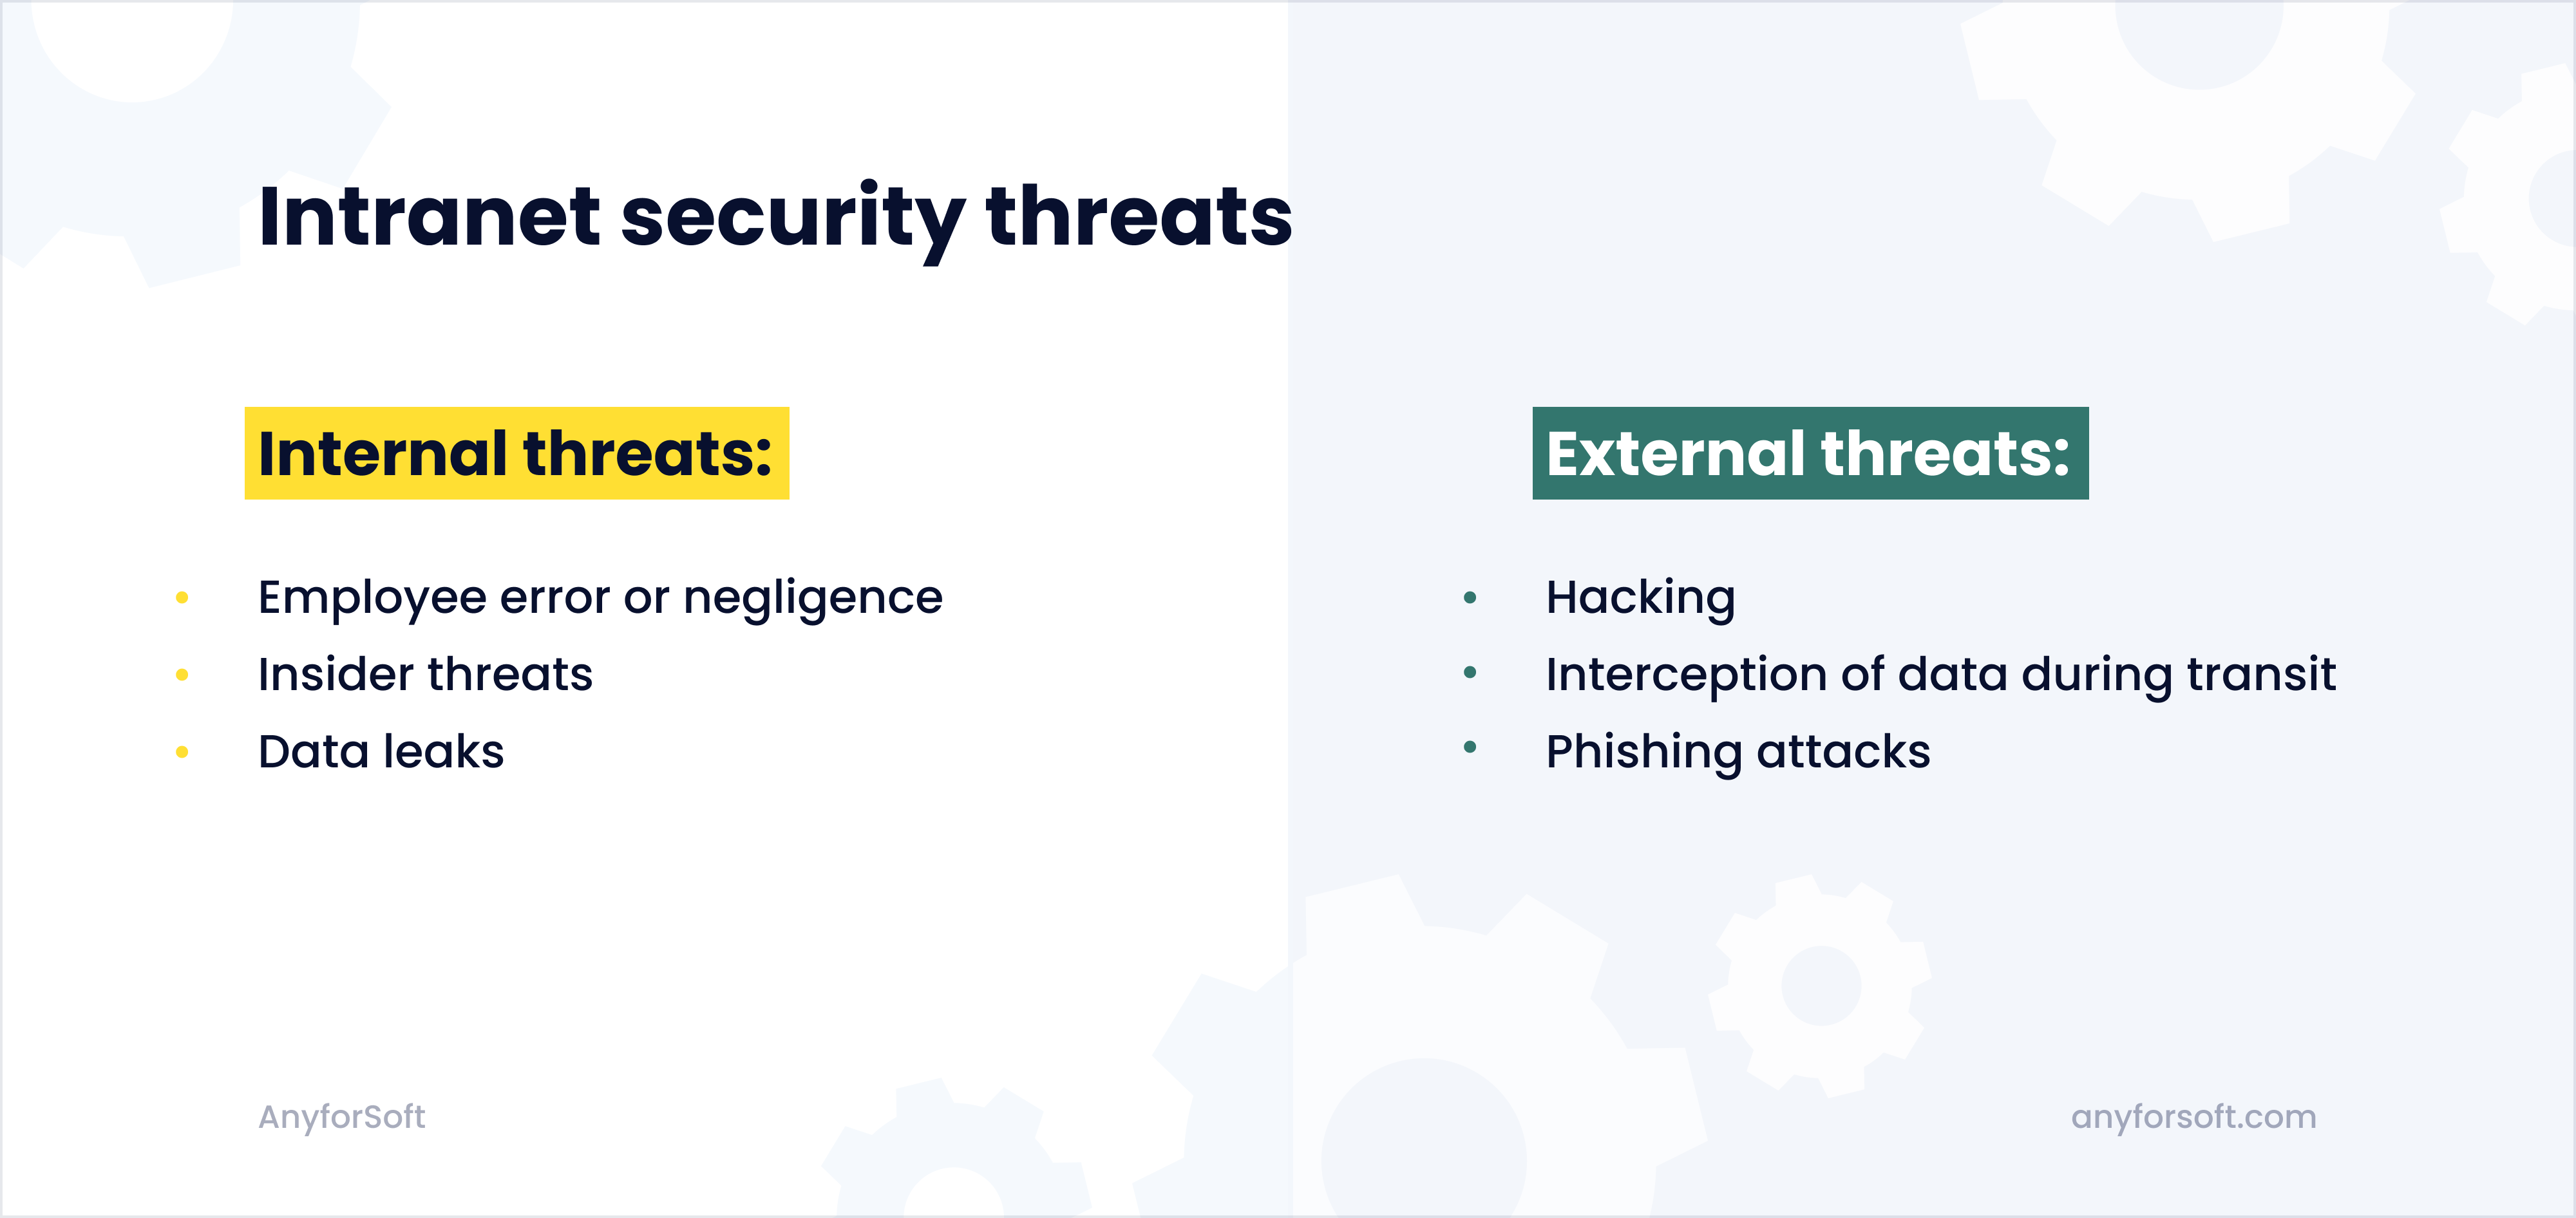
Another area people overlook is certificate management. An expired TLS certificate on an internal web app might not seem urgent until you realize it forces staff to use HTTPS workarounds or revert to unencrypted HTTP for internal services. I found a case once where the intranet's HR portal had been running on self-signed certificates for eight years because no one remembered who set it up. The workaround was to spin up a lightweight internal CA using a tool like MiniCA or step-ca, issue proper certificates to all internal services, and set up automatic renewal with a simple cron job or Ansible playbook. That cut our certificate-related outages from roughly one per quarter to zero over the next two years. Here's where things get bluntly honest about limitations: no amount of perimeter security stops a credentialed insider from causing damage, and it won't fully protect you from a sophisticated supply-chain compromise either. If someone has valid credentials and knows your network topology, they can move laterally regardless of how many firewalls sit between segments. The mitigation here is not a product you buy. It's continuous monitoring, least-privilege access policies, and regular credential rotation. I recommend reviewing user access rights quarterly at minimum, and immediately whenever someone changes departments or leaves the company. For remote access specifically, the old model of giving everyone a VPN account with broad intranet access is no longer defensible. I switched my last client to a zero-trust model where users authenticate through an identity provider and get application-level access only. It adds about ten minutes to the initial setup per user but reduces the blast radius of a compromised account from "entire network" to "the specific applications that person was authorized to use." The tooling stack for this typically involves something like OPA or a service mesh like Istio for policy enforcement, combined with a proper SSO solution.
Get the Full Details

If you're starting from scratch and want a baseline configuration, I've found that applying the CIS Benchmarks for your specific OS and firewall platform, then running a vulnerability scan with Nessus or OpenVAS to validate your work, gets you to a solid starting point in about a week for a small deployment. After that, it's maintenance. Schedule monthly patch windows, quarterly access reviews, and annual penetration tests. The annual pentest is non-negotiable. It will find things your own team misses, and that's exactly why it exists. One final thing worth mentioning: documenting everything you do. I keep a running network diagram in draw.io and update it whenever anything changes. When an incident hits at 2 AM and you need to know which VLAN a server belongs to, having an accurate diagram saves you thirty minutes of panic instead of thirty seconds of looking.