Why Your Security Setup Keeps Failing
Most people treat internet security like a product you buy, not a process you maintain. You install something, click "enable," and assume you are safe. That approach works until it doesn't, and by then the damage is already done. I have spent years dealing with security incidents and preventing them, and the pattern is always the same: people ignore the boring parts until a breach forces them to pay attention. The real issue isn't that security tools don't work. It's that people deploy them wrong. A firewall without logging is just decoration. Antivirus without endpoint detection and response leaves massive blind spots. Password managers are useless if you reuse the same master password across three different services. The problems compound because nobody checks any of this regularly.
Understanding Internet Security Issues And Solutions
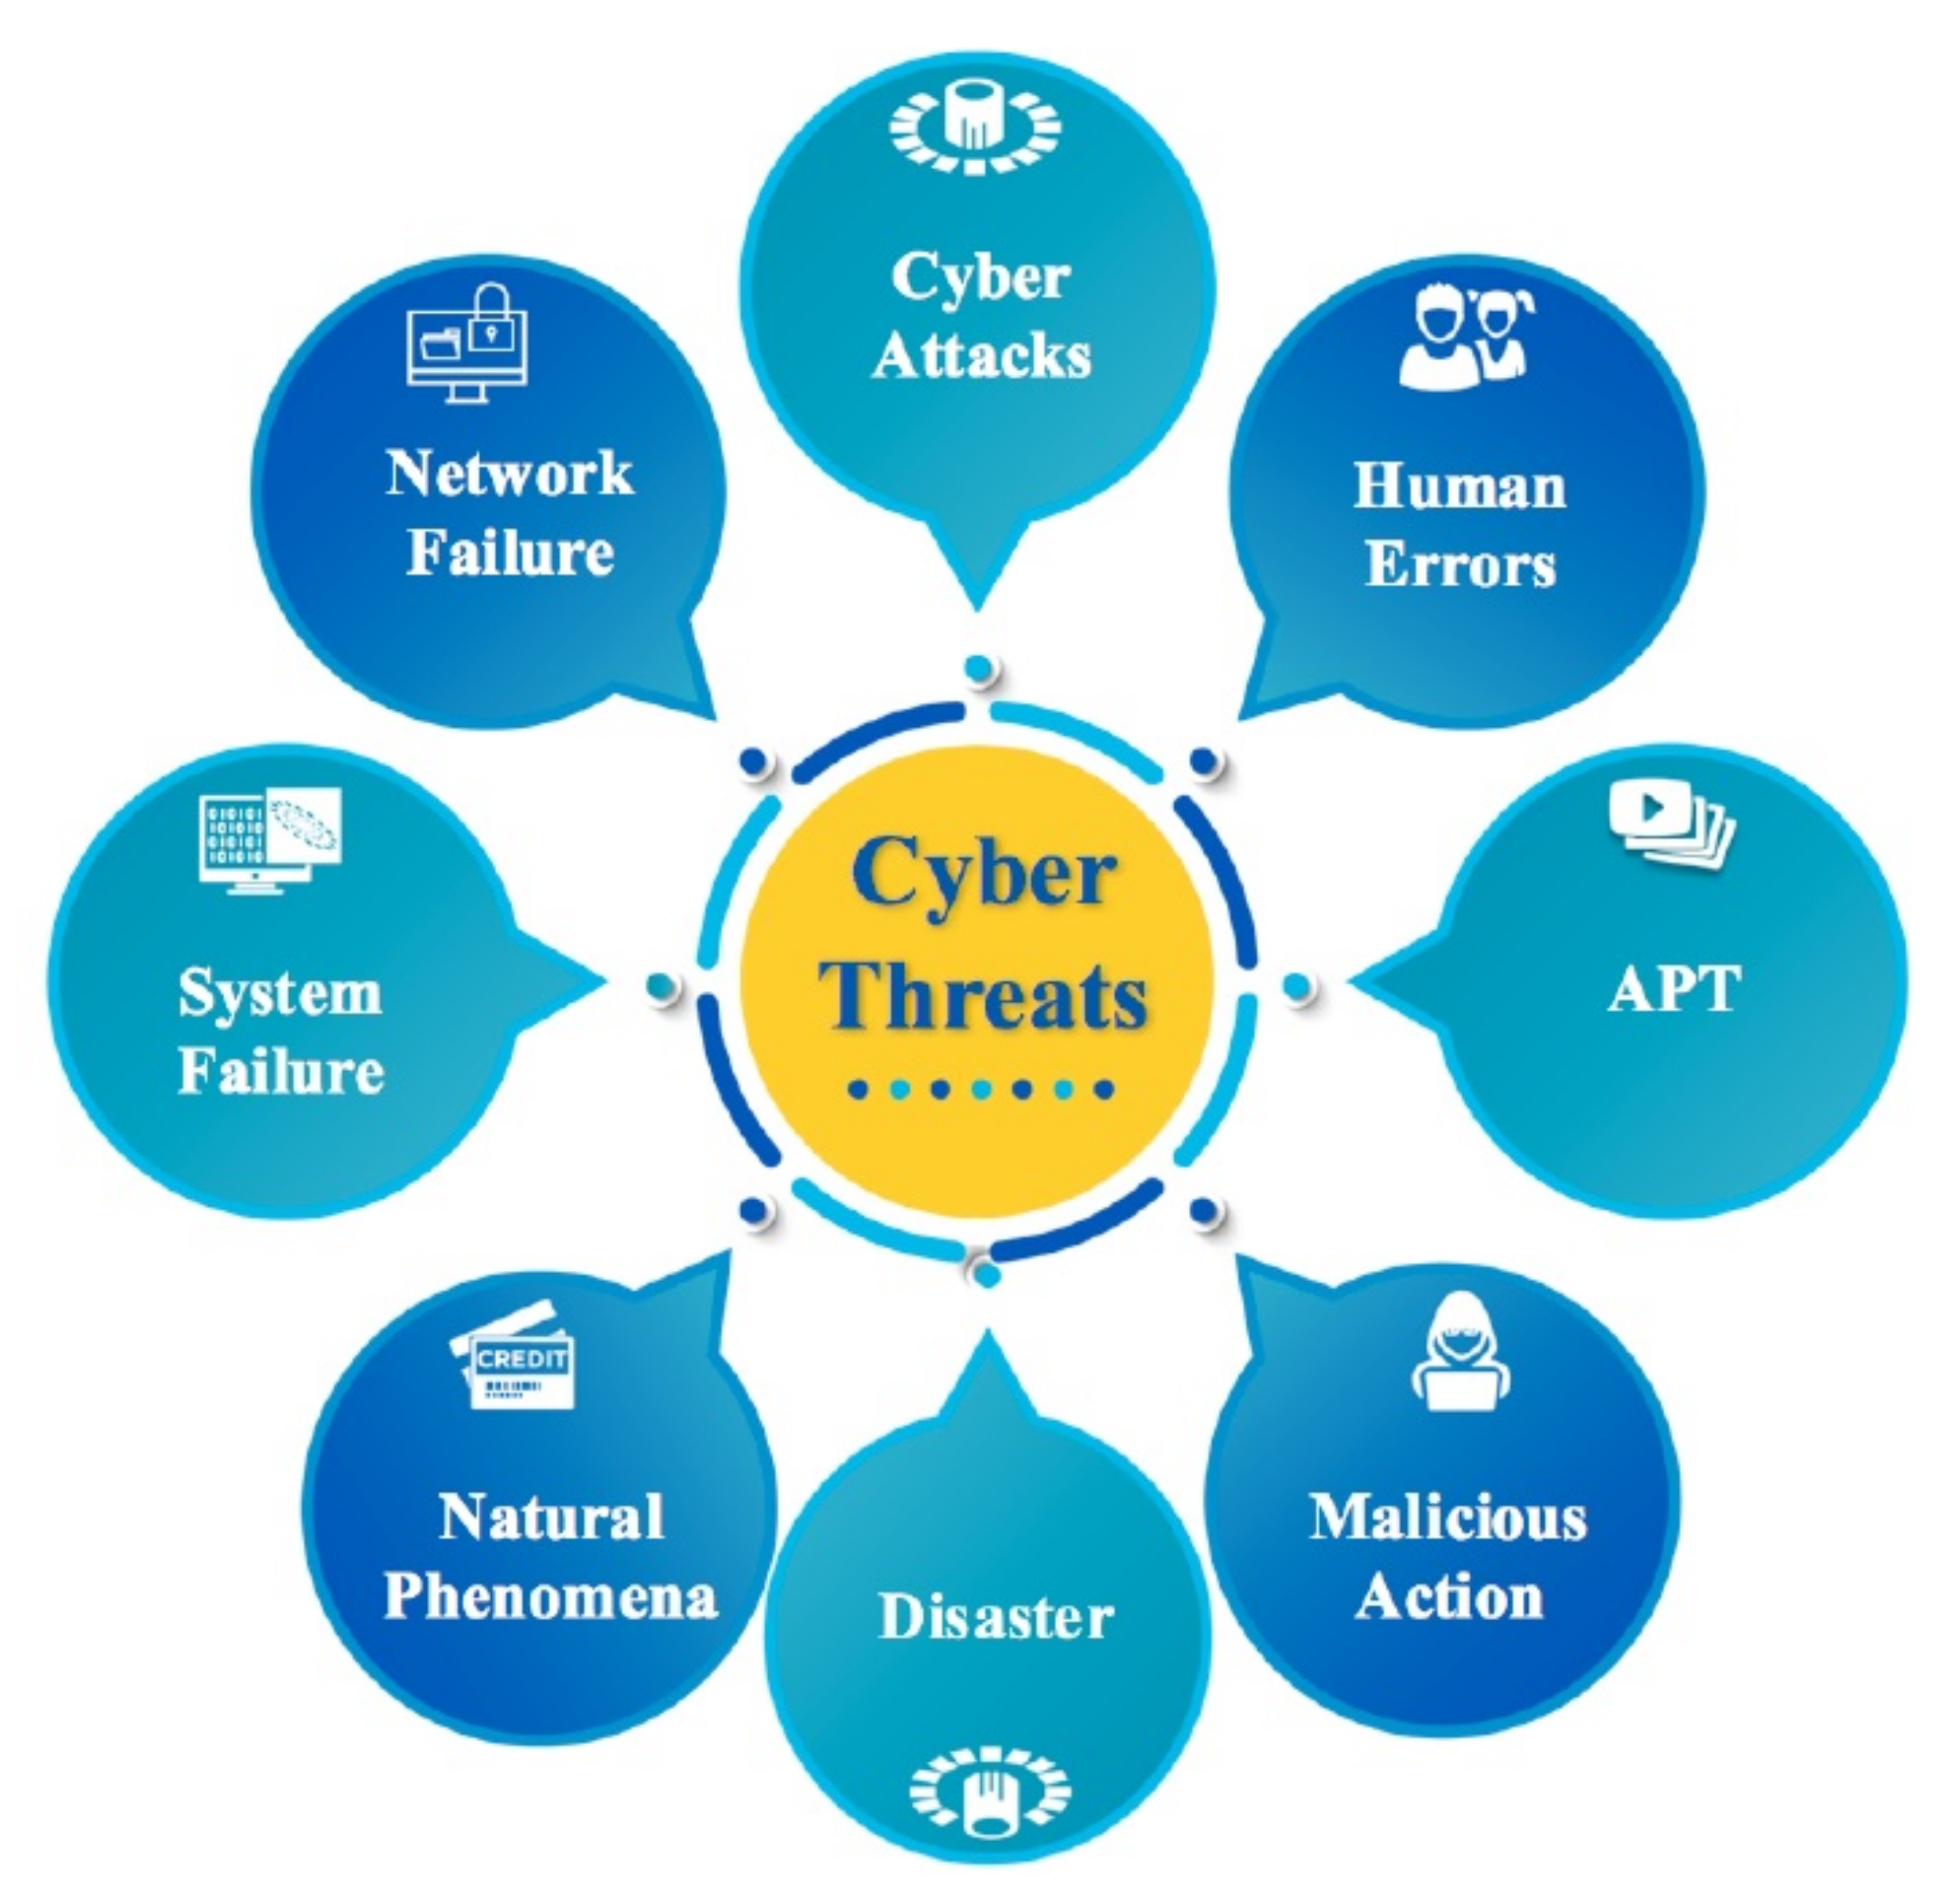
Let me be clear about what actually causes breaches and what fixes them. The top issues aren't complicated. They are phishing, unpatched software, weak authentication, misconfigured cloud storage, and insider mistakes. Each one has a known solution, but the solutions require work. There is no single tool that solves all of these. Anyone telling you otherwise is selling something. Phishing remains the #1 initial access vector. The solutions are layered: email filtering with DMARC, DKIM, and SPF enforced across every domain; browser-based phishing protection; and mandatory security awareness training that includes simulated phishing campaigns. The training part matters more than people realize. Simple one-hour annual compliance videos don't change behavior. Quarterly micro-training sessions with immediate feedback on simulated phishing results show measurable improvement in click rates within three months. Unpatched software is the second biggest issue. This includes operating systems, browsers, plugins, and especially third-party applications running on your network. The solution is automated patch management. Windows Update for Business can handle endpoints. For servers, configuration management tools like Ansible or Puppet enforce patch compliance. The catch is that patching breaks things occasionally, so you need a testing window before deployment to production. I usually recommend staging patches on a parallel environment for at least 48 hours before rolling them out globally.
Misconfigured cloud storage accounts cause data leaks at scale. S3 buckets left public, Azure blob containers with anonymous read access, and Google Cloud storage with wildcard permissions are routine findings during security audits. The fix starts with a cloud security posture management tool, but the real work is establishing a policy that requires all new storage to be private by default. I once inherited an environment where someone had created over 200 S3 buckets with inconsistent naming conventions and zero access policies. It took three days just to inventory what existed before we could begin securing it. That is the problem with reactive security: you are always behind.
Get the Full Details
What Actually Works In Practice
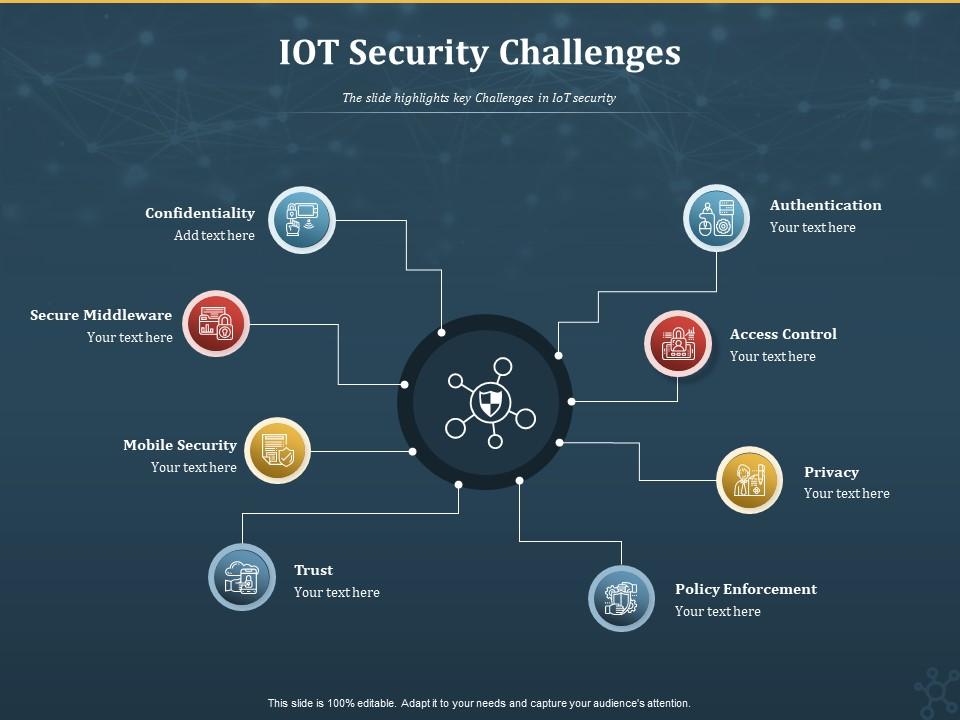
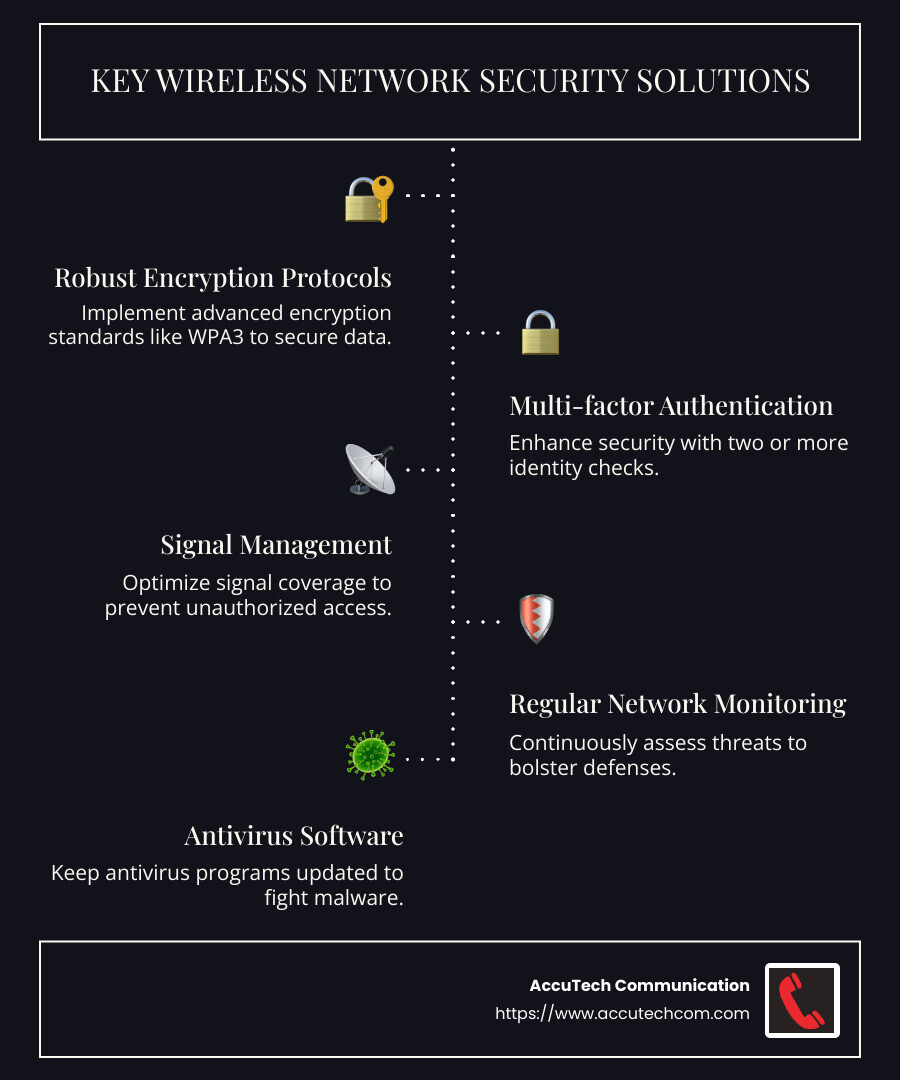
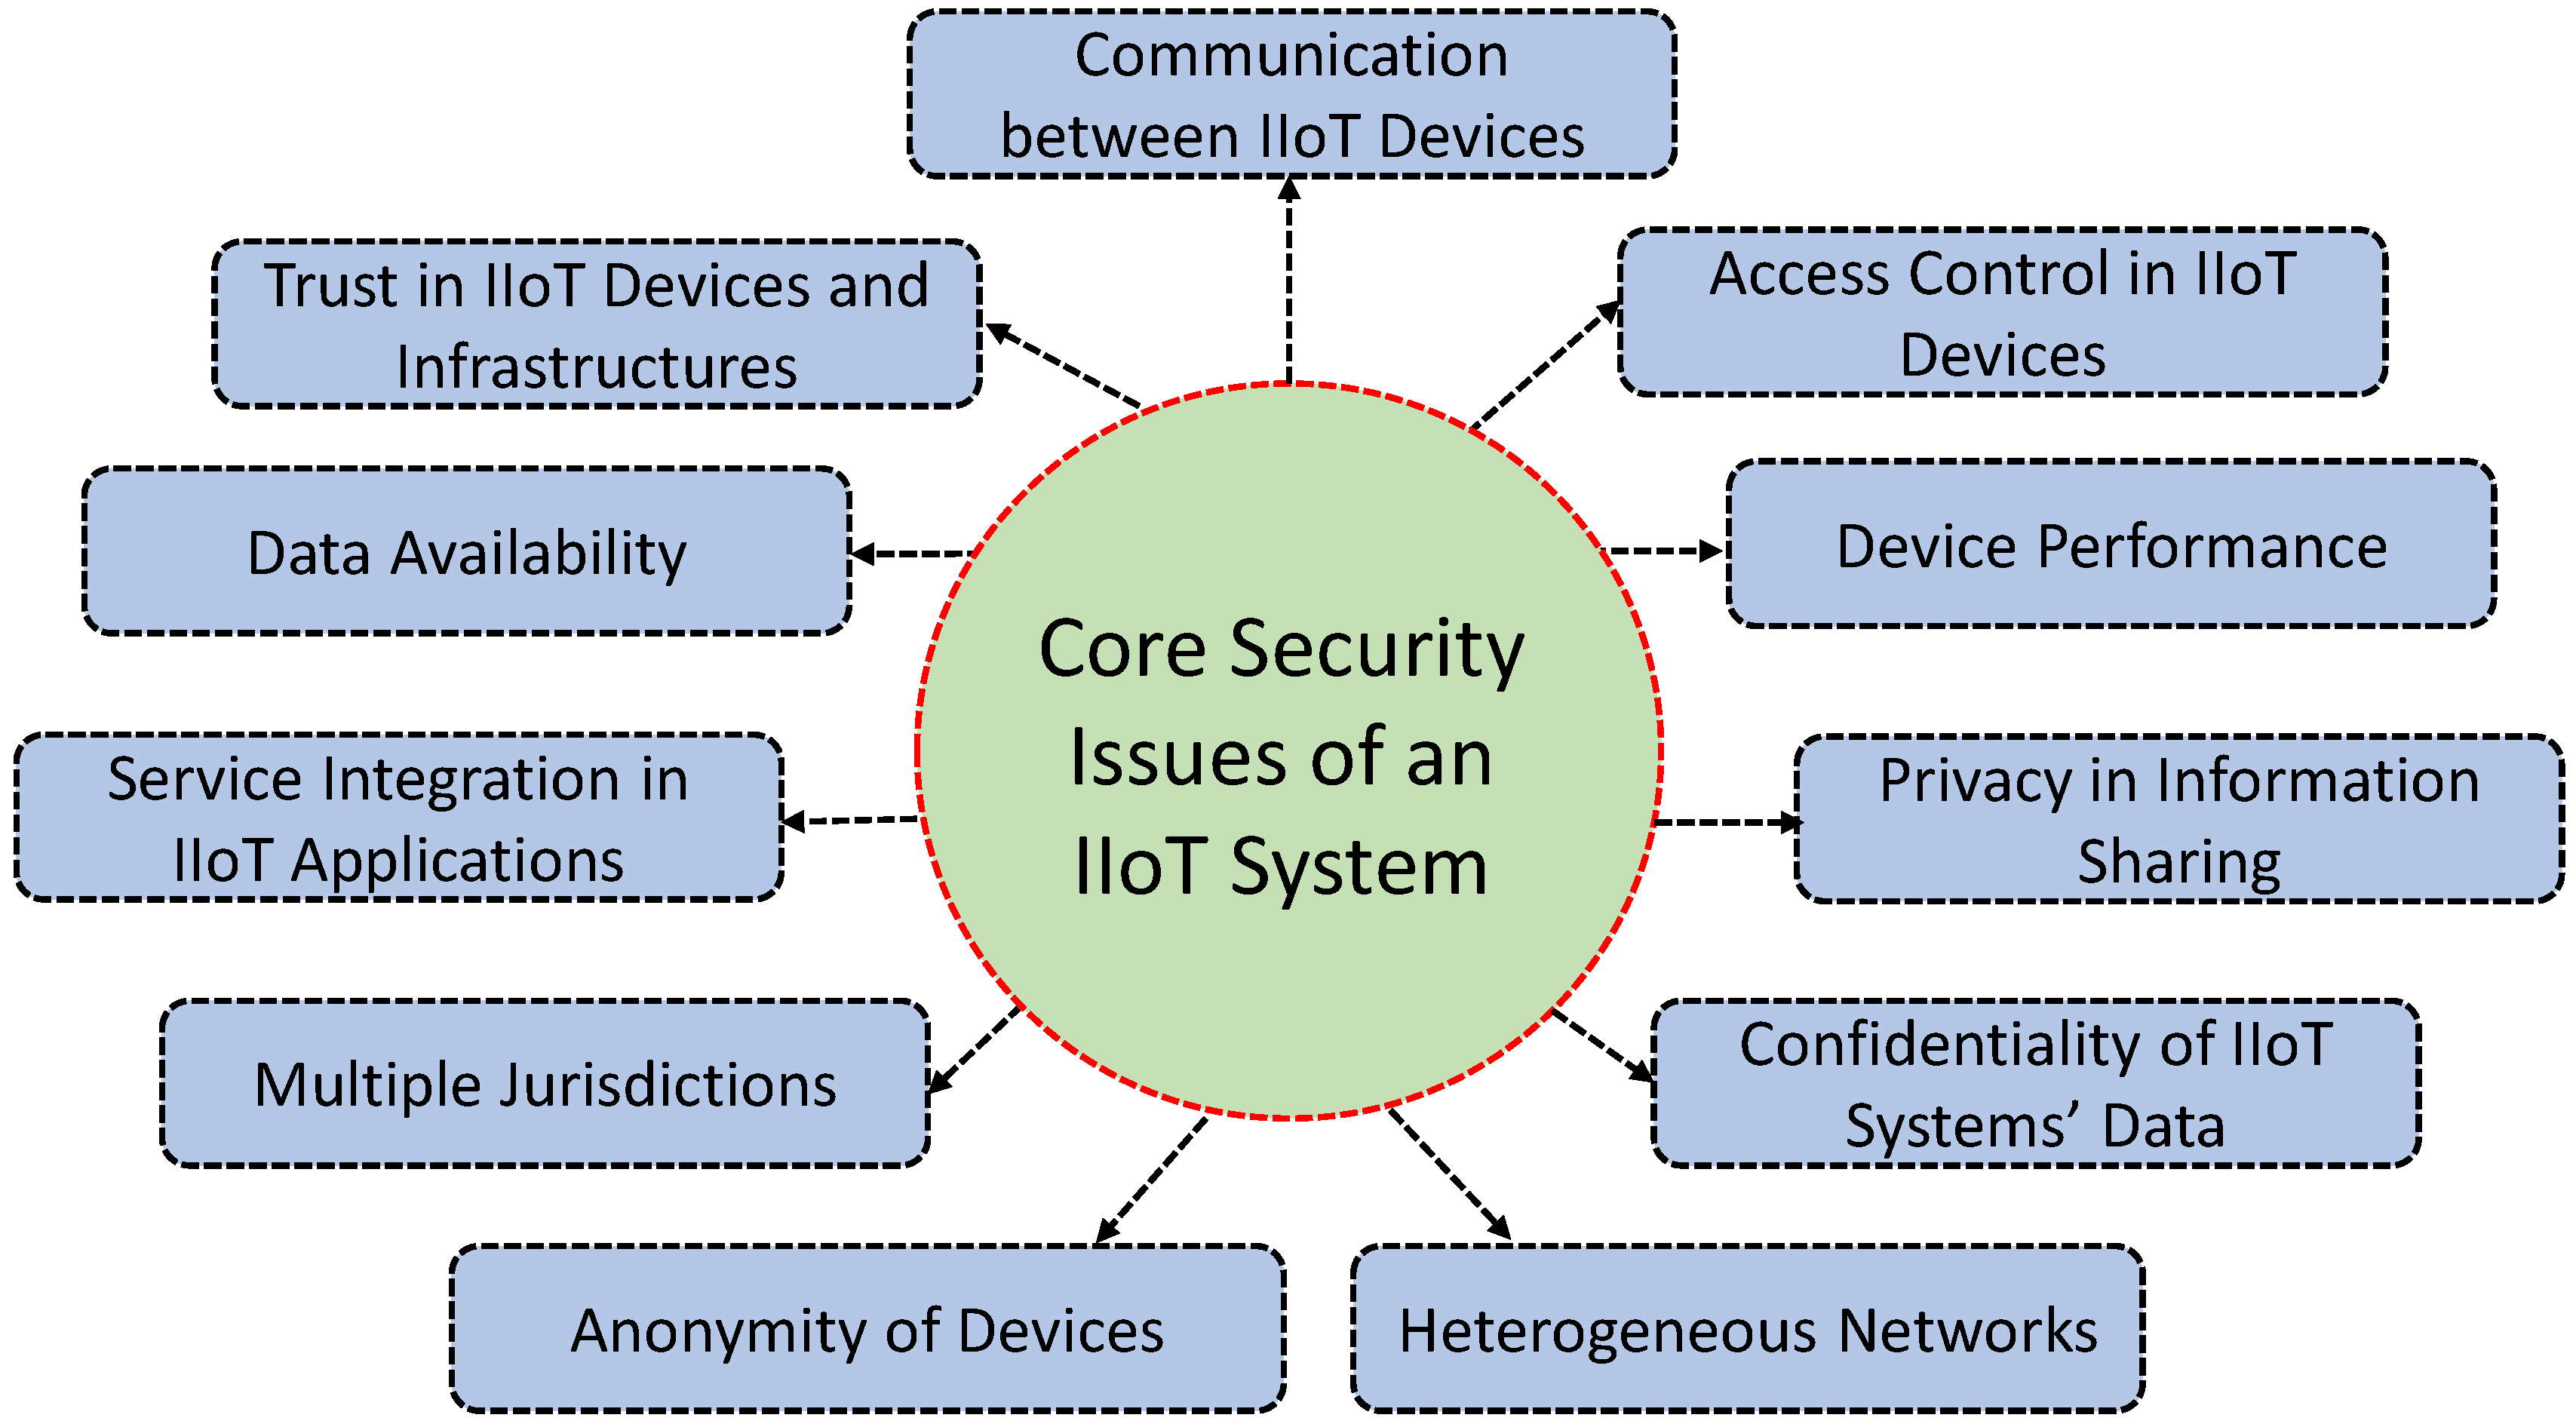
Authentication is where most organizations fail, and it is also where you get the most improvement for the least effort. Multi-factor authentication should be mandatory everywhere. Not optional. Not for admins only. For every account, including service accounts and API keys where possible. I prefer FIDO2 security keys over SMS-based two-factor authentication because SIM swapping attacks are trivially easy to execute and have compromised numerous high-profile accounts. If you cannot deploy security keys, app-based TOTP is the next best option. Time-based one-time passwords generated by an app are significantly more secure than anything sent via text message. Network segmentation is another area where people cut corners. You do not need a Fortune 500 budget to segment your network. VLANs on managed switches can isolate guest Wi-Fi from internal systems, separate IoT devices, and create a quarantine zone for vulnerable equipment. When I audited a small hospital last year, their medical devices were on the same flat network as the reception computers. One compromised printer could have reached patient records. We restructured their VLAN layout in a single weekend, which reduced their attack surface dramatically without purchasing new hardware. Logging and monitoring are non-negotiable. Centralized logging through a SIEM platform lets you correlate events across systems. Without it, you are flying blind. The common pitfall here is log volume. A busy server can generate terabytes of logs daily, and storing everything is expensive and often unnecessary. I recommend keeping detailed logs for 30 days on hot storage, moving to cold archival storage for 90 days, and deleting anything older than that unless compliance requirements dictate otherwise. That timeline covers most investigation needs without blowing your budget.
The Tools Worth Your Money
For endpoint protection, EDR solutions from CrowdStrike, SentinelOne, or Microsoft Defender for Endpoint are the current standard. They detect anomalous behavior rather than relying solely on signature matching, which catches zero-day threats that traditional antivirus misses. The tradeoff is cost and complexity. Deployment across a large organization can take weeks, and tuning the detection rules to reduce false positives requires dedicated security staff. If you are a small business, Defender for Endpoint integrated with Microsoft 365 gives you solid coverage at a reasonable price point. Firewall and perimeter defense have shifted. Traditional hardware firewalls still have a place, but cloud-native firewalls and web application firewalls are where the action is now. AWS Network Firewall, Cloudflare's WAF offerings, and Azure Firewall provide granular control with less maintenance than physical appliances. The learning curve is steeper, though. Rules that worked for a stateful packet inspection firewall don't translate directly to next-gen cloud firewalls. Budget two weeks of focused work for the migration if you are moving from on-premises to cloud-based perimeter security. Backup and disaster recovery round out the basics. The 3-2-1 rule still applies: three copies of your data, on two different media types, with one copy offsite or air-gapped. Ransomware encryption has made this non-negotiable. I recommend immutable object storage for your backup target. S3 Object Lock and Azure Blob Immutable Storage prevent attackers from deleting or modifying your backups even if they compromise your credentials. The cost premium is typically 10-15% compared to standard storage, and that premium pays for itself the first time you need to restore from a ransomware event.
Where Everything Breaks Down
I need to be honest about what these solutions cannot do. No tool catches everything. Detection gaps exist because new attack techniques emerge faster than signature updates can be written. Sophisticated threat actors use living-off-the-land techniques, executing legitimate administrative tools to blend in with normal activity. PowerShell scripts, WMI queries, and BITS jobs are all commonly abused because they look identical to routine system administration work. Human error will always be the weakest link. You can implement every security control in the book, but if an employee clicks a malicious link because the phishing email looked convincing, you have lost. This is why security culture matters more than security tools. Training programs that emphasize critical thinking over rote memorization produce better results. People who understand why security exists follow procedures consistently. People who treat security as an IT checkbox find workarounds that undermine the controls. Compliance frameworks like SOC 2, ISO 27001, and NIST CSF are not security solutions. They are audit frameworks. Following them improves your security posture measurably, but checking boxes does not equal safety. I have seen organizations pass SOC 2 audits with serious vulnerabilities still in production because the auditors focused on documentation rather than actual technical controls. Treat compliance as a baseline, not a goal.
The biggest bottleneck in implementing these solutions is resource constraints. Small teams wear too many hats. A single IT person managing a dozen responsibilities will always prioritize keeping systems running over hardening them. The practical workaround is to delegate or outsource the security workload. A managed security service provider can monitor your environment 24/7 at a fraction of the cost of hiring dedicated staff. For teams under five people, this is usually the only realistic path to adequate security coverage.
Getting Started Without Overcommitting
If you are starting from scratch or rebuilding a neglected setup, do not try to do everything at once. Prioritize authentication hardening first, because weak credentials unlock everything else. Then patch management, because unpatched software is the easiest exploit path. Then logging and monitoring, because you cannot detect incidents you cannot see. Then network segmentation and backup hardening. This sequence addresses the highest-risk items first and builds a foundation for more advanced controls. The timeline depends on your environment size. A small business with under 50 endpoints and basic cloud infrastructure can complete this prioritized sequence in two to four weeks with focused effort. Larger environments with complex architectures will take months. Plan accordingly. Rushing security implementations produces gaps that attackers exploit just as effectively as having no security at all. Documentation is the part everyone skips and everyone regrets. A single page that lists your security controls, responsible parties, incident response contacts, and backup locations saves hours during a crisis. Write it while you are not in a crisis. Update it when you change anything. The version that exists only in someone's head stops being useful the moment that person is unavailable.