What You Need to Know Before Diving In
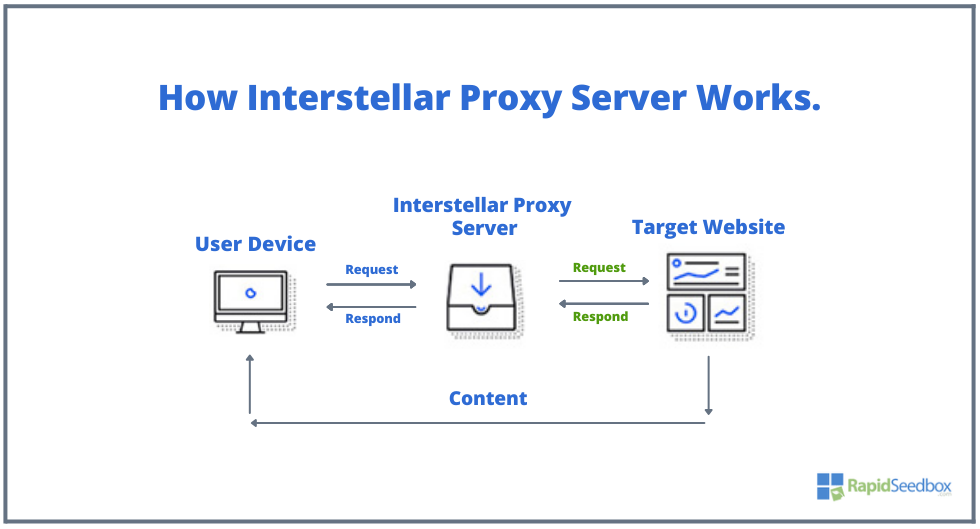
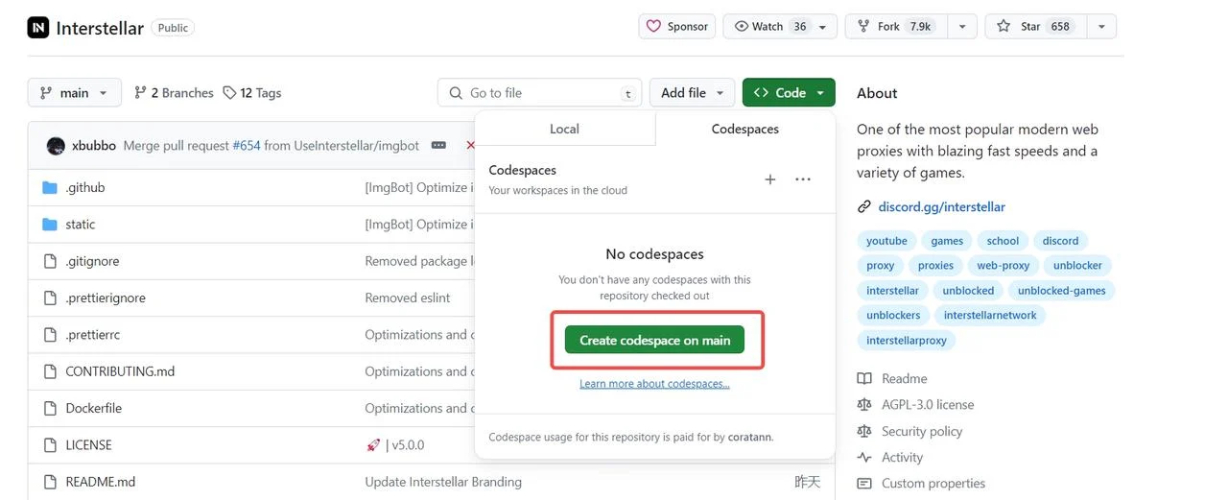
Interstellar Proxy GitHub is a self-hosted proxy solution that routes traffic through intermediate servers to bypass geo-restrictions, content filters, and network-level blocks. It gained attention mainly because of how straightforward it is to deploy and the fact that it can run on just about anything with Docker support. That convenience comes with trade-offs, which I will get to later. The project lives at a public repository where contributors maintain configuration templates, Docker Compose files, and scripts designed to make setup fast. The typical workflow involves cloning the repo, editing a few environment variables, and spinning up the stack with docker compose. That is the simple version. In practice, things get messier depending on your infrastructure, your ISP, and what exactly you are trying to unblock.
Interstellar Proxy GitHub Setup Walkthrough
Here is how I normally approach it. First, grab a Linux machine or VPS. Something modest works fine for a personal deployment. Two vCPU cores and 2 GB of RAM is a decent baseline, though heavier traffic or more concurrent users will require more headroom. Install Docker and docker-compose if they are not already present. Most modern distros have packages in their default repos, so that part is usually painless. Clone the repository directly from the Interstellar Proxy GitHub page. From there, navigate into the project directory and look at the .env.example file or the docker-compose.yml file. Those two files tell you what environment variables are required and what ports need to be open. Copy the example env file to a real .env file, then fill in your specifics: the upstream proxy endpoints, your desired listening port, TLS certificate paths if you plan to use HTTPS, and any authentication credentials you want to set. After that, run docker compose up -d. Check the container logs with docker compose logs -f to make sure everything started correctly. If you see fatal errors related to certificate paths or DNS resolution, stop and fix those before proceeding. A common mistake I see people make is pointing the container at a certificate file that does not actually exist inside the container filesystem. The host path needs to be volume-mounted properly, or you need to copy the certs into the container explicitly.
Once the proxy is running, point your browser or system proxy settings to the address and port your container is listening on. For a local test, that is usually http://localhost:8080 or whatever port you configured. For remote access, you will need to make sure your firewall rules allow inbound traffic on that port, and ideally set up TLS so the traffic is encrypted in transit.
Get the Full Details

Things That Actually Break in Production
I ran into a specific issue a while back that took me about four hours to track down. I was deploying Interstellar Proxy on a lightweight Debian VPS and everything appeared to work initially. Web pages loaded, requests were being routed through the upstream proxies, and the logs looked clean. Then I noticed that certain sites were returning incomplete responses. HTML would load fine, but assets like CSS and JavaScript files would time out or come through corrupted. The root cause turned out to be a buffer size mismatch between the proxy and certain CDNs that use chunked transfer encoding with unusually large headers. The default buffer configuration in the project was too small for those edge cases. I solved it by overriding the buffer pool size in the configuration and increasing the connection read timeout from the default 30 seconds to 60 seconds. It was not a bug in the traditional sense. It was more of an incompatibility with certain upstream response patterns that the default settings simply were not tuned for. Another thing nobody really emphasizes is DNS resolution inside the container. If your upstream proxies rely on DNS lookups and your container is using the host network mode incorrectly, you can end up with slow or failed resolution. I had a case where queries were taking eight seconds instead of sub-second times because the container was falling back to a slow public DNS resolver. Setting the DNS explicitly in the compose file to something like 1.1.1.1 or 8.8.8.8 fixed it immediately.
Limitations You Should Accept Upfront
This tool is not a silver bullet. It has real limitations that matter depending on your use case. For one, it is not designed for high-throughput commercial deployments. If you are running this for a small team or personal use, you are probably fine. But once you push more than a few dozen concurrent connections through it consistently, you will start seeing latency spikes and increased memory usage. The project is relatively lightweight compared to enterprise-grade proxy solutions, but that is partly because it lacks many of the optimizations those solutions have. Another limitation is maintenance overhead. The project does see active development, but releases can come with breaking configuration changes. I have personally upgraded from one version to the next and found that an environment variable I had been relying on for months was renamed without a migration guide. Always keep a backup of your configuration before pulling a new image, and check the commit history or changelog before upgrading. Security is also a concern if you expose this proxy to the internet without proper hardening. The default setup includes basic authentication in some configurations, but if you are running it without TLS or without restricting which IPs can connect, you are basically offering an open relay. Anyone who discovers your instance can route traffic through it, which exposes you to abuse and potential legal complications depending on your jurisdiction. At minimum, put it behind a reverse proxy with TLS, restrict access by IP if possible, and never expose it on a public interface without authentication and logging.
For users who need something more robust or enterprise-ready, alternatives like Shadowsocks-libev, V2Ray, or commercial proxy hosting services tend to offer better performance under load and more mature security features. Interstellar Proxy GitHub is useful when you want something quick to deploy and easy to understand, but it is not the right choice if you need production-grade reliability at scale.
Practical Tips That Save Time
Monitor your container memory usage regularly. A simple docker stats command run every few minutes will show you if memory is creeping up, which is a sign that you need to tune the connection limits or increase your available RAM. I usually set things so that the container gets no more than half the host's available memory to leave room for the OS and other processes. Use a reverse proxy like Nginx or Caddy in front of Interstellar if you need TLS termination. Doing it inside the container is possible, but managing certificates directly inside Docker adds unnecessary complexity. Let a proper reverse proxy handle the certificates, terminate TLS, and forward plain HTTP to the proxy container. That way you also get features like rate limiting and access logging for free. Keep your logs rotated. By default, Docker will accumulate logs indefinitely unless you configure log rotation in your compose file. Without rotation, you can fill up your disk in a matter of days if the proxy is handling a lot of traffic. Add a logs section to your service definition with max-size and max-file options set to reasonable values, like 50 MB per file with three files kept.
If you are using this to bypass regional restrictions for media streaming, be aware that some platforms actively detect and block known proxy IP ranges. You may need to rotate upstream proxies or use residential proxy endpoints to avoid throttling or outright blocking. This is not a problem unique to Interstellar Proxy. It is a general limitation of any proxy-based approach to geo-unblocking. The official repository for Interstellar Proxy GitHub can be found by searching the project name directly on GitHub. There is no official binary distribution, so you are working from source or Docker images built from the repository. The README usually contains the most up-to-date setup instructions, so rely on that rather than older blog posts or tutorial videos that may reference deprecated configuration options.