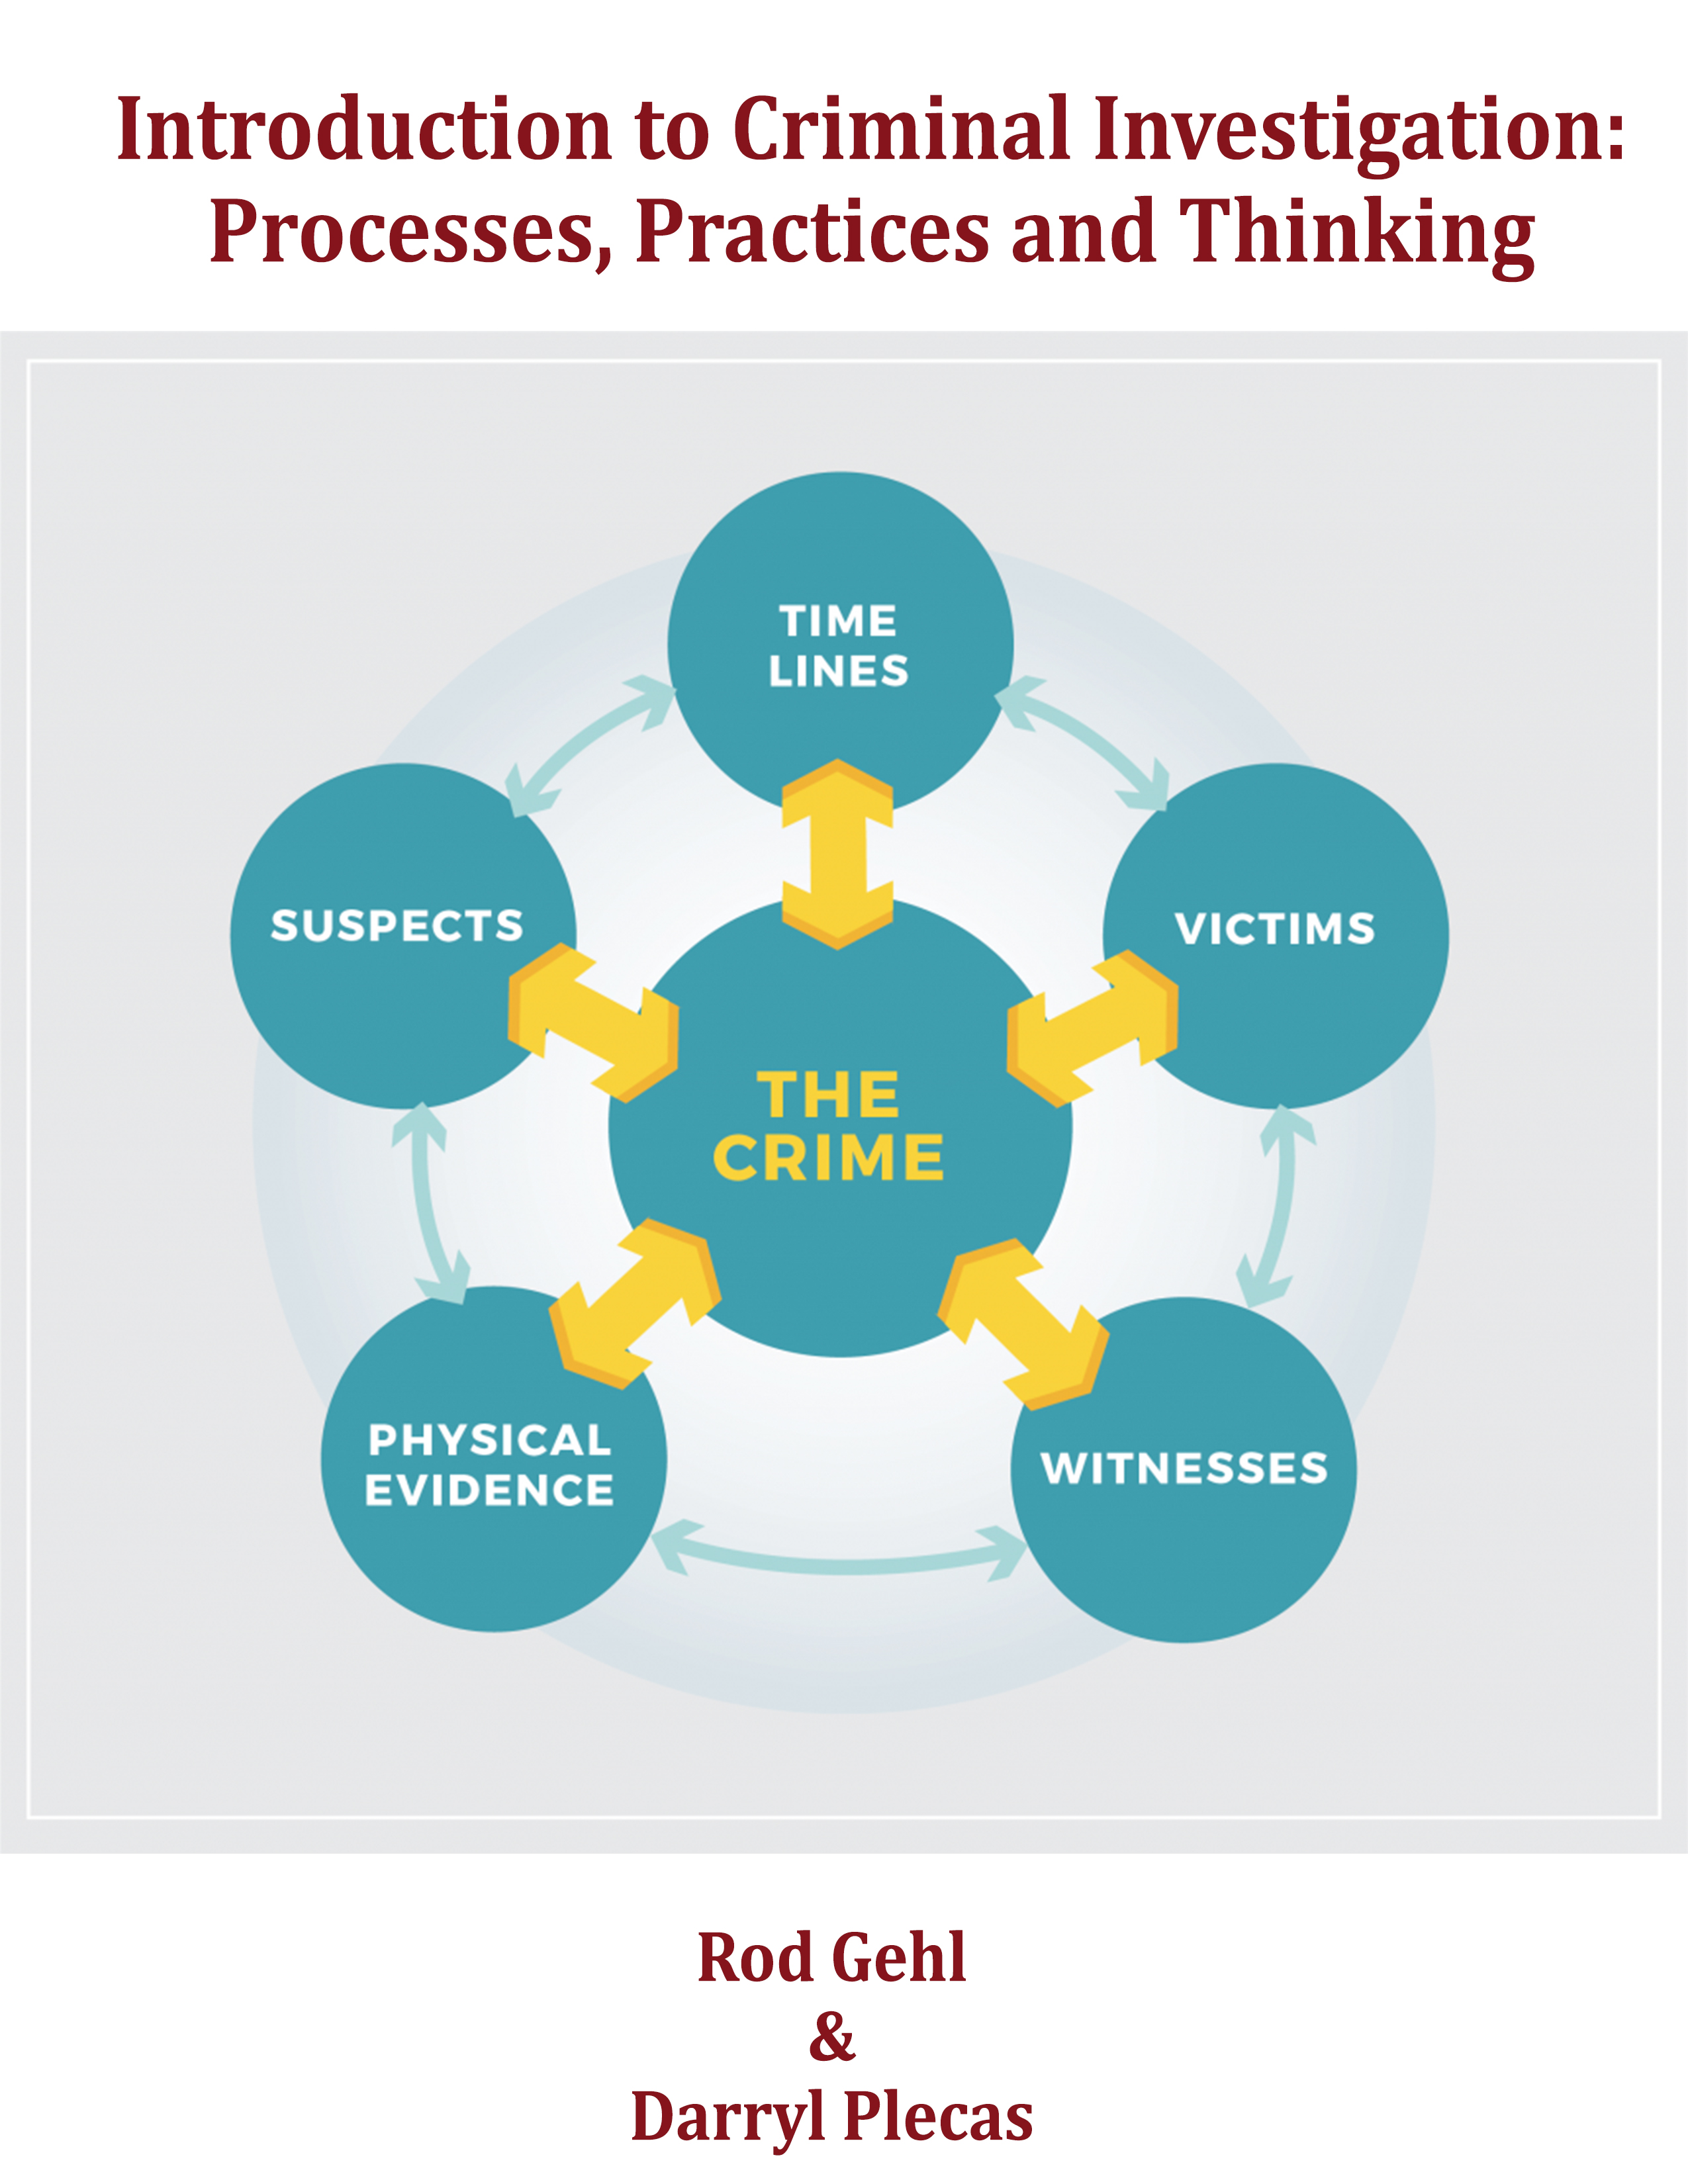
What actually happens when you start an investigation
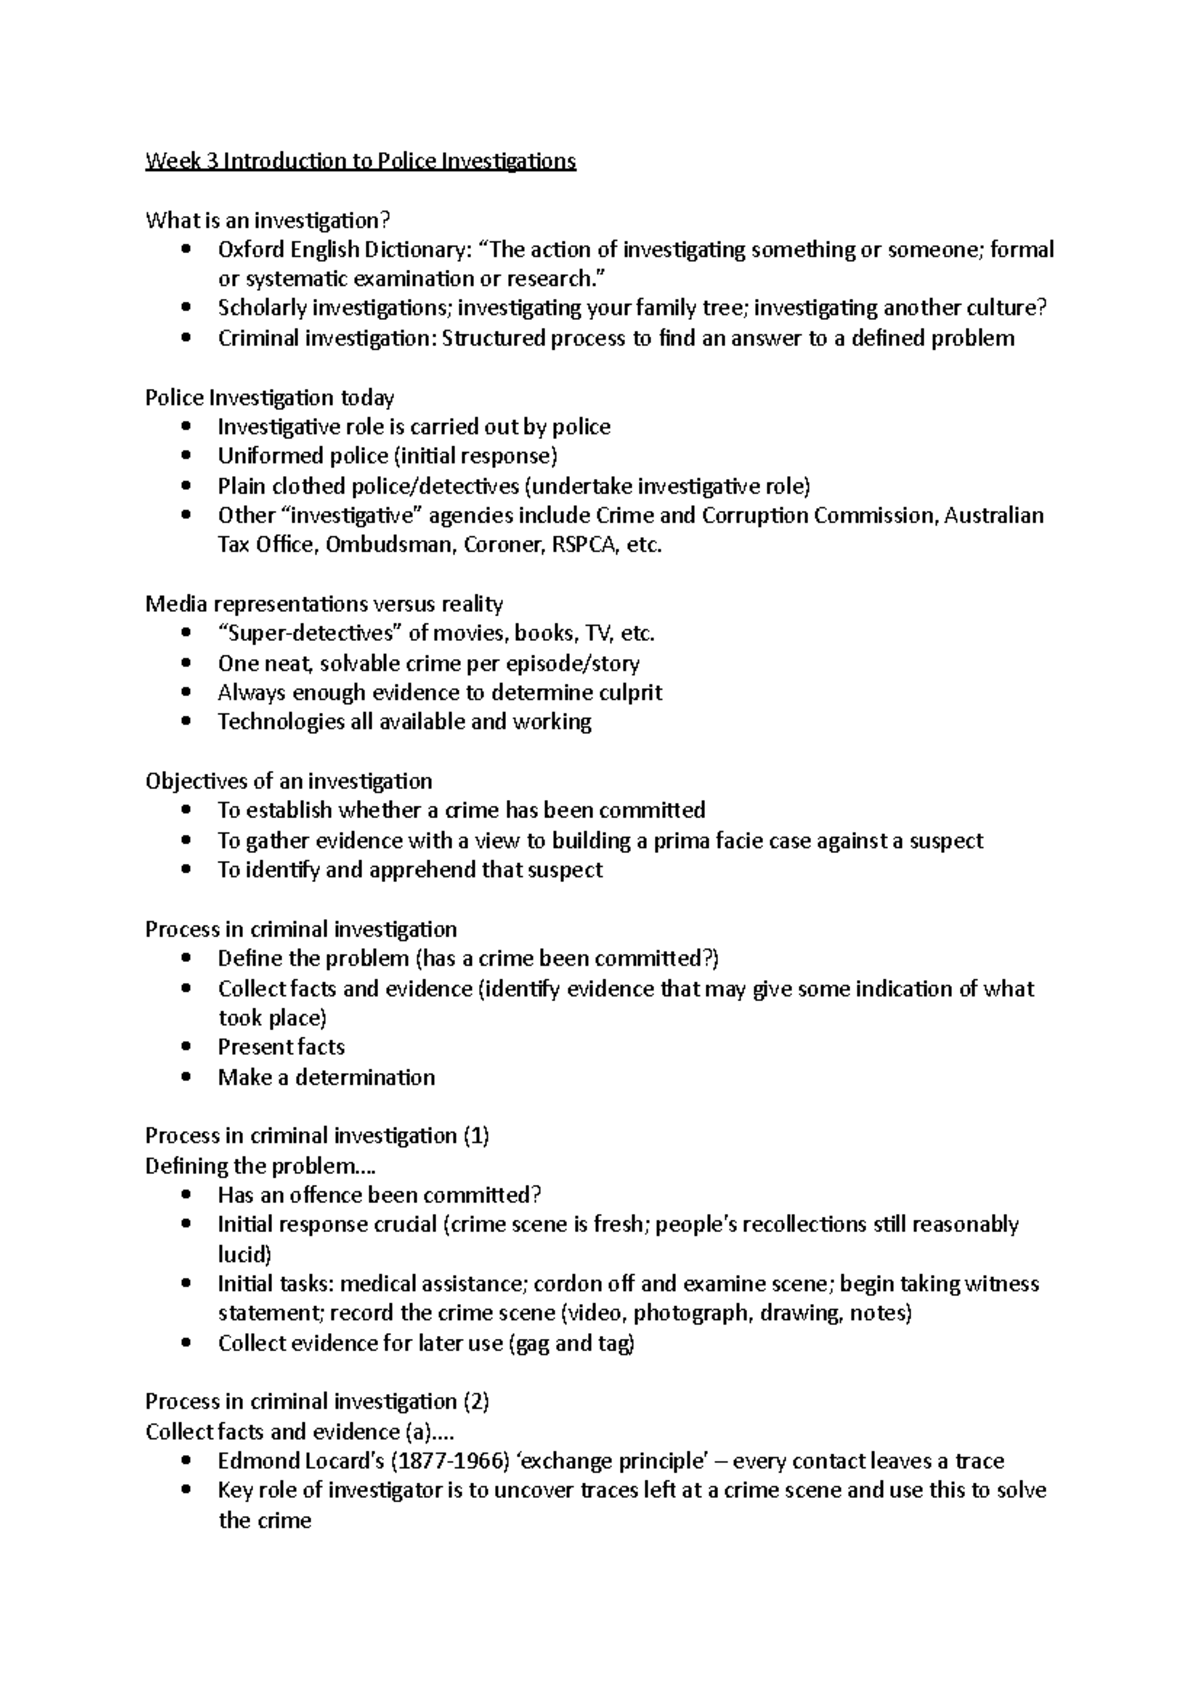
Most people think investigations are about following a checklist. They're not. The checklist comes later, once you've figured out what you're actually looking for and why the data isn't cooperating. I spent years building out formal methodologies for internal investigations, mostly in corporate and compliance settings, and the hardest part was never finding the evidence. It was knowing what question to ask before the evidence even existed. The first step in any Introduction To Investigations process is defining the scope of inquiry with enough precision that you can tell when you're done. Most people fail here. They launch into data collection without narrowing the universe of what matters. An investigation into suspected expense fraud, for example, doesn't start with downloading every receipt from the last five years. It starts with identifying the specific account type, the geographic region, the employees involved, and the timeframe where anomalies cluster. I once inherited a case that looked like it would require six months of manual review across three departments. I spent three hours mapping the transaction codes and found that 94% of the fraudulent activity ran through two specific GL accounts using one particular vendor category. The scope dropped from millions of records to about forty thousand. That's the difference between an investigation that dies under its own weight and one that actually finishes. There's a technical term for it — chain of custody documentation — but it just means recording who touched what evidence and when, from the moment you identify it to the moment it's filed away. If you can't explain who handled it at any given point, the evidence becomes unreliable in any formal proceeding. This isn't academic. I worked a case where the HR director wanted to use internal interview transcripts as leverage in an employment dispute. The legal team rejected the entire set because the original documents had been forwarded through three separate email threads without consistent metadata preservation. Six weeks of interview work, gone. Not because it was irrelevant, but because it wasn't properly maintained.
The practical workaround I adopted and still use is simple: create a single evidence log spreadsheet from day one, not after you've accumulated data. Each row tracks the document name, source, extraction date, person who retrieved it, hash value if applicable, and current location. It takes about ten minutes to set up and three minutes per piece of evidence to update. The alternative is reconstructing that provenance from memory, which rarely works and never works well under scrutiny.
Common approaches and what they get wrong
There are several standard frameworks you'll encounter. The traditional investigative method follows a linear path: define the problem, gather information, analyze, conclude, report. The digital forensics model adds stricter acquisition protocols and validation steps. The intelligence-driven approach treats the investigation as a hypothesis-testing loop rather than a straight line. The problem with teaching any of these as rigid sequences is that real investigations don't behave sequentially. You'll analyze a small sample of data before you've finished gathering the full set. You'll revise your original hypothesis three times. You'll discover that the problem you defined in week one was only a symptom of something else entirely. The framework that works best in practice is the one that lets you pivot without burning the work you've already done. I learned this the hard way during an investigation into potential insider trading involving senior sales staff. I had built a timeline connecting specific trades to non-public revenue announcements. Two months in, I found that the correlation was actually caused by a third variable — a quarterly bonus threshold that coincidentally aligned with both the trades and the announcement schedule. My timeline was technically accurate but causally wrong. The fix wasn't starting over. It was adding a confounding variables section to the analysis and re-running the correlation with the bonus structure as a control. That alone saved about forty hours of dead-end verification work.
Get the Full Details
Tools that actually matter
You don't need expensive software to start. The core toolkit is: a spreadsheet for logging, a secure storage location with access controls, a hashing tool for any digital files you collect, and a notes system where every decision and rationale is recorded. That's it. The tools people over-prioritize are case management platforms and automated analytics suites. They're useful, but they add complexity that slows you down more than it helps during the early stages. For people who want to go further, open-source options exist. Autopsy is a solid digital forensics workbench. Splunk's free tier handles log analysis at a reasonable scale. Excel or Google Sheets will serve as your primary evidence log until you hit the point where they can't. There's no download requirement for the methodology itself — it's a process, not a product. If you're looking for structured training material, the SANS Institute offers free Introduction To Investigations resources that cover the fundamentals without selling you anything.
What breaks when you skip the boring parts
The parts people skip are the documentation, the scope definition, and the version control on your working files. When you skip them, three things happen. Your findings become impossible to reproduce. Someone else picks up the case and wastes days figuring out what you already knew. And if the investigation ever faces external review — legal, regulatory, or public — you have no way to demonstrate that your conclusions weren't manufactured retroactively. I've seen all three. The worst case involved a compliance investigation where the lead analyst hadn't dated-stamped a single extracted file. When the external auditor asked for the original source of a key email, the analyst couldn't produce it. The conclusion — that there was no evidence of wrongdoing — was dismissed not because it was wrong, but because it was unverifiable. The cost was roughly eight months of the organization's time and significant reputational damage that had nothing to do with the original suspicion.
When investigations should stop
This is the part nobody teaches. An investigation should stop when the remaining questions can't change the outcome, when the cost of further inquiry exceeds the value of the answer, or when you've reached the limit of what the available evidence can support. I've watched colleagues extend investigations for months chasing marginal probabilities that would never have held up in any formal setting. The organization spent more on the investigation than the potential recovery or enforcement action would ever justify. That's not thoroughness. That's sunk cost fallacy wearing a professional coat. The cleanest way to know you're done is to write the conclusion first. If you can state what the evidence supports, what it doesn't, and what remains unknowable, you're ready to close the file. Anything after that is just accumulating pages.