The Short Answer
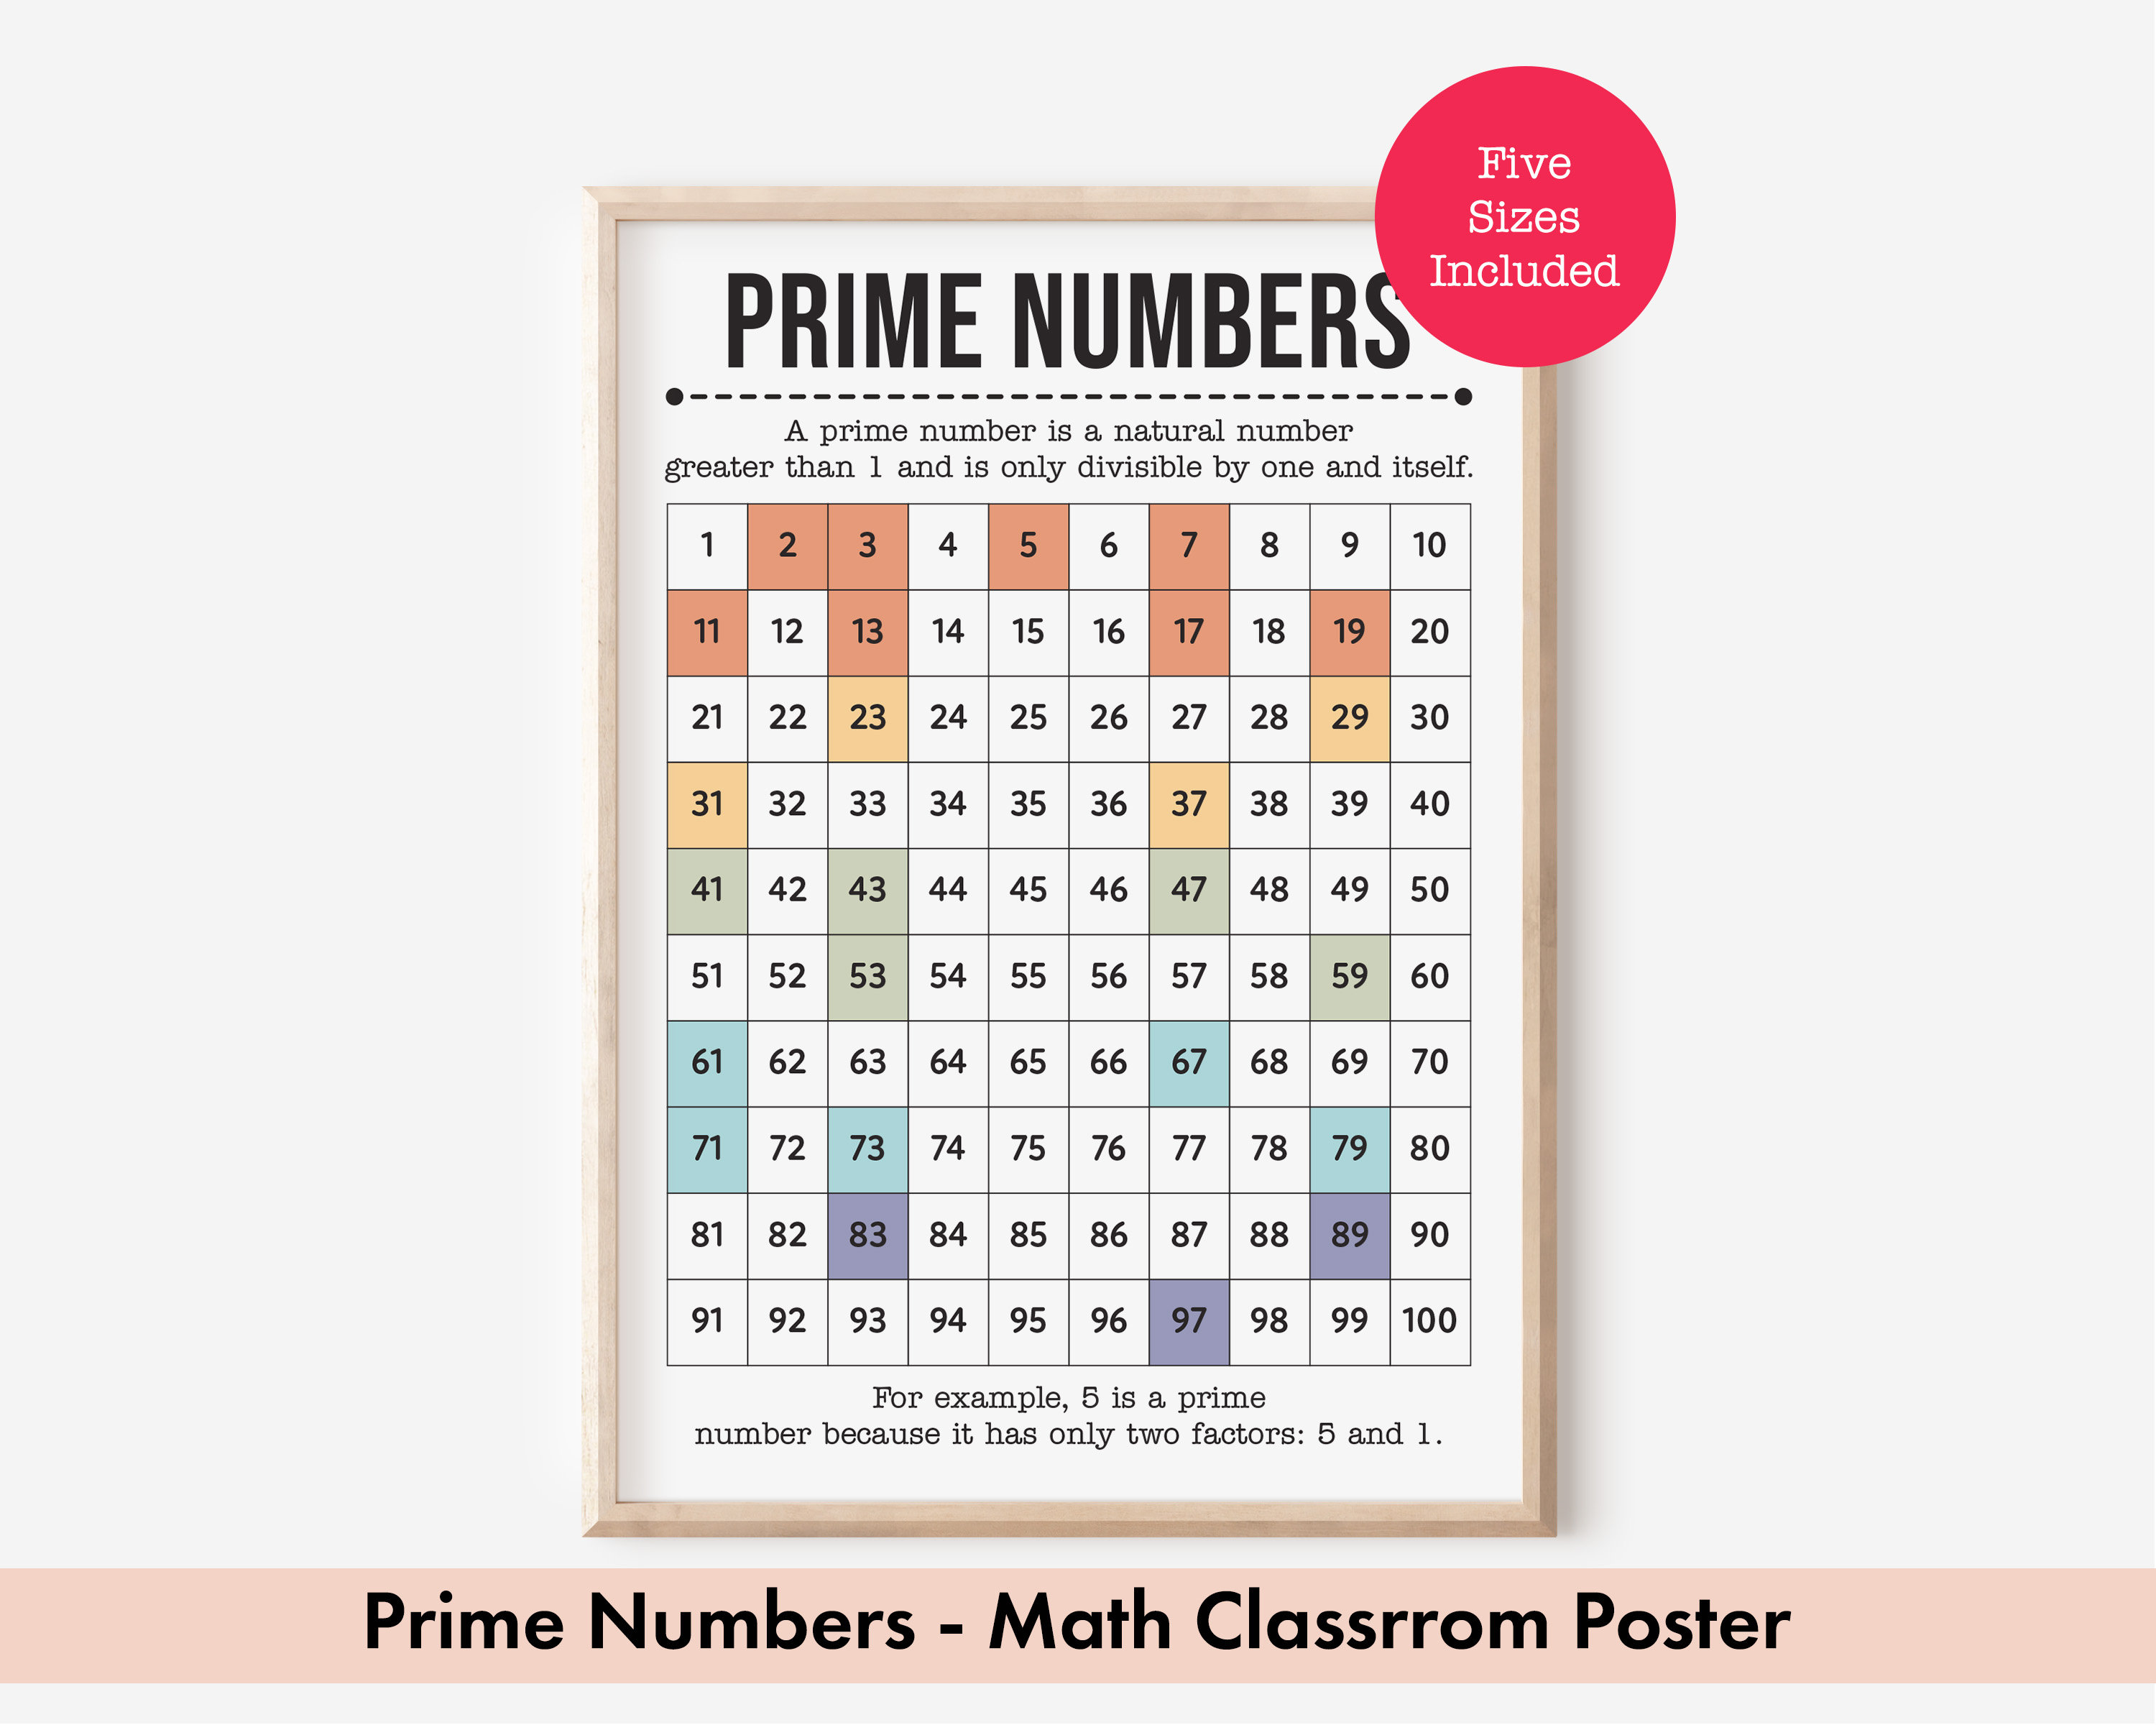
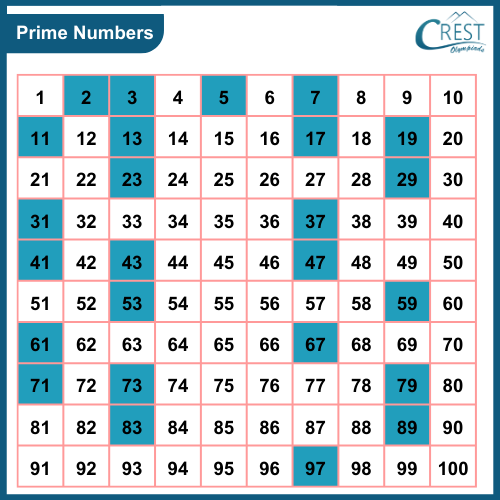
No, 1 is not a prime number. This isn't a trick question or a modern redefinition that appeared recently. The exclusion of 1 from the primes is one of the oldest conventions in mathematics, going back at least to Euclid's Elements, though the formal definition we use today solidified much later. If someone tells you 1 is prime, they're either mistaken or working in a context that explicitly redefines things, which is vanishingly rare. The modern definition of a prime number is straightforward: a natural number greater than 1 that has exactly two distinct positive divisors—1 and itself. Since 1 only has one divisor (1 itself), it fails the definition on its face. You don't need to dig deeper than that for most practical purposes. The definition exists for a reason though, and that reason is the fundamental theorem of arithmetic. This theorem states that every integer greater than 1 can be expressed as a product of primes in a way that is unique up to the order of the factors. If you include 1 as a prime, that uniqueness collapses entirely. You could insert any number of 1s into a factorization without changing the result, which makes the whole concept of unique factorization useless. Mathematically, it's not just a minor inconvenience. It breaks the theorem.
I ran into this more directly than you might expect when I was writing a custom integer factorization routine for a project that needed to decompose numbers up to around 10^12. Early on, I had the primality check returning true for 1, and it didn't cause an immediate crash. The real problem showed up downstream when the code started producing factorizations with spurious 1s in them. One particular edge case was when the input was itself a prime like 999983. My function returned [1, 999983] instead of [999983]. That looked fine at first glance until I fed the output into a function that checked whether a list represented a complete prime factorization by multiplying everything back together. The multiplication check passed because 1 times anything is anything, so the bug was silently invisible for a long time. I caught it only because I added a separate validation step that verified each element in the factorization was actually prime using an independent library. That library rejected 1 immediately. It took me maybe twenty minutes to track down, but the fix was simply adding a guard clause that returns false for any input less than 2 before even attempting a trial division loop. The deeper insight most people miss is that excluding 1 isn't arbitrary pedantry. It's structurally necessary. Primes are the multiplicative building blocks of the integers. Units like 1 and -1 occupy a completely separate category in ring theory. In the integers, 1 is a unit, not a prime. Conflating the two creates noise in proofs and algorithms alike. The same logic applies to 0, which isn't prime for a different set of reasons involving division by zero and the fact that every integer divides 0. There are also practical computational considerations. Many algorithms assume the smallest prime is 2. Sieve of Eratosthenes implementations start marking from 2 squared, which is 4. If you accidentally include 1 in your prime list, a sieve that blindly trusts its input can produce corrupted output arrays or infinite loops depending on how the indexing is set up. I've seen this happen in student code and in some older libraries that predate widespread adoption of the standard convention. It's worth knowing what to look for if you're integrating external prime-generating code.
Some older textbooks and a handful of introductory resources still list 1 as prime, usually because the author is using a pre-19th century definition or hasn't updated their material. Don't treat those as authoritative on this point. The mathematical community settled this over a century ago. The current consensus is uniform and unambiguous. For anyone building systems that depend on prime numbers—cryptography, hash functions, randomized algorithms—the exclusion of 1 is baked into essentially every implementation you'll encounter. OpenSSL, GMP, the Python standard library's sympy package, Rust's num-prime crate. All of them treat 1 as non-prime. If you write your own primality test and get a different result, the bug is almost certainly on your side, not in the definition.
Get the Full Details