What the ISACA CCA Exam Actually Tests
The ISACA Certified in Cybersecurity (CCA) credential isn't a certification you pass by memorizing acronyms. It's built around a question format that mixes scenario-based items with direct knowledge recall, and the way the questions are written forces you to think like someone who has actually sat in an incident response meeting rather than someone who finished a training video series. When I first started working with this exam format, I expected the same kind of plug-and-play studying that works for CompTIA Security+. That approach doesn't work here. The questions deliberately push you into ambiguity. You will see scenarios where multiple answers appear technically correct, but only one aligns with the ISACA framework priorities. The trick isn't finding the right answer. The trick is understanding which governance layer ISACA prioritizes when two valid practices conflict.
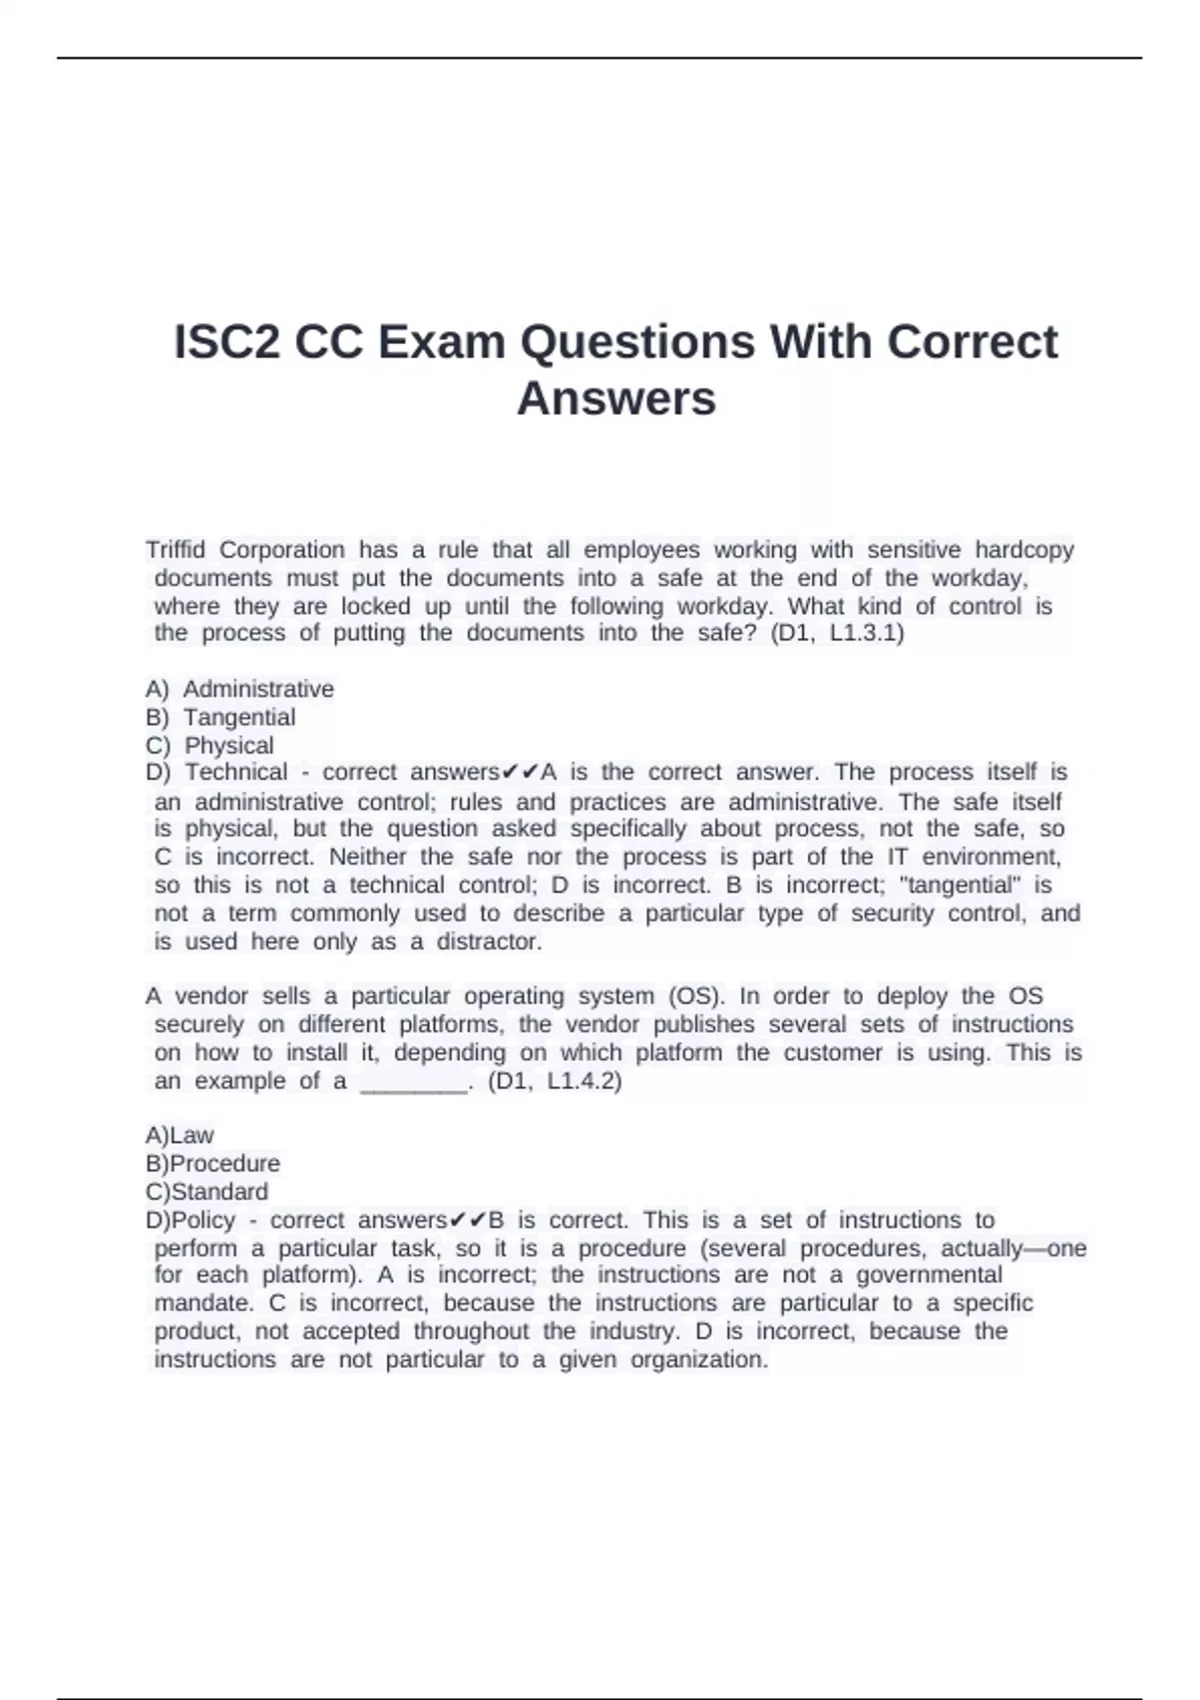
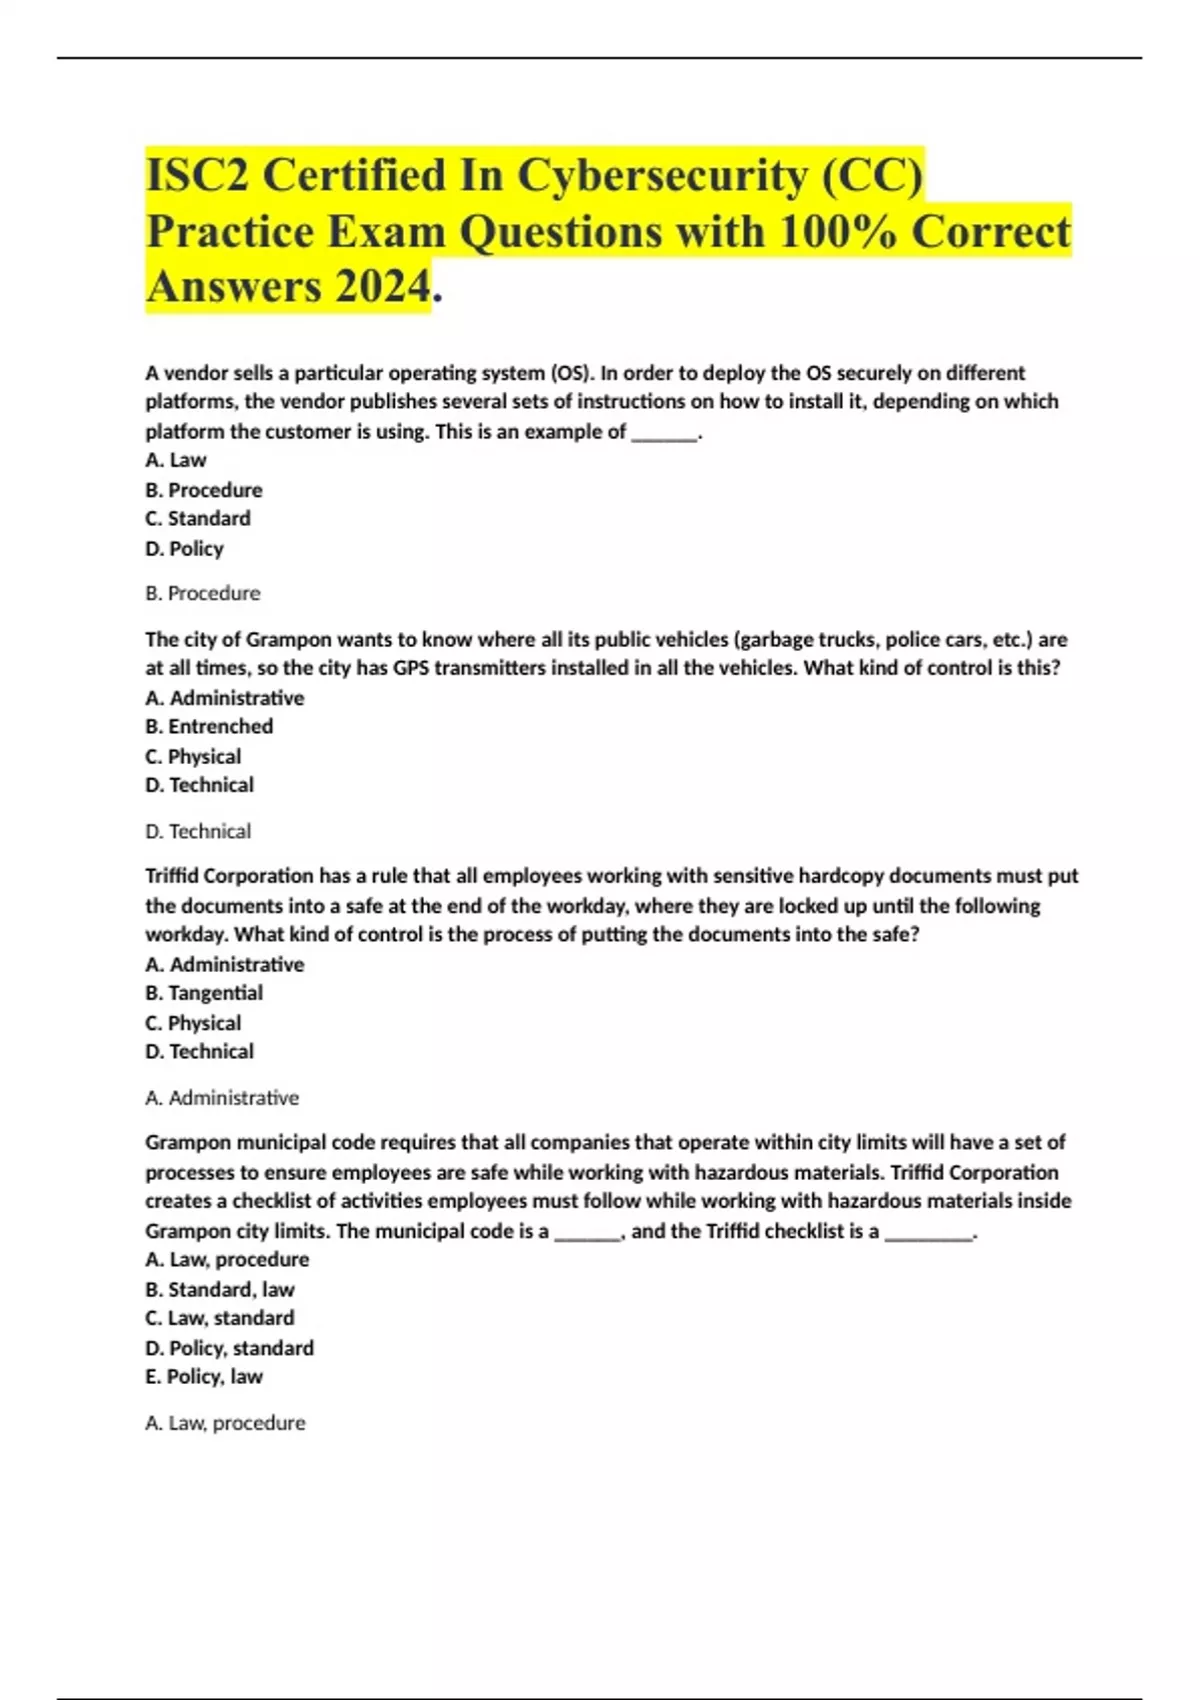
Isc2 Cc Exam Questions
The structure breaks down into three main buckets: risk management and governance, security operations, and incident response fundamentals. Each bucket carries roughly equal weight, and the exam uses adaptive testing to adjust question difficulty based on your performance. That means early questions matter more than later ones in terms of how the algorithm calibrates the difficulty curve. You cannot coast through the first half and then power through the second half because the scoring mechanism treats them differently. I remember running into a specific problem during my own prep that took me three days to resolve. The practice questions I was using had answer explanations that were vague to the point of being useless. They would say something like "answer A is correct because it aligns with best practices" without specifying which best practice, which framework section, or which ISACA document. That explanation style doesn't exist in the real exam. The official materials ground every answer in a specific domain reference. I had to switch to using the ISACA CCA Review Manual directly and stop relying on third-party dumps that stripped out the reasoning framework. This changed my accuracy from about 58 percent to 74 percent over two weeks because I finally started mapping each wrong answer back to the specific governance principle it violated rather than just memorizing the right choice. The counter-intuitive part most people miss: the exam tests more on operational decision-making than on technical configuration. You will see questions asking what to do when a security policy conflicts with a business deadline, not questions asking how to configure a SIEM rule. This is intentional. ISACA built the CCA credential for people who need to operate at the intersection of business and security, not purely technical staff. If your study plan focuses entirely on technical concepts and ignores governance and risk communication, you will underperform even if you know the technology cold.
How to Approach Studying
Start with the official ISACA CCA Exam Outline published on their website. It lists the exact content domains and their percentage weights. Read it before opening any other material. Most people skip this step and jump straight into a study guide, which means they spend weeks studying things that carry less weight on the exam. Here is the practical timeline that works: allocate four to six weeks with consistent daily study. Use the first two weeks for domain reading and note-taking, the next two weeks for targeted practice questions per domain, and the final week for full-length simulated exams under timed conditions. If you are working full-time, expect to spend roughly 60 to 90 minutes per day. Cutting it shorter than 45 minutes daily rarely produces retention because the question style requires context-switching ability, and short sessions don't give you enough mental runway to build that skill. I ran into a bottleneck once where I kept getting 68 to 72 percent on practice exams but couldn't break past 75 no matter how many questions I completed. The problem wasn't knowledge. It was question interpretation speed. I was reading too slowly and over-analyzing each scenario. I fixed it by doing timed sets of 20 questions at a time with a strict four-minute limit per question, forcing myself to commit to an answer without going back. My score jumped to 78 within five days of using that method. The exam allows about 90 seconds per question on average due to the adaptive structure, so practicing under time pressure isn't optional. It's mandatory.
Get the Full Details
Where to Find Legitimate Practice Materials
The official ISACA Question, Answer, and Explanation database is the closest resource to the real exam. It includes the same explanatory depth you will find in the actual test. Third-party providers exist, but their quality varies wildly. Many recycle outdated questions or strip the reasoning layers that make the exam distinctive. I used a mix of official materials and one commercial platform, and the difference in explanation quality was stark. The official database references specific ISACA publications. Cheap dumps do not. Be careful with study groups and forums: some people share recalled questions from the exam, which violates ISACA's non-disclosure agreement and can result in certification revocation if discovered. I've seen it happen. The risk isn't theoretical. ISACA tracks answer patterns and can flag candidates who demonstrate knowledge of recently retired questions. Stick to officially approved or clearly labeled practice sources.
What the Exam Actually Feels Like
The exam environment is proctored remotely through ISACA's testing platform. You will need a quiet room, a webcam, and a stable internet connection. The proctor monitors your screen and your physical space through the camera. They will ask you to show your workspace before the exam starts. This usually takes about eight minutes. Plan accordingly. The question format includes multiple-choice and some drag-and-drop items. You will not see performance-based questions that require building a firewall rule or writing a script. The CCA is a knowledge and judgment assessment, not a hands-on lab exam. If you are preparing for this expecting to configure tools, you are preparing for the wrong exam entirely. One specific edge case I want to mention involves terminology. ISACA has its own definitions for terms like "risk appetite" and "residual risk" that differ slightly from NIST or ISO formulations. The exam follows ISACA definitions, not the newer frameworks. I lost points on two questions because I answered using NIST SP 800-37 guidance instead of the ISACA position. It sounds minor, but those two questions cost me about four percent of my total score. Always default to ISACA publications when definitions conflict.
Limitations You Should Know About
The CCA credential has clear scope limits. It is entry-level by design. Employers in certain regions treat it as a hiring filter for junior SOC analysts or compliance assistants, but it does not carry the same weight as CISSP or CISM in senior roles. If your goal is leadership certification, this is a stepping stone, not a destination. Factor that into your decision. Another limitation: the exam does not cover cloud security configuration in depth. You will see conceptual questions about shared responsibility models, but you will not be tested on AWS IAM policies or Azure Sentinel rule creation. If your job requires hands-on cloud security skills, the CCA alone will not validate those. Pair it with a technical certification if that gap matters for your career path. The retake policy allows you to sit for the exam up to three times within a 12-month period from your initial registration. The fee resets each attempt. Budget for this possibility so it doesn't become a surprise expense. I knew someone who failed twice and almost gave up because the second retake fee hit harder than expected. It is manageable if you plan for it, but it is easy to overlook until the bill arrives.
My recommendation for preparation is straightforward: read the outline, use the official question database, practice under timed conditions, and treat every wrong answer as a learning opportunity rather than a failure metric. The exam rewards systematic thinking over technical memorization. If you build that habit during study, the test itself becomes considerably easier than most people expect.