What You Actually Need From an ISC2 CC Prep Resource
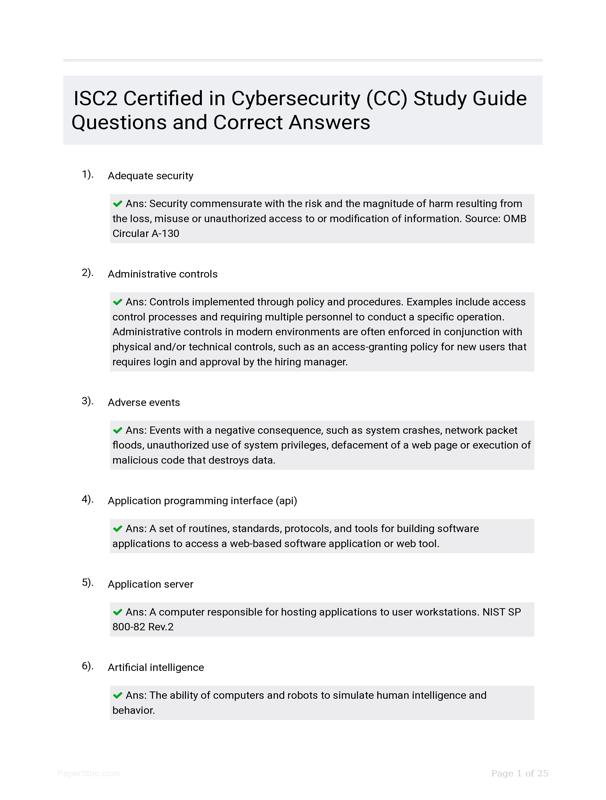
Most people buy or download a study guide and then don't know what to do with it. The ISC2 Certified in Cybersecurity exam is broad by design, not deep. It covers foundational terms across domains, and the question style rewards reading comprehension more than rote memorization. A good Isc2 Cc Study Guide will give you the structure, but it won't do the work for you. Start with the official exam outline, not the guide itself. The outline is your source of truth for domain weighting and topic inclusion. The guide is supplementary. I've had people waste three weeks on flashcards for CISSP-level domains that don't even appear on the CC exam in meaningful detail. The CC has four domains: security principles, business continuity principles, access control concepts, and incident response principles. That's it. Keep it narrow. Here's what works in practice. Read one domain section from your guide in a single sitting, then immediately answer 20-30 practice questions on that same domain. Don't move forward until you're scoring above 75 percent. If you're not, go back and re-read, but this time take notes by hand. Writing things down changes how you retain them, and the CC exam has more reading-heavy questions than most people expect.
I ran into this issue once during my own prep: the practice questions in one popular guide were phrased so differently from the actual ISC2 style that I was overconfident before the real exam. Their questions told you exactly what they wanted. Real ISC2 questions are deliberately ambiguous and test whether you can pick the best answer, not just a correct one. I switched to the official ISC2 practice exam and a few other sources that mimic the wording more closely. The difference was noticeable on test day. I still missed two questions where I second-guessed myself, but I wouldn't have passed without fixing that habit beforehand.
Domain Breakdown - What to Focus On
Security principles is the biggest domain and it's also the one people overprepare for. You don't need to know every framework detail. Focus on the CIA triad, risk management fundamentals, security policies, and the difference between detective, preventive, and corrective controls. Also understand what cryptography actually does at a basic level. You'll get questions about encryption types, but they won't ask you to derive keys or run algorithms. They want to know whether you understand symmetric versus asymmetric in practical terms. Business continuity is smaller but easy to lose points on because the terminology overlaps. Know the difference between BCP, DRP, and continuity planning. Understand RTO, RPO, and MTD. These acronyms show up repeatedly and mixing them up costs marks. I once saw someone on a forum argue that RTO and RPO were the same thing. They're not. RTO is how quickly you need to be back online. RPO is how much data loss you can tolerate. Getting those wrong changes your entire backup and recovery strategy. Access control concepts sounds technical but the exam treats it at a conceptual level. Know the difference between discretionary, mandatory, and role-based access control. Understand what least privilege means in practice. You should also recognize what a firewall, IDS, and DLP do at a high level. You won't be configuring any of them. The question will describe a scenario and ask which control type applies.
Get the Full Details

Incident response principles is the last domain and it's straightforward if you know the NIST incident response lifecycle. Containment, eradication, recovery, and post-incident activity. The exam likes to test whether you know the correct order of operations. A common trap is choosing eradication before containment. If you eradicate without containing first, you're just cleaning up a spreading problem. That's a wrong answer on the real exam.
Common Mistakes People Make With Their Study Guide
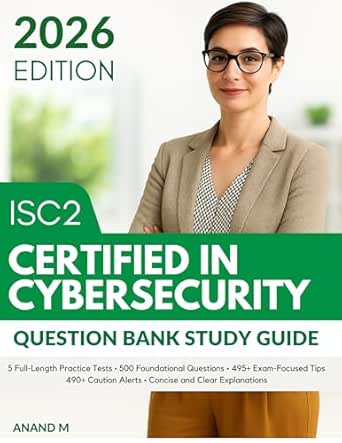
Reading passively is the biggest one. Going through the guide like a novel without taking notes or testing yourself is a waste of time. The material is simple enough that passive reading gives you a false sense of competence. You think you know it because the words look familiar. They won't help you when the question is worded differently. Another mistake is ignoring the practice questions. Some people treat them as an afterthought. Practice questions are where you find out what you don't know. If your guide has 500 questions, do at least 300 of them before the exam. Read every explanation, even the ones for questions you got right. You'll pick up nuances that way. There's also a trend of relying too heavily on dump sites. I won't name any, but they exist. Using them won't help you learn anything and ISC2 actively monitors for compromised questions. If the exam changes frequently, that's partly because they retire questions that leak. Studying from dumps is a bad investment of time and it doesn't reflect actual exam difficulty.
What to Do Right Before the Exam
Don't try to learn new material the week of the test. You're just adding stress without real retention gains. Instead, review your handwritten notes and redo the practice questions you got wrong the first time. Your brain needs consolidation, not new input at that point. Sleep matters more than people admit. The CC exam is 45 to 90 minutes depending on the version. You'll see around 100 to 150 questions. You need to read carefully under time pressure, and fatigue makes you miss details in the question stem. I used to pull all-nighters before exams thinking I was being productive. That strategy backfires. One extra hour of sleep is worth more than one extra hour of cramming.
A Note on What This Guide Won't Do For You
No study guide guarantees a pass. The ISC2 CC is designed to be fair, which means the questions can feel unpredictable. There's no shortcut around doing the work. If you've only read the guide once and scored below 60 percent on practice exams, you need more time, not a different resource. The gap is usually in applying concepts to scenarios, not in knowing definitions. Scenarios are where the exam separates people who understood the material from people who memorized it. Use the guide as a map, not a destination. The official outline, practice questions, and your own notes should carry you through. Everything else is noise.