How to Actually Use the Isc2 Cissp Exam Outline Without Losing Your Mind
The CISSP exam isn't a knowledge test. It's a judgment test. That distinction matters more than anyone admits, because it changes everything about how you should approach your study materials. I spent six months preparing for my first attempt and bombed it on the questions that looked easy. The questions that killed me were the ones where I knew the textbook answer but couldn't figure out what the question was actually asking. The official
Isc2 Cissp Exam Outline
is a 15-page document that most people treat like a checklist. It isn't. It's a mapping of the domain weightings that determine your entire score distribution. You need to understand the domains, but more importantly, you need to understand how ISC2 constructs the questions within those domains. The gap between knowing the material and passing the exam is entirely about learning the test's logic. Here's what happens when you actually sit down with the outline and try to use it as a study tool. Domain 1 covers Security and Risk Management at 15 percent. Domain 2 is Asset Security at 10 percent. Domain 3, Security Architecture and Engineering, is 13 percent. Domain 4 is Identity and Access Management at 13 percent. Domain 5, Security Operations, carries the largest chunk at 13 percent. Domain 6, Software Development Security, is the smallest at 10 percent. Domains 7 and 8 split the remaining 26 percent roughly evenly across the exam. These percentages don't change year to year in any meaningful way, but they do tell you where to invest your time if you're short on hours.I've seen people spend three weeks on software development security and then skimp on security operations, which is the exact wrong trade. Security operations is where the bulk of the operational mindset questions live, and those are the hardest ones to get right if you haven't internalized theISC2 perspective. The exam doesn't care what you think is most important in the real world. It cares whether you can think like a manager who has already made a risk assessment decision and now needs to justify it. The first thing I'd recommend is downloading the current outline directly from the ISC2 website. It's free. There's no paid portal barrier. Once you have it, map every single topic under each domain to a study resource. Not the other way around. Most people buy a book or watch a video course and then try to figure out which domain it covers. That's backwards. Start with the domain, find the resource that covers it, and only move on when you can answer the practice questions in that domain at a 75 percent minimum rate. Practice questions are the single most important study tool you have, but only if you review the explanations for every wrong answer. I learned this the hard way during my first attempt. I was scoring 65 to 70 percent on practice exams from a major vendor and felt confident going in. I scored a 58 on the real exam. The problem wasn't that I didn't know the material. The problem was that I was answering questions based on what I thought was correct, not what ISC2 considers correct. These are two different things.
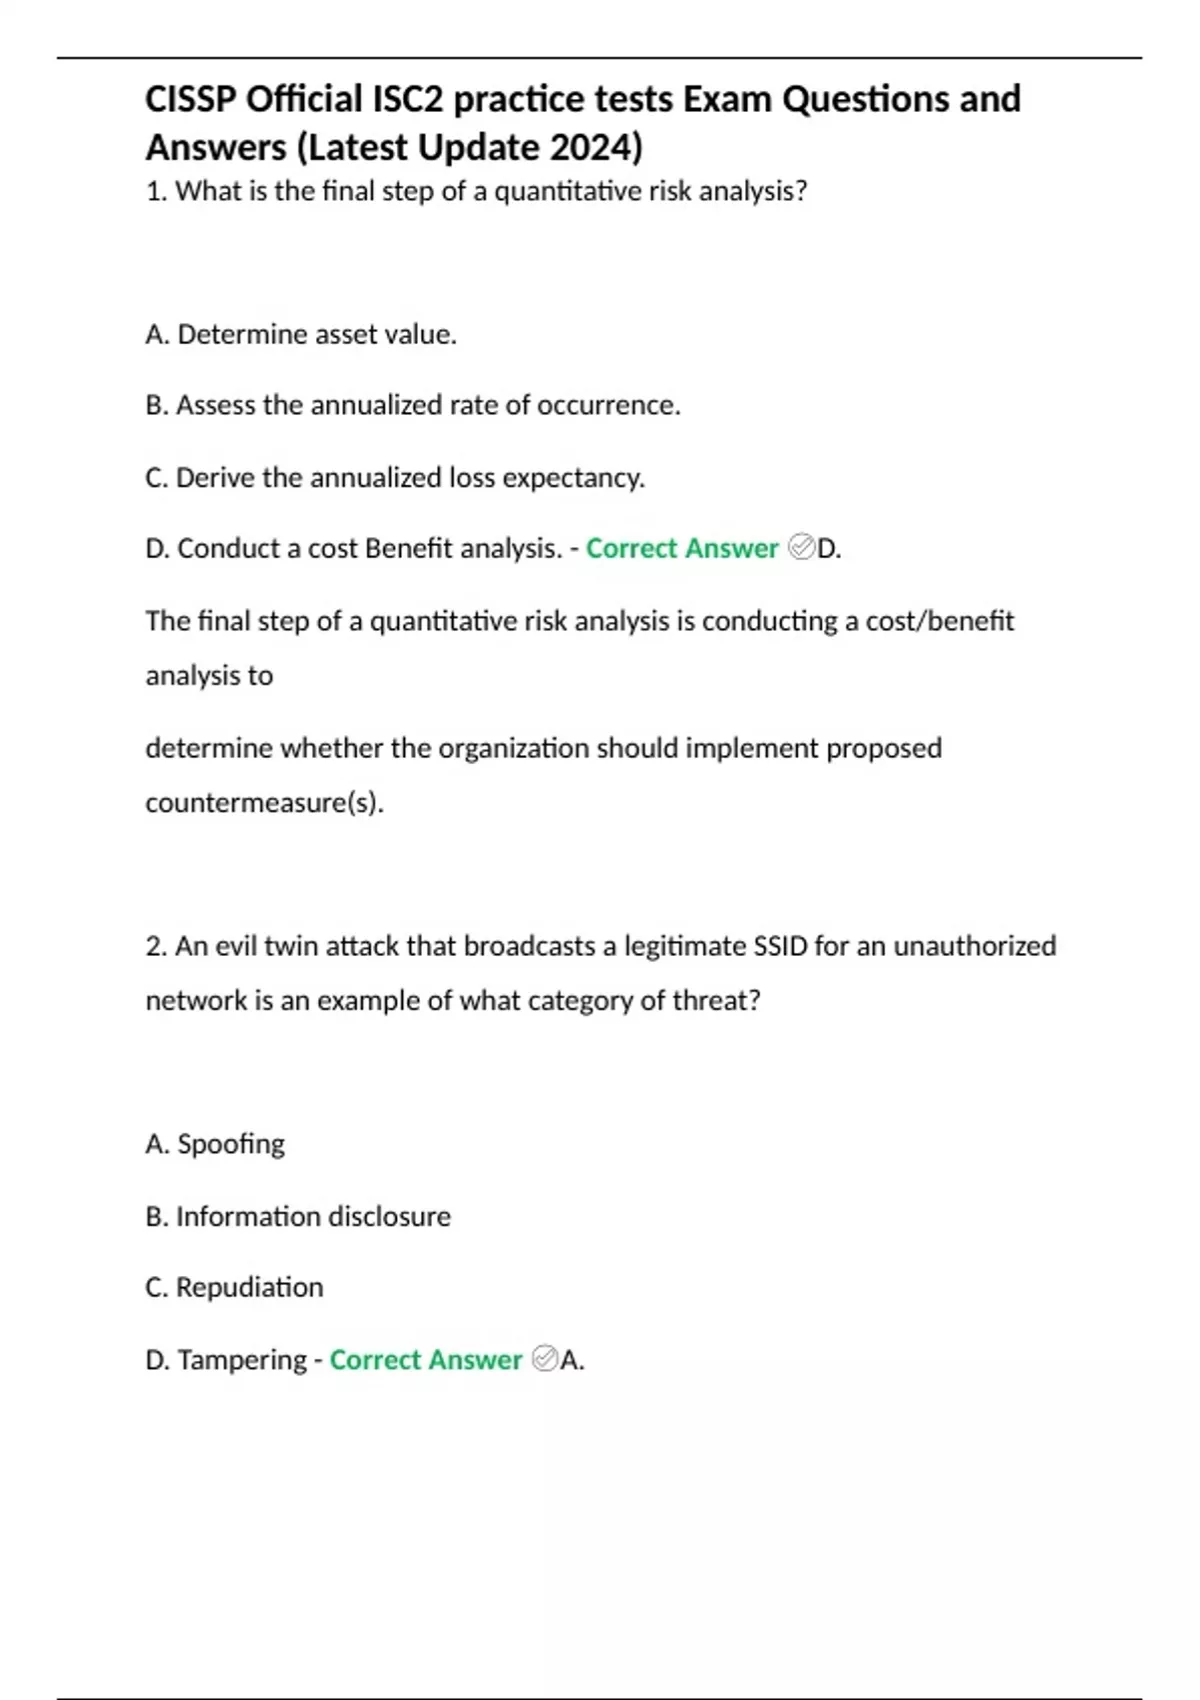
There's a specific edge case that caught me off guard and one I want to highlight because it comes up repeatedly. The exam will give you a scenario where multiple security controls seem appropriate. You might know that encryption is the right answer, but the question is asking about the first thing you should do. In those cases, the answer is almost never the technical control. It's always the process step that precedes it: identify the problem, assess the risk, consult policy, or escalate to the appropriate authority. I remember one question verbatim where the scenario described a data breach in progress and the correct answer was "notify the incident response team" rather than "contain the breach." The reasoning is that containment is an IR team function, not something an individual consultant or junior analyst should be initiating without the formal process. I got that one wrong and had to spend a full week reworking my mental model of the exam. Another common pitfall involves the terminology. ISC2 uses very specific definitions for terms like "risk," "threat," "vulnerability," and "impact." If you're coming from a technical background, you might define these loosely. The exam will penalize you for that. Risk is the combination of likelihood and impact. Threat is anything that could exploit a vulnerability. Vulnerability is a weakness. These definitions are simple but the questions around them are deliberately confusing. They'll describe a scenario that sounds like a threat and ask you to identify the vulnerability, or vice versa. Getting comfortable with the exact definitions early saves you from second-guessing yourself later. For study resources, I'd point you toward the Official CISSP Study Guide by Mike Chapple and David Hook, the Sybex study guide, and the Practical CISSP video courses from both Sean McNellis and Professor Messer. Messer's content is free and sufficient for most people. If you want something more structured, the CISA-style question banks from Pearson or the Boson practice exams are closer to the actual exam difficulty than most other vendors. I found the Boson questions to be the closest simulation of the real exam's tone and complexity. The explanations are detailed enough that you learn from each question, not just memorize the answer.
Get the Full Details
There's a tradeoff you need to be aware of with the CISSP framework. It's designed to be vendor-agnostic, which means it covers a very wide range of technologies at a surface level. This is intentional and good for a management-level certification, but it's a real limitation if you're studying purely from a technical perspective. You'll encounter questions about cloud security, network security, and application security without enough depth to feel satisfying. Don't fight it. The exam is testing your ability to make decisions with incomplete information, which is exactly what a security manager does daily. Accept the breadth-over-depth approach and move on. If you're working full-time and studying part-time, plan for three to four months minimum. I know people who compress it into six weeks, but those people either have prior CISSP-adjacent experience or they're studying full-time. The outline itself doesn't lie. Sixteen domains, approximately 100 to 150 scored questions, adaptive testing through CAT. You need a minimum of 700 out of 1000 points to pass. Every domain counts, but the higher-weight domains are where you'll make or break your score. One last thing that nobody tells you: the exam is long. Two hours for the CAT version, but the cognitive load is significant. By question 80 or so, you'll be fatigued. The questions get harder as you go, and your ability to think clearly degrades. I recommend doing full timed practice exams at least twice before the real thing, ideally back-to-back with no breaks, so your brain gets accustomed to maintaining focus under fatigue. This is practical advice, not motivational fluff. It made a measurable difference in my second attempt score.
Download the outline, map it to your resources, work the practice questions methodically, and don't assume that knowing the material is the same as knowing how to answer the questions. They're different skills. The exam tests the second one.