Getting through an ISO 13485 audit without losing your mind
Most companies treat the ISO 13485 Audit Checklist like it is a formality, something you fill out in a weekend and file away. It does not work that way. The checklist is the structural backbone of your audit, and if it is half-assed, the auditor will find it within the first hour. I spent seven years on the receiving end of these audits, both as an internal quality manager and later as an external auditor. The difference between a clean audit and a messy one almost always comes down to how thorough the checklist was before the auditor showed up.
Building the Iso 13485 Audit Checklist
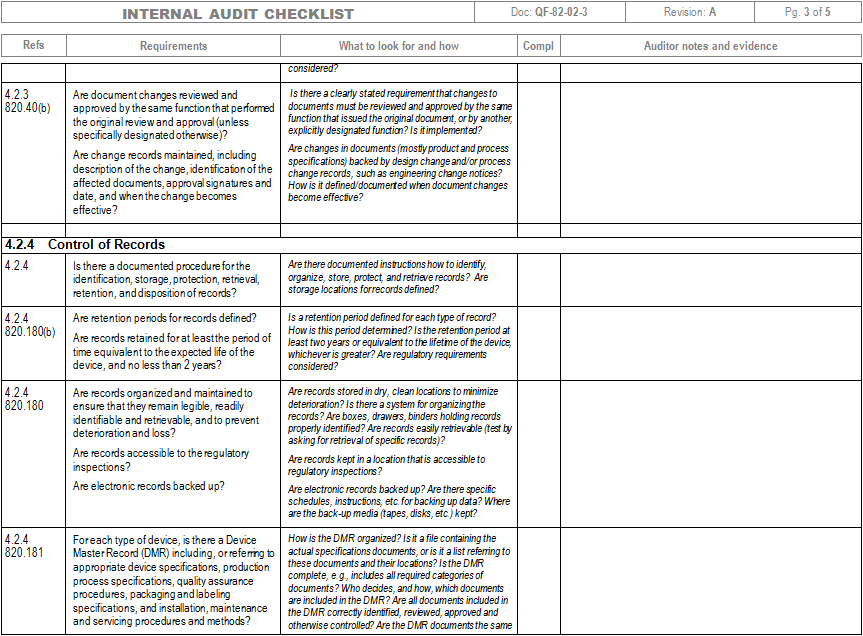
Start with the standard itself. ISO 13485:2016 has eight main clauses, and each one needs to be mapped to your actual processes. Do not just copy a template from the internet and call it done. Every template I have seen online assumes a generic medical device manufacturer, which means it will miss the specific nuances of your product line, your supply chain, or your market. Clause 4 covers the quality management system. This is where most companies fail first. Auditors will ask to see evidence that your QMS is documented, implemented, and maintained. A blank checklist here tells the auditor nothing. Fill it with references to your quality manual, your documented procedures, and the records they produce. Clause 5 is management responsibility. This clause gets short shrift in many checklists because people think it is about leadership rhetoric. It is not. It is about management review records, resource allocation decisions, and customer feedback analysis. I once watched an auditor spend forty-five minutes in this section alone because a company had management reviews that were essentially copy-pasted from the previous year with only the date changed. That is an easy trap to avoid. Make sure every management review record shows actual decisions, actual data, and actual actions taken.
Clause 6 is resource management. Your checklist should cover personnel competency records, infrastructure maintenance logs, and workplace environment controls. The common mistake here is forgetting about temporary or contract staff. If you use agency workers in your cleanroom, their training records need to be in the same system as your permanent employees. Auditors do not care about the distinction. Clause 7 is product realization. This is the biggest section and the one that eats the most audit time. It runs from design and development through production, servicing, and installation. Break it into sub-items. Design controls alone can account for hours of audit work if they are not properly documented. Your checklist should have a dedicated subsection for design and development planning, inputs, outputs, reviews, verification, validation, and transfers. Each one needs a specific document reference, not a general statement like "see design files." I ran into a problem once with a client who had a solid design history file but could not produce traceability between their design inputs and design outputs for a specific implant device. The auditor asked a simple question: show me where each requirement in your design input document was addressed in your design verification results. The traceability matrix existed in a shared folder that three different engineers had updated at different times, and the versions did not match. It took us two days to reconcile everything. The workaround was straightforward but painful. I had every engineer pull their working files, we created a single master traceability matrix in Excel with conditional formatting to flag mismatches, and we went through each input requirement line by line. It should have been done that way from the start.
Get the Full Details
Production and service provision under Clause 7.5 is another area where checklists tend to be vague. You need specific items: cleaning and disinfection procedures, sterilization validation records, equipment calibration, cleanroom monitoring data, and traceability during manufacturing. The sterile devices niche adds another layer with bioburden testing and endotoxin validation. If your checklist does not explicitly call these out, the auditor will assume they are not being managed. Clause 8 covers measurement, analysis, and improvement. Internal audits, corrective and preventive actions, and customer satisfaction data all live here. The most common pitfall I see is with CAPA. Companies will list "CAPA process exists" on their checklist but provide no evidence of actual CAPAs being closed out. An auditor wants to see a sample of opened CAPAs with their status, root cause analysis, effectiveness checks, and closure dates. Pull twenty recent CAPAs before the audit and verify each one is complete. This usually takes about three hours of work but prevents a major finding if the auditor decides to sample your CAPA file.
How to use the checklist effectively
A completed checklist is not the goal. The goal is to have a document that lets you walk an auditor through each clause systematically while providing evidence on demand. The best checklists I have used are living documents with version control, owner assignments, and evidence cross-references built into them. Use a spreadsheet format if you want something flexible, or a dedicated quality management software platform if your organization already has one. The format matters less than the discipline behind populating it. Each line item should have a responsible person, a document reference, a revision number, and an expiry date if the evidence is time-limited like a calibration certificate or an audit report. I recommend doing a full checklist review at least quarterly, not just before an external audit. Companies that treat it as an annual event always discover gaps on audit day. Quarterly reviews catch issues while there is still time to correct them without looking reactive.
One counter-intuitive insight that beginners miss: auditors do not expect perfection. They expect honesty and traceability. If your checklist flags a gap, disclose it. A minor nonconformity for a documented gap is infinitely better than a major finding for hiding a gap. I have seen companies lose a certificate over rather than over a procedural shortcoming. The data supports this. Major findings related to undeclared nonconformities result in immediate scope restrictions or certification withdrawal in roughly sixty percent of cases, while minor or major findings that are openly acknowledged typically result in a ninety-day corrective action window with certification maintained.

Limitations and what the checklist cannot do
An ISO 13485 Audit Checklist is not a substitute for an actual quality management system. It is a tool for preparation and evidence tracking. It cannot verify that your processes are effective, only that they are documented and referenced. It cannot predict what an individual auditor will choose to focus on during a two-day audit. Two auditors can look at the same company and produce completely different findings based on their experience, their mood, and the specific sample size they choose. The checklist also breaks down in organizations with multiple sites or complex supply chains. A single master checklist becomes unwieldy and difficult to maintain. In those cases, I recommend site-specific checklists linked to a master index rather than one massive document. The coordination overhead is higher, but the accuracy improves significantly. If you are a small manufacturer with limited resources, consider engaging a consultant for the initial checklist build. A one-time investment of two to three thousand dollars can save you weeks of internal effort and prevent costly audit failures. Do not skimp on this step. A poorly constructed checklist is worse than no checklist because it creates a false sense of readiness.
Practical steps for implementation
Map each ISO 13485 clause to your documented procedures. Verify that every procedure has an owner, a current revision, and accessible evidence. Cross-reference design controls, risk management, and CAPA as priority areas. Run a mock audit using the checklist before the real one. Assign someone who is not involved in day-to-day operations to conduct it, preferably someone with auditor experience. Their findings will differ from yours, and that difference is where the real value lies. Document everything. The checklist itself should be a controlled document with version history. When you update a line item, record what changed, why it changed, and who approved the change. Auditors notice when a checklist looks recently edited, especially if the edit dates cluster right before the audit. Spreadsheets with locked cells and protected sheets help prevent accidental or suspicious-looking modifications. The whole process typically takes a mid-sized medical device company between forty and eighty hours for an initial build, assuming all documentation already exists. If your QMS is fragmented or undocumented, budget two to three months and significantly more effort. There is no shortcut around that reality.