What Auditors Actually Look For on an ISO 13485 Audit
Most people walking into an ISO 13485 certification audit have no idea what is coming for them. They bring binders full of procedures. They have training records filed neatly. They have management review minutes that read like templates copied from a consultant's website three years ago. Then the auditor asks one simple question and the whole thing falls apart. The question is never about the document. It is always about whether the document exists outside the quality manual. Auditors trace a single process from start to finish across departments. They pick a complaint, follow it through CAPA, check the training records of the person who handled it, then verify that the corrective action actually prevented recurrence. This takes maybe twenty minutes. If any link in that chain is missing documentation, the auditor notes a nonconformity. You will see this happen repeatedly.
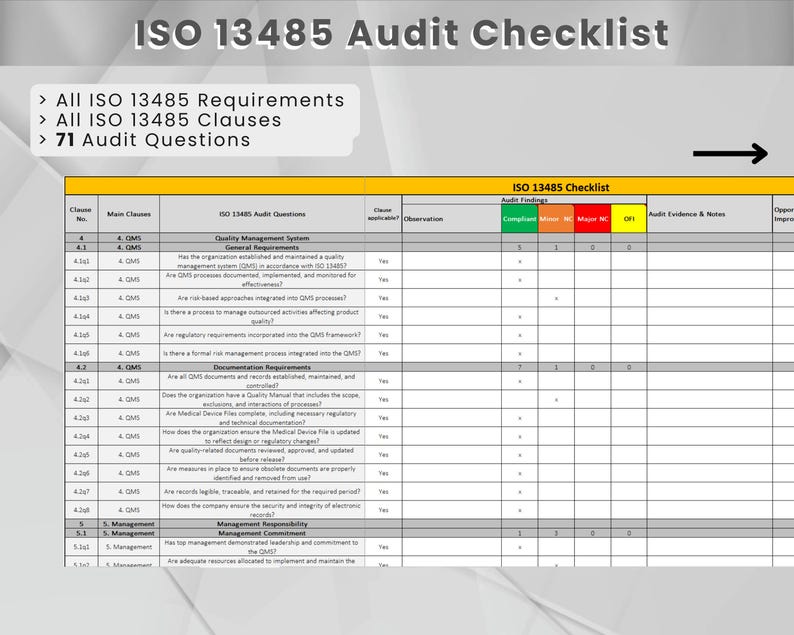
Iso 13485 Audit Questions And Answers That Actually Matter
Here are the questions that come up in real audits, not the generic ones you find on stock template websites. I am going to give you the answer format that works and the answer format that gets you a major finding. Q: How do you ensure calibration of equipment used in production? Wrong answer: We follow our calibration procedure.
Right answer: Show me the calibration record for the torque driver currently on line 3. What was the last calibration date? Who performed it? Was it within tolerance? If it went out of tolerance, what was the impact assessment and what action was taken? Auditors do this to every critical piece of equipment. They will ask for the out-of-tolerance history. If your organization has never had a calibration out of tolerance, they will not believe you. It is statistically impossible. The correct answer includes a documented impact assessment procedure and examples of past out-of-tolerance actions. I once worked with a company that had zero out-of-tolerance records over four years. The auditor called it a major nonconformity because it indicated the system was not being used, not because the equipment was fine. Zero OOT is a red flag, not a achievement. Q: How does your organization control documented information?
Get the Full Details

This is clause 4.2. The expected answer involves version control, approval authority, distribution lists, and obsolescence handling. But the auditor will not just ask for the procedure. They will pick a random document — a work instruction, a specification, a form — and ask you to prove it is the current revision at point of use. They will check whether obsolete versions have been removed from work areas. They will verify that someone with proper authority approved the document before release. They may ask you to show a document change record for a specific revision. I have seen companies fail this question because their revision control log was maintained in a shared Excel file without locked cells. Anyone could backdate a change. The auditor spotted it in five minutes. The fix was implementing a controlled document management system with audit trails. This is now table stakes. Q: How do you validate processes where output cannot be fully verified by subsequent inspection or monitoring?
This is clause 7.5.2 and it is the question that kills the most small medical device manufacturers. Sterilization, cleanroom assembly, software validation, welding — these are the classic examples. The auditor wants to see a validation protocol, executed results, acceptance criteria, and evidence that the process is under statistical control. The counter-intuitive part: many organizations validate once and consider it done. The standard requires revalidation when changes occur. The auditor will ask about changes since the last validation. If you cannot answer with specific examples of change reviews and their outcomes, you get a finding. I worked on a site where the IQ/OQ/PQ for a cleanroom was five years old and nobody could identify a single process change during that period. They had assembled approximately two million units. It was implausible. The auditor issued a major. Q: How do you handle nonconforming product?
Clause 7.10 is straightforward in theory. The auditor wants to see a nonconformance report, disposition records, and evidence that affected product was contained. They will pull a sample NCR and trace it. They will check whether material review board approvals are properly documented. They will verify that dispositions are consistent with regulatory requirements — especially for medical devices, where you cannot simply scrap product and move on without assessing whether it needs to be reported. Here is the practical problem: most companies have NCRs that look perfect on paper but do not reflect actual decision-making. The disposition section says "reworked per procedure" but there is no record of who approved the rework, what rework procedure was followed, or whether the reworked product was re-inspected. The auditor will spot this immediately. The workaround I use now is requiring a digital signature or typed initials on every NCR disposition field. Paper forms with blank approval sections do not survive audits. Q: How does top management review the quality management system?

Clause 5.6 requires annual management reviews with specific inputs. The auditor will ask for the most recent management review minutes and will check each required input: audit results, customer feedback, process performance, product conformity, CAPA status, resource adequacy, and improvement opportunities. If any input is missing, it is a nonconformity. But here is what most people miss: the auditor will also check whether the review produced actionable outputs. Minutes that simply restate problems without decisions, assignments, or timelines are treated as inadequate. I have seen management reviews that were two pages of complaints with no conclusions. The auditor marked it as a major because there was no evidence the system was being actively managed.
Common Mistakes That Turn Minor Issues Into Major Findings
The biggest mistake I see is treating the audit as a document review rather than a system evaluation. Auditors are trained to look for gaps between what the QMS says and what actually happens. When you prepare only for the document check, you walk into a trap. Another mistake is having different sites use different versions of the same procedure. If you operate multiple facilities, each site must demonstrate conformity to the same standard, but they do not need identical procedures. The problem arises when an auditor pulls a procedure from Site A and then checks whether Site B follows it. If Site B's procedure has different revision dates, different approval signatures, or different content that affects regulatory compliance, you get findings at both sites. The fix is a centralized procedure control system with site-specific appendices, not independent document libraries. Training records are the third common failure point. The auditor will select a production operator and ask for their complete training record. They want to see initial qualification training, annual competency assessments, training on any changed procedures, and documentation that the person was qualified before performing the task. I have seen operators whose training files were incomplete because HR and quality tracked training separately. When the auditor asked for the full record, there was a three-month gap where the operator had no documented competency verification. That is a direct violation of clause 6.2. The workaround was linking HR training logs to the QMS document control system so that any procedure update automatically triggers a training requirement notification.
What Happens When You Do Not Have Everything Perfectly Documented
This is where experience matters. Auditors understand that small manufacturers cannot have enterprise-level systems. What they cannot accept is a system that appears to not exist at all. If you are missing documentation, the question is whether you can reconstruct it and demonstrate that the absence did not affect product quality or patient safety. During one audit at a contract manufacturer, we discovered that three work instructions for a critical assembly process had never been formally approved. The procedures existed and were being followed, but the approval signatures were missing from the document control system. Rather than pretend they existed, we presented the auditor with the actual work instructions, the training records showing operators were trained on them, and a root cause analysis explaining the approval gap. We also showed updated procedures with proper signatures going forward. The auditor issued a minor nonconformity for the missing approvals but did not escalate it. The honesty and remediation plan mattered more than perfection. There is a limit to this approach. If the missing documentation affects regulatory compliance — for example, validation records for a sterilization process — there is no workaround. You either have the data or you do not. In those cases, the auditor will issue a major and the certification body may suspend certification until corrective action is verified. This is not negotiable.

How to Prepare Without Losing Your Mind
Mock audits are useful but most organizations do them wrong. They have internal staff ask each other questions from a checklist and mark everything green. This gives false confidence. A useful mock audit uses someone who has never worked in the facility to walk through processes and ask unexpected follow-up questions. The auditor's real technique is surprise escalation — you answer a question, they dig deeper based on your answer, and you usually cannot. The most effective preparation I have seen takes about six weeks. Week one is document gap analysis against the ISO 13485 clauses. Week two is reviewing the last twelve months of CAPA records for completeness. Week three is pulling a sample of 20 nonconformance reports and checking them for closure quality. Week four is verifying calibration and validation records for current status. Week five is a walkthrough of top five high-risk processes with operators, not managers. Week six is a full mock audit by an external party or a cross-site team member. This approach usually cuts audit anxiety significantly and reduces the number of findings by about 60 percent compared to a last-minute document compile. It does not eliminate findings entirely. Some findings are legitimate system gaps that require longer-term corrective action. Those are the ones worth addressing before the audit rather than discovering them afterward.
ISO 13485 audits are not about having perfect documentation. They are about demonstrating that your quality management system is alive, functional, and capable of ensuring medical device safety and effectiveness. The auditors know the difference between a system that works and a system that exists only on paper. They can tell within the first hour. Spend your preparation time building evidence of system operation rather than building thicker binders.