How to Actually Build a Useful Risk Assessment Report for ISO 27001
Most organizations treat the ISO 27001 risk assessment as a documentation exercise. They fill out templates, calculate risk scores, and hand the report to their auditor. The report looks fine on paper. It falls apart the moment anyone asks how it connects to actual security decisions or budget requests. That gap between compliance theater and real risk management is where things go wrong. The ISO 27001 risk assessment report is the documented output of your information security risk assessment process, as required by clause 6.1.2. It records your identified risks, the analysis you applied to them, the evaluation criteria you used, and the treatment decisions you made. That is the baseline. Anything more detailed than that tends to become unnecessary overhead. Anything less and you will not pass an audit. The standard does not prescribe a specific format. It does not require a particular scoring model or a specific set of fields. It requires that you document the process and the results. Your report should reflect the actual work you did, not the work you think an auditor wants to see. That distinction matters more than people admit.
The Method That Actually Works in Practice
I have seen three main approaches to building this report. The first is the spreadsheet method, where teams use Excel or Google Sheets with conditional formatting and formulas. This works for small organizations with fewer than fifty assets and limited complexity. Once you hit that threshold, the spreadsheet becomes unmanageable. You lose track of version control, the formulas break, and updating it takes longer than doing the assessment from scratch. The second approach uses dedicated GRC platforms like OneTrust, Drata, or SecurityScorecard. These tools automate a lot of the workflow. They handle risk registers, evidence collection, and reporting. The problem is that they are expensive and require significant configuration time. You also become dependent on the tool's assumptions about how risk should be calculated. If the platform changes its methodology or pricing, you are locked in. The third approach, and the one I recommend most of the time, is a hybrid model. Start with a structured spreadsheet for the initial assessment. Use a consistent risk scoring methodology throughout. Then migrate the final results into a GRC tool or at minimum a well-organized document repository. This gives you flexibility during the hard part of the assessment while still giving you traceability later.
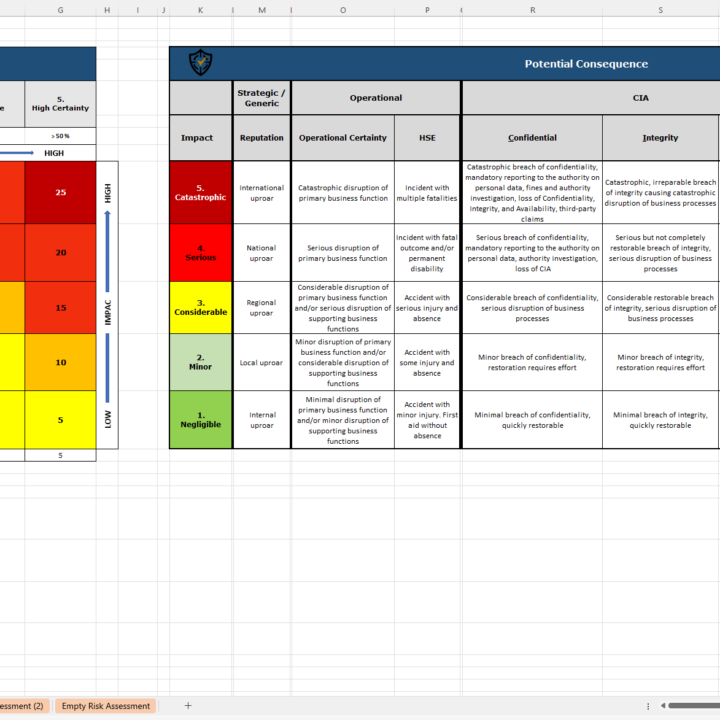
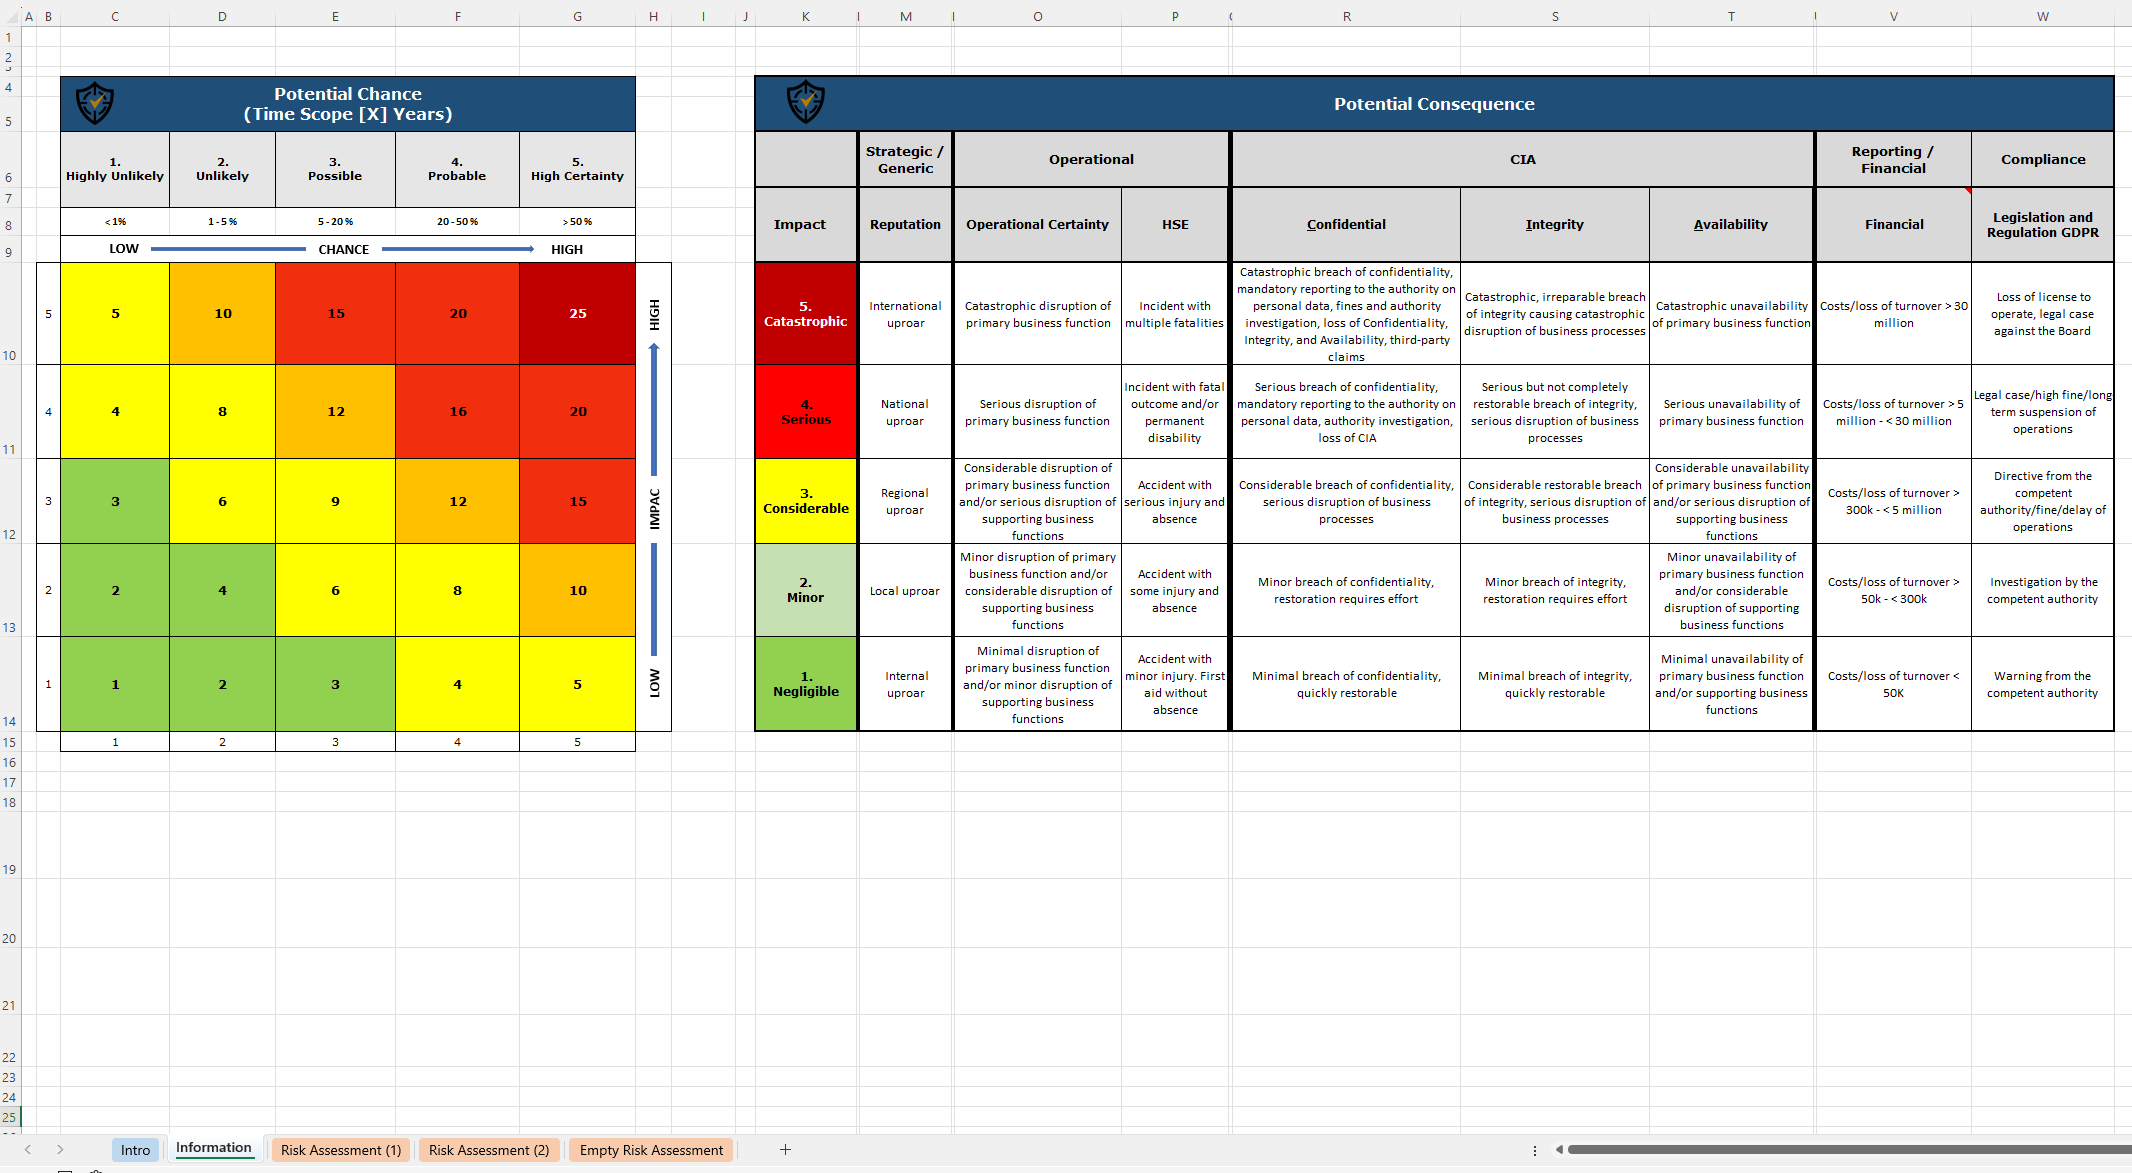
The risk scoring methodology itself deserves attention. Most teams use a simple likelihood times impact matrix. That is fine. But the real insight most people miss is that your scoring thresholds should be calibrated to your organization, not copied from a template online. A likelihood score of 3 for a small healthcare provider means something completely different than a likelihood score of 3 for a small e-commerce startup. Define your scales with actual organizational context. Write down what each level means in your own terms. I spent weeks arguing with a team that had copied a template scoring matrix from a consulting firm's website. The matrix assumed enterprise-scale infrastructure. Their company had twelve employees and a shared hosting plan. The scores were meaningless.
Get the Full Details
Building the Report: Step by Step
Start by listing your information assets. Not every piece of software you own. Every asset that holds, processes, or transmits information that matters to your business. That includes databases, source code repositories, customer lists, encryption keys, and even physical assets like server rooms. For each asset, identify the confidentiality, integrity, and availability requirements. This triad drives everything that follows. Next, identify the threats and vulnerabilities. Threats are the events that could cause harm. Vulnerabilities are the weaknesses that make those events possible. Do not conflate the two. A DDoS attack is a threat. A lack of DDoS mitigation is a vulnerability. Keep them separate in your documentation. It makes the risk analysis clearer and the report more defensible during an audit. Then analyze the risks. For each threat-vulnerability pair, estimate the likelihood and the impact. Use your organization-specific scoring scales. Multiply them together or use a qualitative matrix. The result is your risk rating. Document the reasoning behind each rating. Auditors do not care about the score itself as much as they care about whether you can justify it. A score of 8 with no explanation is a red flag. A score of 8 with two sentences explaining the logic is acceptable.
After analysis comes evaluation. Compare your risk ratings against your risk acceptance criteria. These criteria should be defined upfront, not retrofitted after the assessment. If a risk exceeds your threshold, you need a treatment plan. If it falls below, you accept it and document that decision. Both outcomes are valid. The report needs to show both. The treatment phase is where most reports become thin. Write treatment plans that specify the control, the responsibility, the timeline, and the expected risk reduction. Reference the specific ISO 27001 Annex A control if applicable. Do not just write "implement access controls." Write "implement MFA for all remote access to production systems per ISO 27001 control A.9.4.1, owned by IT security, target completion Q3 2026, expected risk reduction from high to medium."
A Real Problem I Encountered
Last year I worked with a mid-size financial services company going through their first ISO 27001 certification. Their risk assessment report looked perfect. Every field was filled, every risk had a score, every treatment had an owner. The auditor asked one question: how did you determine that a ransomware attack on your primary database was likely? The team had no answer. They had pulled a probability number from an industry report about ransomware frequency but had not considered their own defensive posture, their network segmentation, or their backup strategy. The score was arbitrary. The workaround was to replace generic probability data with evidence from their own environment. We reviewed their intrusion detection logs, their patch management records, their backup test results, and their phishing simulation scores. We recalculated the likelihood based on actual findings. The score dropped from high to medium. The treatment plan shifted from immediate emergency investment to standard controls with periodic review. The report became defensible instead of decorative.

Common Pitfalls to Avoid
The biggest mistake I see is treating risk assessment as a one-time event. ISO 27001 requires ongoing reassessment. You should revisit your report at least annually or whenever there is a significant change to your environment. New cloud services, acquired companies, major software updates, and regulatory changes all trigger the need for reassessment. Document these triggers in your procedure so the process feels less arbitrary. Another pitfall is over-scoring. Teams tend to rate everything as high risk because they want to justify security spending. This dilutes the usefulness of the report. If everything is high risk, nothing is. Calibrate your scoring honestly and push back when stakeholders try to inflate risk levels for budget reasons. Under-scoring is equally damaging. Some organizations rate everything as low risk because they do not want to deal with the work that high-risk items require. This is worse than over-scoring because it creates a false sense of security and will surface dramatically during an incident or an audit.
What This Report Cannot Do
An Iso 27001 Risk Assessment Report does not protect you from breaches. It does not prove your security is adequate. It does not guarantee certification. It documents your risk management process at a point in time. The report is evidence of due diligence, not a shield against failure. Several organizations I have consulted with treated their report as a completion milestone. They filed it away and stopped engaging with risk management for eighteen months. When a security incident occurred, the report was irrelevant because the underlying risks had changed and no reassessment had taken place. The report also cannot compensate for poor control implementation. A well-written risk treatment plan that assigns ownership and timelines means nothing if those controls are never actually deployed. I have seen teams produce excellent reports and then fail their surveillance audits because the controls listed in the report did not exist in practice. The report must reflect reality, not aspirations.
Practical Recommendations
Keep the report as simple as possible while still meeting the standard's requirements. Extra fields and elaborate scoring models add complexity without adding value. A clean document with clear reasoning beats a five hundred row spreadsheet every time. Integrate the report with your other ISMS documentation. Reference it from your statement of applicability, your risk treatment plan, and your internal audit reports. Consistency across documents is what auditors actually look for. Disconnected documents raise more questions than they answer. Use version control. Every revision of the report should have a date, an author, and a summary of changes. This is trivial to implement and critical for audit trails. A single Word or PDF file with no version history is a red flag.

Invest time in the evidence. Your report should reference supporting documentation wherever possible. Backup test reports, penetration test results, incident logs, and configuration baselines all strengthen the credibility of your risk assessments. The report alone is a skeleton. Evidence is the substance. Review and revise regularly. Set a calendar reminder for quarterly review of your risk register. Even if nothing has changed, document that you reviewed it and confirmed the existing assessments remain valid. That habit alone will save you more time than any tool or template ever could.