How to actually fill out an ISO 27001 risk assessment without losing your mind
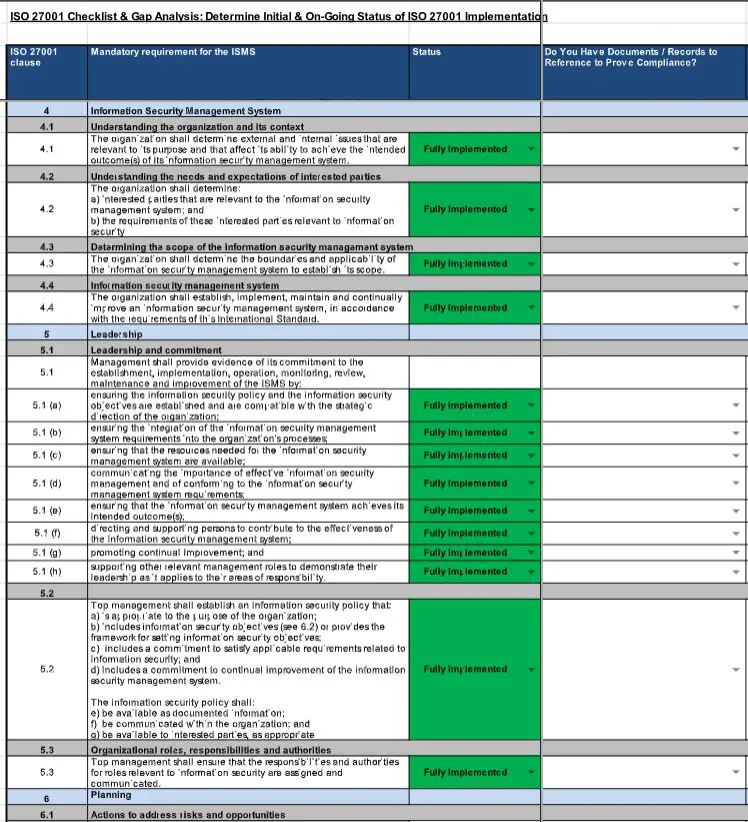
Most people approach this task wrong. They open a blank spreadsheet and try to assess everything at once. That's how you end up with a 200-row document nobody reads and a certifier who asks questions you already answered three times. I learned this the hard way during my first ISMS implementation in 2019. We spent six weeks building this enormous risk register that was fundamentally useless because we hadn't scoped the information assets properly first. The key insight nobody tells you is that ISO 27001:2022 clause 6.1.2 doesn't require you to assess every single thing in your organization. It requires you to assess assets within the scope of your ISMS. Define that scope first. Write it down. Then only bring things inside that boundary into your risk assessment. This alone cut our initial draft from three weeks to about four days.
The practical workflow
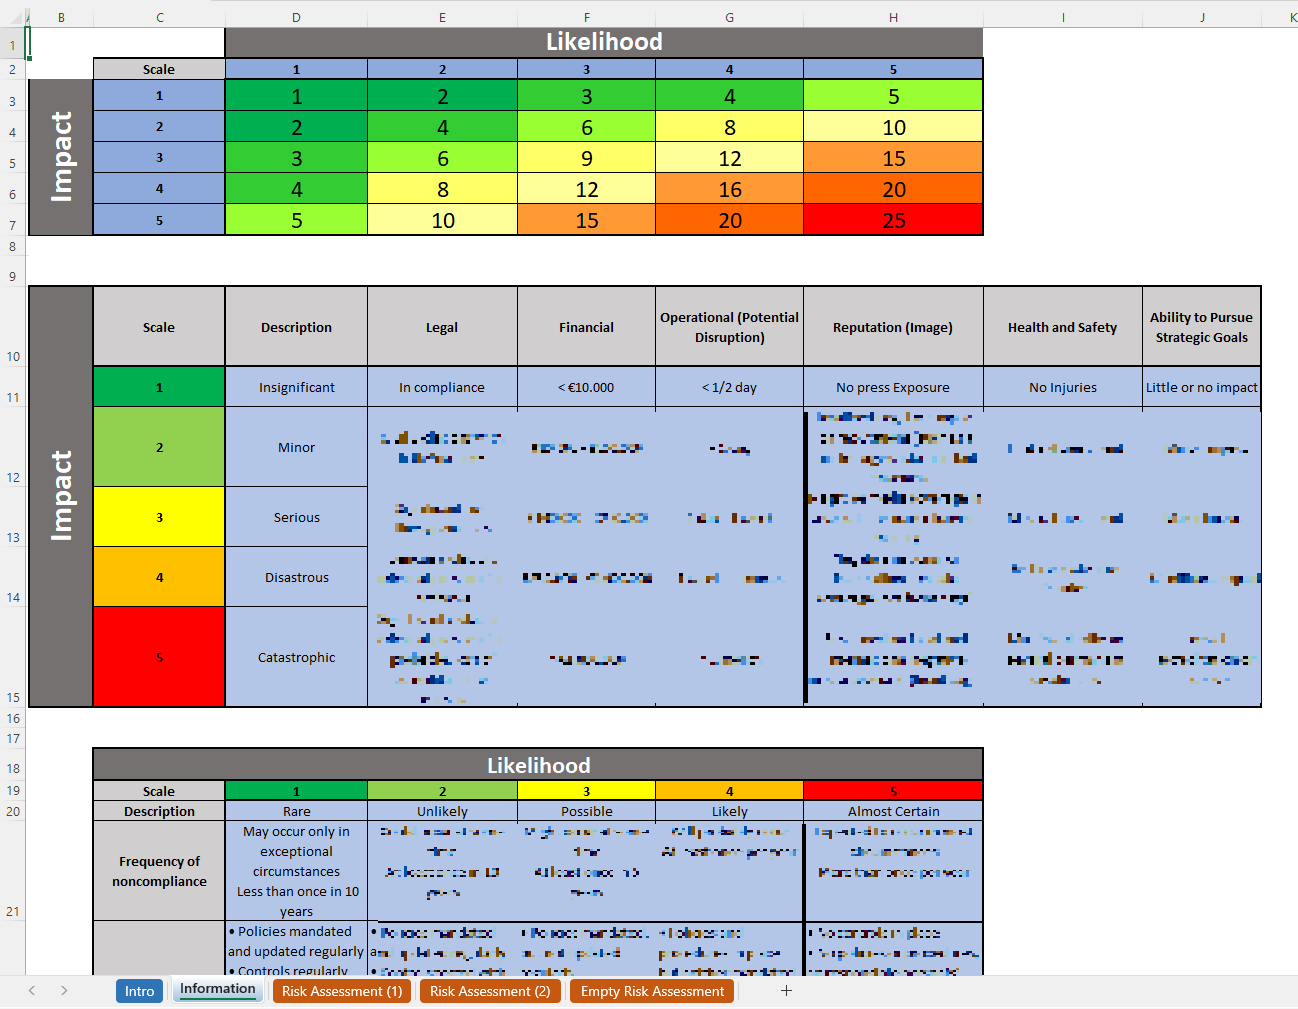
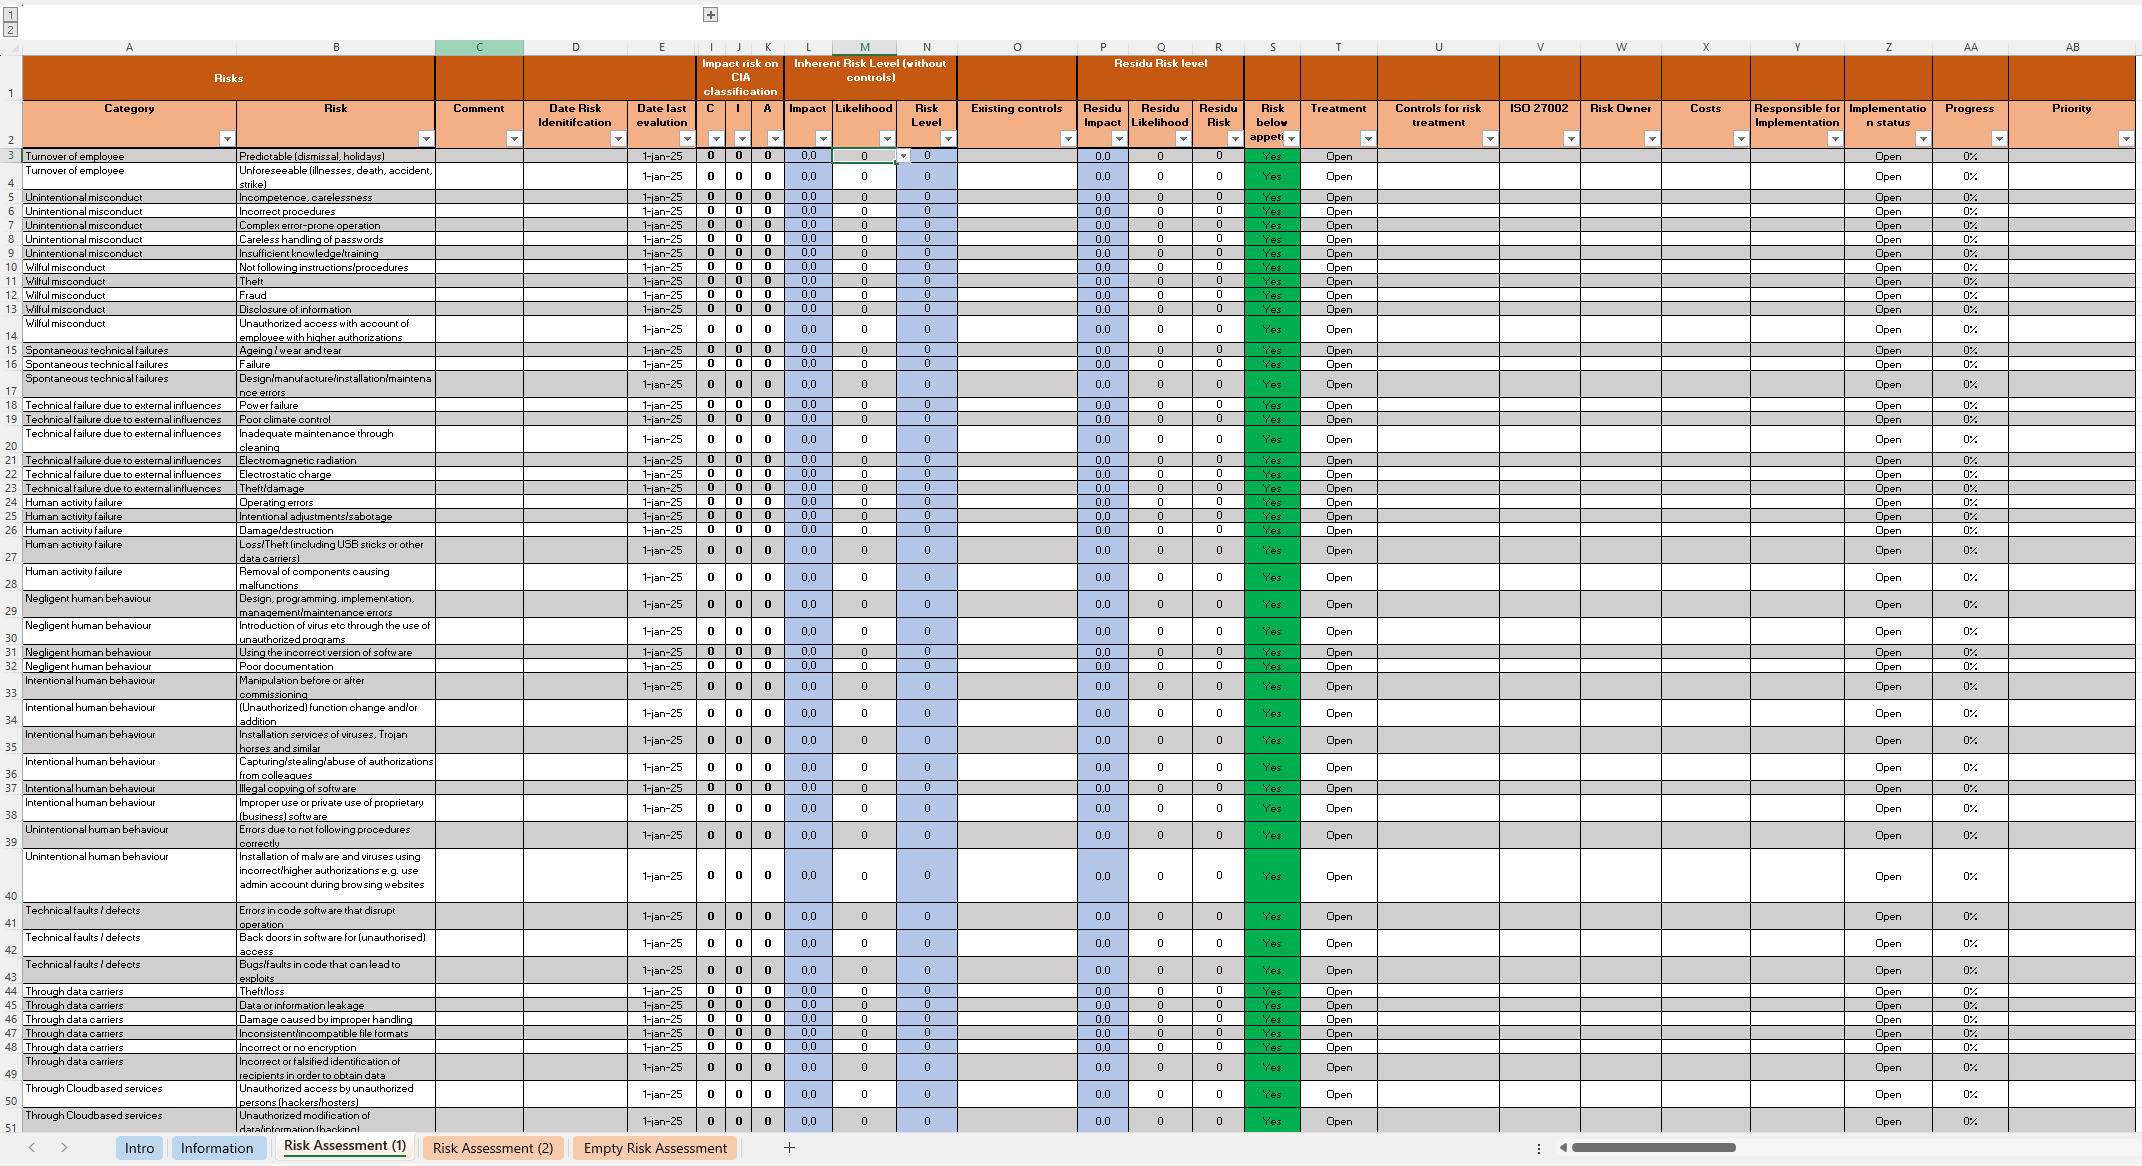
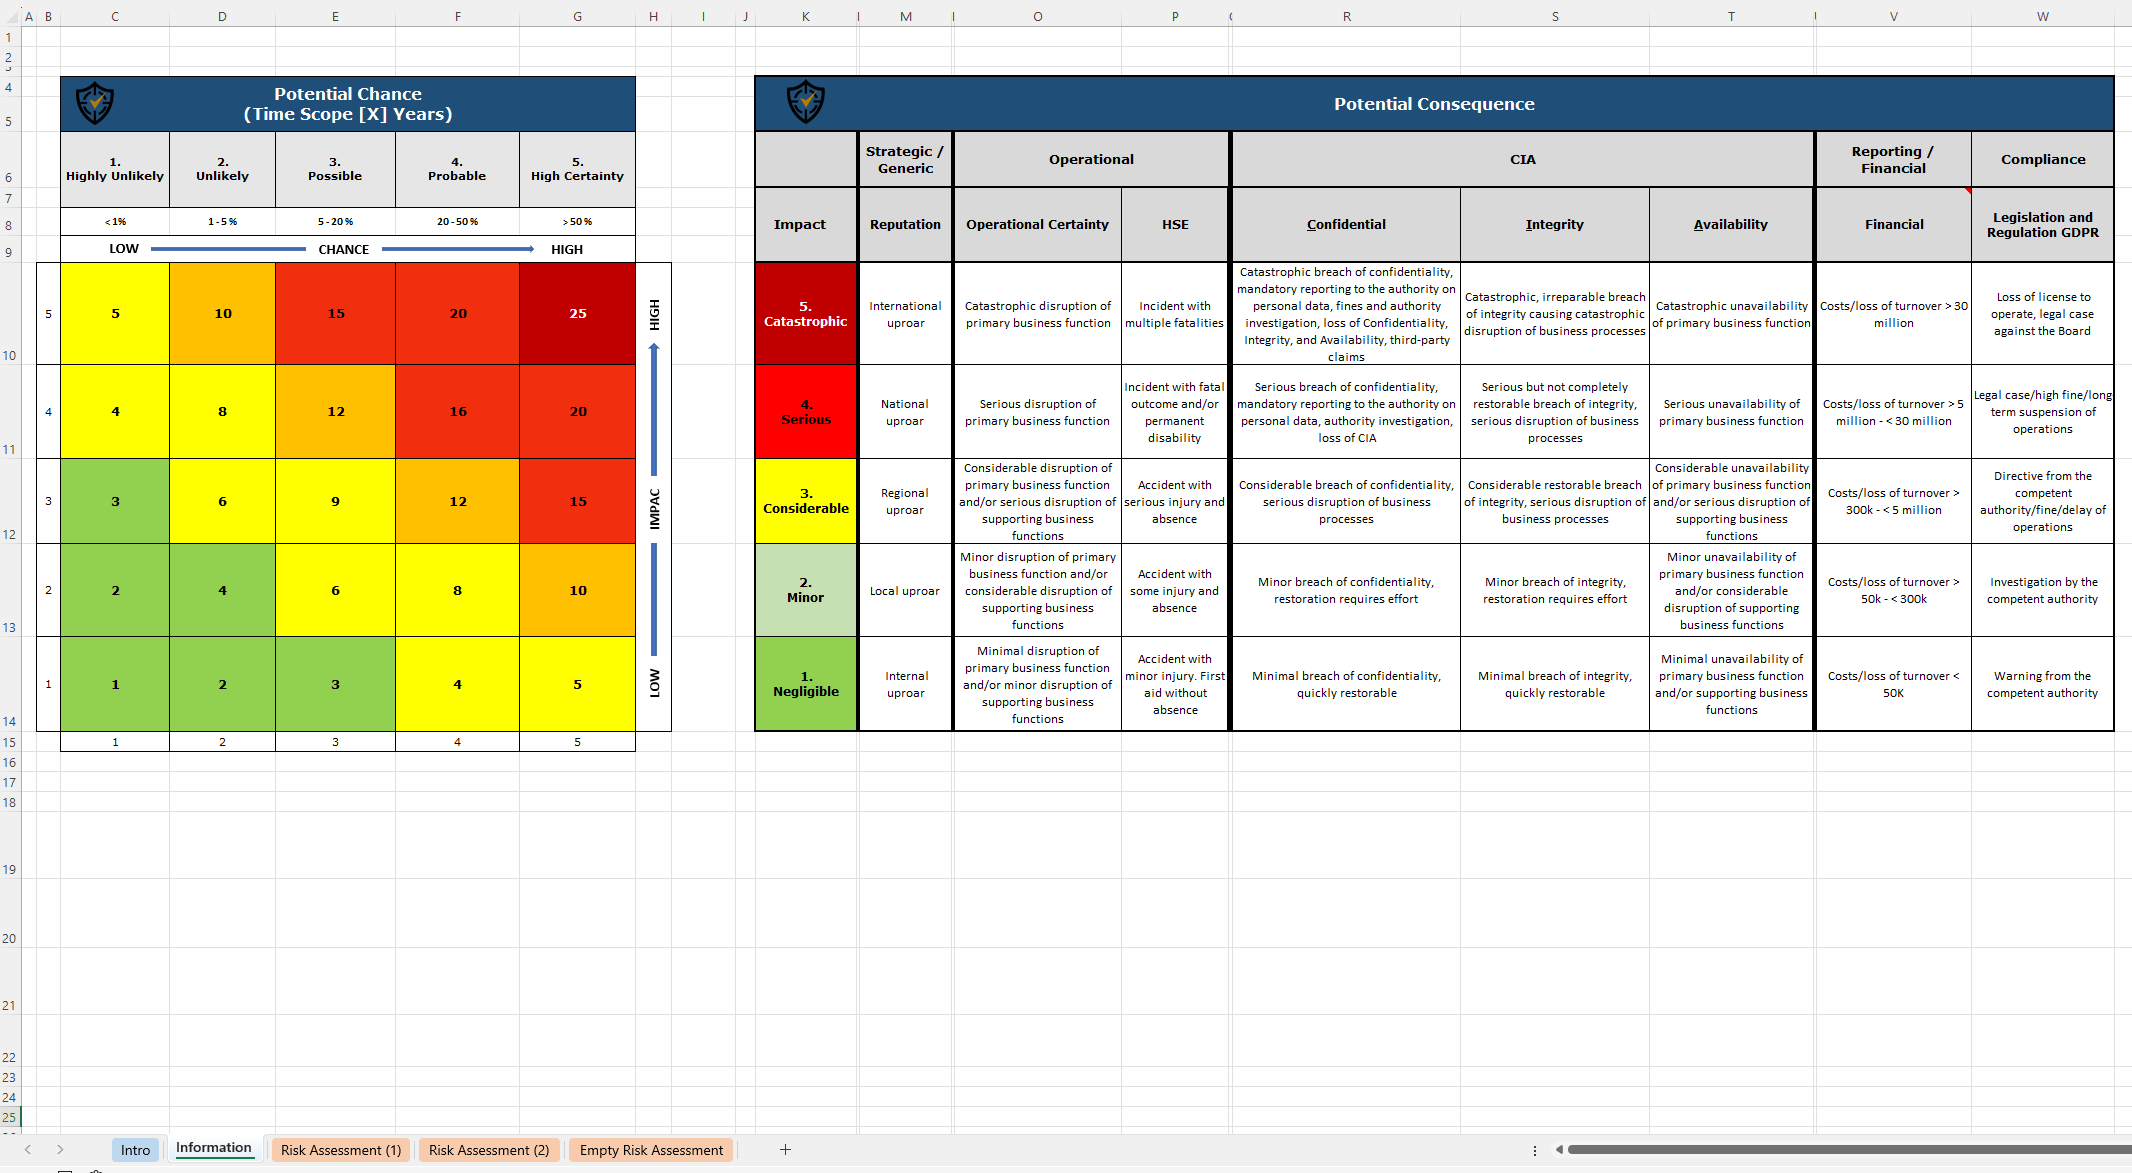
Start with asset identification. Not risk. Assets. List what you're protecting: customer databases, source code repositories, employee PII, VPN infrastructure, third-party payment processors. For each asset, assign a value based on confidentiality, integrity, and availability requirements. Be specific about the business impact. "System down" means nothing. "Payment processing halted for 4 hours resulting in €12,000 in lost transactions and SLA penalties" means something. Next, identify threats and vulnerabilities for each asset. Threats are external or internal events that could cause harm. Vulnerabilities are weaknesses that threats exploit. Don't conflate them. A brute force attack is a threat. Lack of account lockout policy is a vulnerability. Using a free Iso 27001 Risk Assessment Template Free format helps keep these columns distinct because the structure forces you to separate them rather than blur them together. Then calculate risk levels. The standard doesn't prescribe a specific mathematical formula, which confuses people. Most organizations use a simple 5x5 matrix: likelihood (1-5) times impact (1-5). This gives you risk scores from 1 to 25. Anything above 12 typically requires treatment. Below that sits in your risk acceptance register and gets reviewed annually. Simple, defensible, and what every auditor expects to see.
The edge case that trips everyone up
Here's something I've seen cause problems repeatedly: third-party risk assessments. Your ISMS scope probably includes cloud providers, managed service providers, and vendors who process data on your behalf. Clause 8.1.2 requires you to address these in your risk assessment. The template you're using needs a column for "third party" as an asset category, not just as a note in the vulnerability field. I encountered a specific problem during a SOC 2 audit where the assessor rejected our risk register because we had listed AWS as a vendor in the assets column but hadn't independently assessed their controls. We'd relied entirely on their SOC 2 Type II report without documenting that reliance. The workaround was straightforward: add a "reliance on third-party certification" column and reference the specific attestation reports. We also mapped our data flows through AWS to show the assessor we understood the actual exposure, not just that we'd read their marketing page.
Get the Full Details
What your template should actually contain
A functional ISO 27001 risk assessment template has these columns at minimum: Asset name and description. Be concrete. "Production database server" not "IT infrastructure." Asset owner. Someone who can answer questions about it. If the answer is "the company," that's a red flag.
Confidentiality, integrity, availability ratings. Use LOW, MEDIUM, HIGH consistently. Don't mix scales. Threat scenarios. Write these as complete sentences describing the event. "Insider exfiltrates customer data via unauthorized USB device" is better than just "data theft." Vulnerabilities. The specific weakness that enables the threat. "No DLP solution deployed," "No USB port blocking policy," "Employees not trained on data handling procedures."
Risk score. Likelihood times impact. Treatment option. One of four choices: mitigate, transfer, avoid, or accept. If you're accepting risk, document why. "Cost of mitigation exceeds potential loss" needs actual numbers to be credible. Remaining risk after treatment. This is where most people fail. Calculate what the risk score becomes after your controls are applied. The gap between inherent risk and residual risk is what demonstrates the effectiveness of your ISMS.
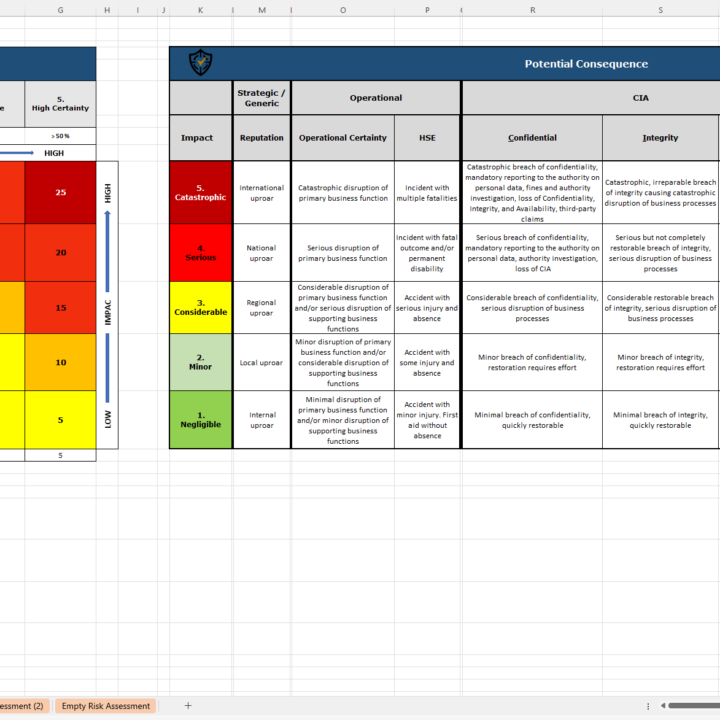
Control reference. Link to your Statement of Applicability. Each risk treatment should map to one or more controls from Annex A. Don't just write "implement firewall." Write "Control A.8.22 - Network security."
Common mistakes that waste weeks
The biggest mistake I see is treating the risk assessment as a one-time exercise. ISO 27001 requires periodic reviews. Clause 6.1.2 says you need to consider changes and at planned intervals. In practice, that means re-running your assessment whenever there's a material change: new system deployed, new regulation, breach incident, major org restructuring. Most organizations do this annually, which is acceptable, but the annual review often becomes a ritual where people just copy last year's scores without actually re-evaluating. That's not compliance. That's fraud with extra steps. Another issue is over-assessing. I've seen teams put 300+ risk entries into a register for a company of 50 people with minimal IT infrastructure. The auditors can tell when you're padding the document. Quality over quantity. 40 well-reasoned risk assessments beat 300 copy-pasted ones every time. Underestimating likelihood is also common. People rate threats as "rare" because they've never happened internally. But the threat landscape isn't defined by your history. Ransomware was "rare" in your industry until it wasn't. Use industry data, not just your own experience. The National Cyber Security Centre publications, ENISA threat landscape reports, and sector-specific ISAC bulletins give you baseline likelihood data that's more credible than gut feelings.
Building or downloading a working template
You don't need to build this from scratch. Search for an Iso 27001 Risk Assessment Template Free resource, but don't just download anything you find. Check that it covers the columns I listed above. If it's missing a "remaining risk" column or a "control reference" field, it won't survive an audit. The free templates from government bodies tend to be more complete than random blog downloads. UK NCSC, Australian Cyber Security Centre, and ENISA all publish templates that align with the standard's requirements. Once you have your template populated, run it through a test. Pick ten risk entries and explain each one to a colleague who has no context about your business. If they can't understand the risk, the entry is inadequate. Rewrite until it's clear. This takes maybe twenty minutes but saves days of auditor follow-up questions. The whole process, from blank template to audit-ready risk register, typically takes a small team 2-3 weeks if they're doing it properly for the first time. If you've done it before and have a validated template, 3-5 days is realistic. Anything faster usually means you're cutting corners on scope definition or likelihood analysis.