What You Actually Need to Know About ISO 9001:2015 Audits
Most people approach ISO 9001:2015 audits wrong. They treat them like a checklist to survive rather than a tool to understand their own operations. I spent six years doing internal and external audits across manufacturing, construction, and service sectors. The ones that actually work don't rely on memorized question banks. They rely on understanding what the standard is asking for and being able to trace evidence. Let me be straight about something nobody tells you: there is no universal set of "audit questions and answers." The standard is principle-based, not prescriptive. If an auditor gives you a generic list and expects uniform answers, you are either being poorly audited or preparing for an audit that will miss the actual nonconformities in your system.
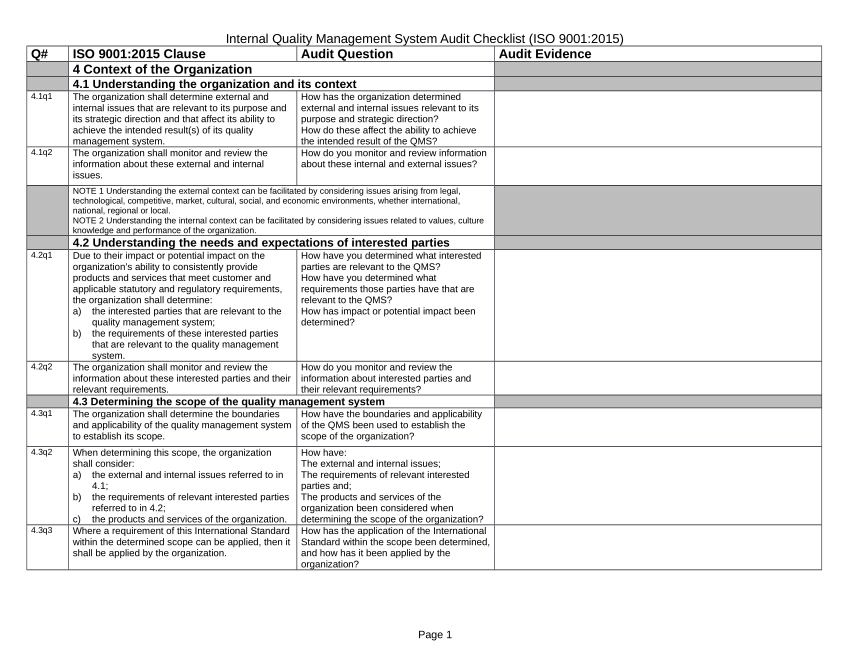
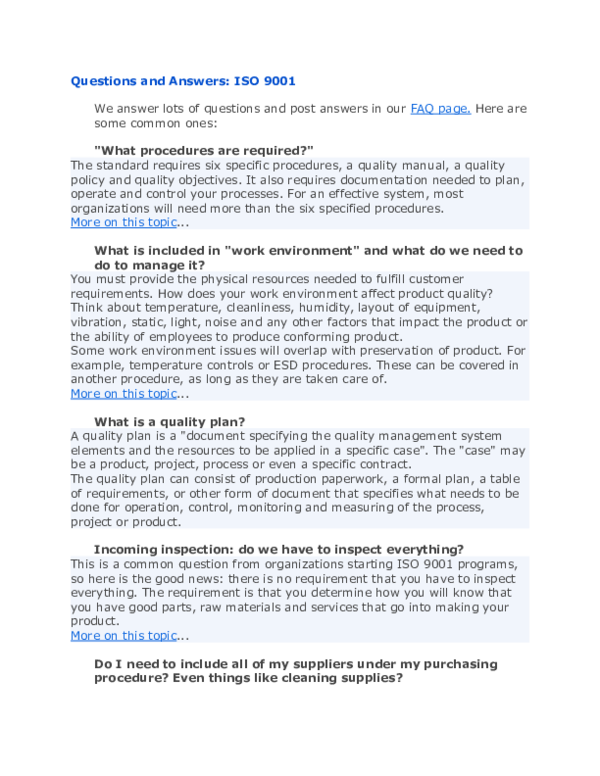
How to Build Your Own Iso 9001 2015 Audit Questions And Answers
The practical approach starts with clause mapping. Go through the standard clause by clause. For each requirement, write down one question that probes whether the requirement exists in your organization, and then write down what evidence you would need to confirm it. That evidence is where most people fail. Here is the clause-by-clause breakdown that actually works in practice: Clause 4 — Context of the Organization: Ask who the relevant stakeholders are and what their requirements are. The answer must reference documented information. I have seen organizations claim they performed a context analysis while producing zero documents from that exercise. That is an automatic nonconformity waiting to happen.
Clause 5 — Leadership: Focus on top management's demonstrated involvement. The standard does not accept "our quality manager handles this." You need evidence of management review meetings with actual records, documented quality policy communication, and role assignment records. During an audit at a mid-sized machine shop in 2019, the auditor asked about leadership commitment and the general manager pointed to a laminated quality policy on the breakroom wall. That was cited as a minor nonconformity under Clause 5.1. The workaround was to establish quarterly recorded management reviews with actionable output documented in writing, not just a signature sheet. Clause 6 — Planning: This is where risk-based thinking lives. The question is not whether you identified risks. The question is whether your actions to address those risks are proportionate to the potential impact. A common failure I see is organizations producing elaborate risk registers with fifty entries and zero prioritization. The auditor will ask how you determined which risks matter most and what you did about them. If your answer is "we listed them all equally," you are already in trouble. Clause 7 — Support: Resource adequacy, competence records, awareness, and documented information control. For competence, you need evidence of training, qualification assessment, and ongoing evaluation. For documented information, you need version control, change tracking, and access management. Do not confuse this with IT documentation systems. Clause 7.5 is about controlling your quality management system documents and records specifically.
Get the Full Details
Clause 8 — Operation: This is the biggest clause and the one that produces the most findings. Product and service requirements, design and development controls, external provider management, production control, and release criteria. Each sub-clause needs specific questions. For design and development, ask about planning, inputs, controls, and outputs with verification and validation evidence. For external providers, ask about evaluation criteria and ongoing monitoring. I once worked through a situation where a client's sole supplier for a critical component went bankrupt without notice. The organization had no clause 8.4 evaluation records because they treated the supplier relationship as informal. That became a major nonconformity during certification surveillance. Clause 9 — Performance Evaluation: Monitoring, measurement, analysis, internal audit, and management review. Internal audit is where most organizations get exposed. The standard requires audits at planned intervals to determine if the QMS conforms. This means you need audit schedules, audit criteria, competent auditors, and records of findings with corrective action follow-up. Using your own operations team to audit their own processes without proper independence is a recurring problem. Clause 10 — Improvement: Nonconformity and corrective action. This is the clause that separates organizations that maintain certification from those that genuinely improve. The question here is whether you have a process for identifying nonconformities, taking action to control them, analyzing root causes, implementing corrections, and reviewing the effectiveness of those actions. The standard explicitly requires root cause analysis. Just fixing the symptom and closing the record is insufficient and auditors know it.
The Real Problems People Face With ISO 9001:2015 Audits
Having gone through dozens of these audits, here are the counter-intuitive things that actually trip organizations up: First, the scope statement. If your scope is vague or excludes significant activities, auditors will expand it during the audit itself. I saw a company with a scope of "provision of logistical services" get three nonconformities because the auditor determined their warehouse operations fell outside the stated scope, which meant those operations were unmanaged under the QMS. Define your scope precisely with boundaries clearly stated. Second, management review inputs and outputs. The standard lists specific inputs required under Clause 9.3.2. Many organizations skip this entirely or produce a document that merely records attendance. The output must include decisions and actions related to continual improvement. A management review with no recorded decisions is worse than no management review at all, because it creates a documented gap.
Third, the interaction between Clause 8 and Clause 6. Risk-based thinking must connect to your operational controls. If you identify a risk in Clause 6 but your Clause 8 procedures do not address it, the risk treatment is theoretical. During an audit of a medical device distributor, I found that the organization identified supplier reliability as a significant risk but had no Clause 8.4 provisions for supplier monitoring. The risk register and the operational controls existed in completely separate systems with no cross-reference. There is also a practical limitation worth noting upfront: ISO 9001:2015 does not prescribe specific forms, templates, or software. This flexibility is both its strength and its weakness. Organizations that try to over-document every requirement tend to produce systems that are cumbersome and rarely used. Organizations that under-document struggle to prove conformity. The balance depends entirely on your organization's size, complexity, and the competence of your people. Small organizations with stable processes often need less documentation than large, complex ones. That is a direct consequence of the proportionality principle built into the standard.

What to Do Before an Audit
Run a mock internal audit using your own question list. Not the generic template from a consultant. The one you built from your own clause mapping. Schedule it at least three weeks before the external audit. This gives you time to find gaps, document corrective actions, and produce evidence trails. A mock audit typically takes one to two days for a small organization and three to five days for larger operations. Check your documented information against the requirements in Clause 7.5. You need a quality manual (not explicitly required but still common practice), the quality policy, objectives with monitoring records, and evidence of operational control where your processes are complex. Some of these are mandatory. Some are optional depending on your context. Know the difference. Review your last management review output. Make sure any actions from it have been completed or have documented status. Auditors always check whether management review decisions led to actual changes in the system. If your management review recommended process improvements and nothing changed, that becomes a finding about the effectiveness of your QMS.
Prepare your personnel. Not by coaching them on what to say. By ensuring they understand their roles in the QMS and can describe what they do in relation to the standard's requirements. When an auditor asks a shop floor worker about a procedure and that worker cannot explain how their work connects to quality objectives, it reflects poorly on Clause 7.3 awareness regardless of whether the worker actually knows their job well. The audit itself usually runs from two days to a week depending on organization size and number of sites. Be present. Have your QMS manager available. Bring records when asked. Do not volunteer extra information beyond what the question requires. Answer the question that was asked. If the answer is unclear, ask for clarification rather than guessing. I have found that the organizations that pass audits cleanly are not the ones with the most documentation. They are the ones whose actual practices align closely with what the standard requires. Documentation follows practice. It does not create it. That distinction matters more than anything else in this process.