Why Your Risk Department Keeps Getting Rejected by Auditors
I spent three years dealing with insurance companies who would flat-out reject risk assessment reports because the terminology didn't match what they expected. The problem wasn't that our risk methodology was wrong. It was that we were using "probability" when they meant "likelihood," or "severity" when they wanted "consequence." This is exactly what
Iso Iec Guide 73
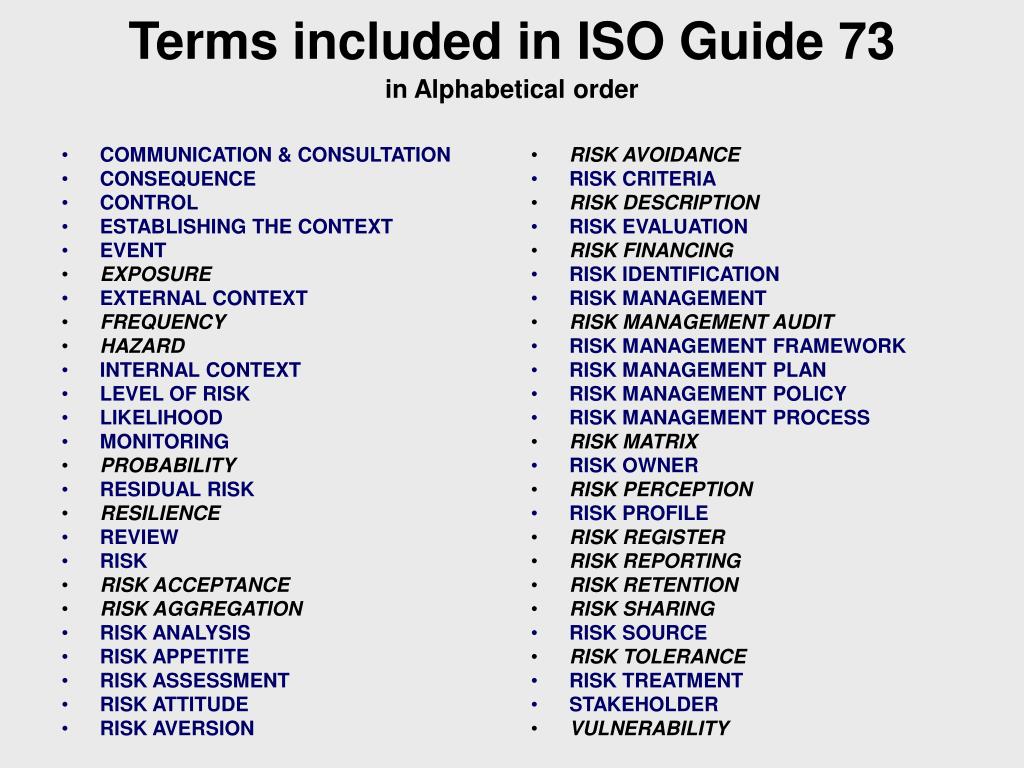
exists to fix, and most people treat it as an afterthought instead of the foundation it actually is. ISO/IEC Guide 73 is the international standard for risk management vocabulary. Full stop. It was originally published in 2009 and revised in 2018 to align with ISO 31000. The guide doesn't tell you how to manage risk. It tells you how to talk about risk so that when you say "risk," everyone in the room understands the same thing. Here's what most people miss. Guide 73 defines risk as the effect of uncertainty on objectives. Not just negative outcomes. Not just threats. Effect. That word matters. An effect can be positive, negative, or both. When your organization's risk culture treats risk purely as something to avoid, you're already outside the standard's definition before you even start. I've seen this break assessments in defense contracting and pharmaceutical compliance equally.The vocabulary section is deceptively thick. There are about 85 defined terms across nine categories: foundations, framework, process, principles, evaluation, identification, analysis, treatment, and monitoring. Most consultants skim the first few chapters and go straight to the charts. That's a mistake. The definitions of "risk criteria" and "risk appetite" are where 90% of disputes happen in audit reviews.
How It Actually Works in Practice
I remember working with a mid-tier hospital network that needed to align their clinical risk framework with ISO 31000. They had two different departments using completely different scales for the same concept. One used a 1-5 likelihood scale based on frequency. The other used a 1-5 scale based on impact. Neither referenced Guide 73's definition of "likelihood" as "the chance of something happening," which explicitly separates the concept from "impact" or "consequence." Their matrices were incomparable. The fix wasn't complicated. We went back to Guide 73 Section 4.2 and 4.3, established separate scales for likelihood and consequence, and cross-referenced them to the ISO 31000 risk assessment process. It took about two weeks of work and eliminated three months of back-and-forth with their external auditors. The key insight is that Guide 73 is designed to be used alongside ISO 31000, not independently. Using it alone gives you vocabulary without methodology, which is worse than having no standard at all.
Get the Full Details
Where People Get Stuck
The biggest practical problem I've encountered involves "risk treatment." Guide 73 defines four treatment options: retain, reduce, avoid, and transfer. But the standard deliberately doesn't specify how to choose between them. That's left to the organization's own risk criteria and context. When auditors find organizations that just pick "transfer" for everything because it's easiest on paper, that's a direct violation of the principle behind the guide. Another edge case: residual risk. Guide 73 defines this as the risk remaining after treatment. The problem is that many organizations calculate residual risk incorrectly by simply subtracting the treatment effect from the original risk score. That doesn't work mathematically when you're dealing with probabilities and complex risk models. I once caught this in a financial services audit where a firm claimed 80% risk reduction from a control, but the residual risk calculation didn't account for compounding variables. The auditor rejected the entire risk register because of it.
What This Standard Doesn't Cover (And Why That Matters)
Guide 73 is not a risk management framework. It's a vocabulary reference. If you try to implement it as a standalone system, you'll fail. The standard provides definitions, not procedures. It doesn't tell you how to identify risks, how to analyze them quantitatively, or how to create a risk register. For that, you need ISO 31000, ISO 31010 (which covers risk assessment techniques), and sector-specific standards. Another limitation: the standard assumes a certain level of organizational maturity. Small businesses or startups often find Guide 73 unnecessarily detailed for their needs. The vocabulary is precise, but precision requires a certain administrative overhead to maintain. A two-person tech startup managing project risks doesn't need 85 defined terms. They need a simple risk matrix. Guide 73 becomes useful when you're operating across departments, geographies, or regulatory environments where communication breakdowns are costly. The revision history is also worth noting. The 2018 update restructured several definitions to align with ISO 31000:2018. If you're working with older versions of documents that reference Guide 73:2009, you may encounter terminology conflicts. "Risk assessment" in the 2009 version had a slightly different scope than in 2018. Always verify which version your organization is using and document it clearly. I've seen this cause confusion in merger and acquisition due diligence.
The Download Situation
ISO/IEC Guide 73 is a paid standard. It's available through the ISO website and national standards bodies. There's no legitimate free PDF. Any site offering a free download is distributing it illegally. The cost is approximately 60-80 Swiss francs, depending on your region. Some organizations get institutional access through university libraries or professional bodies. Check if your industry association has a license agreement before paying retail. If you're doing this on a budget, consider starting with the free summary documents ISO publishes. They outline the main concepts without the full legal definitions. For actual compliance work, though, you'll need the complete standard. The definitions section is the part that carries legal weight in contracts and audits.

One Counter-Intuitive Thing About This Guide
Most people treat Guide 73 as a reference document they consult when asked. The smarter approach is to make it the first document you write into your risk management procedure. Before you build a single risk register, before you create any assessment templates, define your terms using Guide 73. This prevents the terminology drift that happens when different teams interpret "risk" and "impact" differently. I've seen organizations save hundreds of hours in audit preparation time by doing this upfront instead of trying to retrofit consistency later. The standard also pairs particularly well with ISO 31000's principle of "tailoring." Guide 73 gives you the vocabulary; ISO 31000 gives you the framework. Together they form the backbone of any serious risk management program. Used separately, each one is significantly weaker than its combined potential.
-Character PDF document8448-600x849.png "ISO/IEC Guide 73:2002 PDF – IEC Norm Store")