What You Actually Need to Know About IT Audit Interview Questions And Answers
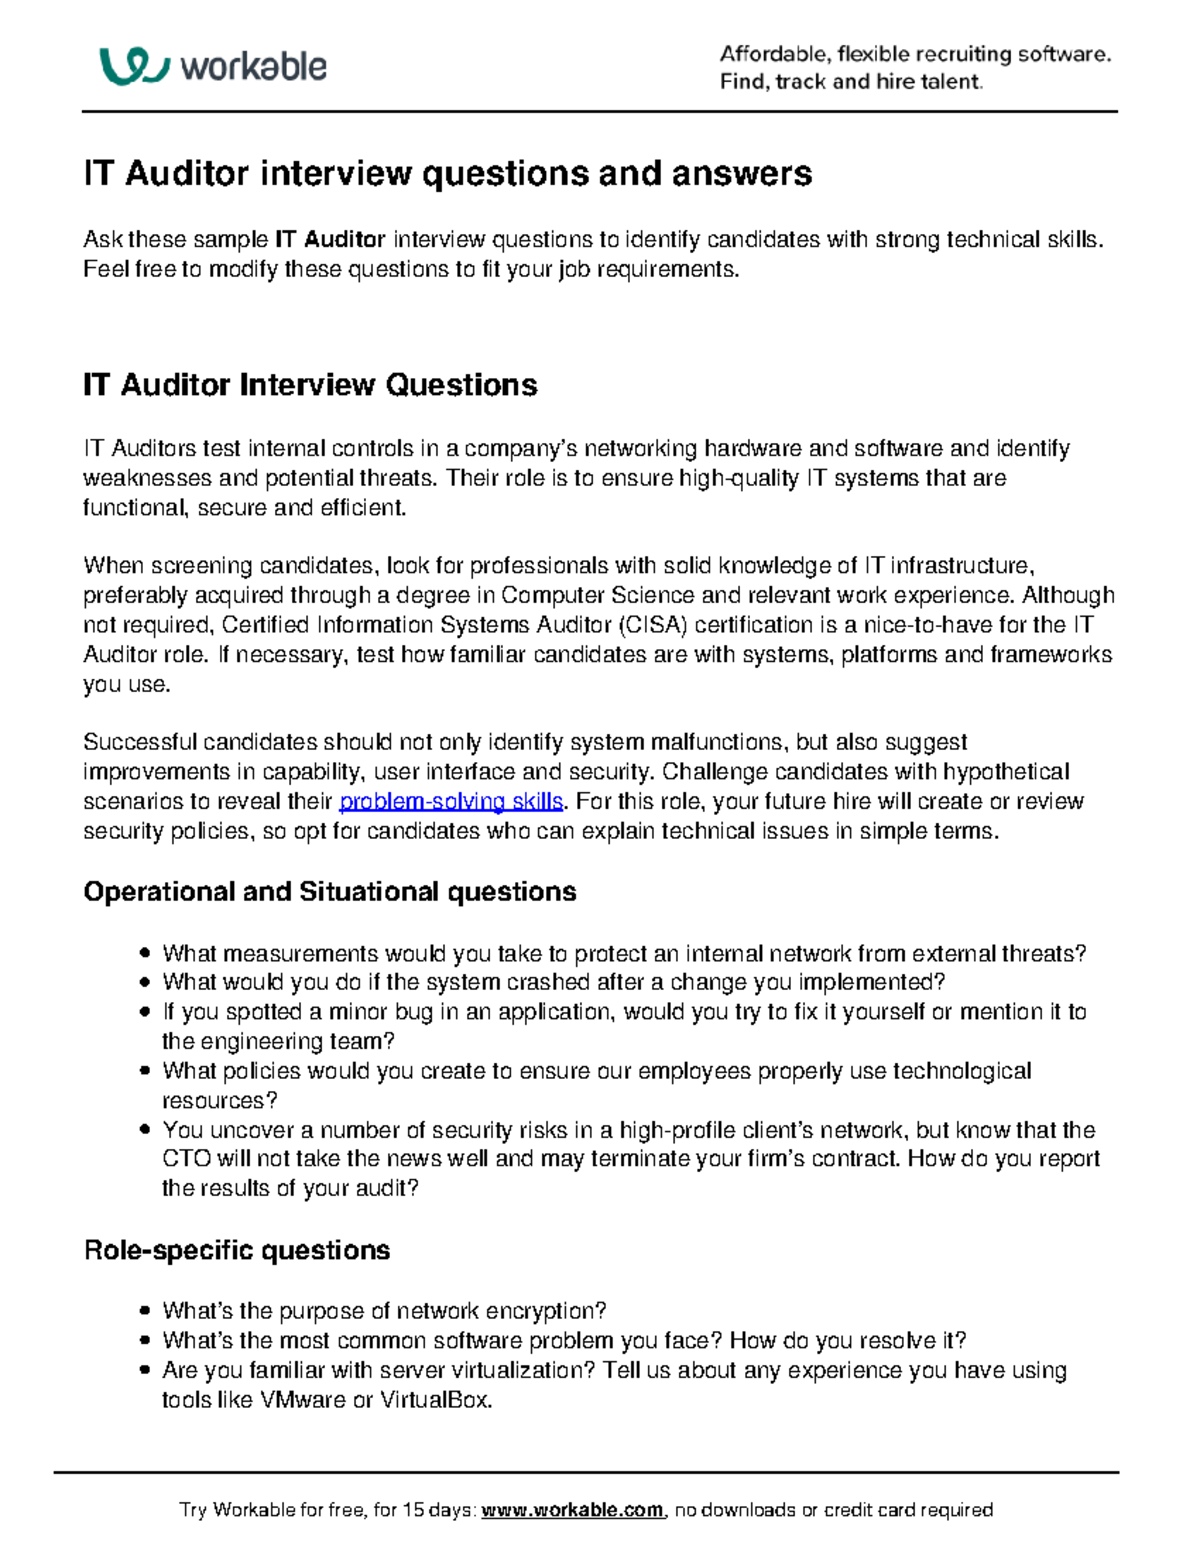
Most people prep for IT audit interviews by memorizing generic answers from YouTube videos. That approach fails because real interviewers dig past rehearsed responses within the first five minutes. I've sat on both sides of those tables too many times to waste time on theory. Here is what actually works when you are trying to prepare solid It Audit Interview Questions And Answers that show you understand the work. The first thing I look for is whether the candidate can walk through a specific audit lifecycle without getting lost in buzzwords. A typical path goes like this: risk assessment, scoping, control testing, finding documentation, and reporting. That sounds straightforward until someone asks you to explain how you'd scope a cloud migration audit across three different AWS regions while the infrastructure team refuses to share network diagrams. I ran into that exact situation at a manufacturing client last year. The workaround was pulling VPC flow logs directly from CloudWatch and reconstructing the network topology from NAT gateway traffic patterns instead of waiting on the team. That kind of problem-solving is what separates candidates who get the offer from the ones who don't. Don't just recite frameworks. COBIT, ISO 27001, NIST, SOC 2 — they all exist and interviewers expect you to know which ones map where. But the real test comes when they ask you to pick one framework and justify why it fits a specific engagement. If you say NIST for a financial services firm, you should also mention that FINRA and SEC regulations pull different compliance requirements that NIST doesn't fully cover. A candidate who brings that up without being prompted is already ahead of half the room.
Control testing is where most people fumble. There are two types of controls and you need to know the difference cold. Design effectiveness checks whether a control is properly structured on paper. Operating effectiveness checks whether it actually runs consistently over time. I had a junior auditor once spend three weeks documenting all the password rotation policies for a healthcare client only to discover during operating effectiveness testing that the automated tool enforcing those rotations had been disabled for eleven months. The design was perfect. The reality was completely different. That gap between documented controls and actual execution is exactly what interviewers want to see you understand. When they ask about sampling methodologies, don't just name-drop statistical versus non-statistical sampling. Explain the practical constraints. Judgmental sampling takes hours instead of weeks. Random sampling sounds cleaner but requires a complete population list that rarely exists in messy enterprise environments. I once told an interviewer I preferred stratified random sampling because it balances rigor with the reality that nobody hands you a clean data dump. She asked how I'd handle a population of 47,000 active directory accounts without automated tools. I said I wouldn't. I'd use attribute sampling with a confidence level of 90 percent and a tolerable deviation rate based on the control's risk rating. She nodded and moved to the next question. Here is something most prep guides skip: technology stack familiarity matters more than candidates realize. You don't need to be a developer, but saying you've never audited a SQL Server environment or looked at application logs from a Java-based system raises eyebrows. I recommend picking up a basic understanding of how Windows Event Logs, SIEM platforms like Splunk or ELK, and common database query structures work. Understanding how to pull a basic SELECT statement with a WHERE clause to verify data integrity saves you from looking lost when the engagement manager asks whether you've ever tested data completeness directly.
Interviewers also test how you handle pushback. Every audit encounters resistance. The most common form is someone telling you their control is working fine without providing evidence. I dealt with this at a retail chain where the inventory management team insisted their reconciliation process was foolproof. I asked for thirty days of signed reconciliation reports going back six months and they produced seventeen. The gap itself became the finding. Learning to push for documentation without being confrontational is a skill you develop slowly. The phrase "I just need to verify that for my workpaper" works better than you'd expect. Reporting is another area where answers tend to sound hollow until you've written actual audit reports. Findings need four components: condition, criteria, cause, and effect. Anyone can list those. The hard part is writing the cause and effect sections in a way that management actually understands and can act on. A finding that says "access reviews are not performed" tells management nothing useful. A finding that explains "monthly access reviews were not conducted between January and September 2024, resulting in forty-three terminated employees retaining active directory access beyond their offboarding date" is actionable. I've seen good findings destroyed by vague language and bad findings elevated by clear cause-and-effect writing. One counter-intuitive point about IT audit interviews: knowing less is sometimes better than bluffing. When an interviewer asks about something you genuinely haven't encountered, the correct answer is to acknowledge the gap and explain how you would approach learning it. I was asked once about ISAE 3402 type II reports and admitted I'd only worked with SOC 2 reports before. I then explained the structural similarities and differences I'd drawn from reading the standard. The interviewer said that was exactly the right way to handle it. Bluffing gets caught and it never recovers.
Get the Full Details
Here is a practical limitation you should be aware of: there is no single definitive list of It Audit Interview Questions And Answers that covers every scenario. Interview questions shift depending on whether the firm focuses on financial services, healthcare, government contracts, or general enterprise audits. A firm auditing HIPAA compliance will ask very different questions than one auditing PCI DSS for payment processors. Your preparation should reflect the target employer's industry focus rather than trying to master every possible angle. If you want a concrete starting point, build your own question bank organized by domain. Cover general IT controls, application controls, change management, incident response, and access governance. For each domain, write a scenario-based question that forces you to explain your reasoning rather than just naming a concept. Then test yourself out loud. Recording your answers and listening back reveals filler words, vague statements, and logical gaps faster than any written practice. The bottom line is that IT audit interviews test judgment more than knowledge. You will get questions where the technically correct answer depends entirely on the context provided. The candidates who perform best are the ones who pause, ask clarifying questions, and structure their response around risk rather than framework compliance. Everything else is noise.