
Preparing for security analyst interviews is mostly about recognizing patterns and knowing where you'll get stuck
I've sat on both sides of these It Security Analyst Interview Questions for years now. You'll notice the format doesn't change much across companies, even though they pretend it does. The technical rounds usually test the same three buckets: networking fundamentals, log analysis, and incident response procedures. The behavioral round tests whether you'll panic when something breaks at 3 AM. I've learned to stop being surprised by either outcome. Start with the TCP/IP model and understand it at a layer-by-layer level. Not just "TCP is reliable," but what happens during a three-way handshake when one of the packets is dropped, or why an SYN flood works the way it does. I had a candidate once describe the OSI model as "seven layers that stack up" and then couldn't explain why ARP doesn't route. That's the bar for the networking portion, which is honestly lower than most people expect. Log analysis comes next. You need to be comfortable reading raw logs — Apache access logs, Windows Event Logs, firewall logs from Palo Alto or Fortinet, and something SIEM-adjacent like Splunk or ELK. A realistic exercise I give involves dropping a CSV of pseudo-authentication events and asking candidates to find the anomaly. The trick isn't finding the obviously malicious IP. The trick is spotting the slow lateral movement that looks normal for four days and then spikes on day five. Most people miss it because they're looking for explosions instead of whispers.
Incident response frameworks matter too. NIST 800-61 and SANS PICERL are the ones that get referenced. You don't need to memorize them verbatim, but you should know the stages and be able to talk through what happens in each one under pressure. I once watched a candidate recite the phases perfectly and then couldn't explain what they'd personally do if they found a suspicious process running on a production server at 2 AM with no team member available. That gap between textbook knowledge and real judgment is what separates people who get offers from people who don't. Here's something most prep guides won't tell you. The tools section matters less than you think. People spend weeks learning Snort rules or getting SIEM platform certifications, but the actual interview will probably ask you to walk through a scenario using concepts, not specific product syntax. I've hired analysts who couldn't write a Splunk search but could reason clearly about how to triage a ransomware alert. I've also rejected analysts who knew Splunk inside out but couldn't explain why a false positive might look identical to a real detection. For the hands-on portion, expect a practical exercise. Some companies use platforms like TryHackMe or Security+ style labs. Others just give you a scenario document and ask you to write out your investigation steps. The scenario I run most often involves a compromised endpoint with suspicious PowerShell execution. The candidate needs to identify the indicators of compromise, explain containment steps, and outline evidence preservation. The mistake most people make is jumping straight to remediation without establishing a timeline first. I want to see them talk through what happened before they start talking about what to fix.
There's also the cloud angle now. Every interview I sit on includes at least one question about AWS or Azure security. IAM misconfigurations, security groups, S3 bucket permissions — these come up constantly. One candidate got everything right on-premises and then froze when I asked about the difference between an IAM role and an IAM policy in AWS. That's a real gap I see more often than I'd like. Soft skills get tested implicitly throughout the process. When you're explaining a technical finding, are you talking down to the listener or adapting to their level? I've seen strong technical candidates fail because they treated the interviewer like an exam proctor instead of a future colleague. The role requires communicating risk to people who don't think in terms of CVEs and IOC hashes. If you can't explain why a vulnerability matters to a business stakeholder in two sentences, you'll struggle in the job regardless of your technical depth.
Get the Full Details

Common question categories and what they're really testing
Network security questions typically cover firewalls, IDS/IPS, VLANs, and DNS. You should know the difference between stateful and stateless inspection, understand how DNS tunneling works as an exfiltration method, and be able to explain why a DMZ exists. A frequent question is "how would you detect data exfiltration over DNS?" The answer involves looking at unusually long subdomain labels, high query volume from a single host, and encoding patterns consistent with tools like iodine or dnscat2. People who just say "monitor DNS traffic" are giving the kind of answer that gets nodding but no offer. Threat intelligence questions test whether you understand the difference between strategic, operational, and tactical intelligence. I once asked a candidate to explain how they'd use threat intel during an active breach. They talked about downloading IOCs from AlienVault OTX and blocking them. That's reactive. The better answer involves correlating adversary TTPs with your environment, understanding the attacker's likely objectives, and prioritizing detections based on relevance to your specific infrastructure. The distinction matters because blocking IOCs alone is what keeps defenders behind the curve. Vulnerability management is another standard topic. You need to understand CVSS scoring, patch management cycles, and the tradeoff between risk acceptance and remediation. A question I use involves a critical vulnerability in an unsupported legacy system. The expected answer acknowledges the risk, proposes compensating controls like network segmentation or WAF rules, and discusses the business impact assessment process. Candidates who immediately say "patch it" without considering downtime impact or fallback options haven't worked in an operational environment long enough.
Cryptography questions show up less frequently now than they used to, but they still appear. Know the difference between symmetric and asymmetric encryption, understand what TLS actually protects, and be able to explain why SHA-1 is deprecated. I asked someone once to explain the practical risk of using MD5 for password hashing. They correctly identified collision attacks but couldn't connect that to why rainbow tables and brute force are the actual day-to-day threat for most organizations. That disconnect between academic knowledge and practical relevance is telling.
What most candidates do wrong
The biggest mistake I see is treating the interview like a knowledge recitation test instead of a problem-solving demonstration. When you answer, walk through your reasoning. Say things like "I'd start by checking X, then if I see Y I'd move to Z." It's okay to say "I'm not sure, but here's how I'd find out." That's genuinely better than a confident but wrong answer because it shows you understand the boundaries of your knowledge. Another common error is over-indexing on tools. Learning the interface of one SIEM or one EDR product won't help much if the interviewer asks conceptual questions. I'd rather see someone who understands detection engineering principles than someone who can click through a dashboard. Tools change. The underlying logic of how you approach a security problem doesn't. People also tend to undersell their practical experience. If you've managed a home lab, contributed to open-source security projects, or participated in CTFs, mention it. I had a candidate who dismissed their bug bounty experience as "just a hobby" and then spent twenty minutes trying to sound theoretical about vulnerability classification. They could have walked in talking about actual findings and real-world impact assessment. That's valuable and relevant.
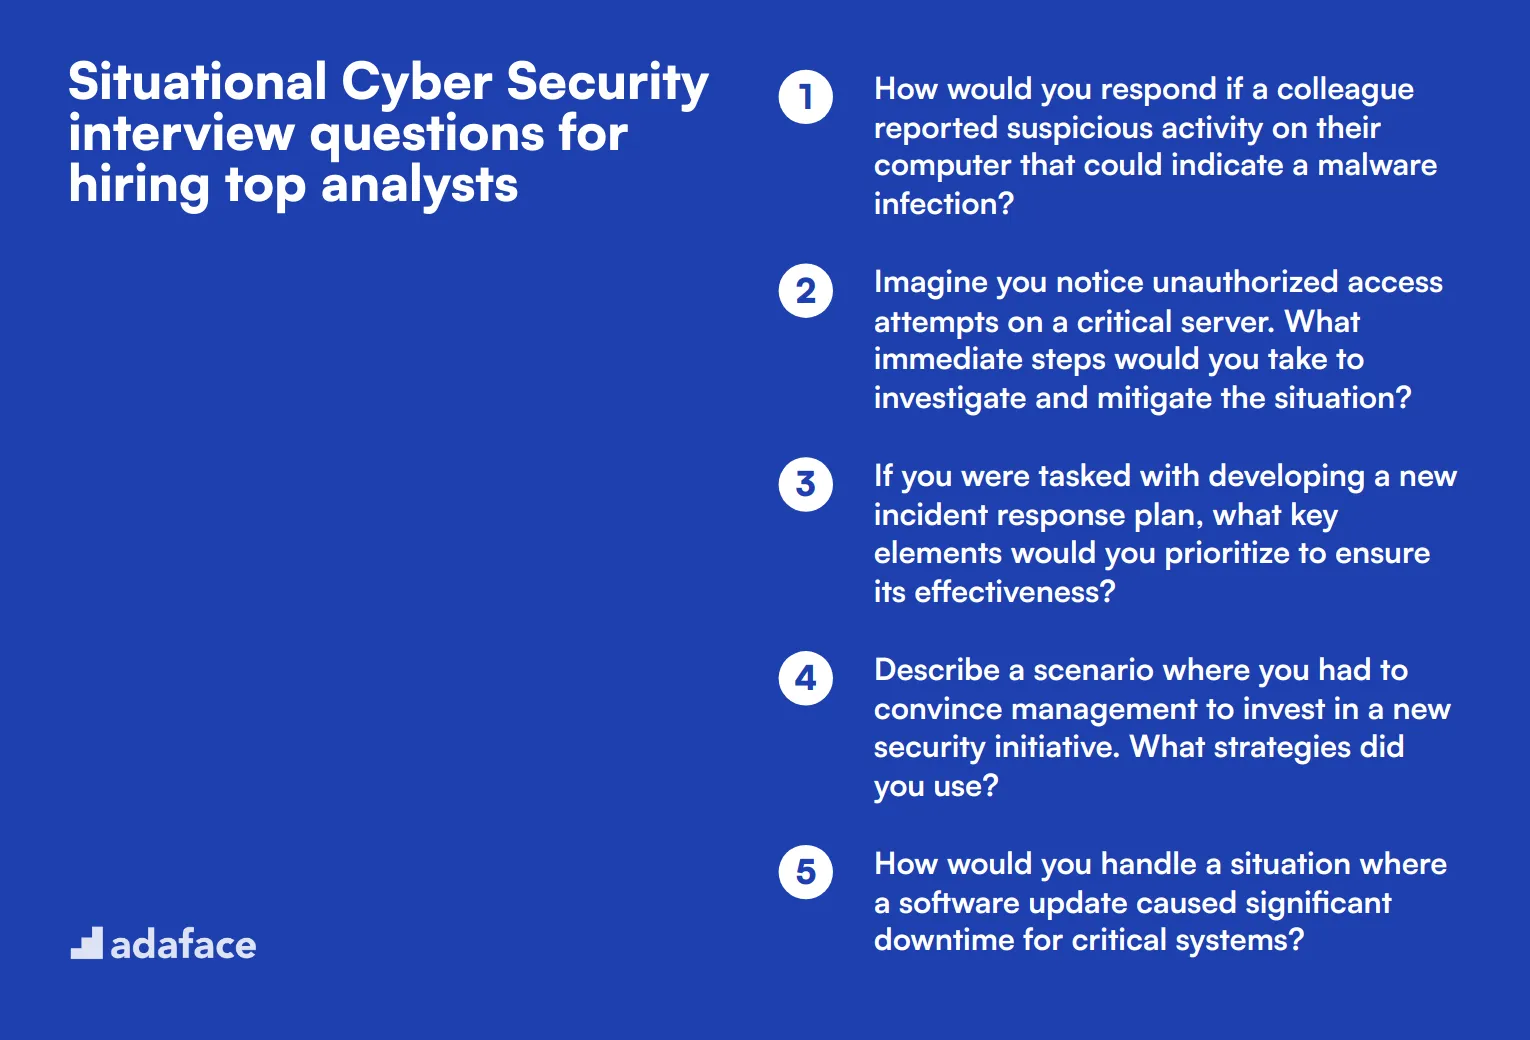
There's also the preparation paradox. Studying too hard for the specific questions you expect will backfire because interviewers vary their questions based on what they hear. I adjust my follow-ups based on a candidate's answers, so someone who memorized a script looks robotic when I pivot. The better approach is understanding fundamentals deeply enough that you can reason through unfamiliar scenarios. That requires more effort upfront but pays off throughout the entire interview.
A specific edge case from my experience
During one interview cycle, I gave candidates a scenario where an endpoint was reporting anomalous outbound connections to a seemingly legitimate domain. The domain was registered recently but had a legitimate-looking SSL certificate from a known CA. Most candidates focused on the SSL certificate validity and missed the DNS layer entirely. The actual indicator was a DNS record created only three days prior with a DGA-like pattern in the subdomain. This scenario forced candidates to decide which detection layer to prioritize and whether to investigate the domain or the endpoint first. The ones who got it right talked about correlating DNS logs with endpoint process trees to establish causality. The ones who got it wrong started discussing certificate pinning as if that were the primary concern. Three weeks before the interview, spend your first week on networking fundamentals. Review IP addressing, subnetting, common ports and protocols, and the OSI model with a focus on where security controls actually operate. The second week covers security concepts — cryptography basics, common attack vectors, defense in depth principles, and the tools used at each layer. The final week is dedicated to hands-on practice and scenario walkthroughs. For hands-on practice, set up a simple lab with Wireshark and generate some traffic. Capture HTTP requests, observe the TLS handshake, and practice identifying protocol anomalies. If you have access to a SIEM trial version, ingest some sample logs and write detection queries. Even basic pattern matching in Splunk's Search Processing Language will improve your comfort level significantly. One hour of actual log interaction is worth more than three hours of reading documentation.
Mock interviews with a peer or mentor are worth the time investment. Record yourself explaining a security concept out loud. You'll immediately notice where your explanation jumps over gaps in understanding. I always recommend doing this before the actual interview because nervousness amplifies every weak point in your knowledge.

What happens after the technical interview
The final round is typically cultural fit and scenario-based discussion. You might be asked about handling conflicting priorities, working with uncooperative teams, or explaining risk to non-technical stakeholders. These aren't easy questions to prepare for because the answers depend heavily on your actual work history. The honest approach works best. If you haven't dealt with a situation, describe the framework you'd use to figure it out rather than pretending you have experience you don't have. Reference checks and background verification follow standard procedures. Make sure your certifications are current and your LinkedIn profile matches your resume. I've seen candidates lose offers because their listed CloudSec certification had expired six months prior and they hadn't mentioned it. The whole process from application to offer typically takes two to four weeks depending on the organization. During the waiting period, don't stop studying. Keep reviewing material and practicing scenario explanations. Interviewers sometimes circle back for additional rounds or reference checks, and being caught off guard during a follow-up conversation looks worse than it should.
The security analyst role itself demands continuous learning after you're hired. The questions you face in interviews are the entry threshold, not the ceiling. The field moves fast enough that the knowledge you build during interview prep will need significant updating within your first year on the job. That's not a deterrent, it's just the reality of working in this space.


