What actually happens when you try to bridge JavaScript and assembly
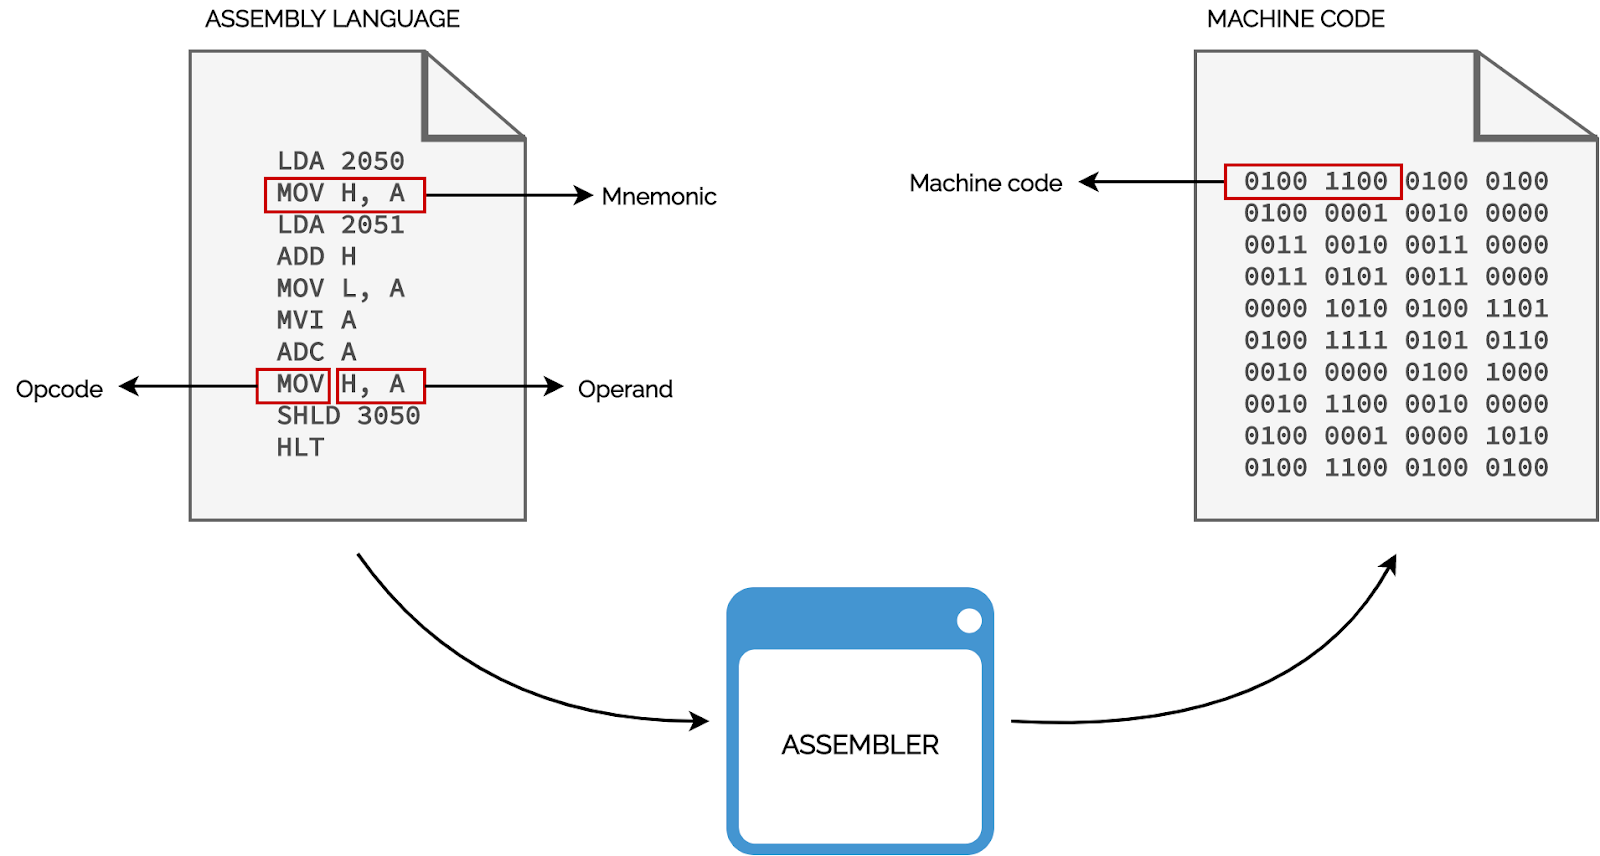
JavaScript runs on a virtual machine or runtime like V8, Node.js, or SpiderMonkey. Assembly runs directly on hardware. They exist at completely opposite levels of abstraction. When someone asks about Js In Assembly Language, they usually mean one of three things: emitting assembly from JavaScript tools, calling assembly routines from JavaScript via WebAssembly or native addons, or manually reading/understanding the assembly output that a JS compiler produces. I spent about six months dealing with the third use case when we were optimizing a hot loop in our WebGL rendering path. V8's TurboFan generates x64 assembly during compilation, and we needed to verify that the JIT was doing something reasonable. The toolchain for that is messy but straightforward once you know where to look.
How to see assembly generated from JavaScript
If you want to observe the actual assembly that V8 emits for your code, you don't need anything exotic. Run Node.js or Chrome with the appropriate flags: node --print_opt_info your_script.js This dumps optimization info to stderr including the listing for optimized functions. On older Node versions you would use --trace-opt --trace-deopt to watch which functions get compiled and which get kicked out of optimization. It is not a decompiler. It shows you what the JIT decided to emit, not your original source.
For a browser environment, you can use console.log(functionName.toString()) in some contexts, but that just shows the source, not the assembly. The real way is through the Chrome DevTools console if you are running a build with internal APIs exposed, or by using the --print-opt-info flag in a headless Chrome instance built with internal flags enabled. Most production Chromium builds hide those flags.
Get the Full Details

Calling assembly from JavaScript
The most practical route today is WebAssembly. You write the logic in C, C++, or Rust, compile it to a .wasm module, and call it from JavaScript. The JavaScript side looks almost normal. The assembly side is handled by whatever compiler you used. Here is what a basic setup looks like:
// JS side
const wasm = await WebAssembly.instantiateStreaming(fetch('module.wasm'));
const result = wasm.instance.exports.do_heavy_computation(42, 77);
The Rust side compiles to WebAssembly target: I ran into a specific problem with pointer passing between JS and Wasm when dealing with typed arrays. You might think you can just pass a JavaScript Uint8Array reference and read it on the Wasm side. You cannot. The correct approach is to use the Wasm linear memory and copy data in both directions, or use the newer JSBigInt and reference type proposals if your runtime supports them. The copy overhead is usually acceptable for blocks under a few megabytes. Beyond that you start hitting GC pressure and allocation spikes that make the whole thing slower than just doing it in JavaScript. If WebAssembly is not sufficient and you need direct system access, Node.js native addons written in C or C++ are the other option. The Node.js N-API gives you a stable ABI, which means your addon does not break between Node major versions. The downside is that you are now maintaining compiled binaries for multiple platforms and architectures.
A minimal addon that exports a function accepting two integers and returning their product looks like this in C:

#include <node_api.h>

napi_value Add(napi_env env, napi_callback_info info) {
    size_t argc = 2;
    napi_value args[2];
    napi_get_cb_info(env, info, &argc, args, NULL, NULL);

    int64_t a, b, result;
    napi_get_value_int64(env, args[0], &a);
    napi_get_value_int64(env, args[1], &b);
    result = a + b;

    napi_value output;
    napi_create_int64(env, result, &output);
    return output;
}
Compile with napi_build_v5 and load in JavaScript with require('./build/Release/addon.node'). That path changes depending on your build system and target platform. Writing assembly by hand for performance gains in a JavaScript context is almost never worth it. The JIT compilers in V8, SpiderMonkey, and JavaScriptCore are significantly better than what a single developer can produce in inline assembly. The times when it makes sense are narrow: you need to interface with existing C/C++ libraries, you are doing cryptographic operations that need constant-time implementations, or you are working on a WebAssembly module where the compiler is not producing acceptable code for a very specific algorithm. Even then, the debugging experience is terrible. Stack traces from Wasm call sites are indirect. Error messages reference instruction offsets, not line numbers in your source. Native addon crashes take down the entire Node process with no recovery. A segmentation fault in C becomes an unhandled exception in JavaScript that you cannot catch at the point of origin.
If you genuinely need performance, profile first. Use the Chrome profiler or Node's built-in CPU profiler. Most of the time you will find that the bottleneck is not the computation but allocation patterns, garbage collection pauses, or I/O. Fixing those issues in pure JavaScript will give you more gain than any amount of hand-written assembly.
When manual assembly actually helps
There is one scenario where understanding the assembly output matters: verifying that your code is not triggering hidden allocations or boxing. V8 optimizes primitive operations extremely well, but certain patterns cause the JIT to bail out of optimization. A function that does simple integer arithmetic can suddenly become unoptimizable if you mix in a string concatenation anywhere in the same scope, because the type inference gets confused. The way to catch this is to watch the deoptimization traces. Run with --trace-deopt and look for functions that were optimized and then taken out. The typical reasons are type mismatches, missing return type assumptions, or exceeding the inline cache size. Once you know what triggers a deopt, you can restructure the code to keep types consistent throughout the hot path. I once had a function that processed sensor data at 44kHz. It was deoptimizing every few thousand calls because a helper function had a conditional that returned either a number or undefined depending on input. The fix was not to rewrite anything in assembly. It was to add an explicit type check at the entry point and return a default value instead of undefined. The optimized path kicked in and stayed optimized. Execution time dropped from about 12 milliseconds per batch to roughly 0.3 milliseconds.
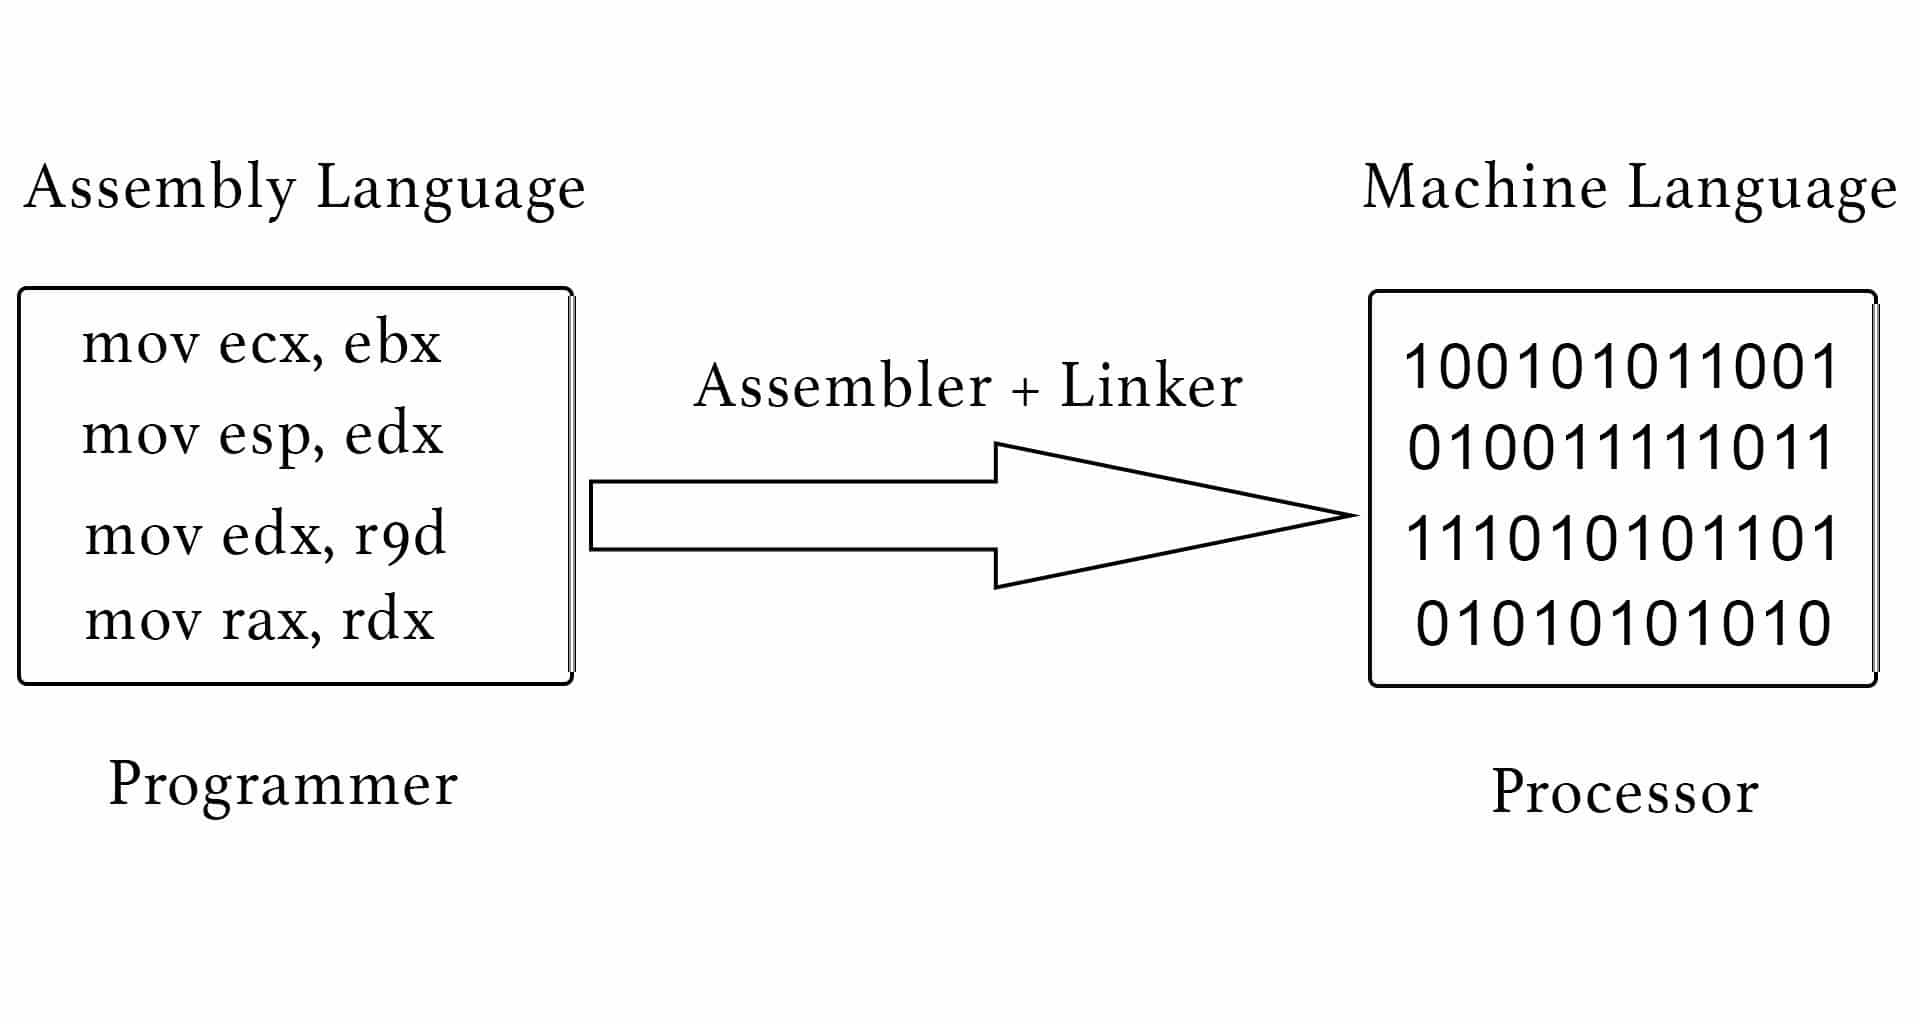
That is the actual value of knowing assembly in a JavaScript context. Not writing it. Recognizing when the compiler is struggling and knowing what to change in the source to help it.