What You Need to Know About KnowBe4 Phishing Test Answers
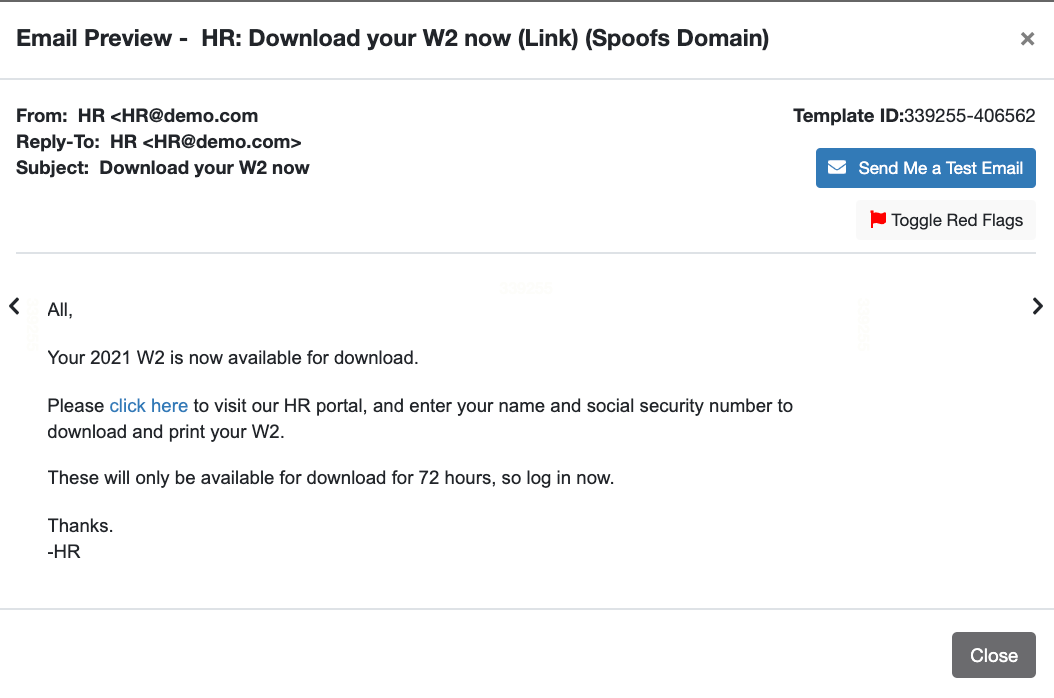
KnowBe4 sends simulated phishing emails to employees as part of security awareness training. When someone clicks the link, they get redirected to a landing page and are then put through a short quiz about what happened. People looking for KnowBe4 Phishing Test Answers are usually trying to pass that quiz after being phished, which is fine on its own. The real question is whether it's doing anything useful. When an employee clicks a simulated phishing link, they land on a page that explains what just happened. The quiz that follows tests whether they understood the warning signs. Typical questions cover things like verifying sender addresses, spotting urgency tactics, and recognizing spoofed domains. The answers aren't tricky. They're intentionally straightforward because the goal is reinforcement, not punishment. I've sat through enough of these modules to notice a pattern. The quiz questions vary slightly depending on which phishing simulation template was used. A fake HR email quiz will ask different questions than a CEO impersonation or a fake IT password reset prompt. If you're searching for answers, you need to match the quiz to the specific simulation type. Generic answer lists found online often won't line up perfectly.
Here's the thing most people skip over. The quiz isn't graded in a way that hurts you. It's designed to be educational. The system tracks whether you completed the training module, not your score. Some organizations configure it so that failing the quiz triggers additional training, but the default behavior in most deployments is that finishing the module satisfies the requirement regardless of quiz performance. So the urgency around finding correct answers is mostly manufactured by anxiety, not by actual policy.
Where the Common Pitfalls Are
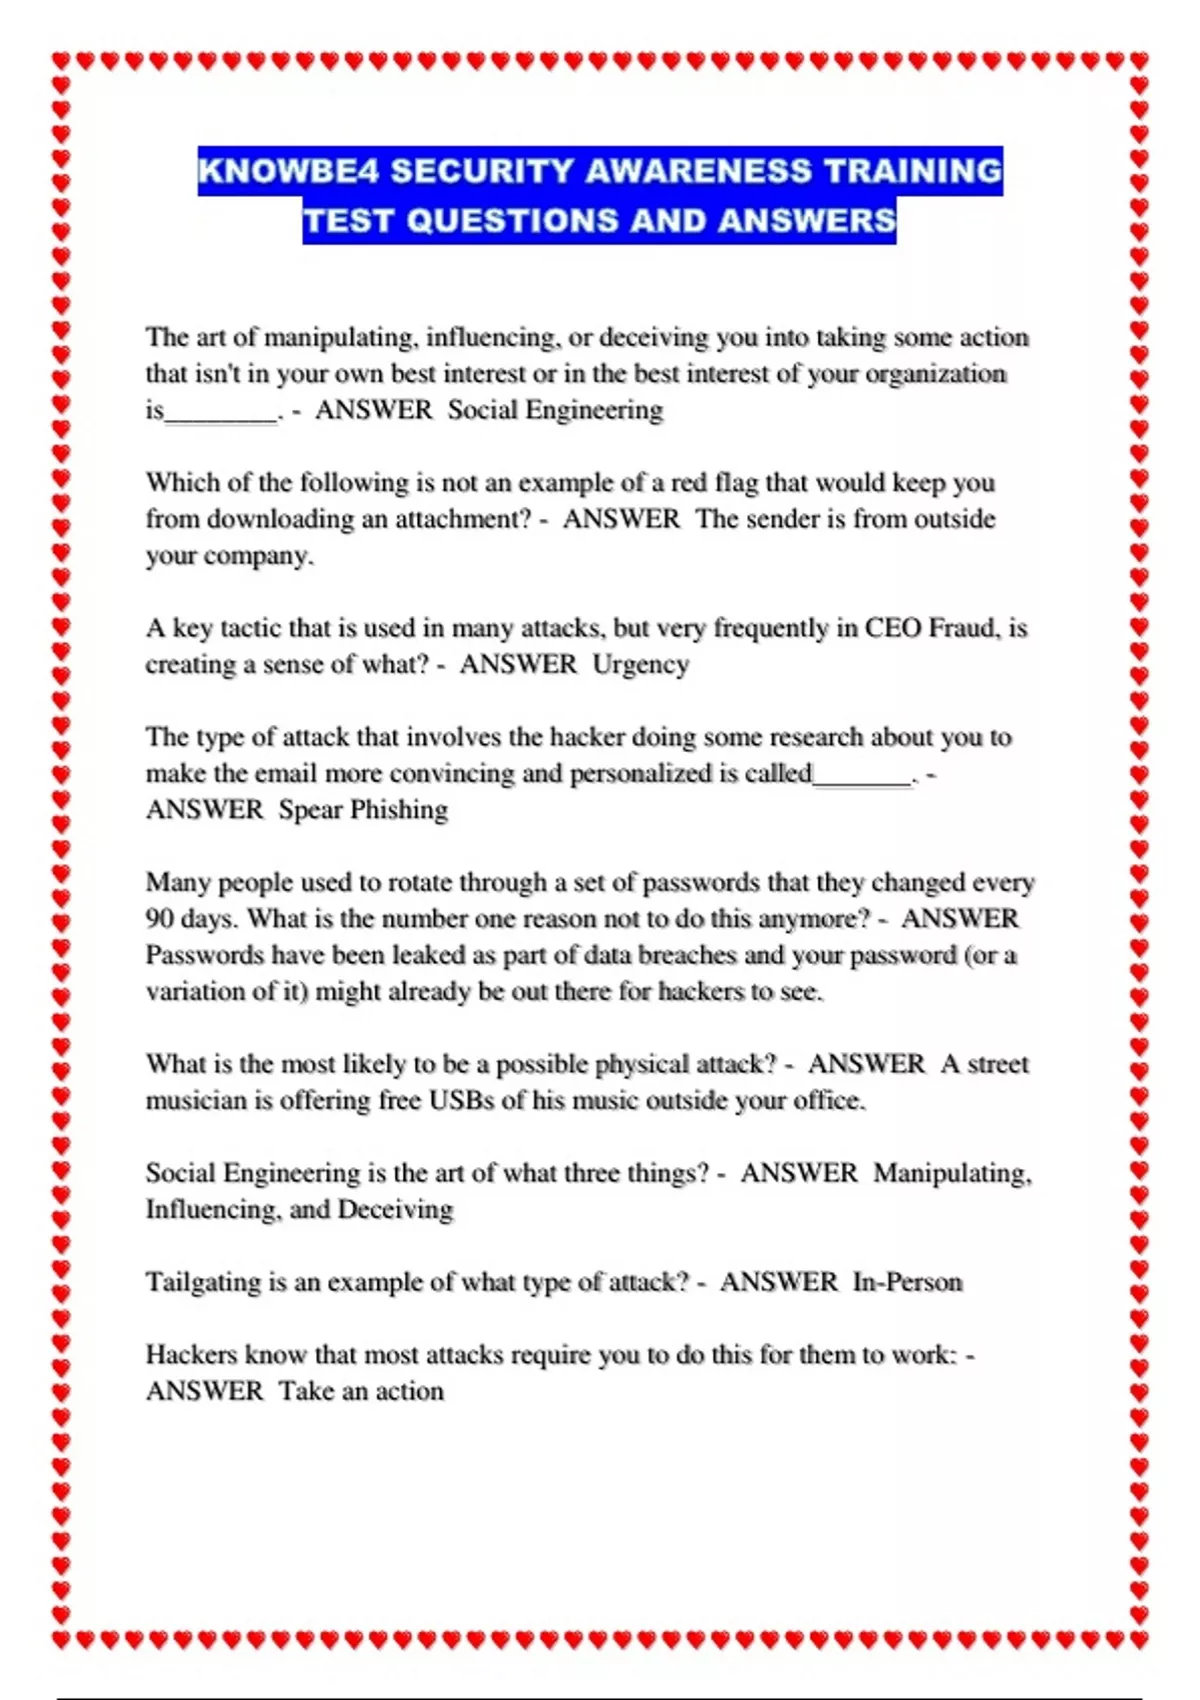
The biggest mistake people make is copying answer keys from third-party sites without reading the actual questions in front of them. KnowBe4 updates its question pools periodically, and the wording shifts. An answer that was correct six months ago might not match the current phrasing. I had a colleague once paste a list of answers into a quiz and get three wrong because two of the questions had been reworded from "Which indicator suggests this email is suspicious?" to "What red flag is present in the sender address?" The meaning was the same but the answer choices were ordered differently. Another issue is time pressure. The training module doesn't impose a strict timer, but people tend to rush through because they want to get back to work. Rushing leads to misreads. I recommend reading every question twice before selecting an answer. It takes maybe thirty seconds extra per question and prevents the frustration of having to restart the module. There's also a configuration edge case worth mentioning. In my experience, some organizations use KnowBe4's "Knowledge Check" feature, which is a separate assessment tool from the phishing simulation quiz. These two systems have completely different question banks. If you find answers for one and try them on the other, they won't work. The Knowledge Check covers broader security topics like password hygiene and social engineering, while the phishing quiz is tied directly to the simulated email scenario you just encountered. Mixing them up is surprisingly common and completely wastes time.
Get the Full Details
The Real Value (and What It Doesn't Do)
These training modules are marginally effective if you actually engage with the material. Reading the explanation on the landing page before answering the quiz questions improves retention compared to rushing through for the sake of completion. I've watched people go from consistently clicking simulated phishing emails to rarely doing so after completing several modules with attention. The improvement isn't dramatic, but it's measurable over time when the organization tracks click rates across quarters. What they don't do is make you secure. KnowBe4 simulations only cover the email vector. Employees who fail the phishing quiz but regularly fall for USB drops or vishing calls haven't learned anything meaningful. The platform offers social engineering simulations beyond email, but most organizations only license the phishing component. That's a gap I've seen repeatedly in customer environments where the security team treats a low click rate as a completed initiative rather than a baseline metric. If you're looking for KnowBe4 Phishing Test Answers, the most reliable approach is to read the training content on the landing page first. The answers are usually contained within that material. Bookmarking the page, reading it carefully, and then answering from memory takes about two minutes longer than searching for a shortcut but actually results in you learning something. That's the whole point, even if the corporate compliance checkbox makes it feel incidental.